ROMULUS ClickFix Platform Delivers LegionLoader and Other Malware
Summary
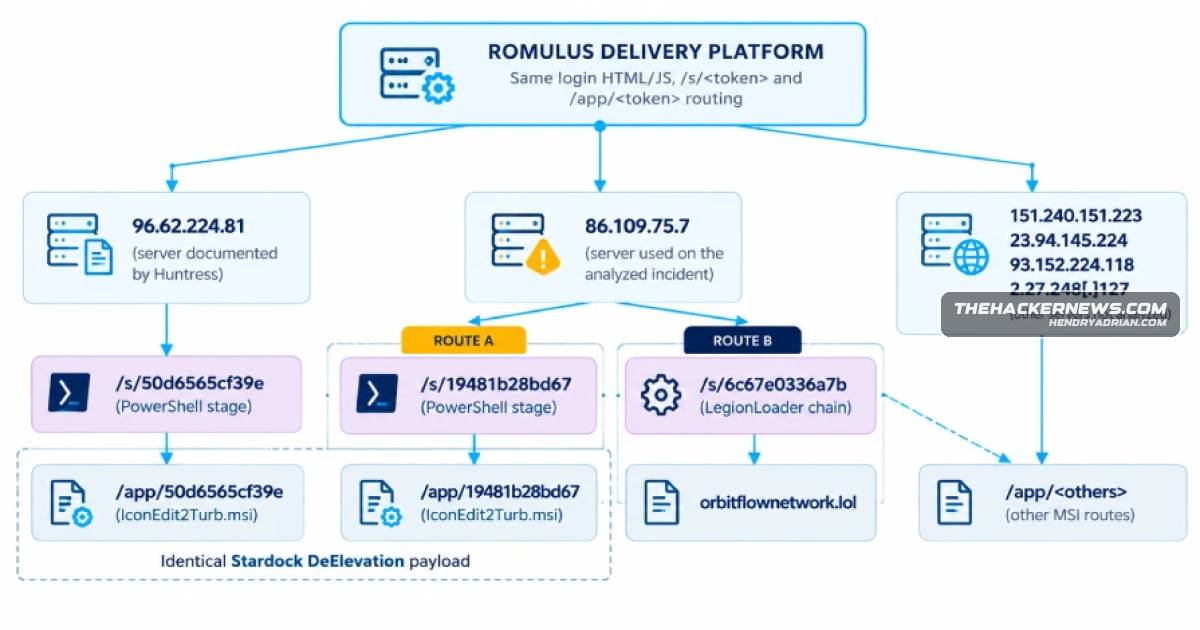
Forescout researchers identified ROMULUS, a ClickFix delivery platform that tricks users into running malicious commands and can deliver LegionLoader and other malware. The platform’s operator is unknown.
Key points
- ROMULUS uses bogus landing pages and ClickFix lures to persuade users to run malicious commands.
- Forescout identified six IP addresses running ROMULUS; one server also hosted a ClickFix script and MSI installer linked to another campaign.
- A separate ClickFix chain runs a PowerShell script that can deliver Legion Loader, CurlyGate, or RobotDropper.
- ROMULUS exposes endpoints that download a PowerShell staging script, which selects a trojanized MSI installer or an encrypted archive containing Legion Loader.
- The Legion Loader archive is padded to nearly 1 GB, potentially to bypass upload limits, sandbox budgets, or static-analysis thresholds.
- Researchers have not identified who operates ROMULUS and reported no overlap with RomulusLoader, which is associated with the Silver Fox threat actor.
- The researchers recommend hunting for suspicious PowerShell commands and DLL sideloading events.
Article Details
- Event Type
- Disclosure of ROMULUS, a ClickFix-style malware delivery platform.
- Impact
- ROMULUS uses bogus landing pages to trick users into running malicious commands. The reported delivery chains can install malware loaders and Legion Loader, which can fetch and run additional payloads. Researchers also report an encrypted Legion Loader archive padded to nearly 1 GB. The article does not identify who operates ROMULUS.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 86[.]109[.]75[.]7 | Server reported to deliver malware and host a panel codenamed ROMULUS. |
| IPV4 | 96[.]62[.]224[.]81 | Reportedly hosted a ClickFix script and MSI installer associated with a malware-delivery campaign. |
MITRE ATT&CK
People
Threat Actors
Malware
DCRatrepeatedly using tax-related pretexts to distribute remote access trojans like ValleyRAT (aka Winos 4.0), DcRAT, and potentially Venom RAT via DLL sideloading techniques.Legion LoaderCybersecurity researchers have disclosed details of a ClickFix delivery platform called ROMULUS that's being used to distribute malware such as Legion Loader.RomulusLoaderAs of writing, it's not known who is behind the ROMULUS platform. However, it shares no overlaps with RomulusLoader, a malware family associated with Silver Fox (aka TA4922), a China-aligned threat actor known forValleyRATthreat actor known for repeatedly using tax-related pretexts to distribute remote access trojans like ValleyRAT (aka Winos 4.0), DcRAT, and potentially Venom RAT via DLL sideloading techniques.VenomRATpretexts to distribute remote access trojans like ValleyRAT (aka Winos 4.0), DcRAT, and potentially Venom RAT via DLL sideloading techniques.Winos 4.0known for repeatedly using tax-related pretexts to distribute remote access trojans like ValleyRAT (aka Winos 4.0), DcRAT, and potentially Venom RAT via DLL sideloading techniques.