
Proofpoint Details TA4922’s Expanding Malware Campaigns
Summary
Proofpoint reports TA4922 expanded from East Asia into Europe and Africa, using localized business lures to deliver Atlas RAT, RomulusLoader, SilentRunLoader and RMM tools. The analysis details sideloading, process injection and Chrome-data theft.
Key points
- Proofpoint tracked TA4922 campaigns from spring 2025 and reported a sharp increase in activity during March and April 2026, with targeting expanding beyond East Asia into Europe and South Africa.
- Proofpoint assesses TA4922 is likely Chinese-speaking and financially motivated; campaigns use localized HR, payroll, tax, benefits and invoicing lures.
- The actor used DLL sideloading to deliver Atlas RAT, RomulusLoader and SilentRunLoader, and used RomulusLoader to deploy legitimate RMM tools AnyDesk and SyncFuture.
- RomulusLoader decrypts and maps an embedded payload, then can inject code into other processes and retrieve further payloads from its command-and-control server.
- SilentRunLoader collects Chrome credentials, cookies and browsing data and exfiltrates it via HTTP POST to infrastructure at ws[.]ztts88[.]cyou.
- Atlas RAT supports system-information collection, file upload, plugin loading, keylogging, and audio, video, clipboard and screenshot capture.
- Proofpoint recommends application allowlisting, monitoring execution from temporary user directories and unexpected system paths, restricting local administrator rights, and monitoring unnecessary network ports.
Article Details
- Attack Vectors
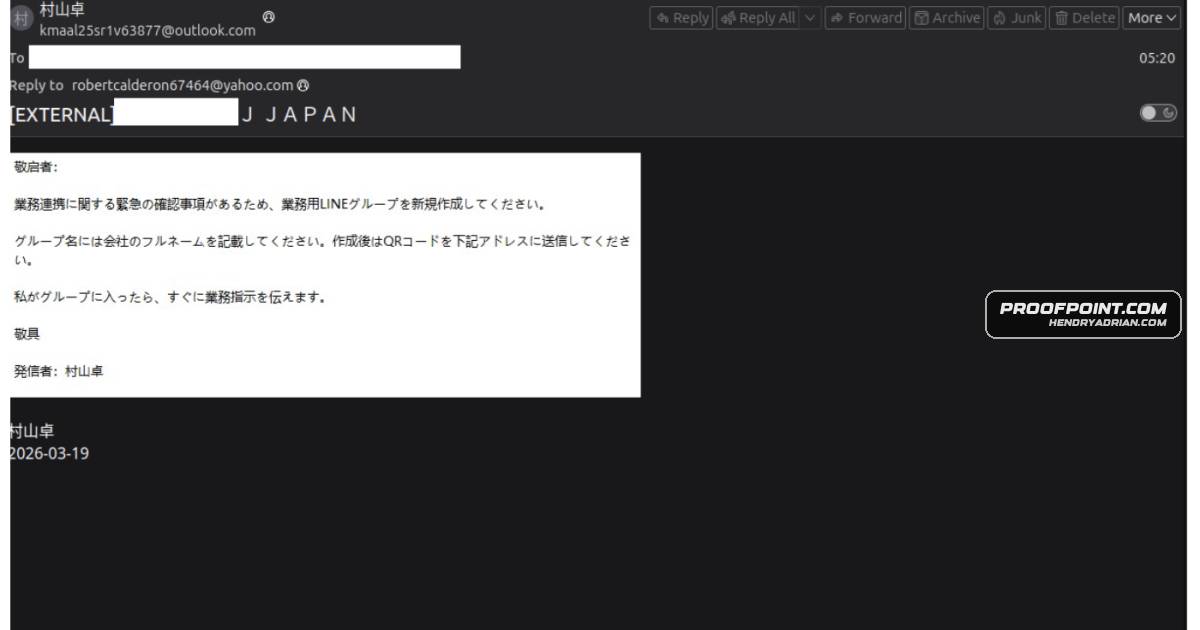
- TA4922 used localized phishing lures about HR, payroll, taxes, benefits, and invoicing to direct recipients to malicious links or attachments, including ZIP, RAR, and IMG files.
- Malware was delivered by pairing legitimate executables with malicious DLLs and using DLL sideloading to install Atlas RAT, RomulusLoader, or SilentRunLoader.
- RomulusLoader downloaded additional payloads and was used to deploy the legitimate RMM software AnyDesk and SyncFuture.
- SilentRunLoader harvested Google Chrome credentials, cookies, and browsing information and exfiltrated data using HTTP POST requests.
- Some campaigns impersonated trusted authorities or internal contacts and attempted to move conversations from email to messaging platforms.
- Defensive Notes
- Enforce application allowlisting on trusted directories.
- Prevent or monitor execution from temporary user-path directories such as %TEMP% and %APPDATA%.
- Monitor for executable files written to system paths or root directories such as C:.
- Prevent or monitor traffic to non-standard or unnecessary ports, including port 1234, for processes that are not allowlisted.
- Enforce least-privilege principles and limit local administrator rights.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | aeya388[.]club | Domain listed as a Winos4.0/ValleyRAT C2 in the malware configuration. |
| DOMAIN | ws[.]ztts88[.]cyou | SilentRunLoader C2 domain used to receive stolen Chrome data. |
| IPV4 | 103[.]214[.]172[.]33 | First-stage infrastructure used in RomulusLoader campaigns to host subsequent payloads. |
| IPV4 | 154[.]211[.]86[.]110 | Atlas RAT C2 IP used by the April 2026 campaigns. |
| IPV4 | 18[.]139[.]83[.]110 | SilentRunLoader data-exfiltration IP associated with its C2 infrastructure. |
| IPV4 | 206[.]238[.]115[.]58 | Atlas RAT C2 IP used by the March 2026 campaign. |
| IPV4 | 43[.]156[.]77[.]97 | RomulusLoader C2 IP observed in campaign network traffic. |
| SHA256 | 0857148fb0bc4aa7adf967ede2307bdb4fc427065d5b6a6db132688a5a8e1eb8 | RomulusLoader/SyncFuture DLL artifact named teamspeak_control.dll. |
| SHA256 | 2d2a251a88632f010fd9671789746908eeccaa5bc5c0a5d25e4649efe4f5b15d | RomulusLoader/SyncFuture executable artifact. |
| SHA256 | 3119cf37b8267db8a2dcd11d9a83d5237d7ef1e42388e7c9afa2831b91da8a2d | RomulusLoader component named vulkan-1.bin. |
| SHA256 | 314f4b59535d1b783e1c20c2be00f9e30f8ed27b2e21fad06a73b47ea43279ef | RomulusLoader/SyncFuture ZIP archive artifact. |
| SHA256 | 40b41979b317406f8abc601677a3b93aaf6ef8ab8ac188b8f383735e388f13b5 | RAR archive delivering RomulusLoader. |
| SHA256 | 4fcfa88fffacbce30bbe2136753c9ab5a4c092940d2406fd9d44d5118e745b9d | HR (2).zip archive delivering Atlas RAT. |
| SHA256 | 584a9448dda46bd590d7a2f86228100d2ae6e0d6d990c1a4459ed5ee28e07ae8 | Atlas RAT DLL artifact listed in the article's IOCs. |
| SHA256 | 66a3836b9a17771bce2161f6b73cbc2494a91e49d6aa30d2d53711e8d10de60d | Paperwork.zip archive delivering Atlas RAT. |
| SHA256 | 8c9b6542f73c5c7fe455b52f5101314407da4f65ff48e7ebf6896605e607c8d0 | RomulusLoader DLL artifact named vulkan-1.dll. |
| SHA256 | 9d0a55c545c4147956db2c2667c4ed931a2875309147548b1dfdd216228f5f73 | SilentRunLoader campaign artifact listed in the article's IOCs. |
| SHA256 | a648db354820ea4d02940cb1702b35974513b7aae83f6dffaacaac4ba31f9295 | ZIP archive delivering Atlas RAT, listed in the article's IOCs. |
| SHA256 | de82998ad5fcd63deae030803388e0fb4290d6223fda82368fd25b99b823f0d2 | SilentRunLoader ZIP artifact listed in the article's IOCs. |
| SHA256 | e0a6a71c605d9a4076147e9537f82f79f1e1eccadc874595160aa4637ff4088c | SilentRunLoader executable hash listed in the article's IOCs. |
| URL | hxxps[:]//nwphotoblog[.]com | Campaign URL hosting a landing page with a download button in a RomulusLoader/SyncFuture campaign. |
| URL | hxxps[:]//ws[.]ztts88[.]cyou/file/cg[.]exe | SilentRunLoader download URL for the next-stage executable. |
| URL | hxxps[:]//ws[.]ztts88[.]cyou/upload[.]php | SilentRunLoader data-exfiltration endpoint. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe malware used encrypted or encoded payloads and configuration data, including RC4-encrypted blobs and XOR-encoded content.T1036 · MasqueradingCampaigns impersonated HR, tax, and business communications; RomulusLoader components also masqueraded as Vulkan Loader components.T1055 · Process InjectionRomulusLoader injected worker code into other processes; Atlas RAT also supported DLL injection into WeChat.exe.T1056.001 · KeyloggingAtlas RAT includes keylogger functionality.T1057 · Process DiscoveryAtlas RAT checks whether named processes are running.T1071.001 · Web ProtocolsRomulusLoader communicates with C2 over HTTP, and SilentRunLoader exfiltrates data using HTTP POST requests.T1082 · System Information DiscoveryAtlas RAT collects system information and sends it to its C2.T1105 · Ingress Tool TransferRomulusLoader retrieved additional payloads from C2 infrastructure, and SilentRunLoader downloaded a next-stage executable.T1113 · Screen CaptureAtlas RAT includes screenshot capture capability.T1140 · Deobfuscate/Decode Files or InformationMalware decoded or decrypted embedded payloads and configuration data, then decompressed RomulusLoader payloads.T1204.001 · Malicious LinkLures urged recipients to click links or open downloaded archives to launch malware.T1497.001 · System ChecksAtlas RAT checks for sandbox, container, and virtual-machine indicators, including specific usernames, services, devices, and registry keys.T1566.001 · Spearphishing AttachmentTA4922 delivered malware through phishing attachments, including malicious ZIP archives containing executables and DLLs.T1566.002 · Spearphishing LinkPhishing emails embedded links to landing pages or file-sharing services hosting payload archives.T1574.002 · DLL Side-LoadingAtlas RAT, RomulusLoader, and SilentRunLoader were installed by sideloading malicious DLLs alongside legitimate executables.
Threat Actors
Malware
Atlas RATTA4922 is a highly active Chinese-speaking threat actor that has evolved its toolkit to include Atlas RAT, RomulusLoader, SilentRunLoader, and ValleyRAT/Winos4.0 while using regional HR, payroll, tax, and invoicingHoldingHandsThe actor has been historically associated with malware families including Winos4.0 (sometimes referred to as ValleyRAT) and HoldingHands.RomulusLoaderis a highly active Chinese-speaking threat actor that has evolved its toolkit to include Atlas RAT, RomulusLoader, SilentRunLoader, and ValleyRAT/Winos4.0 while using regional HR, payroll, tax, and invoicing lures toSilentRunLoaderChinese-speaking threat actor that has evolved its toolkit to include Atlas RAT, RomulusLoader, SilentRunLoader, and ValleyRAT/Winos4.0 while using regional HR, payroll, tax, and invoicing lures to targetValleyRATthreat actor that has evolved its toolkit to include Atlas RAT, RomulusLoader, SilentRunLoader, and ValleyRAT/Winos4.0 while using regional HR, payroll, tax, and invoicing lures to target organizations across EastWinos4.0actor that has evolved its toolkit to include Atlas RAT, RomulusLoader, SilentRunLoader, and ValleyRAT/Winos4.0 while using regional HR, payroll, tax, and invoicing lures to target organizations across East Asia,
Products
AnyDeskThe group combines DLL sideloading, cloud hosting, trusted tools like AnyDesk and SyncFuture, and credential theft or exfiltration to support financially motivated access and fraud campaigns.Google ChromeUpon execution, the payload installed SilentRunLoader which harvested sensitive data from Google Chrome including stored credentials, cookies, and browsing information.SyncFutureThe group combines DLL sideloading, cloud hosting, trusted tools like AnyDesk and SyncFuture, and credential theft or exfiltration to support financially motivated access and fraud campaigns.WeChat[T1055] Process Injection – RomulusLoader injected workers into other processes and Atlas RAT supported DLL injection into WeChat.exe (‘injected into other processes’, ‘injects DLL into WeChat.exe’).
Tools
CyberChefHere is a Cyberchef recipe that can be used to decrypt this config: SysWhispers3. The malware uses direct syscalls via SysWhispers to allocate memory for the shellcode and execute it. The shellcode is a small, encrypted blob in the DLL which resolves Windows API function addresses it requires to
Countries
GermanyTargeting initially focused on Japan and other parts of Asia, but expanded in 2026 to the U.K., Germany, Italy, South Africa, and other regions.IndiaCampaigns mostly target organizations in Japan, with additional targeting in Asia including Taiwan, Korea, Singapore, and India.IndonesiaTA4922 most frequently targets organizations in Japan, Taiwan, India, Malaysia, Singapore, Indonesia, and occasionally European countries such as Germany and the United Kingdom.ItalyTargeting initially focused on Japan and other parts of Asia, but expanded in 2026 to the U.K., Germany, Italy, South Africa, and other regions.JapanTargeting initially focused on Japan and other parts of Asia, but expanded in 2026 to the U.K., Germany, Italy, South Africa, and other regions.KoreaCampaigns mostly target organizations in Japan, with additional targeting in Asia including Taiwan, Korea, Singapore, and India.MalaysiaTA4922 most frequently targets organizations in Japan, Taiwan, India, Malaysia, Singapore, Indonesia, and occasionally European countries such as Germany and the United Kingdom.SingaporeCampaigns mostly target organizations in Japan, with additional targeting in Asia including Taiwan, Korea, Singapore, and India.South AfricaTargeting initially focused on Japan and other parts of Asia, but expanded in 2026 to the U.K., Germany, Italy, South Africa, and other regions.TaiwanCampaigns mostly target organizations in Japan, with additional targeting in Asia including Taiwan, Korea, Singapore, and India.United KingdomTA4922 most frequently targets organizations in Japan, Taiwan, India, Malaysia, Singapore, Indonesia, and occasionally European countries such as Germany and the United Kingdom.