
Fake Software Download Sites Hijack Clicks to Deliver Three Malware Families
Summary
Check Point Research found 100+ fake software-project sites that intercept download clicks and route users through a gated TDS, which delivered SessionGate, RemusStealer, and AnimateClipper in observed chains.
Key points
- Researchers identified more than 100 active sites impersonating open-source and freeware projects, including tools used by security researchers.
- CloudFront-hosted scripts intercepted eligible download clicks and routed users through a TDS with anti-bot checks, VPN/datacenter filtering, and other session-based gates.
- SessionGate is a multi-stage loader with obfuscation and server-side key gating; researchers observed it delivering potentially unwanted applications.
- RemusStealer uses server-directed tasks to collect browser data, files, registry information, clipboard contents, and, when enabled, screenshots. Captured tasking included 332 browser extension identifiers.
- AnimateClipper was delivered through a ClickFix-style chain and resolved its command-and-control domain through a BNB Smart Chain smart contract before replacing copied cryptocurrency addresses.
- Observed redirect branches also led to benign software and potentially unwanted applications; researchers assessed traffic acquisition and monetization as a likely primary purpose of the broader operation.
Article Details
- Attack Vectors
- Lookalike websites impersonating open-source and freeware projects intercepted the first eligible download click and routed users through a gated Traffic Distribution System (TDS).
- The TDS applied first-visit and click-confirmation checks, anti-bot logic, VPN/datacenter filtering, browser and session context, and frequency capping to select redirect outcomes.
- SessionGate samples were delivered through landing pages using per-session URLs and server-side validation; the loader used decoy installer behavior and environmental checks to gate delivery.
- RemusStealer was delivered through a redirect chain and a password-protected archive; its loader manually mapped an embedded payload and accepted server-driven collection tasks.
- An AnimateClipper chain used a ClickFix-style page to prompt execution of mshta.exe, followed by obfuscated VBScript and PowerShell stages, in-memory shellcode execution, and payload loading.
- Defensive Notes
- Do not rely on search ranking, polished site design, or a visible download-link destination as proof that a project site is legitimate; the article reports that click handling could redirect users despite a legitimate-looking href.
- Review endpoint and network telemetry for mshta.exe retrieving remote content, obfuscated PowerShell, and suspicious HTTP/HTTPS connections and payload downloads.
- The article identifies the listed malware hashes and infrastructure as campaign indicators that defenders can use for investigation and detection.
- Check Point states that Threat Emulation and Harmony Endpoint provide coverage for the tactics, file types, and operating systems described in the report.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | appfreshstart[.]com | SessionGate C2 domain used for loader check-in and payload requests. |
| DOMAIN | appgetonline[.]com | Domain identified in related SessionGate campaigns as C2 infrastructure. |
| DOMAIN | appmakingcenter[.]com | SessionGate C2 domain used by the decrypted module to retrieve configuration. |
| DOMAIN | file-enter-web[.]com | Intermediate gate in an observed redirect chain leading to payload delivery infrastructure. |
| DOMAIN | getfluxfile[.]com | Landing page observed delivering SessionGate samples. |
| DOMAIN | kr[.]hugo-lapp[.]co | AnimateClipper C2 domain resolved by querying a smart contract. |
| DOMAIN | mobileversioncrc[.]com | Domain identified as a SessionGate CRC C2 variant. |
| DOMAIN | oundhertobeconsist[.]org | Dynamic post-click redirector used in the campaign's TDS chain. |
| DOMAIN | trkscope[.]xyz | Intermediate redirect infrastructure in an observed TDS chain. |
| DOMAIN | webinnosetup[.]com | Domain identified in related SessionGate campaigns as C2 infrastructure. |
| DOMAIN | yourfastcrc[.]com | SessionGate CRC C2 domain used to return key material for the loader. |
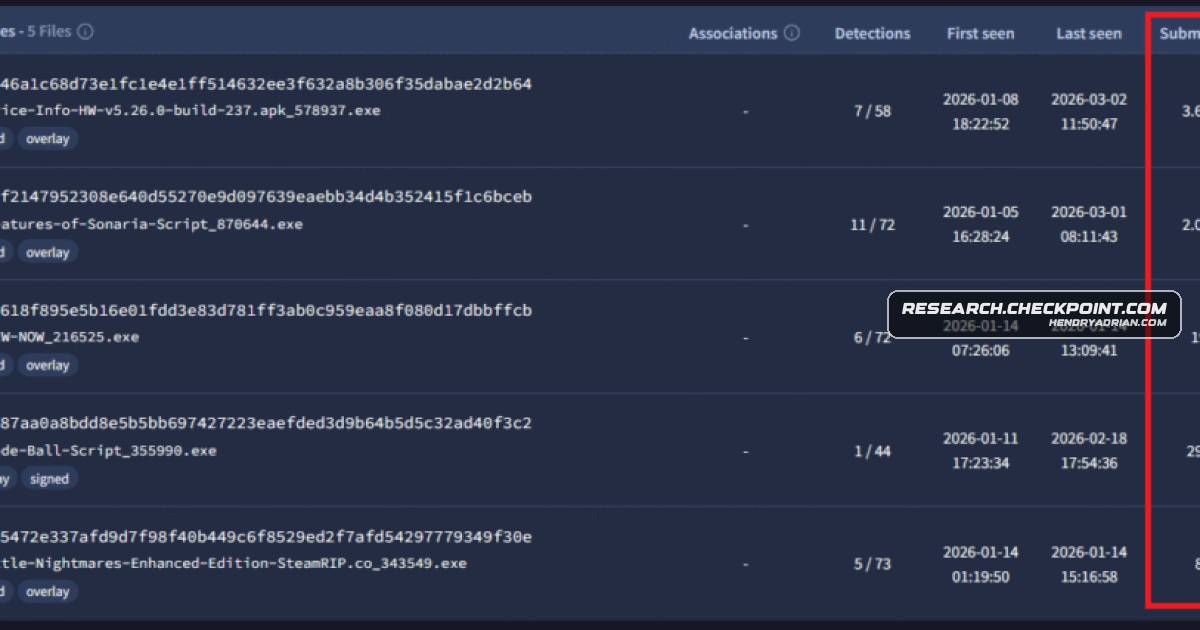
| SHA256 | 15e6df0c95f2147952308e640d55270e9d097639eaebb34d4b352415f1c6bceb | Hash identified in the article for a SessionGate Stage 1 sample. |
| SHA256 | 26f2abfc254a59c2386dd46dca16744f7147a0f0366cb6008e1d53219175f44c | Hash identified in the article for a SessionGate Stage 2 DLL #2 sample. |
| SHA256 | 2e842eab0c16ddd1a2ec4a56610adb58d115b65a1e08e9b67e7e375f8eed0873 | Hash identified in the article for a RemusStealer sample. |
| SHA256 | 39dc2327fe1e5a56ac5ad9dc02f0386cff3d83dcfdc558cacba42ebb9dcc5ec2 | Hash identified in the article for a RemusStealer sample. |
| SHA256 | 3bb92771e287aa0a8bdd8e5b5bb697427223eaefded3d9b64b5d5c32ad40f3c2 | Hash identified in the article for a SessionGate Stage 1 sample. |
| SHA256 | 4cdb1f7ac502289119f7f8256f00baaa994e6ecfb4000dcf5e1c46073508fcb3 | Hash identified in the article for a SessionGate Stage 2 sample. |
| SHA256 | 598b023e56c45b19173e8f96c1c88036d732fec305cf6bf1b9cf4dbe304beb7f | Hash identified in the article for a SessionGate Stage 1 sample. |
| SHA256 | 74091f5a8746a1c68d73e1fc1e4e1ff514632ee3f632a8b306f35dabae2d2b64 | Hash identified in the article for a SessionGate Stage 1 sample. |
| SHA256 | 87361ba2bb412dcf49f8738f3b8b9b7dccb557ad2e76ea8d98ffa5b098ae3886 | Hash identified in the article for an AnimateClipper sample. |
| SHA256 | cbad672d9bd06ce91ce465d049e50696fbaec9d209ca0ab1fd814d993d04bc9b | Hash identified for SessionGate Stage 1 and Stage 2 DLL #1 samples. |
| SHA256 | ce0888df5e28716432013a8ae002437bd3e993fbe8362c5ff9efbddabfe0ab77 | Hash identified in the article for a SessionGate Stage 2 DLL #1 sample. |
| SHA256 | e6a1a428a7c09c9946f7c0179d89b263f442dc3208b5144a9146c200e4185bd6 | Hash identified in the article for an AnimateClipper sample. |
| URL | hxxp[:]//194[.]150[.]220[.]218/4SLEYpfAk57hGubo/fo0suc2ki2.rtf | AnimateClipper chain URL serving an obfuscated PowerShell stage disguised with an RTF extension. |
| URL | hxxp[:]//baxe[.]pics:48261 | Fallback RemusStealer C2 endpoint listed in the article. |
| URL | hxxp[:]//buccstanor[.]pics:28313 | Primary RemusStealer C2 endpoint listed in the article. |
| URL | hxxps[:]//185[.]0xa1[.]0xfb[.]58/navy.7z | AnimateClipper chain URL used by the ClickFix instruction to retrieve an HTA disguised with an archive extension. |
| URL | hxxps[:]//cdn-1415[.]brightcanvas[.]digital/fo0suc2ki2.rtf | AnimateClipper chain URL serving a ZIP-based loader disguised with an RTF extension. |
| URL | hxxps[:]//s3[.]us-east-2[.]amazonaws[.]com/marketstagofortdas/ehjm145uvt/Download_Ready_461049.exe | SessionGate executable payload URL identified in the article. |
| URL | hxxps[:]//s3[.]us-east-2[.]amazonaws[.]com/marketstagofortdas/ehjm145uvt/Download_Ready_461049.html?utm_source=partner_consent | SessionGate per-session landing-page URL identified as part of the sample delivery chain. |
MITRE ATT&CK
T1005 · Data from Local SystemRemusStealer collected local browser databases, profile files, and files selected by server-provided search rules.T1027 · Obfuscated Files or InformationThe analyzed loaders and payloads used encrypted strings or modules, junk code, opaque predicates, and other obfuscation.T1036 · MasqueradingThe campaign used professionally built websites impersonating legitimate open-source and freeware project portals.T1041 · Exfiltration Over C2 ChannelRemusStealer uploaded collected browser, file, registry, clipboard, and screenshot artifacts to its C2.T1057 · Process DiscoverySessionGate enumerated running processes using Toolhelp-based scanning as part of its environment checks.T1059.001 · PowerShellAn AnimateClipper delivery stage retrieved and ran an obfuscated PowerShell script.T1071.001 · Web ProtocolsSessionGate and RemusStealer communicated with C2 endpoints over HTTP or HTTPS.T1105 · Ingress Tool TransferThe loaders downloaded additional payloads and modules from remote infrastructure before execution.T1115 · Clipboard DataRemusStealer captured clipboard text, while AnimateClipper replaced copied cryptocurrency addresses in the clipboard.T1140 · Deobfuscate/Decode Files or InformationThe malware decrypted configuration, embedded modules, and payload data before using or executing them.T1204.001 · Malicious LinkThe TDS handoff depended on a user clicking a seemingly legitimate download link or button.T1218.005 · MshtaThe ClickFix page instructed victims to use mshta.exe to run remote HTA content.T1497.001 · System ChecksSessionGate checked services, processes, registry settings, and Windows edition before proceeding with malicious delivery.T1518 · Software DiscoverySessionGate checked for security-related services and Windows Defender PUA/PUS registry settings.T1555.003 · Credentials from Web BrowsersRemusStealer collected browser login data and related credential stores, including Chromium Login Data and Firefox logins.json.
Malware
AnimateClipperThe same infrastructure was used to deliver SessionGate, RemusStealer, and AnimateClipper, showing that the operation mixed traffic monetization with downstream malware delivery.RemusStealerThe same infrastructure was used to deliver SessionGate, RemusStealer, and AnimateClipper, showing that the operation mixed traffic monetization with downstream malware delivery.SessionGateThe same infrastructure was used to deliver SessionGate, RemusStealer, and AnimateClipper, showing that the operation mixed traffic monetization with downstream malware delivery.
Vendors
Products
7-ZipDownloader with a built-in decoy: embedded 7-Zip SFX contentCheck Point Threat EmulationCheck Point Threat Emulation and Harmony Endpoint provide comprehensive coverage of attack tactics, file types, and operating systems and protect against the attacks and threats described in this report.Harmony EndpointCheck Point Threat Emulation and Harmony Endpoint provide comprehensive coverage of attack tactics, file types, and operating systems and protect against the attacks and threats described in this report.
Tools
dnSpya large-scale campaign that impersonates trusted open-source and freeware projects such as Ghidra, dnSpy, and SpiderFoot to hijack download clicks and route users through a gated Traffic Distribution System.Ghidraexposed a large-scale campaign that impersonates trusted open-source and freeware projects such as Ghidra, dnSpy, and SpiderFoot to hijack download clicks and route users through a gated Traffic DistributionSpiderFootcampaign that impersonates trusted open-source and freeware projects such as Ghidra, dnSpy, and SpiderFoot to hijack download clicks and route users through a gated Traffic Distribution System.