
ThreatsDay Roundup: Attackers Abuse Trusted Platforms to Deliver Malware and Steal Credentials
Summary
The roundup covers attacks abusing browser extensions, AI chat features, developer tools, and OAuth flows, alongside a Cisco SD-WAN zero-day update, npm supply-chain threats, and new security policies.
Key points
- Twenty-three deceptive Chrome extensions hijacked searches and routed queries through monetization brokers; researchers estimated about 758,000 affected users.
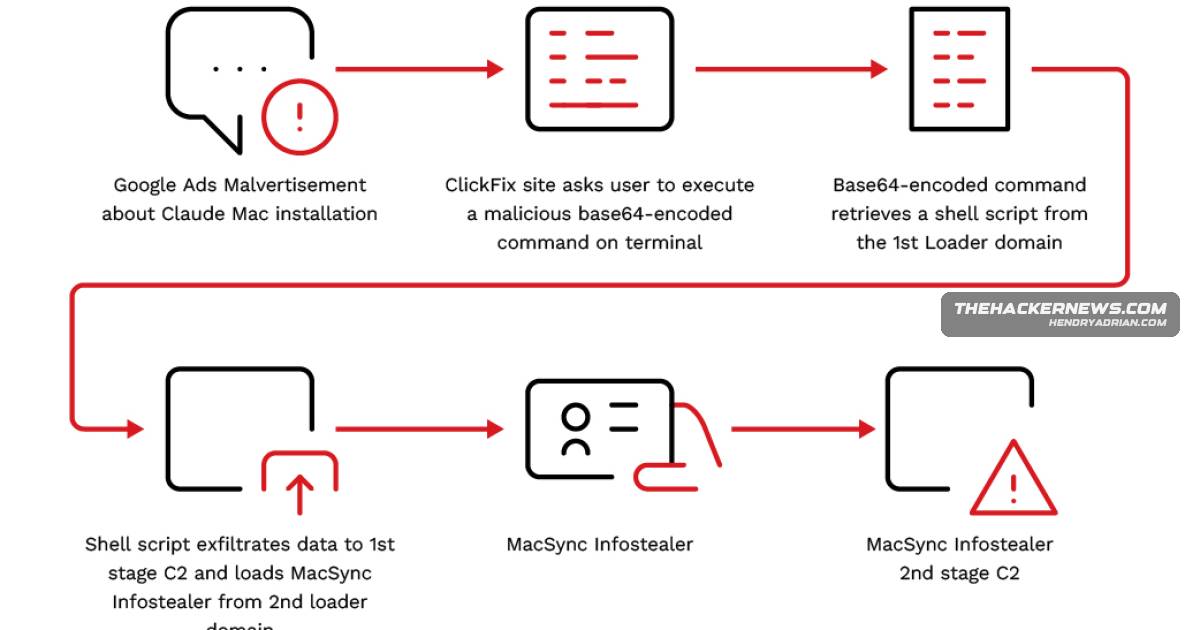
- ClickFix campaigns delivered the Meow (DEBUG) macOS infostealer and MacSync through Claude shared chats. Anthropic disabled malicious conversations and banned the responsible accounts.
- Cisco says CVE-2026-20127 also affects Catalyst SD-WAN Validator; the unauthenticated privilege-escalation flaw has reportedly been exploited as a zero-day since 2023 by UAT-8616.
- Three npm packages were found dropping NastyC2, a Rust post-exploitation framework with more than 80 commands. Another malicious package delivered a worm, a Monero miner, and a Dirty Frag privilege-escalation exploit.
- A Microsoft 365 phishing campaign abused the legitimate OAuth device authorization flow to authorize attacker-controlled devices; malicious repositories were also reported to trick the Cline coding agent into running shell commands.
- CISA's BOD 26-04 requires federal agencies to remediate certain high-risk vulnerabilities on accelerated timelines, potentially within three days. France's ANSSI set quantum-resistance requirements for security products starting in 2027.
Article Details
- Event Type
- Cybersecurity threat and security-development roundup
- Impact
- Reported activity includes malware delivery and credential theft through deceptive browser extensions, AI chat links, phishing, malicious npm packages, and compromised Steam Workshop content. Other reported risks include account takeover, data theft, unauthorized access through a vulnerable Cisco SD-WAN product, and exploitation of exposed or vulnerable systems. The article also reports privacy risks from search-query routing and security consequences from unreliable cloud audit telemetry.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | ipelc[.]gob[.]bo | Compromised Bolivian government website hosting a Boots phishing payload. |
MITRE ATT&CK
T1003.006 · DCSyncNastyC2 was reported to include DCSync capability.T1055 · Process InjectionNastyC2 was reported to support multiple process-injection techniques.T1056.001 · KeyloggingPhantom Stealer and OnyxC2 were reported to collect keystrokes.T1059.002 · AppleScriptThe macOS ClickFix chain executed a second-stage AppleScript through osascript.T1071.001 · Web ProtocolsOnyxC2 was reported to provide a reverse shell over HTTP.T1204.002 · Malicious FileThe reported campaigns relied on victims opening malicious attachments or running compromised wallpaper packages.T1555.001 · KeychainMeow (DEBUG) was reported to harvest macOS keychain contents.T1555.003 · Credentials from Web BrowsersReported stealers harvest credentials from web browsers.T1558.003 · KerberoastingNastyC2 was reported to include Kerberoasting capability.T1566.001 · Spearphishing AttachmentPhantom Stealer and AsynRAT campaigns used phishing emails with malicious attachments.T1620 · Reflective Code LoadingNastyC2 was reported to support reflective DLL loading.
CVE
CVE-2026-20127Cisco has updated its February 2026 advisory for CVE-2026-20127, a critical privilege escalation flaw in Catalyst SD-WAN Controller and Catalyst SD-WAN Manager, to note that the vulnerability also affects CatalystCVE-2026-49975Formally tracked as CVE-2026-49975, the vulnerability ironically chains together two features that were expressly designed to save internet bandwidth to help attackers amplify junk traffic by orders of magnitude.
People
Art UkshiniSecurity researcher quoted on the GCP serviceData telemetry inconsistency and its security risks.Ax SharmaHead of research at Manifold Security, quoted on the Cline AI coding-agent trust-bypass findings.CalifUsed OpenAI's Codex to discover the HTTP/2 Bomb exploit, according to the article.Jean-Marie R.Security researcher quoted on the discovery and risks of deceptive Chrome extensions.Robert SimmonsSecurity researcher quoted describing the Microsoft 365 device-code phishing campaign.
Threat Actors
ContiA ransomware group whose operators were reported to have infected more than 1,000 computers and networks and extorted victims; Oleksii Lytvynenko admitted joining its conspiracy.GhostwriterCERT Polska reported that the Belarus-aligned group ran phishing campaigns targeting Gmail users and seeking to steal credentials, including 2FA credentials.OldphantomoftheoperaA threat actor operating under this alias was reported to sell Phantom Stealer through a subscription model.Oleksii Oleksiyovych LytvynenkoHe pleaded guilty to wire fraud conspiracy in connection with Conti, admitted participating in its ransomware conspiracy and possessing stolen victim data, and was directed to work on a loader.UAT-8616The article reports that this threat actor exploited CVE-2026-20127 as a zero-day against Cisco SD-WAN products since 2023.
Malware
AsynRAT#WindowsServer2025CGrabberAn active campaign is leveraging a multi-stage loader called OnionDrop to deliver malware families like LegionLoader (aka CurlyGate), CGrabber, and Vidar Stealer.clay_Clientdeploying AutoHotkey-based loaders that reflectively inject a .NET remote access trojan [named clay_Client] and AsynRAT into memory for command-and-control communication and follow-on execution.”Conti#WindowsServer2025Legion LoaderAn active campaign is leveraging a multi-stage loader called OnionDrop to deliver malware families like LegionLoader (aka CurlyGate), CGrabber, and Vidar Stealer.LegionLoaderAn active campaign is leveraging a multi-stage loader called OnionDrop to deliver malware families like LegionLoader (aka CurlyGate), CGrabber, and Vidar Stealer.MacSync#WindowsServer2025Meow (DEBUG)A fileless macOS ClickFix chain delivered the Meow (DEBUG) infostealer in memory.NastyC2Windows, and macOS systems to deliver a previously undocumented post-exploitation framework codenamed NastyC2.OnionDrop#WindowsServer2025OnyxC2#WindowsServer2025PhantomStealerAn active phishing campaign is targeting banks to deliver Phantom Stealer, an infostealer that’s sold under a subscription model for between $70 to $240 by a threat actor operating under the alias Oldphantomoftheopera.Shai-HuludIt also highlights major security developments such as Windows Server 2025 DoH, a Cisco SD-WAN zero-day exploited by UAT-8616, and supply chain threats involving npm packages and the Shai-Hulud worm.VidarAn active campaign is leveraging a multi-stage loader called OnionDrop to deliver malware families like LegionLoader (aka CurlyGate), CGrabber, and Vidar Stealer.
Vendors
Amazon Web ServicesAmazon Web Services (AWS) has announced a new artificial intelligence (AI)-powered security agent called AWS Continuum for code vulnerabilities, as models like Claude Mythos by attackers and defenders accelerate theAnthropicIn another ClickFix campaign, threat actors have been spotted weaponizing Anthropic Claude’s shared chat feature, abusing the trust associated with a legitimate domain to deliver the MacSync credential-stealing malware.CiscoIt also highlights major security developments such as Windows Server 2025 DoH, a Cisco SD-WAN zero-day exploited by UAT-8616, and supply chain threats involving npm packages and the Shai-Hulud worm.GoogleClaude shared chat abuse and Google Ads were used to spread MacSync malware.MicrosoftMicrosoft has announced that DNS-over-HTTPS (DoH) for Windows DNS Server is generally available on Windows Server 2025 for client-to-server DNS traffic. “With general availability, organizations can now deploy encrypted
Products
AWS ContinuumWeb Services (AWS) has announced a new artificial intelligence (AI)-powered security agent called AWS Continuum for code vulnerabilities, as models like Claude Mythos by attackers and defenders accelerate theCatalyst SD-WAN ValidatorSD-WAN Controller and Catalyst SD-WAN Manager, to note that the vulnerability also affects Catalyst SD-WAN Validator.Cisco Catalyst SD-WAN Controllerupdated its February 2026 advisory for CVE-2026-20127, a critical privilege escalation flaw in Catalyst SD-WAN Controller and Catalyst SD-WAN Manager, to note that the vulnerability also affects Catalyst SD-WANCisco Catalyst SD-WAN Managerfor CVE-2026-20127, a critical privilege escalation flaw in Catalyst SD-WAN Controller and Catalyst SD-WAN Manager, to note that the vulnerability also affects Catalyst SD-WAN Validator.Claude#WindowsServer2025Cline#WindowsServer2025Google ChromeDeceptive Chrome extensions hijacked searches and routed users through monetization brokers.Microsoft 365 Apps for EnterpriseReversingLabs has detailed a Microsoft 365 device code phishing campaign that makes use of Microsoft’s legitimate OAuth 2.0 Device Authorization Grant flow to obtain access to victim accounts.SteamThreat actors abused npm, Steam Workshop, and AI coding tools to deploy loaders, stealers, and backdoors.VS CodeManifold Security has flagged two high-severity local code-execution paths on a developer’s machine via a malicious repository in Cline, an AI coding agent VS Code extension with more than 4.3 million installs.Wallpaper Engine“To pull this off, they are exploiting Wallpaper Engine – a popular live wallpaper app available on Steam – specifically leveraging its Workshop sharing feature.Windows Server 2025It also highlights major security developments such as Windows Server 2025 DoH, a Cisco SD-WAN zero-day exploited by UAT-8616, and supply chain threats involving npm packages and the Shai-Hulud worm.
Tools
Countries
BelarusBelarus-linked Gmail phishing surgeChinagovernment’s decision to restrict Anthropic’s Claude Fable 5 and Mythos 5 models came after it ordered the AI company to revoke South Korea-based SK Telecom’s access over its alleged ties to China.RussiaAccording to local media reports, Estonia plans to implement additional security screening for emails sent from Russia’s .ru top-level domain before they reach government officials, citing heightened cyber risk.TaiwanAsia-Pacific region bore the brunt of the campaign, accounting for 67.2% of all confirmed victims, with Taiwan alone representing 30.5% of total traffic, a concentration that points to deliberate geographic ad
Industries
business servicesobserved targeting victims mainly in Asia, North America, and Oceania across technology, media, and business services sectors using ClickFix lures to deliver an AppleScript-based infostealer to macOS users.Communicationsphishing campaigns targeting Gmail users through bogus messages designed to imitate official Gmail communications and trick recipients into clicking on malicious URLs that harvest their credentials.GamingFTP clients, and 5 email clients, with a further set of VPN, remote access, messaging, note-taking, and gaming targets.” A premium subscription is available for $500 per month.Governmentgovernment’s decision to restrict Anthropic’s Claude Fable 5 and Mythos 5 models came after it ordered the AI company to revoke South Korea-based SK Telecom’s access over its alleged ties to China.Healthcare“Exposure in this set is led by communication services at 24.9% of observed assets, with information technology contributing 18.0% and healthcare close behind at 17.0%,” CyCognito said.Information Technology“Exposure in this set is led by communication services at 24.9% of observed assets, with information technology contributing 18.0% and healthcare close behind at 17.0%,” CyCognito said.Mediahas been observed targeting victims mainly in Asia, North America, and Oceania across technology, media, and business services sectors using ClickFix lures to deliver an AppleScript-based infostealer to macOSTechnologyattacker has been observed targeting victims mainly in Asia, North America, and Oceania across technology, media, and business services sectors using ClickFix lures to deliver an AppleScript-based infostealer