Malspam Campaign Delivers Fileless .NET Loader That Disables Windows Defenses
Summary
Huntress details a malspam infection chain that uses personalized lures and multi-stage PowerShell and .NET loaders to evade analysis, tamper with Windows defenses, persist, and inject payloads. The malware attribution was corrected to an unidentified .NET loader.
Key points
- A malicious HTML attachment redirected recipients through a trusted ad-tracking service to a personalized lure and ZIP-delivered JavaScript loader.
- The multi-stage chain uses JScript, obfuscated PowerShell, and reflective .NET loading, with much of its execution occurring in memory.
- The loader checks for virtual machines, sandboxes, debuggers, and analysis tools; some detections trigger file cleanup or a system reboot.
- It tampers with Microsoft Defender, AMSI, and ETW, and uses RunPE process hollowing to inject payloads into trusted Windows processes such as InstallUtil.exe or MSBuild.exe.
- Persistence mechanisms include registry Run and RunOnce entries, Startup-folder copies, and scheduled tasks.
- The loader profiles systems, retrieves additional payloads from command-and-control infrastructure, and can execute them through in-memory injection, PowerShell, or file-drop modes.
- Huntress corrected its initial DesckVB RAT attribution; its current assessment is an unidentified .NET loader. Recommended defenses include attachment and link sandboxing, script-file controls, and monitoring for script-launched obfuscated PowerShell.
Article Details
- Attack Vectors
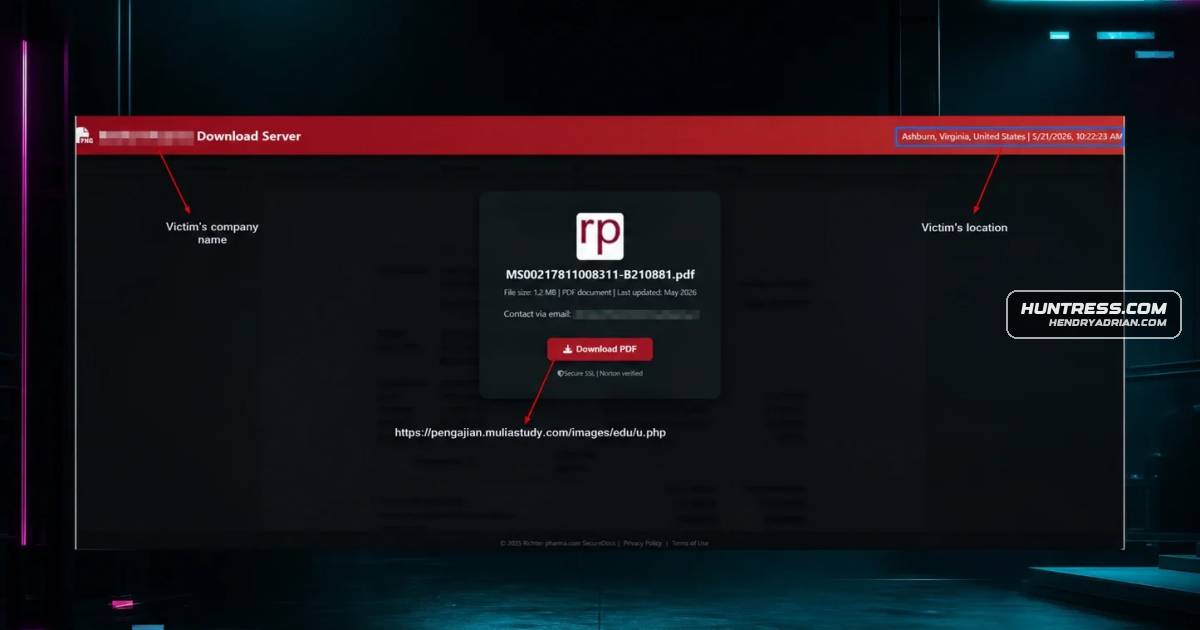
- A malspam email delivered a malicious HTML attachment that redirected the recipient through DoubleClick to a redirector and a personalized delivery kit.
- Clicking the kit's download button caused it to POST the recipient's email address and retrieve a ZIP archive containing a JScript loader.
- The JScript loader staged obfuscated PowerShell, which retrieved further components and reflectively loaded .NET assemblies.
- The loader used RunPE process hollowing to execute payloads in processes including InstallUtil.exe and MSBuild.exe.
- Defensive Notes
- Configure policy to open .js, .vbs, and .hta files in Notepad or Notepad++ by default, and monitor for script files launched by explorer.exe or wscript.exe spawning encoded PowerShell.
- Use email-gateway sandboxing for attachments and links; consider blocking or quarantining script-based and macro-enabled attachments.
- Deploy SPF, DKIM, and DMARC, and conduct phishing-awareness training.
- Monitor for Defender exclusions or protection changes, AMSI and ETW tampering, suspicious Run and RunOnce entries, scheduled tasks, and unexpected process hollowing into InstallUtil.exe or MSBuild.exe.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | afxwd[.]ddns[.]net | Listed in the article's indicators as loader-related infrastructure. |
| DOMAIN | andrefelipedonascime1778799406970[.]2241107[.]meusitehostgator[.]com[.]br | Attacker-used host serving loader staging files. |
| DOMAIN | bth[.]startthewave[.]org | Host serving the personalized malspam delivery kit. |
| DOMAIN | catalogo[.]castrouria[.]com | Attacker-used payload-delivery host serving bl.txt. |
| DOMAIN | fostercareintheus[.]optimizationprime[.]com | Redirector stage in the malicious delivery chain. |
| DOMAIN | xtadts[.]ddns[.]net | Loader C2 server listed in the article's indicators. |
| SHA256 | c356aff1a01c2b0da472e584c8e3c8f875b9a24280435d42836a77b19f5a8c18 | SHA-256 certificate pin embedded in the loader for C2 server identity validation. |
| SHA256 | c61b1941cf756eb7551f7c661743802362728b785adc22e860d269713dfb01a6 | SHA-256 certificate pin embedded in the loader for C2 server identity validation. |
| SHA256 | d5b7247c497788cf0031ceb06e3df77a45fef59f1e49633dc7159816d64759b5 | SHA-256 certificate pin embedded in the loader for C2 server identity validation. |
| SHA256 | e91fb249aa97be5c7931e430781167edfe7ba804720b5f643e6ab70b7e6e74dd | SHA-256 certificate pin embedded in the loader for C2 server identity validation. |
| SHA256 | f1c3ebe78bd8c38559bf3cfcc9a9fa37d221e31780774a3787e26160a61f5348 | SHA-256 certificate pin embedded in the loader for C2 server identity validation. |
| URL | hxxp[:]//catalogo[.]castrouria[.]com/c84da/bl.txt | Malicious URL serving the packed loader payload. |
| URL | hxxps[:]//andrefelipedonascime1778799406970[.]2241107[.]meusitehostgator[.]com[.]br/GpazlLUWIJ_14_05_Meus_ArquivosDeTexto/01.txt | Malicious URL for a downloaded RunPE injector component. |
| URL | hxxps[:]//andrefelipedonascime1778799406970[.]2241107[.]meusitehostgator[.]com[.]br/GpazlLUWIJ_14_05_Meus_ArquivosDeTexto/02.txt | Malicious URL for a downloaded PowerShell template component. |
| URL | hxxps[:]//andrefelipedonascime1778799406970[.]2241107[.]meusitehostgator[.]com[.]br/GpazlLUWIJ_14_05_Meus_ArquivosDeTexto/03.txt | Malicious staging URL used to retrieve the .NET loader. |
| URL | hxxps[:]//pengajian[.]muliastudy[.]com/images/edu/u.php | Malicious delivery endpoint that serves the ZIP archive after the kit submits the recipient's email. |
MITRE ATT&CK
T1012 · Query RegistryThe loader read registry values for GPU details and checked BIOS registry values for virtualization indicators.T1027 · Obfuscated Files or InformationThe chain used junk padding, obfuscated strings, encoded scripts, encryption, and layered packing to hinder analysis and detection.T1053.005 · Scheduled TaskThe loader created scheduled tasks, including a repeating task to restart it if terminated.T1055.012 · Process HollowingThe RunPE components hollowed target processes by creating them suspended, replacing their image, and resuming execution.T1057 · Process DiscoveryThe scripts and loader enumerated running processes to identify security and analysis tools.T1059.001 · PowerShellThe chain used obfuscated PowerShell to stage and execute further components.T1059.007 · JavaScriptThe JScript loader ran through WScript.exe.T1082 · System Information DiscoveryThe loader collected system and hardware details through WMI, including processor, disk, baseboard, video-controller, and operating-system information.T1095 · Non-Application Layer ProtocolThe loader communicated with its C2 over raw TCP sockets.T1105 · Ingress Tool TransferThe loader downloaded staged files and additional payloads from remote URLs and the C2.T1204.002 · Malicious FileThe victim had to interact with the lure and its download button to obtain the ZIP containing the JScript loader.T1218.004 · InstallUtilInstallUtil.exe was identified as a configurable signed-binary execution target for the payload.T1497.001 · System ChecksThe loader checked for virtual machines, sandboxes, debugging, and analysis tooling and stopped or cleaned up when detected.T1518.001 · Security Software DiscoveryThe loader enumerated installed antivirus products through WMI.T1547.001 · Registry Run Keys / Startup FolderThe loader established persistence through Run and RunOnce registry entries and a copy in the user's Startup folder.T1562.001 · Disable or Modify ToolsThe loader disabled Microsoft Defender protections, added exclusions, terminated a security product, and patched AMSI.T1562.002 · Disable Windows Event LoggingThe loader patched EtwEventWrite to suppress ETW event logging.T1566.001 · Spearphishing AttachmentThe malspam email carried a malicious HTML attachment that initiated the delivery chain.T1573.001 · Symmetric CryptographyThe loader used AES-encrypted messages for C2 communication.T1620 · Reflective Code LoadingThe chain reflectively loaded .NET assemblies using Assembly.Load and invoked their methods.
People
Products
DoubleClickBefore the malspam link gets close to a malicious domain, it routes through ad.doubleclick[.]net, a legitimate, high-reputation Google-owned domain that most email gateways won't blink at.InstallUtil.exeInstallUtil.exe and MSBuild.exe are both hardcoded injection targets, giving it cover under trusted system tools.Microsoft Defender Antimalware PlatformMalwarebytes (MBAMService) process is running, the loader executes a PowerShell command to disable Microsoft Defender protections - real-time monitoring, intrusion prevention, MAPS reporting, and sample submission -Microsoft WindowsOnce it lands, the loader actively patches AMSI and ETW at the native API level, effectively blinding Windows telemetry before it even sets up persistence.MSBuild.exeInstallUtil.exe and MSBuild.exe are both hardcoded injection targets, giving it cover under trusted system tools.