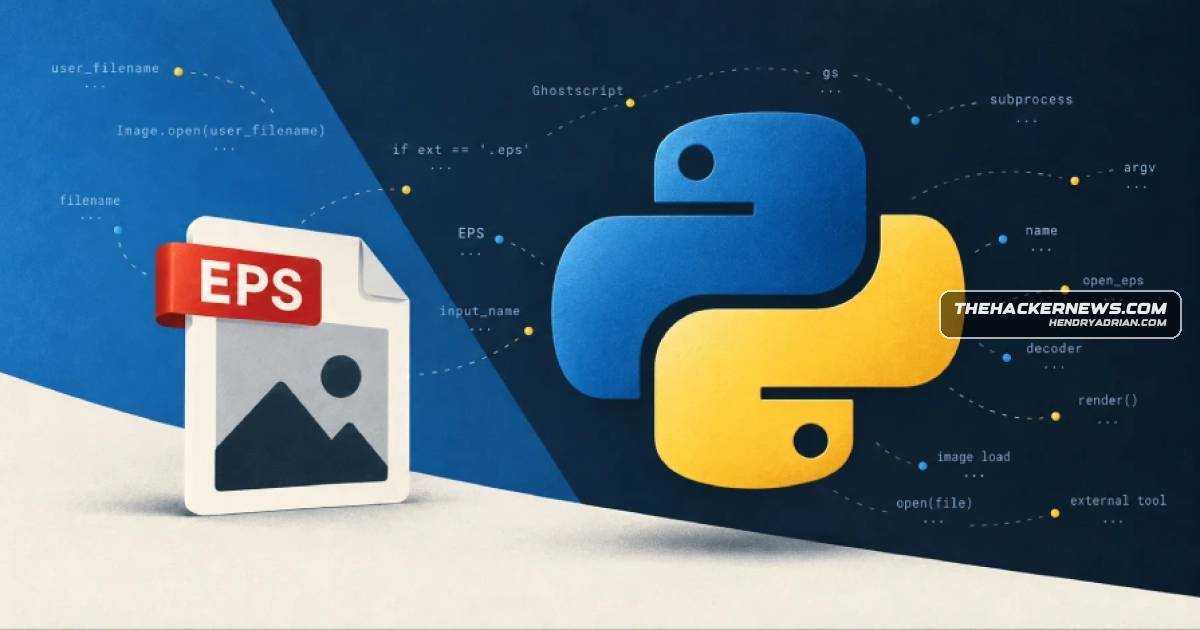
Pillow Flaw Enables Command Execution via an Attacker-Controlled Filename
Pillow versions 2.6.0–12.3.0 have an EPS filename-handling flaw that can pass attacker-controlled input to Ghostscript and enable command execution. Pillow 13.0.0 fixes this and other security flaws.