OpenCode Fixed Windows and WSL Flaw That Let Malicious MCP Servers Run Code During Sign-In
Summary
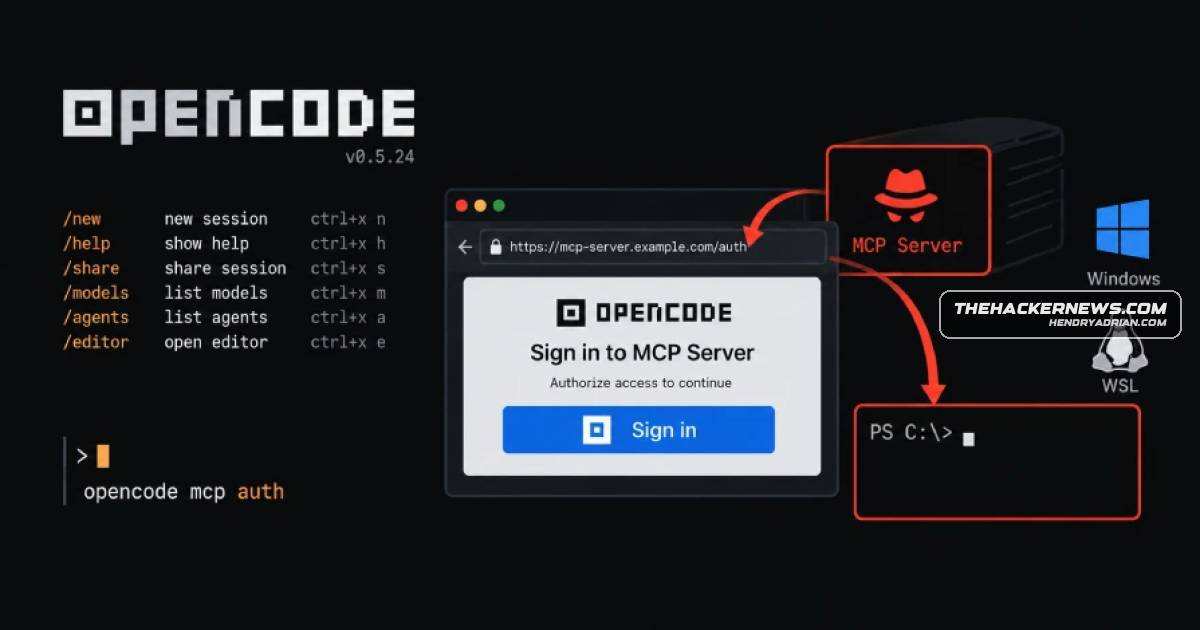
A flaw let a malicious or hijacked MCP server run PowerShell commands when OpenCode users signed in on Windows or WSL. Anomaly fixed it in version 1.18.33; Pillar Security reported no signs of exploitation.
Key points
- Affected versions are OpenCode 1.0.137 through 1.18.32 on Windows and WSL; macOS and Linux are not affected.
- The issue was triggered when a user initiated MCP sign-in, not merely by configuring a server or opening a session.
- A server-controlled OAuth authorization address was passed into a PowerShell command without escaping, enabling command execution with the developer’s access.
- An attacker would need control of an MCP server the developer had added; a server could also be compromised after being added.
- Anomaly fixed the flaw in version 1.18.33. Pillar Security rated it critical, proposing a severity score of 9.8 out of 10.
- No CVE or security advisory was issued, so scanners and dependency alerts will not flag affected builds; users should check their OpenCode version and upgrade.
- Pillar reported no evidence of exploitation and published no indicators for checking for past attacks.
Article Details
- Vulnerability Types
- PowerShell command injection
- Severity
- Critical; Pillar Security proposed a score of 9.8/10.
- Affected Versions
- OpenCode 1.0.137 through 1.18.32
- Exploitation Status
- not_reported
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
CVE
Vendors
Products
OpenCodeA flaw in the OpenCode AI coding agent allowed a malicious or hijacked MCP server to run code on a developer's Windows or WSL machine when the developer signed in. OpenCode connects to MCP (Model Context Protocol)Windows Subsystem for LinuxThe flaw affects OpenCode on Windows and the Windows Subsystem for Linux (WSL). macOS and Linux are not affected, because OpenCode opens the browser there without passing the address through a shell.