

Ransomware Group Spirals Claims Attack on Uganda’s Armada Credit Bureau
A ransomware post attributed to Spirals claims an incident affecting Uganda’s Armada Credit Bureau and its operations. The publisher says it cannot confirm the claim.
A ransomware post attributed to Spirals claims an incident affecting Uganda’s Armada Credit Bureau and its operations. The publisher says it cannot confirm the claim.
Incransom claims it compromised bnlawmacau[.]com and www[.]bn-ip[.]com and threatens to disclose full data. The monitoring post says the claims have not been confirmed.
A ransomware-group claim says NEAD Pro’s Italian network share was encrypted, exposing legal and accounting files and sensitive client and credential data. The report says it could not verify the claims.
A ransomware.live monitoring post attributes an attack on efada[.]sa to krybit, but says the claim and reported operational impact could not be confirmed.
A ransomware group called Qilin claims it targeted UK-based GDM Pipelines, allegedly encrypting systems and disrupting operations. The monitoring post says it could not confirm the claims.
A ransomware.live record says Qilin claimed an attack on French agricultural cooperative Agora coopérative agricole, with files reportedly encrypted and systems disrupted. The claim has not been independently confirmed.
EndZone claims it exfiltrated 15,000 eTeam employee records, including personal and salary information, and threatens to leak them unless the company responds. The report says the claims are unconfirmed.
A ransomware.live record says Barracuda claims to have accessed 463 GB of Solucioning S.A. files and is selling or preparing to publish them after five days without a response. The claims are unconfirmed.
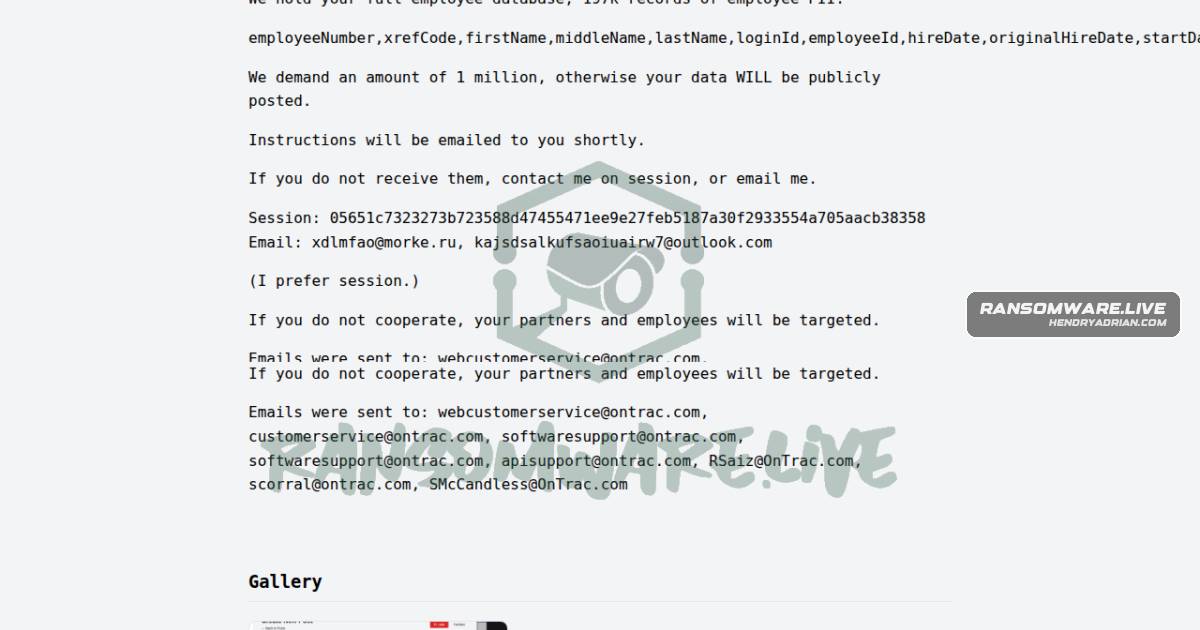
The ransomware actor emperador claims to have exfiltrated 197,000 OnTrac employee records and demands $1 million, threatening public release. The report says the claims are unconfirmed.
A ransomware-monitoring post says Spacebears claims to have targeted Portuguese agricultural equipment manufacturer Tomix / Grupo JOPER. The post says the claim is unverified.
A ransomware.live post records BrainCipher’s unverified claim targeting goldstarfinancial.com, published and discovered on September 23, 2026. The post says the company behind the domain and its operational status could not be confirmed.
Barracuda claims it encrypted Abtach Ltd.’s ESXi systems and employee files and exfiltrated 1.5 TB of data. The monitoring post says the claim is unverified and the data is offered for $100,000.
Ransomware group Spirals claimed an attack on Oman logistics provider ASYAD GROUP and alleged operational disruption. The report says the claim could not be independently confirmed.
Rhysida claims it accessed and exfiltrated data from Legis, including databases, legal documents, financial records, and customer information. The claim is unverified; the post says it cannot confirm the information.
Ransomware.live reports a Settra claim targeting Vestfrostsolutions[.]com in Norway and says the attack disrupted operations. The post states the claim has not been independently confirmed.
The incransom ransomware group claims it leaked 16.8 GB of data across 42,000 files from Virginia A Lemon PLLC, including client, employee, litigation, and financial materials. The claim has not been independently confirmed.
A ransomware.live post attributes to MedusaLocker a claim that 115 email addresses were extracted from Czech organization Seznam (seznam[.]cz). The post says the claim could not be confirmed.
A ransomware.live monitoring post says MedusaLocker claimed to have extracted 137 emails from French organization Aokkef. The post says the claim has not been independently confirmed.
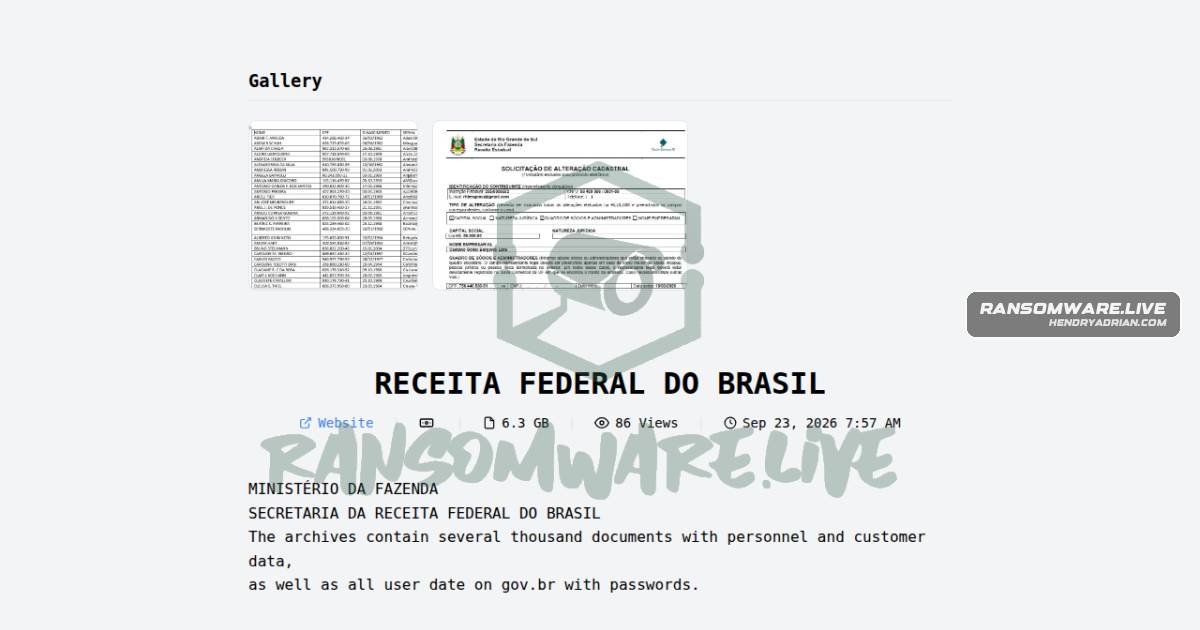
The ransomware group emperador claims it stole thousands of personnel and customer documents from Brazil’s Federal Revenue Service and accessed gov.br user data, including passwords. The report says the claims are unconfirmed.
A ransomware.live record attributes a ransomware claim involving Sherman Chan, DDS, Inc. to Titan, but says the claim is unverified.
A ransomware group named titan claims it targeted Argentina-based healthcare company Grupo Hospifar S.R.L. The report mentions system disruption and data-access attempts but says the claims are unconfirmed.

A ransomware.live monitoring post says the Anubis group claims Gaedke & Partner Steuerberatung’s client data was exposed. The claim is unconfirmed.
A ransomware.live monitoring post says ShinyHunters targeted Fresenius Medical Care in Germany and claims to hold sensitive data, demanding contact by Sep. 25, 2026, to prevent publication. The claim is unconfirmed.
A ransomware.live post attributes a ransomware incident affecting Clark Hill to SilentRansomGroup and says services were disrupted. The post is based on the group’s public claim, which the publisher says it cannot confirm.