
Emperador Claims Data Theft from Brazil’s Federal Revenue Service
Summary
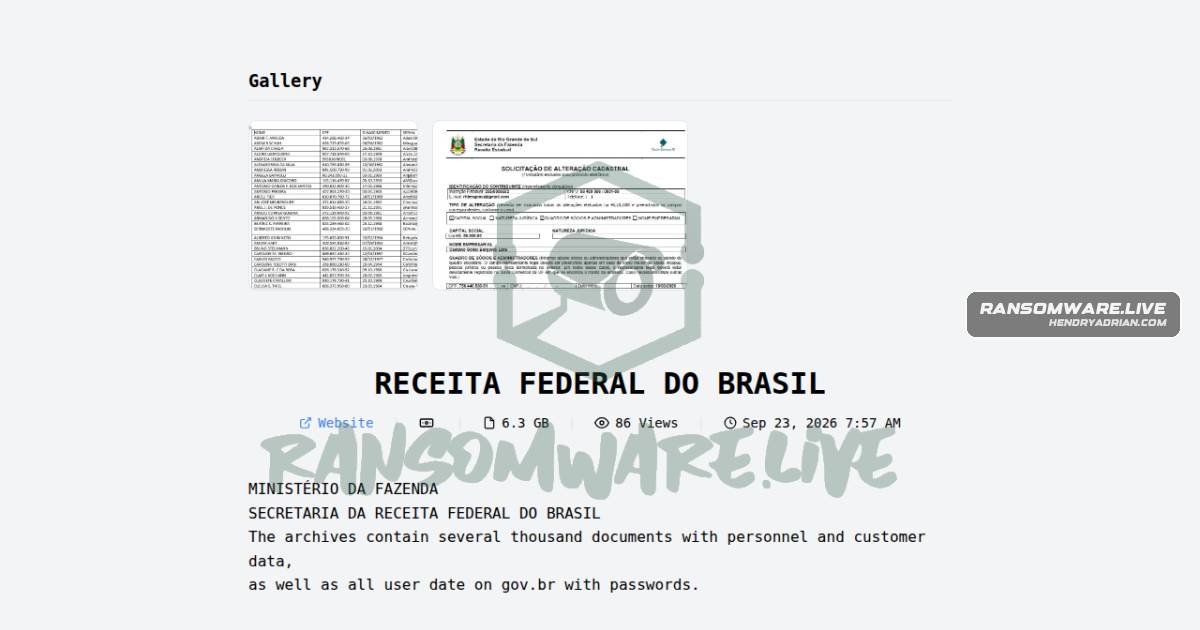
The ransomware group emperador claims it stole thousands of personnel and customer documents from Brazil’s Federal Revenue Service and accessed gov.br user data, including passwords. The report says the claims are unconfirmed.
Key points
- The monitored claim identifies Brazil’s Receita Federal do Brasil as the victim and emperador as the ransomware actor.
- The group claims to have exfiltrated thousands of documents containing personnel and customer data.
- The group also claims access to gov.br user data, including passwords.
- The claim was listed as discovered and published on September 23, 2026.
- The report says it cannot confirm the group’s claims.
Article Details
- Victim
- RECEITA FEDERAL DO BRASIL
- Victim Domain
- gov.br
- Claim Date
- 2026-09-23
- Encryption Status
- Unknown; no encryption claim is reported.
- Exfiltration Status
- Claimed by the ransomware group; unverified.
- Exfiltrated Data
- The group reportedly claimed that archives contained several thousand documents with personnel and customer data, and user data including passwords from gov.br. The source states it cannot confirm the claim.
- Exfiltrated Size
- Several thousand documents were claimed; no volume is reported for the gov.br user data.
- Ransom Demand
- Not disclosed
- Leak Status
- A group claim is reported, but publication or authenticity of leaked data is not confirmed.