

SilentRansomGroup Claims Data Exposure at Redacted Company
Ransomware.live reports that SilentRansomGroup claims full data exposure at a redacted company. The claim appeared on a leak site; the publisher says it cannot confirm its accuracy.
Ransomware.live reports that SilentRansomGroup claims full data exposure at a redacted company. The claim appeared on a leak site; the publisher says it cannot confirm its accuracy.
Ransomware group settra claims it stole thousands of documents from Universal Auto Group. The post says the claim is unconfirmed.
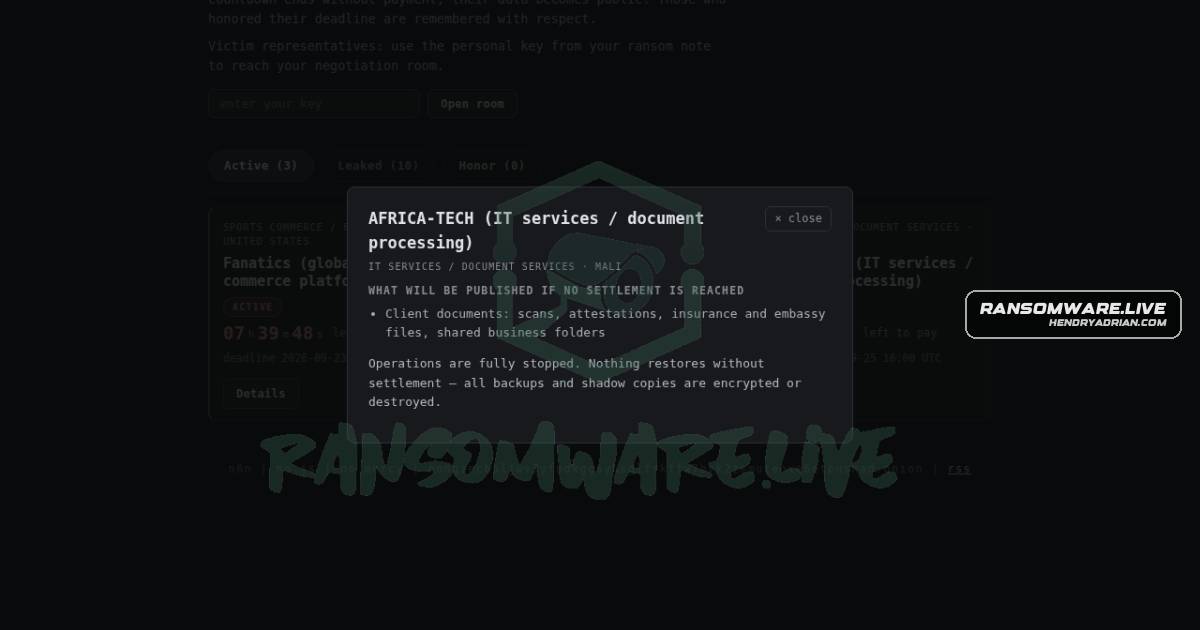
Ransomware group N0n claims AFRICA-TECH in Mali stopped operating after shared client documents and backups were encrypted or destroyed. The report says the claims are unconfirmed.
ShinyHunters claims it compromised FBI systems and sensitive data, threatening disclosure unless a Q2 FLASH report is corrected or removed within a week. The claim is unverified.
Akira claims it will publish 25GB of Coe Press Equipment data, reportedly including employee personal information, financial records, client documents and HR files. The post says the claims are unverified.
Booba Project claims it stole 2 GB of healthcare data from GOTTHELF in Moldova. The post, discovered and published on September 22, 2026, says the claim could not be confirmed.
A ransomware group called Booba Project claimed it stole about 35 GB of Education Administration Programs data from Tulare Western High School. The report says the claim is unverified.
A ransomware.live monitoring post says Qilin targeted Canadian manufacturer Textile City and claims operational disruption and data compromise. The post says the claims could not be confirmed.
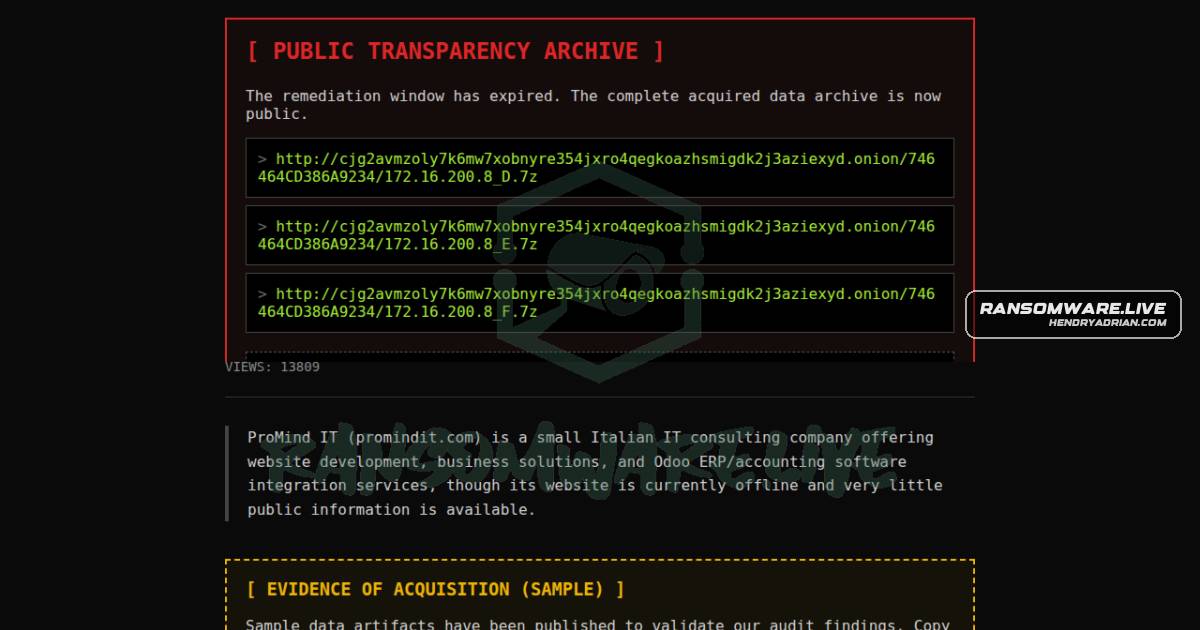
A ransomware monitoring post attributes an alleged encryption and business disruption incident at Italy-based Pr***IT to AuditTeam. The post says the claims are unverified.
Ransomware.live reports an unverified AuditTeam claim involving vit[.]ac[.]in, with a discovery date of September 22, 2026. The article says it cannot confirm the claim.
A ransomware.live monitoring post reports that the Termite group claims to have encrypted data and disrupted operations at Colorado-based cable management provider Sealcon. The post says the claim is unverified.
The ransomware group termite claimed an attack on US wholesale mortgage company theLender. The claim was listed on September 22, 2026; the report says it could not confirm the information.
Ransomware group termite claimed an attack on US real estate firm TruAmerica Multifamily, alleging disruption and unauthorized system access. The claim was published September 22, 2026, and has not been independently confirmed.
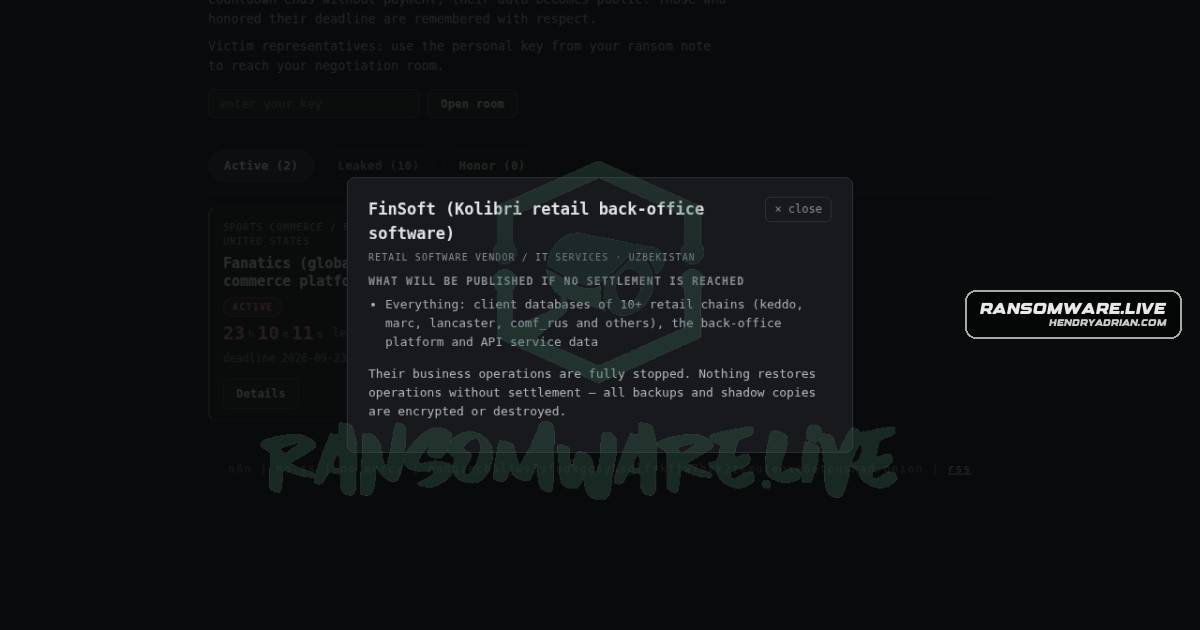
The N0n ransomware group claims it compromised FinSoft’s Kolibri platform and accessed data from more than 10 retail chains. It threatens to publish one client database per day after a September 25 deadline; the claims are unconfirmed.
A ransomware.live monitoring post records a Play group claim naming Brazilian manufacturer Metallco, published September 21, 2026. The post says it cannot confirm the claim’s accuracy.
Nightspire allegedly encrypted and stole documents, projects, and software source code from Italy’s 360 Consulenza S.r.l. The post reports the claim but says it cannot confirm its accuracy.
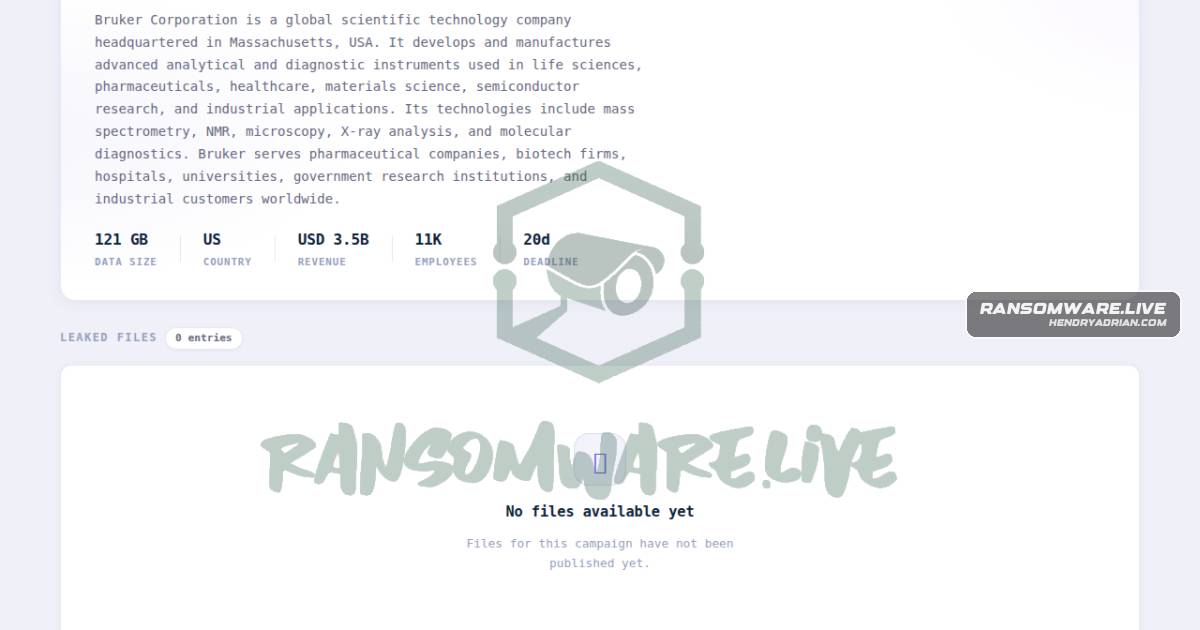
A ransomware.live post attributes an alleged attack on Bruker Corporation to metaencryptor. The post says the group’s claim cannot be independently confirmed.
A ransomware-monitoring post attributes an incident affecting Hudson MD Group’s New Jersey outpatient practices and care centers to metaencryptor. The claim was posted on September 21, 2026, and the post says it could not be verified.
A ransomware.live post says the group moneymessage claimed an attack on U.S. Electrical Services and Wiedenbach Brown, discovered and published on September 21, 2026. The claim is unverified.
Ransomware.live lists Newman Tractor as a threeam ransomware claim, with discovery and publication dates of September 21, 2026. The post says the group’s claim has not been independently confirmed.
LockBit 5 claimed an attack on Ethiopian financial institution Siinqee Bank (siinqeebank[.]com). The monitoring post lists September 20–21, 2026 dates and says the claim could not be confirmed.
Qilin claimed it compromised Japan-based IKEGAMI TSUSHINKI COMPANY LIMITED, exfiltrated data and demanded payment to prevent further disclosure. The report says the claim is unconfirmed.
A ransomware.live monitoring post says Qilin claimed an attack on Thai retailer ShopDunk. The post reports the claim was published on September 20, 2026, and says it could not confirm its accuracy.
A ransomware.live monitoring post records Qilin’s unverified claim targeting Turkey’s Zorlu Holding, published September 20, 2026. The post does not confirm the group’s claims.