
BlackLocks Claims Ransomware Attack on South African Architecture Firm
BlackLocks claimed an attack on South Africa’s ARCA UNLIMITED Architects, alleging disruption and file and data encryption. The report says the claims are unconfirmed.
BlackLocks claimed an attack on South Africa’s ARCA UNLIMITED Architects, alleging disruption and file and data encryption. The report says the claims are unconfirmed.
Ransomware group Barracuda claims it stole about 90 GB of International Chemical Co. data, including formulas, patents and manufacturing information, and is offering it for sale. The claims are unverified.

A ransomware monitoring post attributes an attack on M****n in the US to payoutsking, alleging disruption and data loss. The post says the claims could not be confirmed.
Ransomware.live lists Crossett Home as a claimed Termite ransomware target. The listing says the petroleum transporter operates in the Eastern U.S. and Ontario, but notes the group's claims are unverified.
Wallstreet allegedly targeted UK industrial-equipment distributor Ar Valve Resources. The post says the claim could disrupt operations but notes it cannot confirm the group's claims.
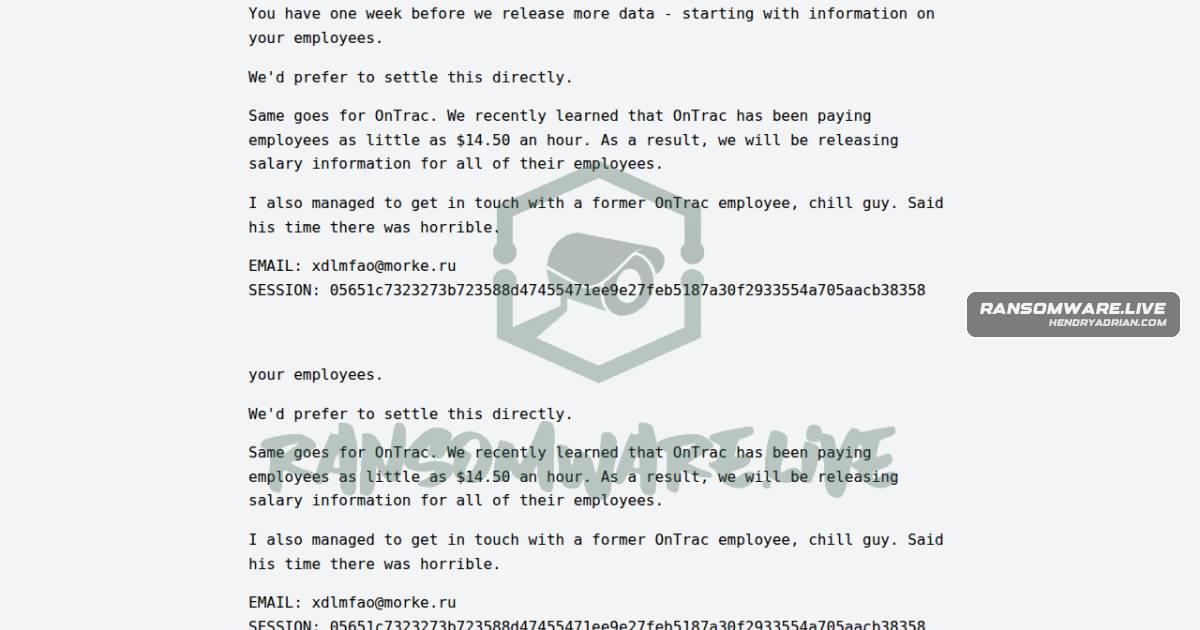
Ransomware group emperador claims it compromised Electrolux and OnTrac and threatens to release employee data within a week. The post says the claims are unverified.
A ransomware.live post attributes a claim of an attack affecting PKF Hadiwinata’s operations in Indonesia to metaencryptor. The post says the information is based on the group’s public claims and is unconfirmed.
MetaEncryptor claims it targeted GE Vernova and alleges disruption across its Power, Wind, and Electrification segments, with data likely affected. The report says the claims are unconfirmed.

A ransomware.live monitoring post records a SilentRansomGroup claim involving a redacted company in an unnamed country. The company name is pending disclosure, and the post says the claim cannot be confirmed.
A ransomware.live-monitored post attributes a claim involving accounting firm Tobin & Company to the Wallstreet group. The post says the claim has not been independently confirmed.
A ransomware.live post attributes an incident affecting Morula IVF’s healthcare network and services to Everest. The post cites the group’s leak site and says the claim could not be independently confirmed.
A ransomware.live post records an Everest claim targeting Securitas Group in Sweden and says the claim could not be confirmed.
A ransomware.live post attributes a claimed ransomware incident affecting Taspen Life in Kazakhstan to LockBit 5. It reports disruption to operations and customer services, but says the group’s claims are unconfirmed.
A ransomware.live record attributes an incident affecting Iberia Compositech Manufacturing in Spain to Qilin, but says the group’s public claim could not be verified.
A ransomware-monitoring post attributes an alleged incident disrupting Majani Insurance Brokers’ operations in Kenya to Vexy Ransomware. The post says the claim comes from the group and is unverified.
A ransomware.live monitoring post says Qilin targeted US manufacturer All Tech Machine & Engineering. The claim is attributed to the ransomware group and has not been confirmed.
A post monitored by ransomware.live attributes a ransomware incident affecting Catholic University of El Salvador to Wallstreet. The post describes disruption and encrypted data but says the group’s claims are unconfirmed.
A ransomware.live monitoring post records a Wallstreet claim involving Prater & Ridley Attorneys At Law, discovered and published on September 24, 2026. The post says the claim is unconfirmed.
Ransomware group N0n claims it stole TapClicks source code and customer marketing data, including password hashes and ad-platform credentials. The claim is unverified; a deadline is listed for 2026-09-28.
Incransom claims it stole ukbjja[.]org’s full data. The ransomware.live record lists the claim as published and discovered on September 24, 2026, and says the information is unverified.
A ransomware.live post reports an incransom claim targeting welgenone[.]com, a Georgia-based wellness provider. The claim’s accuracy has not been confirmed.
A ransomware.live monitoring post records Pear’s claim that Indroj Medical Group Inc., a US healthcare organization, was targeted. The post says it cannot confirm the claim.
The ransomware group pear claims it disrupted Martin Lawrence Galleries’ access to data and systems. The post says the claim has not been independently confirmed.
A ransomware group called pear claimed an incident involving US healthcare provider Westside GI. The post reports service and system disruption but says the claim could not be confirmed.