
SANS Honeypots Record Rising SSHole Exploit Attempts
Summary
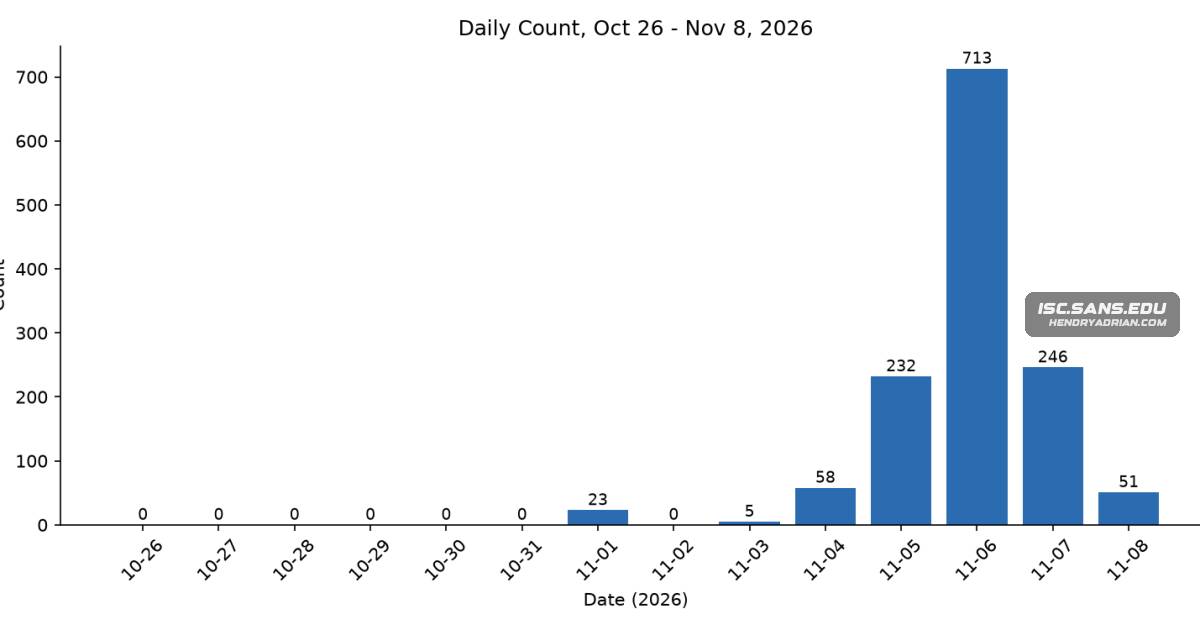
SANS Cowrie honeypots recorded rising SSHole-related activity, with the first identified exploit attempt on Nov. 5 and 713 requests on Nov. 6. The data captures only the first 255 characters of SSH passwords.
Key points
- Long-password submissions began appearing on Nov. 1; the author says the initial submissions did not appear related to SSHole.
- The first attempt identified as an actual SSHole exploit attempt arrived on Nov. 5 and used a password consisting entirely of “A” characters.
- Recorded requests peaked at 713 on Nov. 6, then fell to 246 on Nov. 7 and 51 on Nov. 8.
- Some earlier submissions contained shell commands, which the author attributes to buggy brute-force scripts putting post-login commands in the password field.
- Cowrie records only the first 255 password characters, limiting the dataset; the author expects some login attempts against the honeypots may have succeeded and plans to share more details.
Article Details
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- unknown
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 109[.]94[.]173[.]13 | Source IP listed among scanners attempting to exploit sshole. |
| IPV4 | 112[.]162[.]23[.]132 | Source IP listed among scanners attempting to exploit sshole. |
| IPV4 | 121[.]163[.]224[.]97 | Source IP listed among scanners attempting to exploit sshole. |
| IPV4 | 121[.]190[.]39[.]238 | Source IP listed among scanners attempting to exploit sshole. |
| IPV4 | 152[.]233[.]50[.]185 | Source IP listed among scanners attempting to exploit sshole. |
| IPV4 | 154[.]80[.]128[.]173 | Source IP listed among scanners attempting to exploit sshole. |
| IPV4 | 183[.]99[.]38[.]238 | Source IP listed among scanners attempting to exploit sshole. |
| IPV4 | 185[.]2[.]148[.]137 | Source IP listed among scanners attempting to exploit sshole. |
| IPV4 | 195[.]178[.]110[.]78 | Source IP listed among scanners attempting to exploit sshole. |
| IPV4 | 213[.]86[.]169[.]133 | Source IP listed among scanners attempting to exploit sshole. |
| IPV4 | 220[.]70[.]219[.]98 | Source IP listed among scanners attempting to exploit sshole. |
| IPV4 | 220[.]77[.]237[.]35 | Source IP listed among scanners attempting to exploit sshole. |
| IPV4 | 52[.]119[.]124[.]122 | Source IP listed among scanners attempting to exploit sshole. |
| IPV4 | 58[.]151[.]184[.]226 | Source IP listed among scanners attempting to exploit sshole. |
| IPV4 | 62[.]210[.]173[.]100 | Source IP listed among scanners attempting to exploit sshole. |
| IPV4 | 82[.]74[.]132[.]129 | Source IP listed among scanners attempting to exploit sshole. |
| IPV4 | 87[.]241[.]132[.]12 | Source IP listed among scanners attempting to exploit sshole. |
| IPV4 | 92[.]255[.]57[.]7 | Source IP listed among scanners attempting to exploit sshole. |
| URL | hxxp[:]//156[.]238[.]252[.]37:8000/bot.x86_64 | Payload URL used by buggy brute-force scripts to download bot.x86_64. |
MITRE ATT&CK
T1059.004 · Unix ShellA shell command containing cd, wget or curl, and chmod was submitted in an SSH password field by buggy scripts and may have run.T1105 · Ingress Tool TransferThe command attempted to download bot.x86_64 from a remote URL using wget or curl.T1222.002 · Linux and Mac PermissionsThe command used chmod 777 on the downloaded file.