
SSHole OpenSSH Flaw Exploited Within Hours; Alpine Honeypot Saw Root Access
Summary
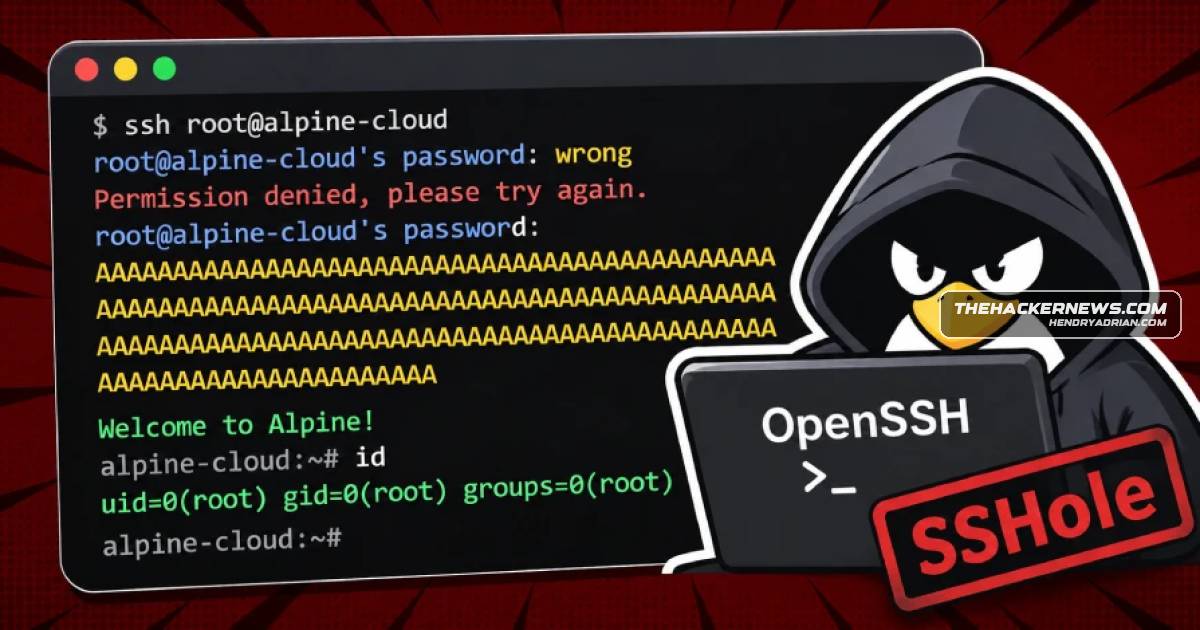
Previdian reported exploitation attempts within nine hours of SSHole’s disclosure and confirmed root access on an Alpine Linux honeypot. The flaw affects specific musl-based OpenSSH configurations; OpenSSH 10.6p2 addresses it.
Key points
- CVE-2026-123158 affects OpenSSH on Linux systems using musl with PAM disabled, including Alpine Linux’s default OpenSSH server configuration.
- An unauthenticated attacker can exploit the flaw with an oversized password to access an account whose password hash is an asterisk; accounts with valid password hashes are not affected.
- The vulnerability stems from password-handling behavior introduced in a 2016 patch for CVE-2016-6210.
- Previdian said it observed the first exploitation attempt less than nine hours after disclosure and confirmed root access on an Alpine Linux honeypot.
- Previdian reported eight exploitation attempts from an IP address geolocated to Japan; the observed source IP was 89.116.89[.]18.
- Install OpenSSH 10.6p2 or a distribution-patched package and restart sshd. Alpine also advises reviewing relevant login logs and investigating exposed systems for signs of unauthorized access.
Article Details
- Vulnerability Types
- Authentication bypass affecting accounts with disabled passwords
- Severity
- CVSS 8.1
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 89[.]116[.]89[.]18 | Source IP Previdian observed attempting to exploit SSHole; the honeypot received oversized passwords and reconnaissance commands from it. |
MITRE ATT&CK
T1021.004 · SSHThe attacker used non-interactive SSH sessions to access the vulnerable honeypot.T1033 · System Owner/User DiscoveryThe attacker ran the id command during reconnaissance through SSH.T1082 · System Information DiscoveryThe attacker ran uname and hostname commands during reconnaissance through SSH.
CVE
People
Products
Alpine Linuxthat run OpenSSH on the musl C library with Pluggable Authentication Modules (PAM) disabled, including Alpine Linux's default OpenSSH server configuration.OpenSSHThreat actors are attempting to exploit a recently disclosed security flaw impacting OpenSSH that can enable sign-ins to accounts that have no password set, according to Previdian.