
Akamai Links APT28 Activity to Exploitation of Patched MSHTML Zero-Day
Summary
Microsoft patched CVE-2026-21513 in February 2026 and said it was exploited as a zero-day. Akamai linked a VirusTotal sample and wellnesscaremed[.]com infrastructure to APT28, describing crafted LNK/HTML files that bypass browser protections.
Key points
- Microsoft said CVE-2026-21513 was exploited as a zero-day and patched it in its February 2026 update.
- Akamai associated a VirusTotal sample uploaded on January 30, 2026, with infrastructure it linked to APT28.
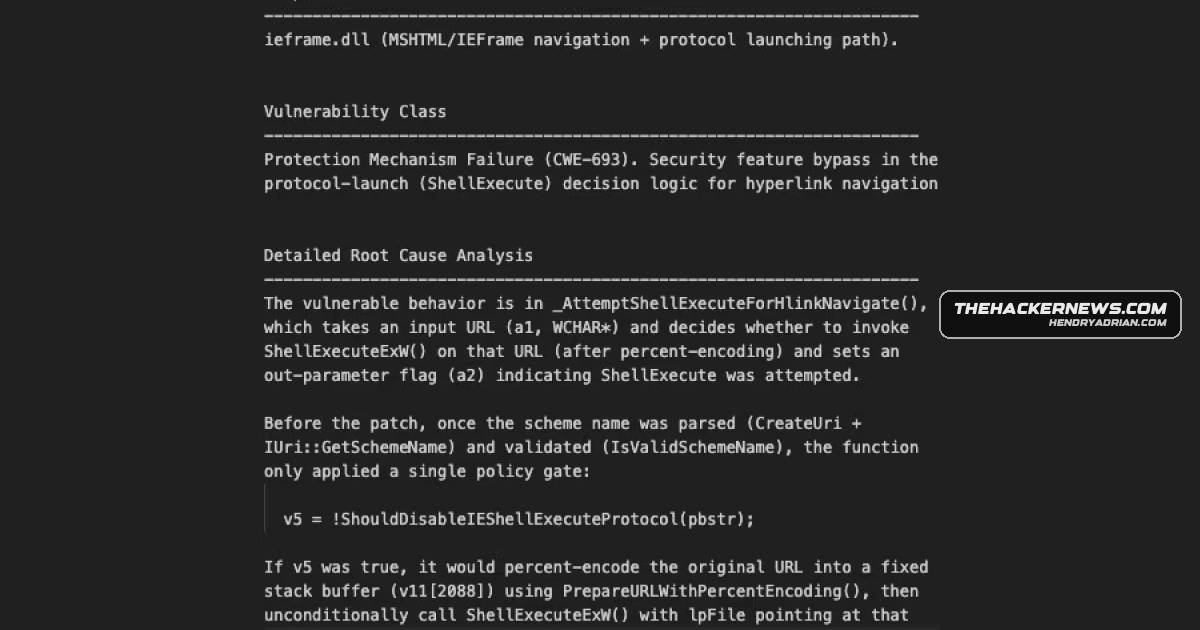
- The high-severity MSHTML flaw stems from insufficient URL validation in ieframe.dll, allowing attacker-controlled input to reach ShellExecuteExW.
- A crafted LNK file can embed HTML and manipulate browser and Windows Shell handling to execute content outside the browser security context.
- Akamai said the technique can bypass Mark-of-the-Web and Internet Explorer Enhanced Security Configuration protections.
- Akamai warned that other components embedding MSHTML could provide delivery paths beyond LNK files.
Article Details
- Vulnerability Types
- Security feature bypass
- Insufficient URL validation
- Severity
- High (CVSS 8.8)
- Exploitation Status
- reported
- Exploit Availability
- unknown
- Patch Status
- available
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | wellnesscaremed[.]com | Domain identified by Akamai as infrastructure associated with APT28-linked campaign payloads. |
MITRE ATT&CK
CVE
CVE-2026-21509Microsoft · Microsoft 365 Apps for Enterprise; Microsoft · Microsoft Office 2016; +3 moreMicrosoft patched the flaw in February 2026, and Akamai found a VirusTotal sample linked to wellnesscaremed[.]com; CERTâUA previously flagged related APT28 activity exploiting CVE-2026-21509.CVE-2026-21513Microsoft · Windows 10 Version 1607; Microsoft · Windows 10 Version 1809; +19 moreA recently patched high-severity MSHTML vulnerability (CVE-2026-21513) may have been exploited by the Russia-linked threat actor APT28, according to Akamai’s findings.
People
Threat Actors
Vendors
Products
Microsoft Office(CERT-UA) early last month in connection with APT28’s attacks exploiting another security flaw in Microsoft Office (CVE-2026-21509, CVSS score: 7.8).Microsoft WindowsAttackers weaponize crafted HTML or LNK files to manipulate browser and Windows Shell handling and reach ShellExecuteExW for code execution.MSHTML FrameworkThe vulnerability in question is CVE-2026-21513 (CVSS score: 8.8), a high-severity security feature bypass affecting the MSHTML Framework.