
Citrix Urges Immediate Patching for Two NetScaler Vulnerabilities
Summary
Citrix patched CVE-2026-3055, which may expose memory and session tokens, and CVE-2026-4368, which may cause session mix-ups. Fixes are available for affected NetScaler versions; the number of vulnerable internet-exposed systems is unknown.
Key points
- CVE-2026-3055 is a critical memory-overread flaw affecting NetScaler ADC and Gateway configured as a SAML identity provider; remote attackers may be able to access sensitive information such as session tokens.
- CVE-2026-4368 is a race-condition flaw affecting Gateway and AAA virtual server configurations that may cause user session mix-ups; exploitation requires low privileges.
- Fixes are available for affected 13.1 and 14.1 versions, including 13.1-62.23, 14.1-66.59, and 13.1-37.262 for FIPS and NDcPP editions.
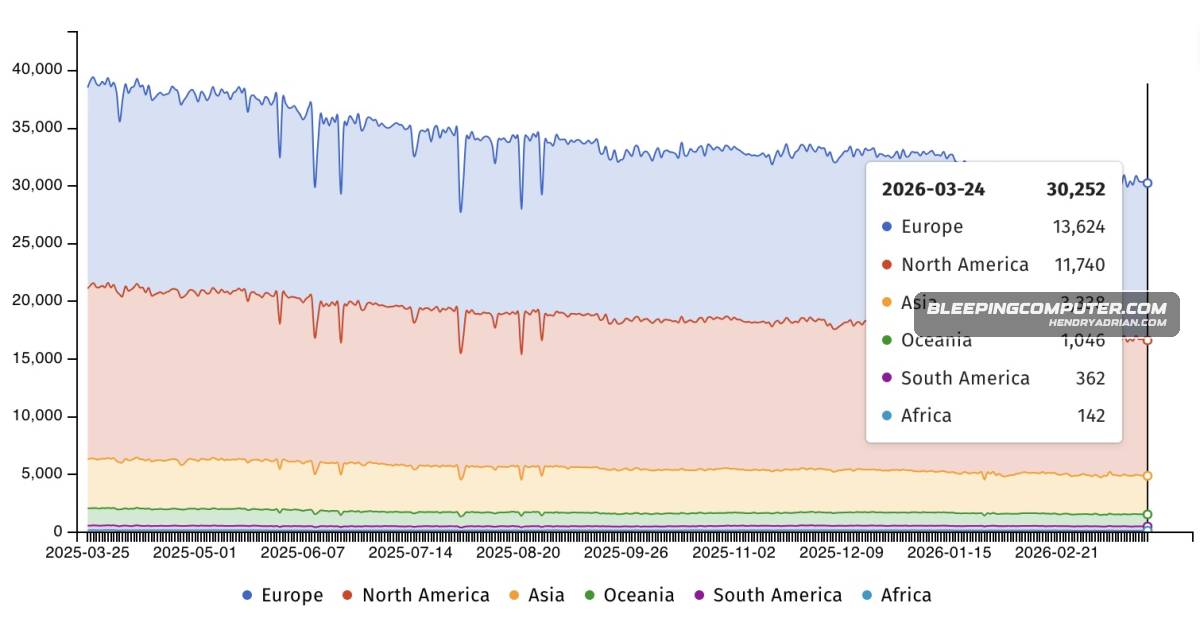
- Shadowserver tracks more than 30,000 NetScaler ADC and 2,300 Gateway instances exposed online, but the number using vulnerable configurations or still unpatched is unknown.
- Security companies warn that attackers may reverse-engineer the CVE-2026-3055 patch; exploitation has not been reported in the article.
Article Details
- Vulnerability Types
- Insufficient input validation causing a remote memory overread
- Race condition that can cause user session mix-ups
- Severity
- CVE-2026-3055 is described as critical; severity for CVE-2026-4368 is not stated.
- Affected Versions
- NetScaler ADC and NetScaler Gateway 13.1 (fixed in 13.1-62.23)
- NetScaler ADC and NetScaler Gateway 14.1 (fixed in 14.1-66.59)
- NetScaler ADC 13.1-FIPS (addressed in 13.1-37.262)
- NetScaler ADC 13.1-NDcPP (addressed in 13.1-37.262)
- Exploitation Status
- unknown
- Exploit Availability
- unknown
- Patch Status
- available
CVE
CVE-2023-4966Citrix · NetScaler ADC; Citrix · NetScaler Gatewayvulnerabilities broadly exploited in the wild, including the infamous ‘CitrixBleed’ vulnerability, CVE-2023-4966, in 2023,” Rapid7 added.CVE-2026-3055NetScaler · ADC; NetScaler · GatewayCitrix patched two serious vulnerabilities in NetScaler ADC and NetScaler Gateway appliances: CVE-2026-3055, a memory overread in SAML IDP configurations similar to past CitrixBleed flaws, and CVE-2026-4368, aCVE-2026-4368NetScaler · ADC; NetScaler · GatewayCVE-2026-3055, a memory overread in SAML IDP configurations similar to past CitrixBleed flaws, and CVE-2026-4368, a race-condition bug that can cause session mix-ups.
Vendors
CitrixCitrix patched two serious vulnerabilities in NetScaler ADC and NetScaler Gateway appliances: CVE-2026-3055, a memory overread in SAML IDP configurations similar to past CitrixBleed flaws, and CVE-2026-4368, aCloud Software Group“Cloud Software Group strongly urges affected customers of NetScaler ADC and NetScaler Gateway to install the relevant updated versions as soon as possible,” the company warned in a Monday advisory.
Products
NetScaler ADCCitrix patched two serious vulnerabilities in NetScaler ADC and NetScaler Gateway appliances: CVE-2026-3055, a memory overread in SAML IDP configurations similar to past CitrixBleed flaws, and CVE-2026-4368, aNetScaler GatewayCitrix patched two serious vulnerabilities in NetScaler ADC and NetScaler Gateway appliances: CVE-2026-3055, a memory overread in SAML IDP configurations similar to past CitrixBleed flaws, and CVE-2026-4368, a