
CISA Orders Federal Agencies to Patch iOS Flaws Used by DarkSword
Summary
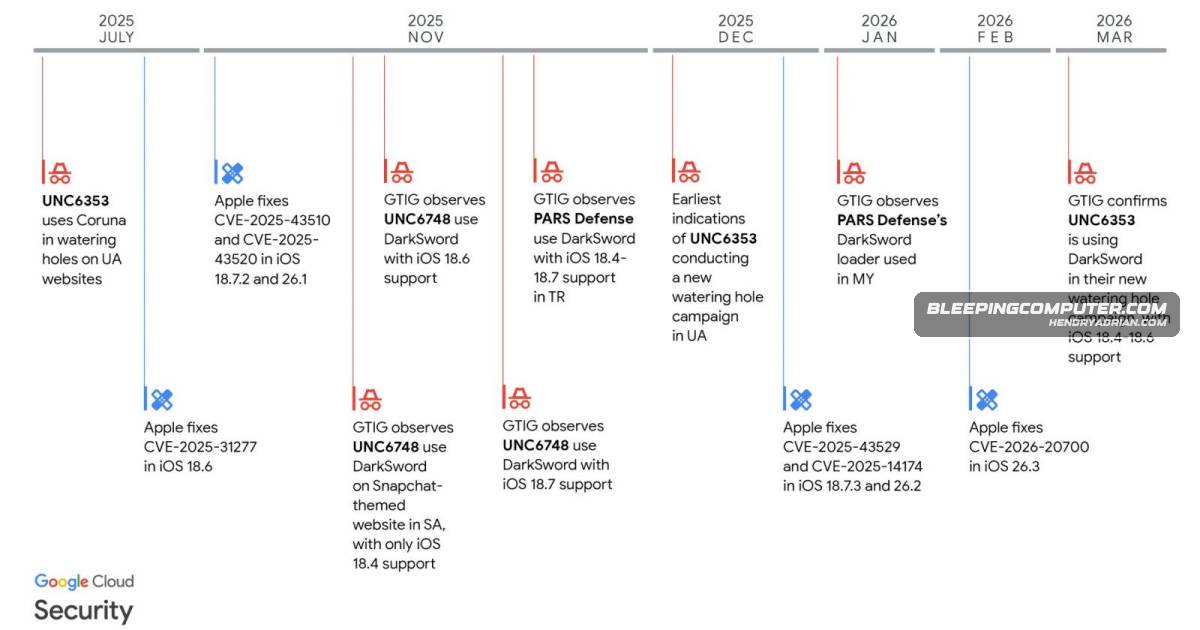
CISA ordered federal agencies to patch three actively exploited iOS flaws by April 3. Researchers say the six-flaw DarkSword chain enables sandbox escapes, privilege escalation and remote code execution on iOS 18.4–18.7.
Key points
- CISA added CVE-2025-31277, CVE-2025-43510 and CVE-2025-43520 to its catalog of actively exploited flaws and set an April 3 remediation deadline for federal civilian agencies.
- Researchers reported that DarkSword uses a chain of six vulnerabilities to achieve sandbox escapes, privilege escalation and remote code execution.
- The six flaws are CVE-2025-31277, CVE-2025-43529, CVE-2026-20700, CVE-2025-14174, CVE-2025-43510 and CVE-2025-43520; the article says they were patched in later iOS releases and affect iOS 18.4–18.7.
- Google Threat Intelligence Group researchers observed the GhostBlade, GhostKnife and GhostSaber information-stealing malware families on targeted devices.
- Researchers linked DarkSword to UNC6748 and suspected Russian espionage group UNC6353; UNC6353 reportedly used DarkSword and Coruna in watering-hole attacks on Ukrainian websites.
- The article says DarkSword removes temporary files and exits after data theft, which researchers interpreted as consistent with short-term surveillance designed to evade detection.
Article Details
- Vulnerability Types
- Sandbox escape
- Privilege escalation
- Remote code execution
- Affected Versions
- iOS 18.4–18.7
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Apply mitigations per vendor instructions; follow applicable BOD 22-01 guidance for cloud services; discontinue use of the product if mitigations are unavailable.
MITRE ATT&CK
T1059.007 · JavaScriptGhostBlade and GhostSaber are JavaScript malware described as stealing data or executing code on victims’ devices.T1068 · Exploitation for Privilege EscalationThe DarkSword exploit chain enables privilege escalation on affected iPhones.T1189 · Drive-by CompromiseUNC6353 used watering-hole attacks involving compromised Ukrainian websites visited by iPhone users.T1203 · Exploitation for Client ExecutionDarkSword exploits a six-vulnerability chain to gain remote code execution on unpatched iPhones.
CVE
CVE-2025-14174Google · Chromeabuses a chain of six vulnerabilities tracked as CVE-2025-31277, CVE-2025-43529, CVE-2026-20700, CVE-2025-14174, CVE-2025-43510, and CVE-2025-43520.CVE-2025-31277Apple · iOS and iPadOS; Apple · macOS; +19 morerevealed last week, the DarkSword delivery framework abuses a chain of six vulnerabilities tracked as CVE-2025-31277, CVE-2025-43529, CVE-2026-20700, CVE-2025-14174, CVE-2025-43510, and CVE-2025-43520.CVE-2025-43510Apple · iOS and iPadOS; Apple · macOS; +3 moreof six vulnerabilities tracked as CVE-2025-31277, CVE-2025-43529, CVE-2026-20700, CVE-2025-14174, CVE-2025-43510, and CVE-2025-43520.CVE-2025-43520Apple · iOS and iPadOS; Apple · macOS; +3 moretracked as CVE-2025-31277, CVE-2025-43529, CVE-2026-20700, CVE-2025-14174, CVE-2025-43510, and CVE-2025-43520.CVE-2025-43529Apple · iOS and iPadOS; Apple · macOS; +4 morethe DarkSword delivery framework abuses a chain of six vulnerabilities tracked as CVE-2025-31277, CVE-2025-43529, CVE-2026-20700, CVE-2025-14174, CVE-2025-43510, and CVE-2025-43520.CVE-2026-20700Apple · iOS and iPadOS; Apple · macOS; +3 moredelivery framework abuses a chain of six vulnerabilities tracked as CVE-2025-31277, CVE-2025-43529, CVE-2026-20700, CVE-2025-14174, CVE-2025-43510, and CVE-2025-43520.
Threat Actors
UNC6353Researchers linked UNC6353 to DarkSword campaigns; the article describes it as a suspected Russian espionage group and says it deployed DarkSword and Coruna in watering-hole attacks.UNC6748Researchers linked UNC6748 to DarkSword campaigns; the article identifies it as a customer of Turkish commercial surveillance vendor PARS Defense.
Malware
GHOSTBLADEResearchers observed three info-stealing families—GhostBlade, GhostKnife, and GhostSaber—dropped by the exploit framework.GHOSTKNIFEResearchers observed three info-stealing families—GhostBlade, GhostKnife, and GhostSaber—dropped by the exploit framework.GHOSTSABERResearchers observed three info-stealing families—GhostBlade, GhostKnife, and GhostSaber—dropped by the exploit framework.
Vendors
Appleescalate privileges, and gain remote code execution on unpatched iPhones, but have all been patched by Apple in the latest iOS releases and now only affect iPhones running iOS 18.4 through 18.7.PARS Defenseto multiple threat groups, including UNC6748, a customer of Turkish commercial surveillance vendor PARS Defense, and a suspected Russian espionage group tracked as UNC6353.
Products
Tools
CorunaUNC6353 and UNC6748 were linked to the campaigns, with UNC6353 using DarkSword and Coruna in watering-hole attacks on Ukrainian sites.DarkSwordfederal agencies to patch three iOS vulnerabilities exploited by the DarkSword exploit kit in campaigns that stole cryptocurrency and conducted cyberespionage.
Industries
E-commerceexploit kits in watering-hole attacks targeting iPhone users visiting compromised Ukrainian websites of e-commerce, industrial equipment, and local services organizations.Industrial Equipmentattacks targeting iPhone users visiting compromised Ukrainian websites of e-commerce, industrial equipment, and local services organizations.Local servicesiPhone users visiting compromised Ukrainian websites of e-commerce, industrial equipment, and local services organizations.