
BRIDGE:BREAK Flaws Put Nearly 20,000 Serial-to-IP Converters at Risk
Summary
Forescout identified 22 BRIDGE:BREAK flaws in Lantronix and Silex serial-to-IP converters, with nearly 20,000 devices exposed online. Exploitation could disrupt communications or tamper with data; vendors released patches.
Key points
- Forescout identified 22 vulnerabilities across Lantronix EDS3000PS and EDS5000 series and the Silex SD330-AC.
- Nearly 20,000 serial-to-Ethernet converters were found exposed to the internet worldwide.
- The flaws include remote code execution, authentication bypass, denial of service, device takeover, and firmware or configuration tampering.
- Successful exploitation could disrupt serial communications, alter sensor or actuator data, and enable movement into critical networks.
- Lantronix and Silex released security updates; recommended measures include patching, replacing default credentials, segmenting networks, and removing direct internet exposure.
Article Details
- Vulnerability Types
- Remote code execution
- Client-side code execution
- Denial-of-service (DoS)
- Authentication bypass
- Device takeover
- Firmware tampering
- Configuration tampering
- Information disclosure
- Arbitrary file upload
- Exploitation Status
- unknown
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Remove direct internet exposure from the devices.
- Replace default credentials and avoid weak passwords.
- Segment networks to restrict access to vulnerable converters and limit movement to other assets.
MITRE ATT&CK
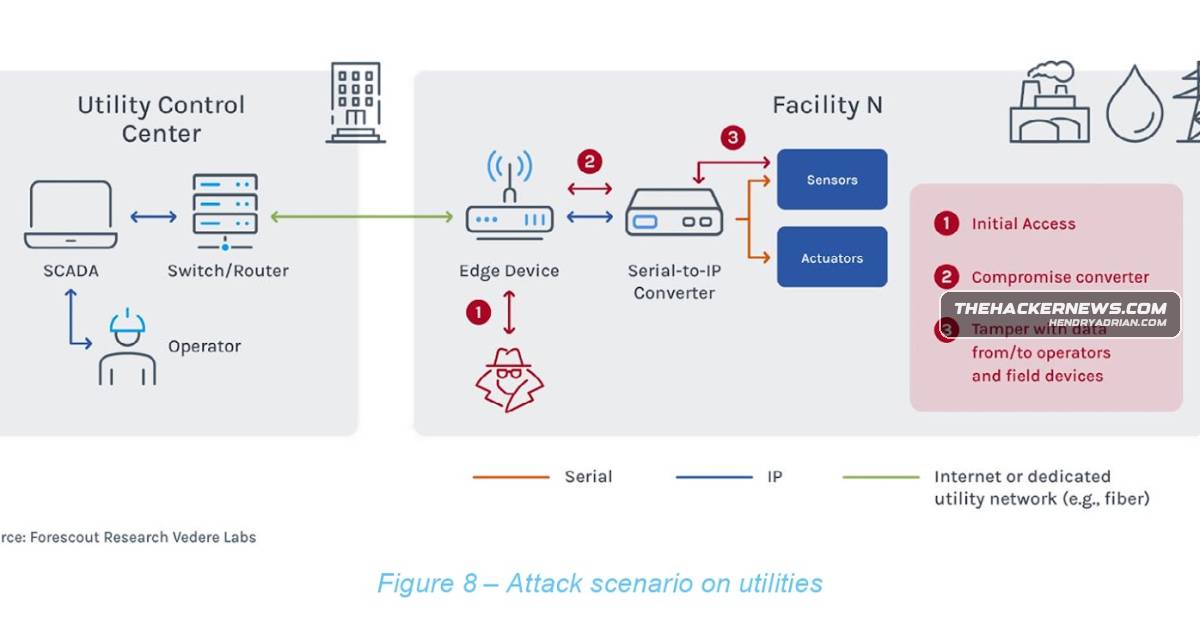
T1190 · Exploit Public-Facing ApplicationThe article describes a hypothetical attack in which an actor weaponizes BRIDGE:BREAK vulnerabilities to compromise a serial-to-IP converter; nearly 20,000 such converters were reported exposed online.T1565.002 · Transmitted Data ManipulationSuccessful exploitation could let attackers alter serial data moving to or from the IP network, including sensor values or actuator behavior.
CVE
CVE-2015-5621Net-snmp · Net-snmpDenial-of-service (DoS) – CVE-2026-32961, CVE-2015-5621, CVE-2024-24487CVE-2024-24487silex · ds-600_firmwareDenial-of-service (DoS) – CVE-2026-32961, CVE-2015-5621, CVE-2024-24487CVE-2025-67034Lantronix · EDS5000 series; Lantronix · G520 series; +1 moreRemote code execution – CVE-2026-32955, CVE-2026-32956, CVE-2026-32961, CVE-2025-67041, CVE-2025-67034, CVE-2025-67035, CVE-2025-67036, CVE-2025-67037, and CVE-2025-67038CVE-2025-67035Lantronix · EDS5000 seriesRemote code execution – CVE-2026-32955, CVE-2026-32956, CVE-2026-32961, CVE-2025-67041, CVE-2025-67034, CVE-2025-67035, CVE-2025-67036, CVE-2025-67037, and CVE-2025-67038CVE-2025-67036Lantronix · EDS5000 series; Lantronix · G520 series; +1 moreRemote code execution – CVE-2026-32955, CVE-2026-32956, CVE-2026-32961, CVE-2025-67041, CVE-2025-67034, CVE-2025-67035, CVE-2025-67036, CVE-2025-67037, and CVE-2025-67038CVE-2025-67037Lantronix · EDS5000 series; Lantronix · G520 series; +1 moreRemote code execution – CVE-2026-32955, CVE-2026-32956, CVE-2026-32961, CVE-2025-67041, CVE-2025-67034, CVE-2025-67035, CVE-2025-67036, CVE-2025-67037, and CVE-2025-67038CVE-2025-67038Lantronix · E210 series; Lantronix · E220 series; +3 moreRemote code execution – CVE-2026-32955, CVE-2026-32956, CVE-2026-32961, CVE-2025-67041, CVE-2025-67034, CVE-2025-67035, CVE-2025-67036, CVE-2025-67037, and CVE-2025-67038CVE-2025-67039Lantronix · EDS3000PS seriesAuthentication bypass – CVE-2026-32960, CVE-2025-67039CVE-2025-67041Lantronix · EDS3000PS seriesRemote code execution – CVE-2026-32955, CVE-2026-32956, CVE-2026-32961, CVE-2025-67041, CVE-2025-67034, CVE-2025-67035, CVE-2025-67036, CVE-2025-67037, and CVE-2025-67038CVE-2025-70082Lantronix · EDS3000PS seriesDevice takeover – FSCT-2025-0021 (no CVE assigned), CVE-2026-32965, CVE-2025-70082CVE-2026-32955silex technology, Inc. · AMC Manager; silex technology, Inc. · SD-330ACRemote code execution – CVE-2026-32955, CVE-2026-32956, CVE-2026-32961, CVE-2025-67041, CVE-2025-67034, CVE-2025-67035, CVE-2025-67036, CVE-2025-67037, and CVE-2025-67038CVE-2026-32956silex technology, Inc. · AMC Manager; silex technology, Inc. · SD-330ACRemote code execution – CVE-2026-32955, CVE-2026-32956, CVE-2026-32961, CVE-2025-67041, CVE-2025-67034, CVE-2025-67035, CVE-2025-67036, CVE-2025-67037, and CVE-2025-67038CVE-2026-32957silex technology, Inc. · AMC Manager; silex technology, Inc. · SD-330ACArbitrary file upload – CVE-2026-32957CVE-2026-32958silex technology, Inc. · AMC Manager; silex technology, Inc. · SD-330ACFirmware tampering – CVE-2026-32958CVE-2026-32959silex technology, Inc. · AMC Manager; silex technology, Inc. · SD-330ACInformation disclosure – CVE-2026-32959CVE-2026-32960silex technology, Inc. · AMC Manager; silex technology, Inc. · SD-330ACAuthentication bypass – CVE-2026-32960, CVE-2025-67039CVE-2026-32961silex technology, Inc. · AMC Manager; silex technology, Inc. · SD-330ACRemote code execution – CVE-2026-32955, CVE-2026-32956, CVE-2026-32961, CVE-2025-67041, CVE-2025-67034, CVE-2025-67035, CVE-2025-67036, CVE-2025-67037, and CVE-2025-67038CVE-2026-32962silex technology, Inc. · AMC Manager; silex technology, Inc. · SD-330ACConfiguration tampering – CVE-2026-32962, CVE-2026-32964CVE-2026-32963silex technology, Inc. · AMC Manager; silex technology, Inc. · SD-330ACClient-side code execution – CVE-2026-32963CVE-2026-32964silex technology, Inc. · AMC Manager; silex technology, Inc. · SD-330ACConfiguration tampering – CVE-2026-32962, CVE-2026-32964CVE-2026-32965silex technology, Inc. · AMC Manager; silex technology, Inc. · SD-330ACDevice takeover – FSCT-2025-0021 (no CVE assigned), CVE-2026-32965, CVE-2025-70082
Vendors
LantronixResearchers at Forescout Vedere Labs uncovered 22 vulnerabilities, labeled BRIDGE:BREAK, in Lantronix and Silex serial-to-IP converters that put nearly 20,000 devices online at risk of hijack and data tampering.SilexResearchers at Forescout Vedere Labs uncovered 22 vulnerabilities, labeled BRIDGE:BREAK, in Lantronix and Silex serial-to-IP converters that put nearly 20,000 devices online at risk of hijack and data tampering.
Products
EDS3000PS SeriesAt a high level, as many as eight security flaws have been discovered in Lantronix products (EDS3000PS Series and EDS5000 Series) and 14 in Silex SD330-AC.EDS5000 SeriesAt a high level, as many as eight security flaws have been discovered in Lantronix products (EDS3000PS Series and EDS5000 Series) and 14 in Silex SD330-AC.SD330-ACForescout identified 22 vulnerabilities in Lantronix (EDS3000PS/EDS5000) and Silex (SD330-AC) serial-to-IP converters.