
Exploit Attempts Target GPUStack Authentication Bypass (CVE-2026-102895)
Summary
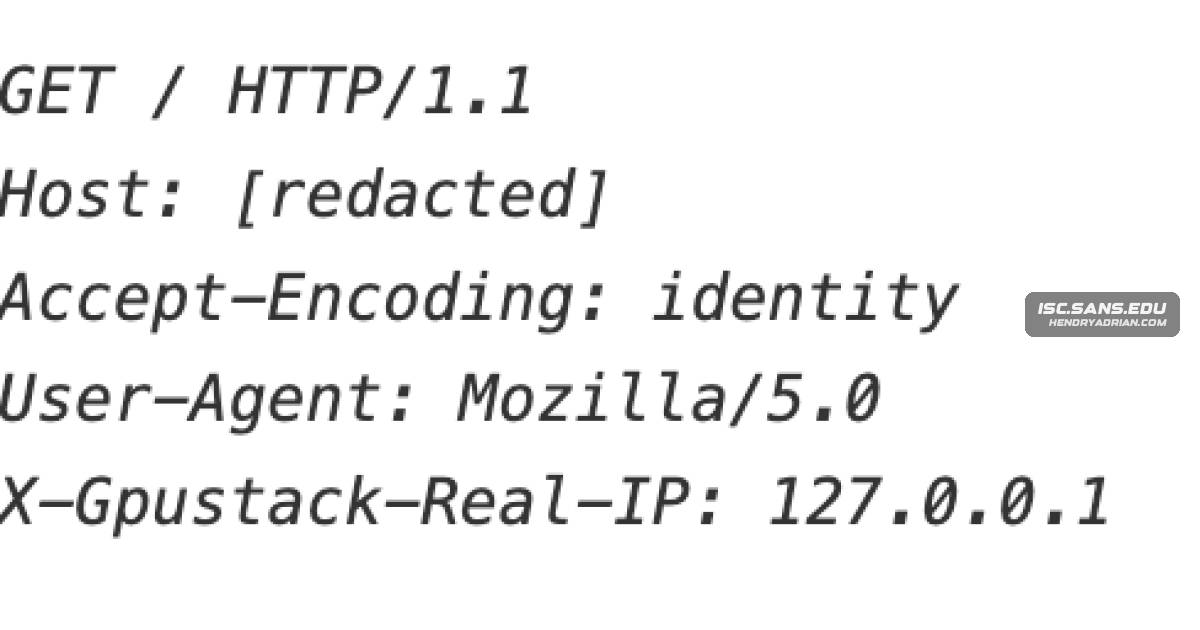
Observed requests spoof the X-Gpustack-Real-IP header as 127.0.0.1 to bypass GPUStack authentication. The article says versions before 2.2.0 are affected; it does not establish that the attempts succeeded.
Key points
- The vulnerability affects GPUStack versions before 2.2.0, released at the end of June.
- GPUStack trusts X-Gpustack-Real-IP to identify the request source and bypasses authentication when it indicates loopback (127.0.0.1).
- Observed requests set X-Gpustack-Real-IP to 127.0.0.1; the article does not confirm successful access.
- The observed requests originated from 144.91.73.103.
- The same IP also probed AI-related paths, including /v1/models, /v1/messages, and /models.
Article Details
- Vulnerability Types
- Authentication bypass
- Affected Versions
- GPUStack versions prior to 2.2.0
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 144[.]91[.]73[.]103 | Source IP of observed requests attempting to exploit the GPUStack authentication bypass. |