
DifyTap Flaws Could Expose Cross-Tenant AI Chats and Files; One Fix Pending
Summary
Researchers say four Dify flaws could expose AI chats, internal APIs, and files across tenants. Dify 1.14.2 fixes most issues; a fix for CVE-2026-41948 is pending.
Key points
- Zafran researchers disclosed four Dify vulnerabilities, collectively named DifyTap; they say three have cross-tenant impact.
- The flaws could expose private AI conversations, allow access to internal Plugin Daemon API endpoints, and permit reading other users’ or tenants’ files.
- CVE-2026-41947, CVE-2026-41949, and CVE-2026-41950 are authorization bypass flaws; CVE-2026-41948 is a path traversal flaw.
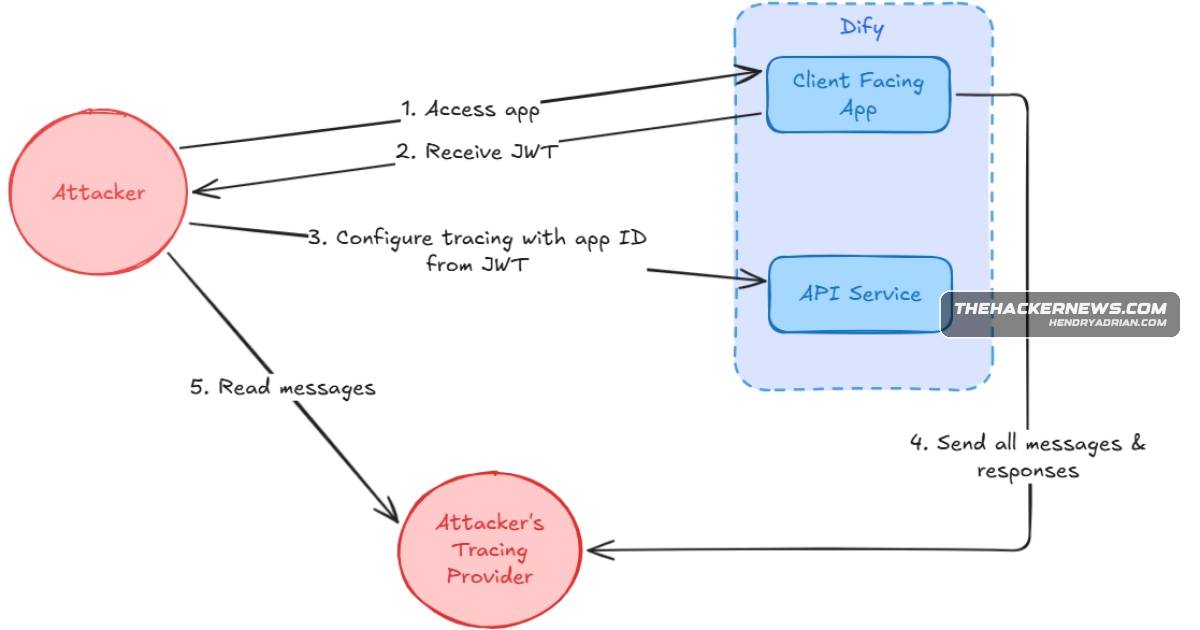
- Researchers say missing tenant ownership checks could let an attacker redirect application messages and responses to an attacker-controlled LLM tracing provider.
- Dify 1.14.2 addresses all four reported flaws except CVE-2026-41948, for which a fix is expected in a future release.
- Zafran also reported that Dify’s PDFium version was vulnerable to CVE-2024-5846, a use-after-free flaw that could be triggered with a crafted PDF.
Article Details
- Vulnerability Types
- Authorization bypass
- Path traversal
- Use-after-free
- Severity
- Two Dify vulnerabilities were described as critical. Reported CVSS scores: 9.4, 9.1, 8.8, 7.5/5.9, and 6.5.
- Exploitation Status
- unknown
- Exploit Availability
- unknown
- Patch Status
- partial