cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · thehackernews.com

F5 Patches Two Critical NGINX Flaws That Could Enable Remote Code Execution

F5 patched two critical NGINX vulnerabilities that could allow remote unauthenticated code execution under specific configurations. No confirmed in-the-wild exploitation was reported; F5 also provided temporary mitigations.
Jun 18, 2026
Vulnerability & Exploit · bleepingcomputer.com

F5 Issues Out-of-Band Patches for Critical NGINX Vulnerabilities

F5 issued out-of-band fixes for critical NGINX flaws that may enable denial of service or, under certain conditions, code execution. It also patched two high-severity NGINX Gateway Fabric flaws and provided mitigations.

Jun 18, 2026
Vulnerability & Exploit · bleepingcomputer.com

Apple Patches Bluetooth Eavesdropping Flaw in Beats Studio Buds

Apple’s Beats Firmware Update 1B211 patches CVE-2025-20701, which could let a nearby attacker listen through an unpaired Beats Studio Buds microphone. Researchers say chaining related flaws could enable broader device control.

Jun 18, 2026
Vulnerability & Exploit · thehackernews.com

Microsoft Developing Patch for RoguePlanet Defender Zero-Day (CVE-2026-50656)

Microsoft is developing a patch for RoguePlanet, a privilege-escalation flaw in its Malware Protection Engine tracked as CVE-2026-50656. Researcher Chaotic Eclipse says the race-condition exploit can grant SYSTEM privileges; Microsoft has not confirmed the exploit’s use

Jun 18, 2026
Vulnerability & Exploit · cyberscoop.com

Researchers Report Active Exploitation of Patched FortiSandbox Flaws

Researchers reported active exploitation of FortiSandbox flaws CVE-2026-39808 and CVE-2026-39813, patched in April, and attempts against CVE-2026-25089. They observed 49 events from 11 IPs; Fortinet has not confirmed exploitation.

Jun 17, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Orders Federal Agencies to Patch Actively Exploited Joomla JCE Flaw

CISA says attackers are actively exploiting CVE-2026-48907, an unauthenticated PHP code execution flaw in the Joomla JCE plugin, and ordered federal agencies to patch by Friday. JCE Pro 2.9.99.6 or later fixes the flaw.

Jun 17, 2026
Vulnerability & Exploit · securityweek.com

Rockwell Automation Patches Vulnerabilities in ICS Products

Rockwell patched vulnerabilities across its ICS controllers and software, including flaws that could enable denial of service, authentication bypass, privileged operations, or account takeover. The company said none of the newly patched flaws had been targeted.

Jun 17, 2026
Vulnerability & Exploit · bleepingcomputer.com

Microsoft Is Developing a Patch for the RoguePlanet Defender Zero-Day

Microsoft says it is developing a fix for RoguePlanet (CVE-2026-50656), an elevation-of-privilege flaw in Microsoft Defender. Researcher Nightmare Eclipse claims a race-condition exploit can spawn SYSTEM-level command prompts on Windows 10 and 11.

Jun 17, 2026
Vulnerability & Exploit · securityweek.com

Joomla and LiteSpeed cPanel Vulnerabilities Exploited in Attacks

Attackers are exploiting Joomla JCE CVE-2026-48907 for code execution and LiteSpeed cPanel CVE-2026-54420 for privilege escalation. Both flaws have fixes; CISA added them to its Known Exploited Vulnerabilities catalog.

Jun 17, 2026
Vulnerability & Exploit · thehackernews.com

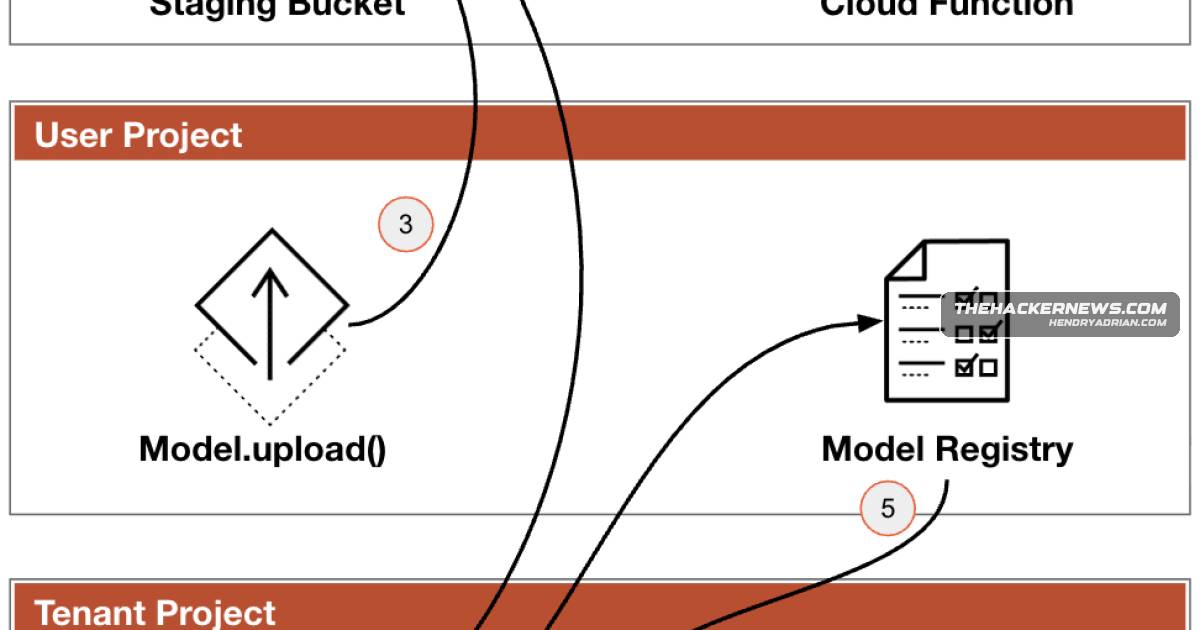
Vertex AI SDK Flaw Let Attackers Hijack Model Uploads Through Bucket Squatting

Unit 42 found that predictable staging-bucket names in the Vertex AI Python SDK let attackers replace uploaded models and execute code in serving containers. Google fixed the flaw in version 1.148.0; Unit 42 reported no in-the-wild exploitation.

Jun 17, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Orders Federal Agencies to Patch Actively Exploited LiteSpeed cPanel Flaw

CISA ordered federal agencies to patch an actively exploited LiteSpeed cPanel plugin flaw within three days. The article identifies it as CVE-2026-48172 but also inconsistently references CVE-2026-54420.

Jun 16, 2026
Vulnerability & Exploit · bleepingcomputer.com

FortiSandbox Flaws Reportedly Exploited as Fortinet Releases Patches

Defused reports exploitation of three critical FortiSandbox flaws that can enable unauthenticated privilege escalation and remote code execution. Fortinet released patches; the company had not confirmed the reports to BleepingComputer.

Jun 16, 2026
Vulnerability & Exploit · securityweek.com

Cisco Reports Limited Exploitation of SD-WAN Zero-Day

Cisco says attackers exploited CVE-2026-20262, an arbitrary file-write flaw in Catalyst SD-WAN Manager, in limited attacks. Exploitation requires valid credentials with write access; CISA added it to the KEV catalog.

Jun 16, 2026
Vulnerability & Exploit · thehackernews.com

CVE-2026-25177: Active Directory Flaw Can Enable Privilege Escalation Through SPN Abuse

The article describes CVE-2026-25177 as a high-severity Active Directory flaw that can enable privilege escalation through SPN manipulation and Kerberos abuse, and recommends patching alongside least-privilege controls and service-account governance.

Jun 15, 2026
Vulnerability & Exploit · bleepingcomputer.com

SimpleHelp CVE-2026-48558 Enables Unauthenticated Technician Account Creation

CVE-2026-48558 lets unauthenticated attackers create privileged SimpleHelp Technician accounts without MFA under specific OIDC settings. Versions 5.5.16 and 6.0RC2 fix the flaw; researchers reported no evidence of active exploitation.

Jun 15, 2026
Vulnerability & Exploit · thehackernews.com

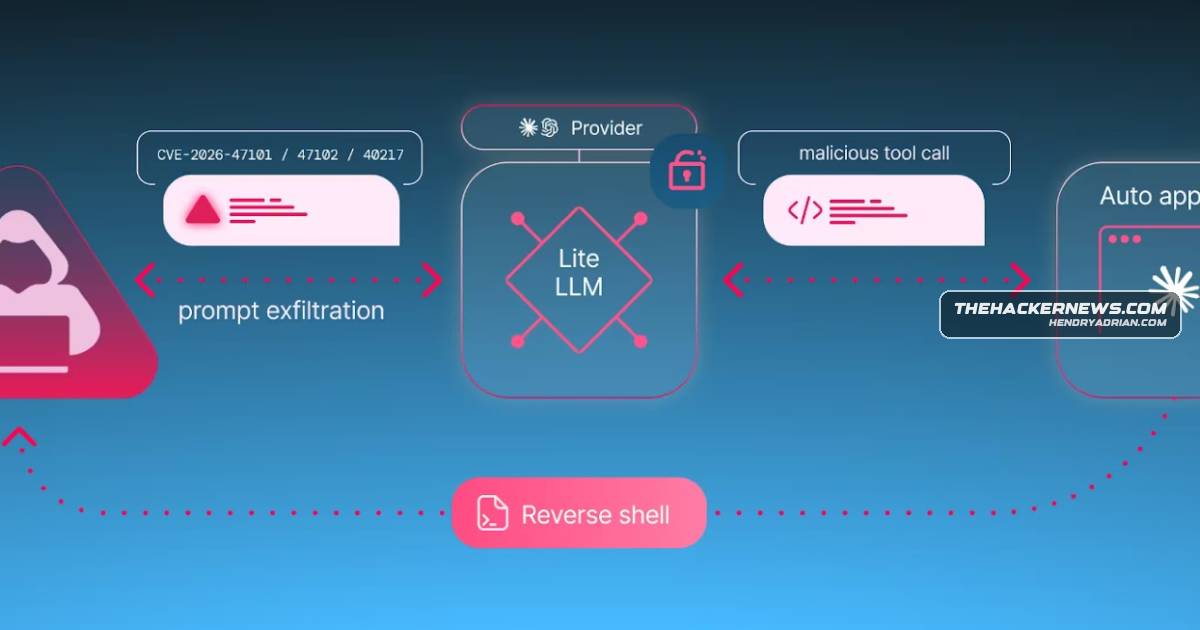
Three LiteLLM Vulnerabilities Could Let Low-Privilege Users Take Over AI Gateways

Obsidian Security disclosed three LiteLLM flaws that can let a low-privilege user gain proxy-admin access and execute code, exposing secrets and enabling response tampering. BerriAI fixed the chain in v1.83.14-stable; the chain was not reported exploited in the wild.

Jun 15, 2026
Vulnerability & Exploit · bleepingcomputer.com

Cisco Patches Exploited Catalyst SD-WAN Manager Zero-Day

Cisco patched CVE-2026-20262, a flaw affecting all Catalyst SD-WAN Manager deployment types. Cisco confirmed exploitation; authenticated remote attackers could upload or overwrite files through an API and escalate to root.

Jun 15, 2026
Vulnerability & Exploit · bleepingcomputer.com

SearchLeak Flaw Could Expose Microsoft 365 Copilot Data Through Crafted Links

Researchers said the SearchLeak chain could let a crafted link expose Microsoft 365 Copilot Enterprise emails, calendar details, and files via prompt injection, a rendering race, and Bing SSRF. Microsoft patched it as critical CVE-2026-42824.

Jun 15, 2026
Vulnerability & Exploit · thehackernews.com

Palo Alto Reports Limited Active Exploitation of PAN-OS Flaw CVE-2026-0257

Palo Alto Networks reports limited active exploitation of a PAN-OS authentication bypass affecting GlobalProtect portals and gateways. No post-access activity or lateral movement has been identified; the company shared IoCs and advised customers to review logs.

Jun 15, 2026
Vulnerability & Exploit · thehackernews.com

Critical Splunk Enterprise Flaw Could Enable Unauthenticated Remote Code Execution

CVE-2026-20253 lets unauthenticated users write or truncate files through Splunk Enterprise’s PostgreSQL sidecar. Researchers described a path to potential remote code execution; Splunk has released fixes, and Splunk Cloud is unaffected.

Jun 13, 2026
Vulnerability & Exploit · bleepingcomputer.com

phpBB Fixes Decade-Old Authentication Bypass Affecting Forum Accounts

Aikido found a decade-old phpBB authentication bypass that can let attackers log in as any user with one HTTP request. phpBB fixed 3.x in 3.3.17; affected 4.x builds have no safe release yet.

Jun 12, 2026
Vulnerability & Exploit · cyberscoop.com

Researchers Link ShinyHunters Extortion Campaign to Oracle PeopleSoft Zero-Day

Mandiant and Google say ShinyHunters exploited CVE-2026-35273 in Oracle PeopleSoft, potentially exposing more than 100 organizations. Nottingham confirmed student-data theft; Oracle issued mitigation guidance but has not released a patch.

Jun 12, 2026
Vulnerability & Exploit · securityweek.com

CISA Flags Ivanti Sentry Flaw as Exploited, but Ivanti Cites Honeypot Attempts

CISA added CVE-2026-10520 to its KEV catalog after attempted exploitation was observed on honeypots, while Ivanti says it has no evidence of in-the-wild exploitation. The flaw allows unauthenticated remote root command execution; patches are available.

Jun 12, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Gives Federal Agencies Three Days to Patch Actively Exploited Ivanti Sentry Flaw

CISA confirmed active exploitation of Ivanti Sentry flaw CVE-2026-10520 and gave federal agencies three days to patch. Shadowserver reported widespread attempts and warned unpatched exposed systems are likely compromised; Ivanti had initially said it had no exploitation

Jun 12, 2026
PreviousPage 45 of 65 Next
© 2026 cyber.hendryadrian.com