
n8n Fixes Token-Exchange Flaw That Could Log Users Into the Wrong Account
Summary
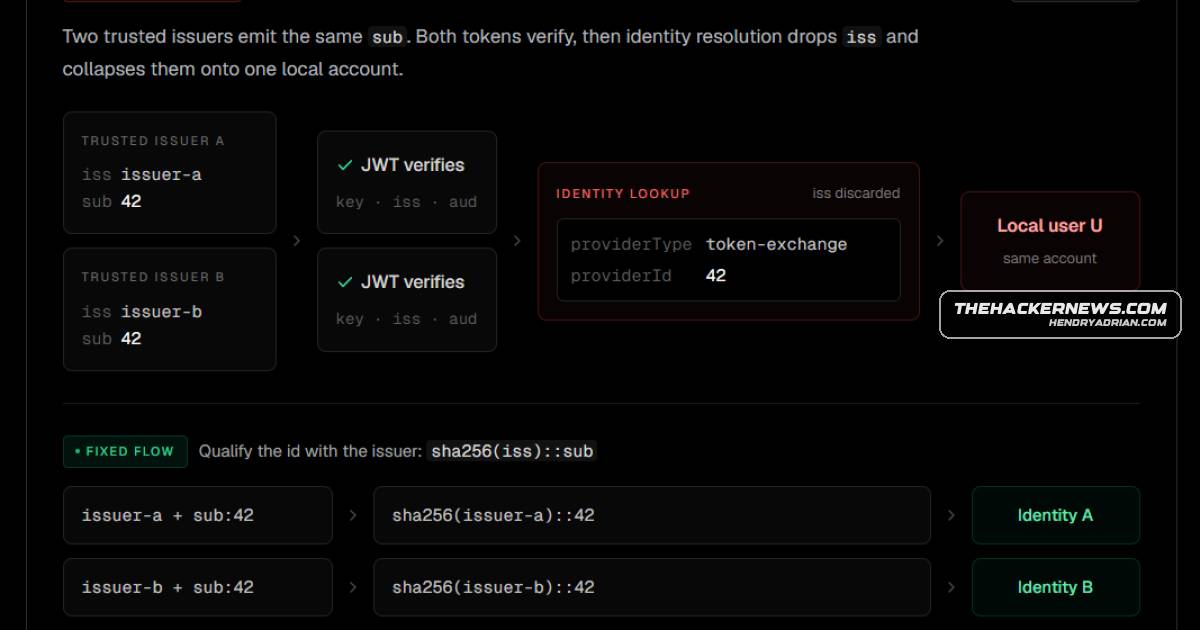
n8n fixed CVE-2026-59208, which could match a trusted issuer’s JWT to another issuer’s local user by subject alone. Affected deployments should upgrade or disable token exchange or reduce trusted issuers.
Key points
- On Enterprise instances trusting multiple external issuers, n8n’s token exchange matched JWTs by the sub claim but ignored iss.
- A valid token from one issuer with a subject matching a user under another issuer could log in as that user.
- The issue affects releases below 2.27.4 and version 2.28.0; fixes landed in 2.27.4 and 2.28.1.
- The risk applies when token exchange is enabled and at least two external issuers are trusted.
- n8n recommends upgrading; interim steps include disabling token exchange or reducing the trusted issuer list, though the advisory says these measures do not fully remediate risk.
- The article says the advisory does not explain how an attacker obtains a token or whether an ordinary user can influence its sub value. CISA’s assessment recorded no exploitation, and the article found no public proof of concept.
Article Details
- Vulnerability Types
- Token-exchange identity-binding flaw: n8n matched users by the JWT sub claim without checking the iss claim.
- Severity
- High (CVSS 4.0 7.6); NVD assessed it as medium (CVSS 3.1 6.8).
- Affected Versions
- n8n releases below 2.27.4
- n8n 2.28.0
- Exploitation Status
- not_reported
- Exploit Availability
- none_reported
- Patch Status
- available
- Workarounds
- Disable token exchange.
- Reduce the trusted issuer list to a single issuer; n8n says this short-term measure does not fully remediate the risk.
MITRE ATT&CK
CVE
CVE-2026-54305n8n-io · n8nTwo weeks before the June 24 fix, the maintainers patched CVE-2026-54305, another Enterprise-only flaw.CVE-2026-59208n8n-io · n8nn8n fixed a token-exchange identity-binding flaw, CVE-2026-59208, that could log an Enterprise user into the wrong account when multiple external issuers were trusted.