
Researchers Say Java4Shell Can Enable Unauthenticated RCE in Jira, Jenkins and More
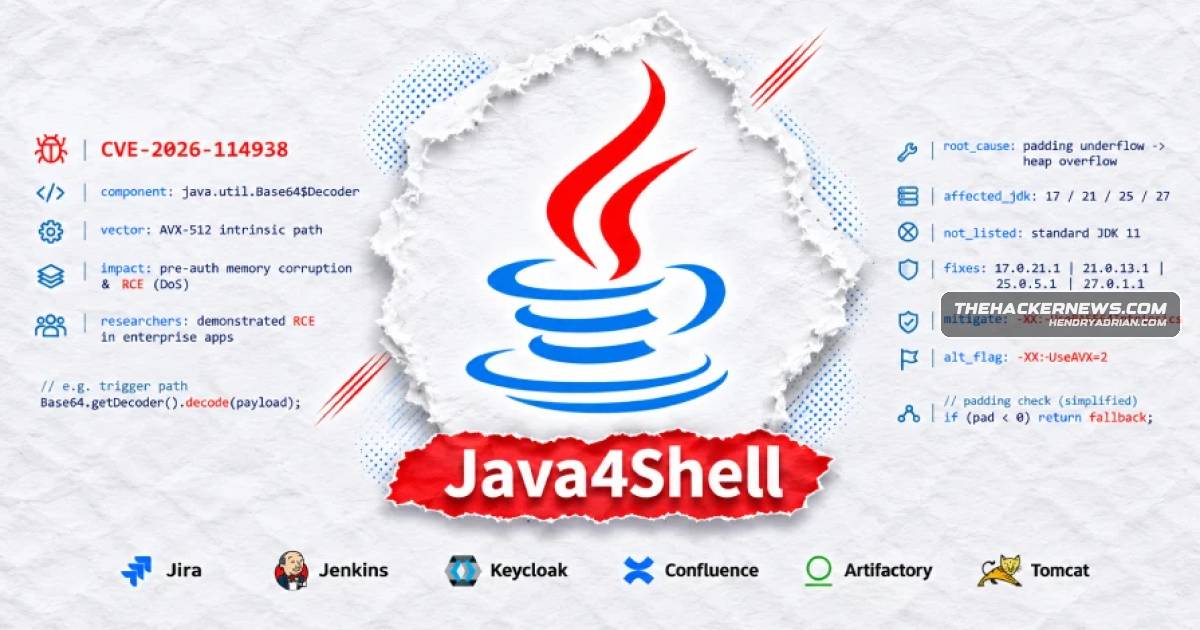
Summary
CVE-2026-114938 affects Java’s AVX-512 Base64 decoder and may enable unauthenticated code execution in several applications, researchers say. Oracle, OpenJDK and other vendors released fixes; Red Hat updates were pending.
Key points
- The flaw affects specified Java versions on x86-64 systems with AVX-512 VBMI; Java 8 and Java 11 are generally unaffected, with a Java 8 Performance Pack exception.
- A malformed Base64 string can cause the optimized decoder to write 62 or 63 bytes beyond its output buffer.
- Researchers say they achieved unauthenticated code execution in several applications under default settings, including Keycloak, Jira, Confluence, Artifactory, Jenkins and PingFederate; other listed applications required login.
- The researchers’ exploit code was not public. Other labs reproduced crashes or memory corruption, but not remote code execution; the article reports no known exploitation in the wild.
- Oracle and OpenJDK released fixes, and Amazon Corretto and Azul Zulu updates were also available. Red Hat fixes were still pending.
- The article advises updating Java, restarting services, and rebuilding and redeploying container images; temporary JVM flags were also reported to stop the overflow in tested versions.
Article Details
- Vulnerability Types
- Out-of-bounds memory write (buffer overflow) in Java's AVX-512 VBMI Base64 decoder
- Out-of-bounds memory read (JavaBleed)
- Remote code execution
- Severity
- Calif rates it 9.2/10 under CVSS 4.0; Oracle rates it 8.1/10 under CVSS 3.1; Red Hat's preliminary rating is 9.8/10; Amazon rates it 8.8/10.
- Affected Versions
- Java 17.0.6 and later on the Java 17 line
- Java 21
- Java 25
- Java 27
- Java SE 8 Performance Pack 8u511b33-perf
- GraalVM for JDK 17.0.21.0.3
- GraalVM for JDK 21.0.13.0.3
- GraalVM Enterprise Edition 21.3.20.0.3
- Exploitation Status
- not_reported
- Exploit Availability
- claimed_or_private
- Patch Status
- partial
- Workarounds
- Use a proxy that waits for complete requests; the article says this blocks some attacks but not all.
MITRE ATT&CK
CVE
People
Vendors
Amazontoday by Oracle and the OpenJDK project, whose open-source code underpins Java builds from many vendors. Amazon has fixed its Corretto Java builds, but Red Hat is still preparing fixes for its own.AzulAzul's November update fixes the flaw in Zulu 17, 21, 25 and 27, according to its Zulu release notes.Microsoftand 27.0.1.1 this week, but their release pages do not specify what they fix. Eclipse Temurin, the Microsoft Build of OpenJDK, and BellSoft Liberica had not listed fixed builds when The Hacker News checked today.OracleTracked as CVE-2026-114938, the fix was released today by Oracle and the OpenJDK project, whose open-source code underpins Java builds from many vendors. Amazon has fixed its Corretto Java builds, but Red Hat is stillRed Hatopen-source code underpins Java builds from many vendors. Amazon has fixed its Corretto Java builds, but Red Hat is still preparing fixes for its own.SAPSAP released SapMachine 17.0.21.1, 21.0.13.1, 25.0.5.1, and 27.0.1.1 this week, but their release pages do not specify what they fix. Eclipse Temurin, the Microsoft Build of OpenJDK, and BellSoft Liberica had not listed
Products
Amazon CorrettoOpenJDK project, whose open-source code underpins Java builds from many vendors. Amazon has fixed its Corretto Java builds, but Red Hat is still preparing fixes for its own.Apache Kafka BrokerJira, Atlassian Confluence, JFrog Artifactory, Jenkins, and PingFederate, and with a login on Apache Kafka Broker, Apache Solr, Elasticsearch, Gerrit, and Spinnaker, Calif says in its technical write-up. TheApache SolrConfluence, JFrog Artifactory, Jenkins, and PingFederate, and with a login on Apache Kafka Broker, Apache Solr, Elasticsearch, Gerrit, and Spinnaker, Calif says in its technical write-up. The researchers' lists areAtlassian JiraA Java flaw called Java4Shell can let attackers without an account run their own code on Jira, Jenkins, Keycloak, and three other widely used applications, says Calif, the security research firm that disclosed it thisAzul ZuluAzul's November update fixes the flaw in Zulu 17, 21, 25 and 27, according to its Zulu release notes.ConfluenceThe attacks worked without a login under the default settings of Keycloak, Atlassian Jira, Atlassian Confluence, JFrog Artifactory, Jenkins, and PingFederate, and with a login on Apache Kafka Broker, Apache Solr,ElasticsearchJFrog Artifactory, Jenkins, and PingFederate, and with a login on Apache Kafka Broker, Apache Solr, Elasticsearch, Gerrit, and Spinnaker, Calif says in its technical write-up. The researchers' lists are incomplete,GerritJenkins, and PingFederate, and with a login on Apache Kafka Broker, Apache Solr, Elasticsearch, Gerrit, and Spinnaker, Calif says in its technical write-up. The researchers' lists are incomplete, and theyGraalVM8 and Java 11 do not contain it, but the Java SE 8 Performance Pack build 8u511b33-perf is affected. GraalVM for JDK 17.0.21.0.3, GraalVM for JDK 21.0.13.0.3, and GraalVM Enterprise Edition 21.3.20.0.3 are alsoJavaA Java flaw called Java4Shell can let attackers without an account run their own code on Jira, Jenkins, Keycloak, and three other widely used applications, says Calif, the security research firm that disclosed it thisJenkinsA Java flaw called Java4Shell can let attackers without an account run their own code on Jira, Jenkins, Keycloak, and three other widely used applications, says Calif, the security research firm that disclosed it thisJFrog Artifactorywithout a login under the default settings of Keycloak, Atlassian Jira, Atlassian Confluence, JFrog Artifactory, Jenkins, and PingFederate, and with a login on Apache Kafka Broker, Apache Solr, Elasticsearch,KeycloakA Java flaw called Java4Shell can let attackers without an account run their own code on Jira, Jenkins, Keycloak, and three other widely used applications, says Calif, the security research firm that disclosed it thisPingFederatedefault settings of Keycloak, Atlassian Jira, Atlassian Confluence, JFrog Artifactory, Jenkins, and PingFederate, and with a login on Apache Kafka Broker, Apache Solr, Elasticsearch, Gerrit, and Spinnaker, CalifSapMachineSAP released SapMachine 17.0.21.1, 21.0.13.1, 25.0.5.1, and 27.0.1.1 this week, but their release pages do not specify what they fix. Eclipse Temurin, the Microsoft Build of OpenJDK, and BellSoft Liberica had not listedSpinnakerand PingFederate, and with a login on Apache Kafka Broker, Apache Solr, Elasticsearch, Gerrit, and Spinnaker, Calif says in its technical write-up. The researchers' lists are incomplete, and they rate the flaw as