cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · databreachtoday.com

PHP2Shell PoCs Proliferate, but No Mass Exploitation Seen

Researchers have demonstrated exploits for the recently patched PHP2Shell vulnerabilities, and proof-of-concept code is proliferating. No mass exploitation in the wild has yet been seen, though attackers remain interested.
Oct 23, 2026
Vulnerability & Exploit · bleepingcomputer.com

PHP Shares Workaround for Unpatched RCE Vulnerability Affecting Unusual Configurations

PHP disclosed CVE-2026-115560, an RCE flaw requiring an unusual session-handler configuration. No patch is available; the PHP team recommends disabling session upload progress until a fix is released.

Oct 23, 2026
Vulnerability & Exploit · bleepingcomputer.com

HPE Patches Eight Critical RCE and Authentication Bypass Flaws in ArubaOS

HPE patched 72 ArubaOS vulnerabilities, including eight maximum-severity flaws affecting AOS-8 and AOS-10 that could allow unauthenticated remote code execution. HPE reported no known public exploit code or in-the-wild exploitation.

Oct 23, 2026
Vulnerability & Exploit · thehackernews.com

Arista Patches Actively Exploited VeloCloud Orchestrator SQL Injection Flaw

Arista says attackers are exploiting CVE-2026-114625, a critical SQL injection flaw in VeloCloud Orchestrator that lets a logged-in user gain operator privileges. Fixes are available for on-premises releases; hosted and dedicated systems are patched.

Oct 22, 2026
Vulnerability & Exploit · thehackernews.com

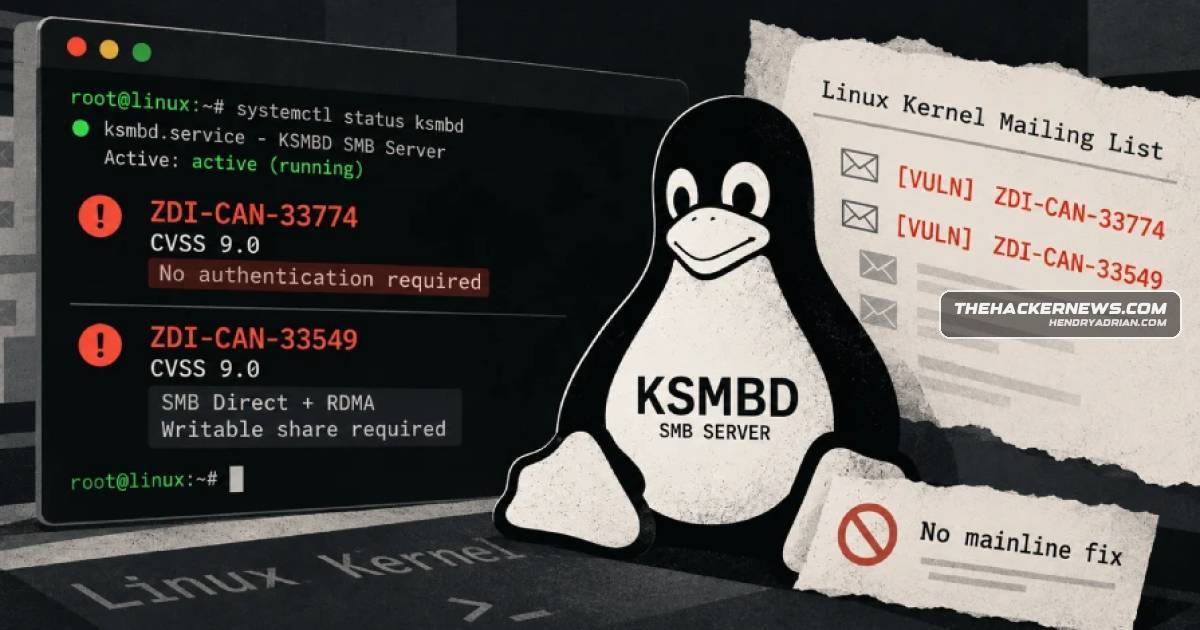
Two CVSS 9.0 KSMBD Remote Code Execution Flaws Reported Before Kernel Fixes

Two publicly reported KSMBD remote code execution flaws are rated CVSS 9.0. One requires no authentication; the other requires SMB Direct and RDMA. Neither had a named mainline kernel fix at the time of reporting.

Oct 22, 2026
Vulnerability & Exploit · securityweek.com

Signal Fixes Critical RingRTC Flaw That Could Keep Calls Active After Hang-Up

A critical RingRTC flaw could let a remote caller keep a victim’s audio and video tracks active after hang-up by flooding the call event queue. Signal fixed it in RingRTC 2.72.0 and advises users to update.

Oct 22, 2026
Vulnerability & Exploit · securityweek.com

Vendors and Agencies Issue Fixes and Warnings for Critical PHP2Shell Flaws

PHP fixed two critical PHP2Shell flaws that enable unauthenticated remote code execution. Vendors and agencies are assessing exposure, issuing patches and detections, and advising organizations to update; exploitation attempts were observed before and after disclosure.

Oct 22, 2026
Vulnerability & Exploit · levelblue.com

PHP2Shell Flaws Enable Pre-Authentication RCE in PHP Applications

PHP2Shell comprises two PHP Core flaws disclosed Oct. 21, 2026, that can enable unauthenticated RCE and memory disclosure. PHP 8.2–8.5 are affected below specified fixed releases; patching is the complete remediation.

Oct 22, 2026
Vulnerability & Exploit · socprime.com

GitLab Patches CVSS 10.0 RCE Flaw Affecting Self-Managed CE and EE

GitLab patched CVE-2026-110264, an unauthenticated RCE flaw caused by an integer overflow in regular-expression compilation. It affects self-managed CE and EE; no in-the-wild exploitation or public PoC has been confirmed.

Oct 22, 2026
Vulnerability & Exploit · socprime.com

Oracle Issues Out-of-Band Alert for Critical Java and GraalVM Flaw CVE-2026-91403

Oracle's Oct. 21, 2026 Security Alert covers an unauthenticated, remotely exploitable JSSE flaw in Java SE and GraalVM. Oracle rates it 9.1 CVSS and recommends patching affected releases.

Oct 22, 2026
Vulnerability & Exploit · securityweek.com

Splunk and SolarWinds Patch Multiple Security Flaws

Splunk and SolarWinds released updates fixing vulnerabilities across their products, including critical access-control and data-exposure flaws, remote code execution, denial-of-service, XSS, and SSRF issues.

Oct 22, 2026
Vulnerability & Exploit · thehackernews.com

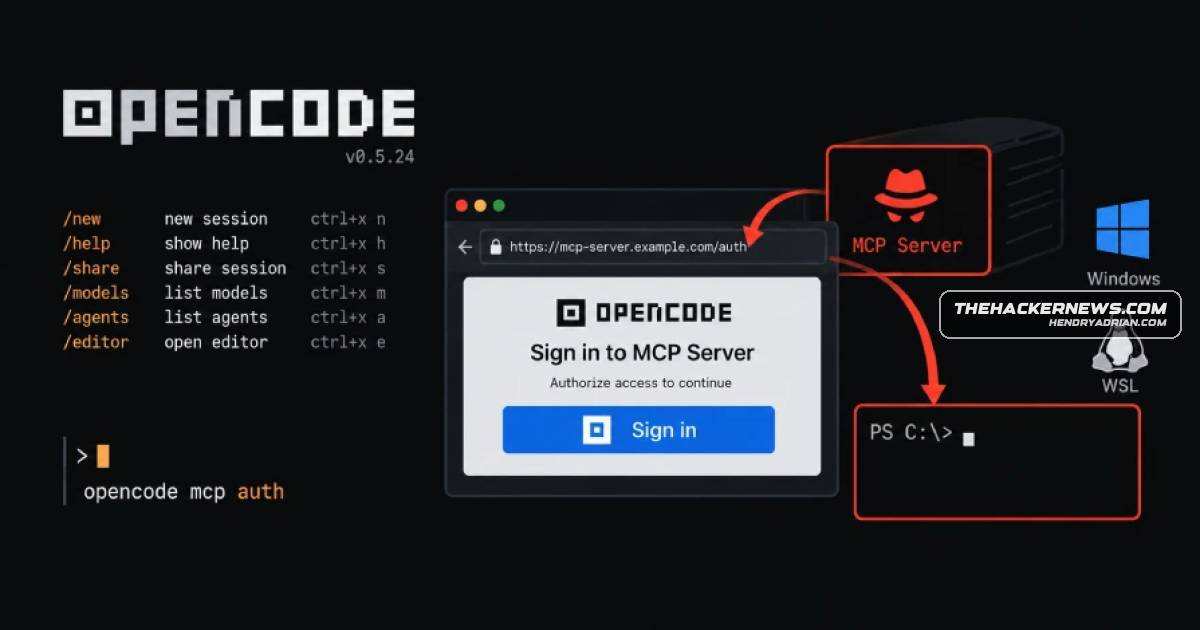
OpenCode Fixed Windows and WSL Flaw That Let Malicious MCP Servers Run Code During Sign-In

A flaw let a malicious or hijacked MCP server run PowerShell commands when OpenCode users signed in on Windows or WSL. Anomaly fixed it in version 1.18.33; Pillar Security reported no signs of exploitation.

Oct 22, 2026
Vulnerability & Exploit · securityweek.com

Cisco Patches 34 Vulnerabilities Across Multiple Products

Cisco patched 34 vulnerabilities across Expressway, IOS XR, Snort 3, Unified Communications and other products. The flaws include critical issues; Cisco says it is unaware of exploitation in the wild.

Oct 22, 2026
Vulnerability & Exploit · securityweek.com

PHP2Shell Exploitation Attempts Began Before Patches, Amazon Says

Amazon says PHP2Shell exploitation attempts began on October 17, before patches for two PHP RCE flaws were released on October 21. Researchers reported widespread attempts, while some said circulating PoCs failed to achieve RCE.

Oct 22, 2026
Vulnerability & Exploit · thehackernews.com

Node.js Updates Fix Brotli Decoder Flaw That Could Enable Remote Code Execution

Node.js fixed 10 flaws across supported release lines, including a Brotli decoder out-of-bounds write. A public proof of concept achieved code execution only on a deliberately weakened build; no in-the-wild exploitation was reported.

Oct 22, 2026
Vulnerability & Exploit · thehackernews.com

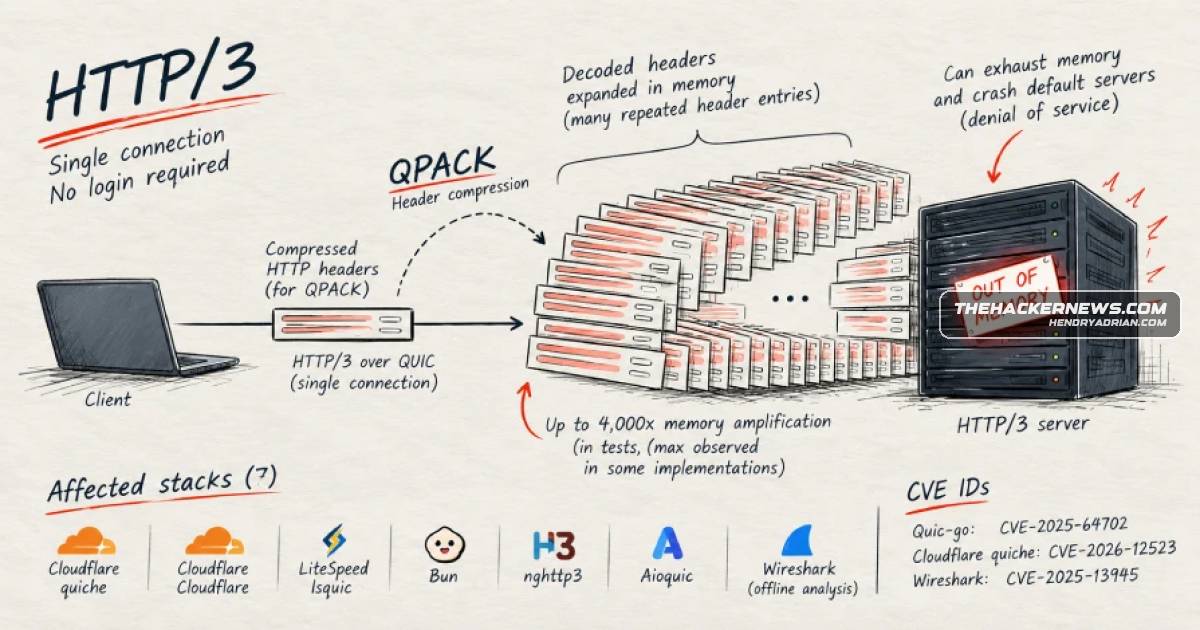
QPACK Flaws Enable HTTP/3 Server Crashes and Up to 4,000× Memory Amplification

FoxIO disclosed QPACK flaws affecting 7 of 10 tested HTTP/3 stacks. Unauthenticated requests can cause denial of service through memory amplification; fixes and interim mitigations vary by implementation.

Oct 22, 2026
Vulnerability & Exploit · thehackernews.com

PHP2Shell Flaws Exploited Before Public Disclosure, Amazon Says

Amazon says it detected a PHP2Shell exploit attempt on its honeypot on October 17, before public disclosure. The flaws enable pre-authentication remote code execution; agencies urge organizations to patch or take affected systems offline.

Oct 22, 2026
Vulnerability & Exploit · sysdig.com

PHP2Shell Flaws Enable Unauthenticated RCE; Exploitation Attempts Preceded Patches

PHP2Shell comprises two critical PHP core CVEs enabling unauthenticated remote code execution and memory disclosure. Attempts were reported before the fixes shipped; Sysdig details affected versions, detection, and mitigation.

Oct 22, 2026
Vulnerability & Exploit · aikido.dev

Node.js Patches Brotli Flaw That Can Enable Remote Code Execution

CVE-2026-111497 is an out-of-bounds write in Node.js’s Brotli decoder. Patched Node.js and Bun versions are available; researchers reported lab code execution, but no in-the-wild exploitation had been reported as of October 22, 2026.

Oct 22, 2026
Vulnerability & Exploit · fieldeffect.com

Plex2Shell Vulnerabilities Exploited to Deploy Miners and Proxy Malware

CISA added four Plex Media Server flaws to its KEV catalog after active exploitation enabled unauthenticated remote code execution. Attackers deployed cryptocurrency miners and proxy malware; upgrade to version 1.43.3.10861 or later.

Oct 22, 2026
Vulnerability & Exploit · security.com

PHP2Shell Flaws Enable Unauthenticated RCE on PHP Servers

PHP fixed two critical PHP2Shell use-after-free flaws (CVE-2026-109618/109619) enabling unauthenticated RCE via crafted requests. Details and PoCs circulated before fixes; patch versions and temporary mitigations are listed.

Oct 22, 2026
Vulnerability & Exploit · bleepingcomputer.com

Arista patches actively exploited VeloCloud Orchestrator zero-day

Arista released updates for an actively exploited critical SQL injection flaw in on-prem VeloCloud Orchestrator. Attackers with an authenticated account can gain operator privileges; Arista also recommends access restrictions, log review, and blocking observed IPs.

Oct 22, 2026
Vulnerability & Exploit · databreachtoday.com

PHP Disclosure Leaks Exposed Two Critical Remote-Code-Execution Flaws

PHP said leaks exposed details of two critical remote-code-execution flaws before patches were ready. Amazon telemetry recorded attempted exploitation before known leaks, while PHP reported no functional exploits at public disclosure.

Oct 22, 2026
Vulnerability & Exploit · databreachtoday.com

PHP2Shell Exploit Attempts Surge as Most Identified Servers Remain Unpatched

Cloudflare reported millions of PHP2Shell exploit attempts, but successful exploitation has not been confirmed. About 99% of identified affected hosts remained unpatched after 24 hours; agencies urge patching or taking exposed systems offline.

Oct 22, 2026
PreviousPage 16 of 65 Next
© 2026 cyber.hendryadrian.com