cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · thehackernews.com

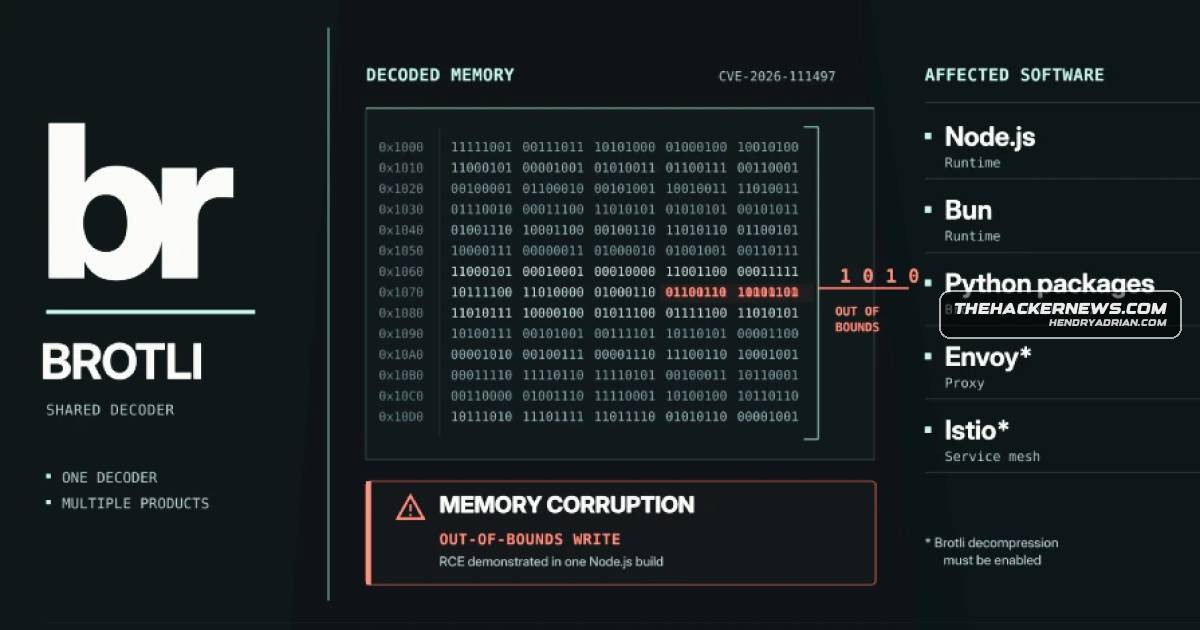
Brotli Flaw Affects Node.js, Bun, Python Packages and Envoy; RCE Shown on One Node.js Build

CVE-2026-111497 is a Brotli decoder memory-corruption flaw affecting multiple runtimes, packages, and proxies. Code execution was demonstrated on one unpatched Node.js build; no real-world exploitation has been reported.
Oct 24, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds Two Actively Exploited Collabora Online and Arista VeloCloud Flaws to KEV

CISA added two actively exploited flaws affecting Collabora Online Built-in CODE Server and Arista VeloCloud Orchestrator to its KEV catalog. Arista says exploitation is ongoing but provided no actor attribution or technical details.

Oct 24, 2026
Vulnerability & Exploit · sysdig.com

Sysdig details six Linux flaws, including public root exploit for ZDI-CAN-33367

Sysdig analyzes six ZDI-reported Linux flaws, including ZDI-CAN-33367, a local privilege-escalation bug with a public PoC reproduced by TuxCare. No in-the-wild exploitation was reported; fixes and exposure vary by flaw.

Oct 24, 2026
Vulnerability & Exploit · sysdig.com

Node2Shell (CVE-2026-111497): Exploit Scope, Detection and Mitigation

Node2Shell is an out-of-bounds write in Brotli that affects Node.js services decoding attacker-controlled data. Code execution was demonstrated in a limited setup; patching, reducing exposure and monitoring post-exploitation behavior are advised.

Oct 24, 2026
Vulnerability & Exploit · cert-agid.gov.it

PHP CVE-2026-115560 Could Enable RCE Under Uncommon Session Configuration

PHP's Security Team says CVE-2026-115560 could enable RCE under an uncommon combination of session settings. No patch was available as of Oct. 24, 2026; disabling session.upload_progress.enabled is the recommended mitigation.

Oct 24, 2026
Vulnerability & Exploit · thehackernews.com

Ruby Patches Three Onigmo Bugs Behind Four Critical GitLab Flaws

Ruby 4.0.9, 3.4.12, and 3.3.13 fix three Onigmo bugs behind four critical GitLab flaws. Apps compiling attacker-controlled regex patterns are affected; Ruby 3.2 and earlier will not receive fixes.

Oct 23, 2026
Vulnerability & Exploit · ic3.gov

FBI Urges Immediate Patching of Two Critical PHP Core Vulnerabilities

The FBI warns that CVE-2026-109618 and CVE-2026-109619 could enable remote code execution in PHP Core. It urges organizations to update affected installations, or take systems offline until mitigated, and monitor for suspicious activity.

Oct 23, 2026
Vulnerability & Exploit · rapid7.com

Metasploit Adds Exploit Modules for Langflow, OpenCTI, Grafana and More

Metasploit adds 11 modules, including six covering Langflow authentication-bypass and code-execution flaws, an unauthenticated OpenCTI RCE chain, and modules for 4gaBoards, Grafana, MongoDB and Apache Solr.

Oct 23, 2026
Vulnerability & Exploit · blog.qualys.com

Node.js Fixes 10 Vulnerabilities, Including Brotli Remote Code Execution Flaw

Node.js fixed 10 flaws across supported 22.x, 24.x and 26.x lines, including a Brotli decoder out-of-bounds write that may enable remote code execution. Qualys says most observed installations remain unpatched or unsupported and recommends upgrading runtimes.

Oct 23, 2026
Vulnerability & Exploit · securityweek.com

VulnCheck Reports PHP2Shell ASLR Bypass as Mirai Exploitation Attempts Emerge

Attackers have attempted to exploit PHP2Shell flaws, including in Mirai-related activity, but no successful compromise is confirmed. VulnCheck reports an ASLR-bypassing exploit, while researchers describe significant configuration hurdles and patching gaps.

Oct 23, 2026
Vulnerability & Exploit · cisa.gov

CISA Adds Actively Exploited Arista VeloCloud Orchestrator SQL Injection Flaw to KEV Catalog

CISA added CVE-2026-114625, an Arista VeloCloud Orchestrator SQL injection flaw, to its KEV Catalog based on evidence of active exploitation and urged organizations to prioritize remediation.

Oct 23, 2026
Vulnerability & Exploit · cisa.gov

CISA Adds Actively Exploited Collabora Online Vulnerability to KEV Catalog

CISA added CVE-2026-110447, an OS command injection vulnerability in Collabora Online’s built-in CODE Server, to its KEV Catalog based on evidence of active exploitation. Federal agencies must prioritize remediation under BOD 26-04.

Oct 23, 2026
Vulnerability & Exploit · thehackernews.com

PHP Warns of New RCE Risk in Unusual Session Configuration

PHP says CVE-2026-115560 may enable code execution in a narrowly configured application. It recommends disabling session upload progress until a routine fix; no exploitation of this issue has been reported.

Oct 23, 2026
Vulnerability & Exploit · socprime.com

Node.js Patches Brotli Flaw That Could Enable Remote Code Execution

Node.js patched CVE-2026-111497, an out-of-bounds write in its Brotli decoder. Attacker-controlled compressed data may reach it through direct APIs or HTTP responses; a PoC showed a crash and limited memory disclosure on standard builds, but no reliable RCE.

Oct 23, 2026
Vulnerability & Exploit · securityweek.com

Arista Patches Actively Exploited VeloCloud Orchestrator Zero-Day

Arista patched CVE-2026-114625, a critical SQL injection in on-prem VeloCloud Orchestrator that it says is actively exploited. Affected releases need updates; exploitation requires VCO web access and an authenticated session.

Oct 23, 2026
Vulnerability & Exploit · thehackernews.com

Pillow Flaw Enables Command Execution via an Attacker-Controlled Filename

Pillow versions 2.6.0–12.3.0 have an EPS filename-handling flaw that can pass attacker-controlled input to Ghostscript and enable command execution. Pillow 13.0.0 fixes this and other security flaws.

Oct 23, 2026
Vulnerability & Exploit · thehackernews.com

Researchers Demonstrate Node2Shell RCE on Official Node.js Build via Crafted Brotli Data

Imperva demonstrated code execution via crafted Brotli data on Node.js 24.22.0 for Linux arm64. The flaw affects the 22.x, 24.x and 26.x lines; Node.js released fixes, and no in-the-wild exploitation had been reported as of October 22.

Oct 23, 2026
Vulnerability & Exploit · thehackernews.com

V12 Details Three Critical x402 SDK Flaws; Fixes Shipped in August

V12 reported three critical x402 SDK flaws that could enable full-balance token payments, free resource access through a Solana facilitator, or relayed wallet sign-ins. Fixes shipped Aug. 18; no attacks have been publicly reported.

Oct 23, 2026
Vulnerability & Exploit · socradar.io

Arista VeloCloud Orchestrator SQL Injection Exploited in the Wild

Arista says attackers are exploiting CVE-2026-114625, an SQL injection flaw that lets an authenticated VeloCloud Orchestrator user gain local superuser operator privileges. Fixed releases are available for affected branches.

Oct 23, 2026
Vulnerability & Exploit · aikido.dev

Brotli CVE-2026-111497 Affects Python and HTTP Libraries

CVE-2026-111497 is an out-of-bounds write in vulnerable Brotli decoders, reachable through attacker-controlled compressed data and potentially enabling memory disclosure, crashes or code execution. Fixes are available for Brotli, Python packages and affected runtimes.

Oct 23, 2026
Vulnerability & Exploit · fieldeffect.com

PHP2Shell Exposure Extends to Embedded Products as PHP Discloses Separate Session Flaw

PHP disclosed CVE-2026-115560, a separate session-configuration flaw, as reporting on PHP2Shell exploitation attempts and scanning continues. Vendor assessments show PHP2Shell exposure in embedded products; successful exploitation remains deployment-dependent, with no |

Oct 23, 2026
Vulnerability & Exploit · bleepingcomputer.com

Abandoned Time4Popcorn Updater Exposed Millions to Potential Remote Code Execution

Time4Popcorn’s Windows and macOS updaters accepted unsigned executables over HTTP from popcorntimeupd[.]xyz, potentially enabling elevated code execution. Eye Security disabled the updater for many users, but warned Android users and others remain at risk.

Oct 23, 2026
Vulnerability & Exploit · darkreading.com

Experts Outline PHP2Shell Patch Challenges and Temporary Mitigations

Experts say PHP2Shell exploitation is accelerating while patching lags. They recommend inventorying PHP deployments, checking vendor fixes, hunting for compromise and isolating unpatchable systems; disabling session upload progress may temporarily mitigate CVE-2026-109

Oct 23, 2026
Vulnerability & Exploit · databreachtoday.com

PHP2Shell PoCs Proliferate as Patching Lags and Exploit Reports Conflict

PHP2Shell (CVE-2026-109618 and CVE-2026-109619) has prompted millions of exploit attempts and a surge in PoCs. PHP patches are available, but reports of successful in-the-wild exploitation remain conflicting.

Oct 23, 2026
PreviousPage 15 of 65 Next
© 2026 cyber.hendryadrian.com