cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1546 articles

Vulnerability & Exploit · thehackernews.com

CISA Confirms Active Exploitation of WordPress Core Flaw

CISA added WordPress Core flaw CVE-2026-119977 to its KEV catalog, citing active exploitation. The unauthenticated TOCTOU vulnerability can enable code execution during upgrades; patches are available, with a November 6 deadline for FCEB agencies.
Nov 4, 2026
Vulnerability & Exploit · bleepingcomputer.com

Zyxel Patches Zero-Day Used to Compromise Nearly 1,000 GS1900 Switches

Zyxel patched CVE-2026-107441, an unauthenticated command-execution flaw in ten GS1900 switch models. GreyNoise reported 996 devices compromised; Binarly found attackers bypassed earlier fixes. Zyxel released firmware updates October 22.

Nov 4, 2026
Vulnerability & Exploit · darkreading.com

Critical Rails Active Storage Flaw Could Allow Arbitrary File Access

A critical Rails Active Storage flaw involving ImageMagick can let unauthenticated attackers write arbitrary files and, in some configurations, read files. Patches and workarounds are available; exposed secrets should be rotated.

Nov 4, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Flags WordPress CVE-2026-119977 as Actively Exploited

CISA says attackers are exploiting a high-severity WordPress Core flaw that can enable remote code execution during upgrades. WordPress patched it in version 7.1.4; CISA urges defenders to prioritize updates.

Nov 4, 2026
Vulnerability & Exploit · bleepingcomputer.com

SonicWall Warns of Two Unpatched Flaws in End-of-Life GMS Software

SonicWall says two flaws affect GMS 9.5.2 and earlier, including unauthenticated access to internal files and privileged SQL injection. No patches will be released because the product is end-of-life; customers are urged to upgrade to NSM.

Nov 4, 2026
Vulnerability & Exploit · securityweek.com

Barracuda Patches Two Flaws That Could Enable Root Access to ESG Appliances

Barracuda patched an ESG authentication bypass and a command injection flaw that can be chained for root access. The flaws affect six products; the advisories do not say whether they have been exploited in the wild.

Nov 4, 2026
Vulnerability & Exploit · picussecurity.com

Node2Shell: Critical Brotli RCE Affects Node.js and Bun

Node2Shell (CVE-2026-111497) is a critical out-of-bounds write in Brotli decoding that can enable remote code execution. The article reports in-the-wild exploitation and lists fixes for Node.js and Bun.

Nov 3, 2026
Vulnerability & Exploit · thehackernews.com

Barracuda Flaws Could Be Chained to Bypass Authorization and Gain Root Access

Barracuda disclosed two flaws that could be chained to bypass authorization and gain root access on affected devices. Exploitation requires access to an affected product’s administrative interface; customers should install the latest firmware and patches.

Nov 3, 2026
Vulnerability & Exploit · securityweek.com

Node-RED CVE-2026-58115 Exploited to Deploy Linux Bots and Webshells

VulnCheck says attackers exploited unauthenticated Node-RED flaw CVE-2026-58115, using malicious flows to deploy Linux bots and persistent webshells. Siemens patched the flaw in SIMATIC IoT2050 Advanced 4.3.4.1 and later.

Nov 3, 2026
Vulnerability & Exploit · cisa.gov

CISA Adds Actively Exploited WordPress Core Vulnerability to KEV Catalog

CISA added CVE-2026-119977, a WordPress Core TOCTOU race condition vulnerability, to its KEV Catalog based on evidence of active exploitation. Federal agencies must prioritize remediation under BOD 26-04.

Nov 3, 2026
Vulnerability & Exploit · thehackernews.com

Linux TCP CVE-2026-98432 Rated Critical as Red Hat Ships Fixes and Ubuntu Updates Remain in Testing

CVE-2026-98432 is a Linux IPv4 TCP use-after-free rated 9.8; it may allow unauthenticated remote code execution. RHEL fixes are available, while Ubuntu updates remain in opt-in testing. No in-the-wild attacks have been reported.

Nov 3, 2026
Vulnerability & Exploit · thehackernews.com

BTCPay Server Urges Upgrade After Hot-Wallet Theft Reports

BTCPay Server says Bitcoin and Litecoin theft reports involve instances running 2.4.1 or earlier and a vulnerability patched in 2.4.2. It urges affected users to move to a fresh server and wallet; a link to an earlier flaw remains unclear.

Nov 3, 2026
Vulnerability & Exploit · labs.k7computing.com

Node.js Fixes 10 Vulnerabilities, Including Actively Exploited Node2Shell

Node.js October 2026 updates fix 10 flaws across 22.x, 24.x and 26.x, including the actively exploited critical Node2Shell Brotli flaw and DNS/TLS validation bugs. The update also removes trust in eight compromised eMudhra intermediate CA certificates.

Nov 3, 2026
Vulnerability & Exploit · thehackernews.com

Attackers Attempt to Exploit Unpatched CryptoPayment Gateway WordPress Flaw

Defused Cyber reports in-the-wild attempts to exploit CVE-2026-81648, an unauthenticated flaw in CryptoPayment Gateway for WordPress that can expose wallet credentials. No fix is available; site owners are advised to remove the plugin and rotate wallet keys.

Nov 3, 2026
Vulnerability & Exploit · thehackernews.com

VulnCheck Observes Attempts to Exploit Critical Siemens IoT2050 Flaw

VulnCheck observed attempts to exploit CVE-2026-58115 on Siemens SIMATIC IoT2050 Advanced devices, deploying Linux payloads and Node-RED command backdoors. Siemens fixed the flaw in version 4.3.4.1 or later.

Nov 3, 2026
Vulnerability & Exploit · fieldeffect.com

Barracuda ESG Flaws Can Be Chained to Gain Root Access

Two Barracuda vulnerabilities can be chained to bypass authorization and gain root access to ESG appliances. Exploitation requires access to the administrative interface; no exploitation has been reported in this case.

Nov 3, 2026
Vulnerability & Exploit · bleepingcomputer.com

Barracuda Patches Two Flaws That Could Enable Root Access to Devices

Barracuda disclosed two vulnerabilities that could enable root access to affected devices and released patches. Exploitation requires access to administrative interfaces; customers should restrict access and update firmware.

Nov 3, 2026
Vulnerability & Exploit · fieldeffect.com

Researchers Report Root-Level Execution via Linux TCP Flaw CVE-2026-98432

Researchers reported exploiting Linux kernel flaw CVE-2026-98432 to run commands as root on a server with an exposed MPTCP listener. Patches are available for some distributions; no in-the-wild exploitation had been publicly reported.

Nov 3, 2026
Vulnerability & Exploit · socprime.com

CVE-2026-112816 Enables Trusted-Client Impersonation in LXD and MicroCloud

An unauthenticated attacker with API access and a trusted client’s public certificate can impersonate it without its private key. Canonical issued LXD and MicroCloud fixes. Sources report no known exploitation; a public reproduction appeared Nov. 2, 2026.

Nov 2, 2026
Vulnerability & Exploit · thehackernews.com

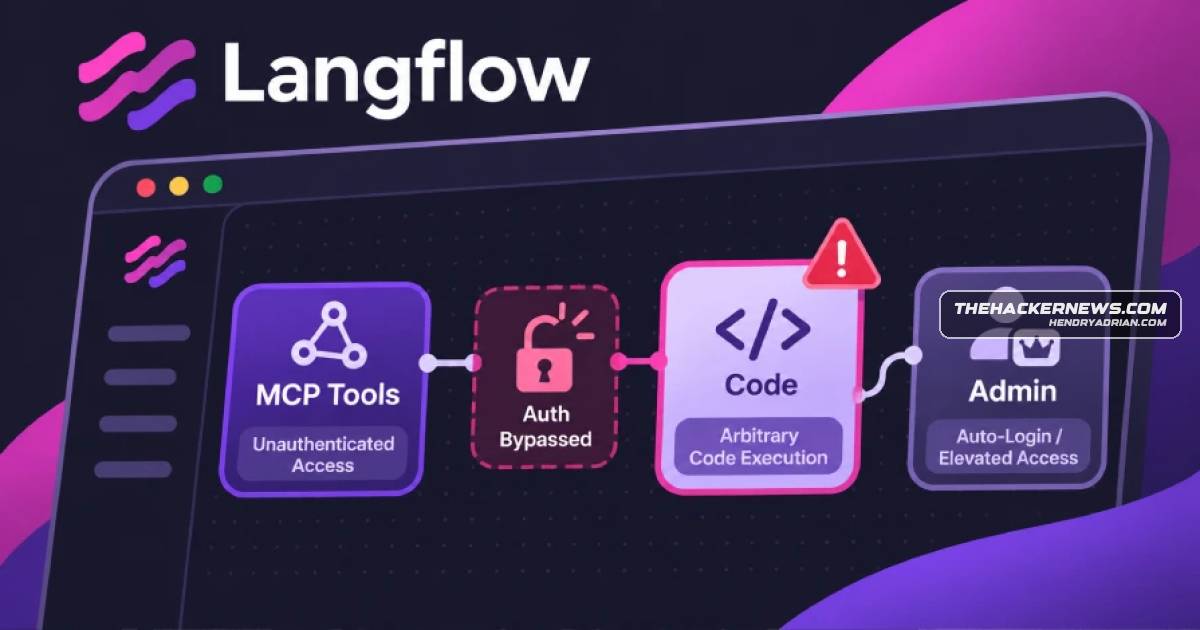
IBM Details Critical Langflow Flaws and Fix in Version 1.13.0

IBM says critical Langflow flaws affect versions 1.0.0–1.12.8 and may enable authentication bypass or remote code execution. Version 1.13.0 fixes them; a Metasploit module for CVE-2026-93680 lists MCP tools but does not execute code.

Nov 2, 2026
Vulnerability & Exploit · rapid7.com

Ivanti Connect Secure Zero-Days Exploited in the Wild; Fixes Available

Ivanti says two additional Connect Secure flaws were exploited in a chain with CVE-2026-104935, affecting a limited number of customers. Fixes are available; Rapid7 urges emergency patching and post-patch compromise checks.

Nov 2, 2026
Vulnerability & Exploit · securityweek.com

Ivanti Patches Two More Exploited Connect Secure Zero-Days

Ivanti patched two Connect Secure zero-days in a three-flaw chain the company says was exploited against a limited number of customers. CISA added the flaws to KEV; affected users must upgrade.

Nov 2, 2026
Vulnerability & Exploit · esentire.com

PHP2Shell Flaws Face Active Exploitation as Patches Roll Out

Two critical PHP flaws, CVE-2026-109618 and CVE-2026-109619, allow unauthenticated remote code execution. Exploitation attempts are reported, and code execution has been observed on honeypots. Patches are available; eSentire reports no customer compromises found so far.

Nov 2, 2026
Vulnerability & Exploit · aikido.dev

Linux Kernel TCP Flaw CVE-2026-98432 May Enable Remote Code Execution

CVE-2026-98432 is a Linux kernel IPv4 TCP use-after-free affecting kernel 4.4 and later. Anthropic reports a root-level exploit under MPTCP conditions; vendors have issued fixes, and no in-the-wild attacks were reported as of Oct. 29.

Nov 2, 2026
PreviousPage 10 of 65 Next
© 2026 cyber.hendryadrian.com