
IBM Details Critical Langflow Flaws and Fix in Version 1.13.0
Summary
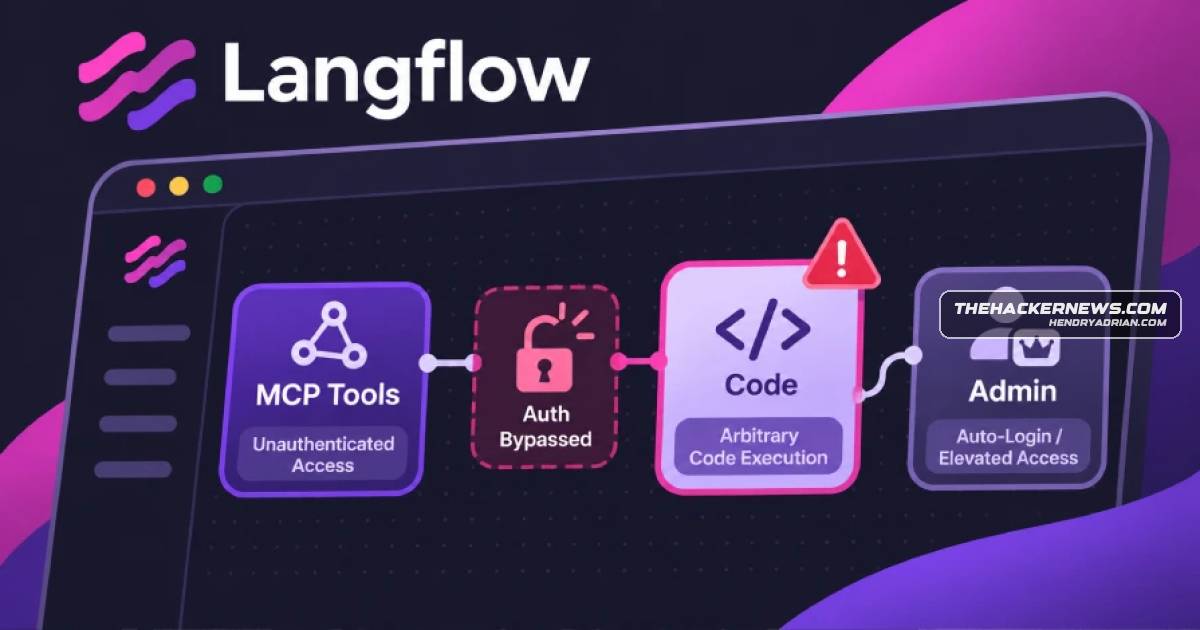
IBM says critical Langflow flaws affect versions 1.0.0–1.12.8 and may enable authentication bypass or remote code execution. Version 1.13.0 fixes them; a Metasploit module for CVE-2026-93680 lists MCP tools but does not execute code.
Key points
- IBM says Langflow versions 1.0.0 through 1.12.8 are affected and identifies version 1.13.0 as the fix; it offers no workaround for servers unable to upgrade.
- A Metasploit module for CVE-2026-93680 connects to a Langflow MCP endpoint without credentials, starts a session, and lists available tools. The module does not run code or commands on the server.
- The module author lists versions 1.5.0 through 1.11.4 as affected, narrower than IBM's range; the module was tested on version 1.8.4 with automatic login enabled.
- LANGFLOW_AUTO_LOGIN is enabled by default in version 1.12.8 and logs users in as superusers. Langflow 1.13.0 disables it by default; IBM does not state whether servers with the setting off are affected by the incomplete-remediation flaw.
- IBM also published records for 29 other Langflow flaws. One, CVE-2026-104339, could allow unauthenticated remote code execution and is rated 9.8 by IBM.
Article Details
- Vulnerability Types
- Authentication bypass
- Remote code execution
- Severity
- Two flaws are described as critical; IBM rates CVE-2026-104339 9.8.
- Affected Versions
- Langflow 1.0.0–1.12.8
- Langflow 1.5.0–1.11.4 (the Metasploit module author's stated affected range for CVE-2026-93680)
- Exploitation Status
- unknown
- Exploit Availability
- public_exploit
- Patch Status
- available
CVE
CVE-2026-104339for 29 other Langflow flaws and named versions 1.12.4 and 1.12.5 as their fixes. One of them, CVE-2026-104339, could also let an attacker with no account run arbitrary code, and IBM rates it 9.8. None of the 33CVE-2026-93680A module in the public Metasploit Framework already cites CVE-2026-93680, the authentication bypass. It connects to a Langflow server's MCP endpoint without credentials, starts a session, and lists the tools the server