cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · fieldeffect.com

Researchers Report Root-Level Execution via Linux TCP Flaw CVE-2026-98432

Researchers reported exploiting Linux kernel flaw CVE-2026-98432 to run commands as root on a server with an exposed MPTCP listener. Patches are available for some distributions; no in-the-wild exploitation had been publicly reported.
Nov 3, 2026
Vulnerability & Exploit · socprime.com

CVE-2026-112816 Enables Trusted-Client Impersonation in LXD and MicroCloud

An unauthenticated attacker with API access and a trusted client’s public certificate can impersonate it without its private key. Canonical issued LXD and MicroCloud fixes. Sources report no known exploitation; a public reproduction appeared Nov. 2, 2026.

Nov 2, 2026
Vulnerability & Exploit · thehackernews.com

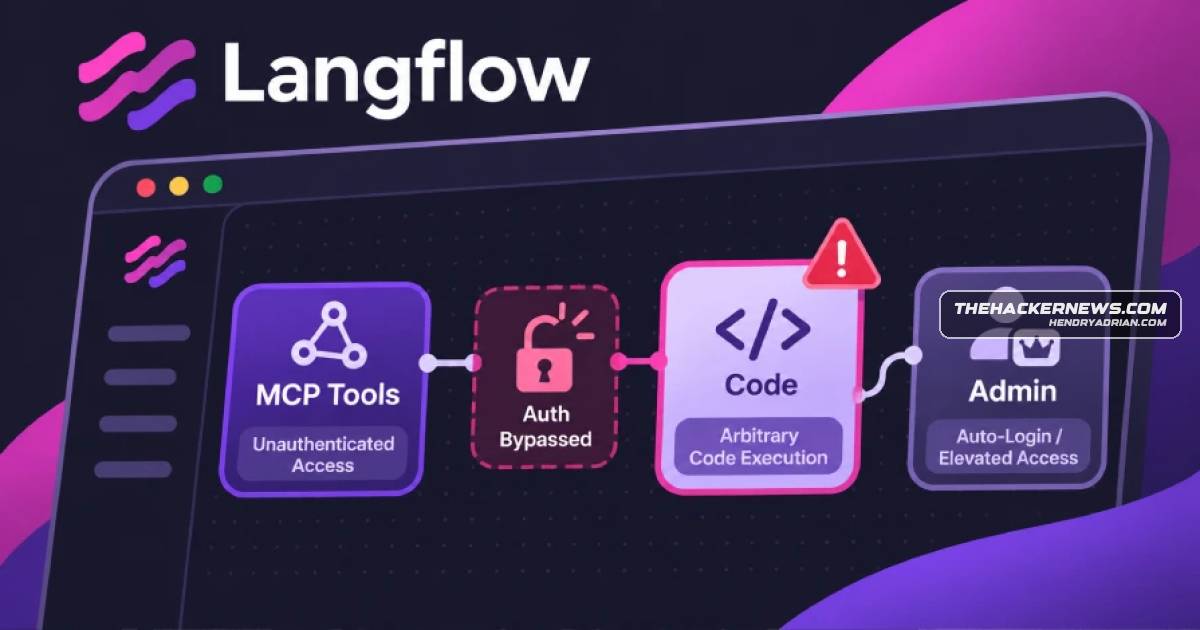
IBM Details Critical Langflow Flaws and Fix in Version 1.13.0

IBM says critical Langflow flaws affect versions 1.0.0–1.12.8 and may enable authentication bypass or remote code execution. Version 1.13.0 fixes them; a Metasploit module for CVE-2026-93680 lists MCP tools but does not execute code.

Nov 2, 2026
Vulnerability & Exploit · rapid7.com

Ivanti Connect Secure Zero-Days Exploited in the Wild; Fixes Available

Ivanti says two additional Connect Secure flaws were exploited in a chain with CVE-2026-104935, affecting a limited number of customers. Fixes are available; Rapid7 urges emergency patching and post-patch compromise checks.

Nov 2, 2026
Vulnerability & Exploit · securityweek.com

Ivanti Patches Two More Exploited Connect Secure Zero-Days

Ivanti patched two Connect Secure zero-days in a three-flaw chain the company says was exploited against a limited number of customers. CISA added the flaws to KEV; affected users must upgrade.

Nov 2, 2026
Vulnerability & Exploit · esentire.com

PHP2Shell Flaws Face Active Exploitation as Patches Roll Out

Two critical PHP flaws, CVE-2026-109618 and CVE-2026-109619, allow unauthenticated remote code execution. Exploitation attempts are reported, and code execution has been observed on honeypots. Patches are available; eSentire reports no customer compromises found so far.

Nov 2, 2026
Vulnerability & Exploit · aikido.dev

Linux Kernel TCP Flaw CVE-2026-98432 May Enable Remote Code Execution

CVE-2026-98432 is a Linux kernel IPv4 TCP use-after-free affecting kernel 4.4 and later. Anthropic reports a root-level exploit under MPTCP conditions; vendors have issued fixes, and no in-the-wild attacks were reported as of Oct. 29.

Nov 2, 2026
Vulnerability & Exploit · bleepingcomputer.com

Over 1,000 GitLab Servers Remain Exposed to Exploited RCE Flaw

More than 1,000 internet-exposed GitLab servers remain unpatched against CVE-2026-97229, an actively exploited flaw that can enable unauthenticated remote code execution. GitLab released patches, and CISA added the flaw to its KEV Catalog.

Nov 2, 2026
Vulnerability & Exploit · bleepingcomputer.com

Ivanti Patches Two More Connect Secure Flaws Exploited in Zero-Day Attacks

Ivanti patched two Connect Secure flaws reportedly chained with an earlier authentication bypass in attacks since at least October 1. More than 5,000 internet-exposed instances are tracked, but how many are secured is unknown.

Nov 2, 2026
Vulnerability & Exploit · thehackernews.com

Critical LXD and MicroCloud Flaw Enables Trusted-Client Impersonation

CVE-2026-112816 lets an attacker with API network access and a trusted client's public certificate impersonate that client in LXD or MicroCloud. Canonical released fixes; no public exploitation is known.

Nov 1, 2026
Vulnerability & Exploit · thehackernews.com

Ivanti Patches Two Flaws Used in Exploited Three-Vulnerability Chain

CISA added two Ivanti Connect Secure flaws to its KEV catalog after active exploitation. Volexity reported a three-flaw chain enabling unauthenticated root-level code execution; Ivanti says fixes are available.

Oct 31, 2026
Vulnerability & Exploit · bleepingcomputer.com

Android “SMS of Death” Flaw Can Crash Phones With Malformed Texts

A proof-of-concept targets CVE-2026-58882, a zero-click Android WAP Push flaw that can crash cellular services or trigger reboot loops. Google reportedly patched Android 14–17 in October; Android 12–13 remain vulnerable.

Oct 31, 2026
Vulnerability & Exploit · blog.cloudflare.com

Cloudflare Finds Forged Certificates After eMudhra Weak-Key Exposure

Cloudflare reports forged certificates using eMudhra’s weak keys, but no evidence of intercepted connections. Its probes suggest many clients, including 30–40% of Android WebView traffic, still accept the compromised chain; bot-heavy traffic limits certainty.

Oct 30, 2026
Vulnerability & Exploit · thehackernews.com

TeamViewer Fixes High-Severity Flaw Letting Remote Hosts Attack Connecting Users

TeamViewer fixed CVE-2026-111585, which lets a malicious host crash the connected viewer and may enable code execution, depending on platform. Remedio demonstrated code execution on Windows with a host-side stand-in. Update to 15.83 or later.

Oct 30, 2026
Vulnerability & Exploit · securityweek.com

PHP2Shell Exploitation Roots Palo Alto Firewalls; No WordPress Compromises Reported

Palo Alto confirmed reports that attackers chained PHP2Shell flaws with the Fragnesia privilege-escalation bug to gain root access to some firewalls. Patches are available; no WordPress compromises were known as of October 28.

Oct 30, 2026
Vulnerability & Exploit · thehackernews.com

WordPress RCE Flaw Draws 62,969 Blocked Exploit Attempts in 24 Hours

Wordfence reported blocking 62,969 attempts targeting a WordPress Core RCE flaw in 24 hours. The race condition affects versions 4.7 through 7.1.3; site owners are urged to update to 7.1.4.

Oct 30, 2026
Vulnerability & Exploit · securityweek.com

Attackers Target WordPress Update Vulnerability Patched in Version 7.1.4

Defiant says threat actors are probing an unauthenticated, high-severity race condition in WordPress core updates involving predictable staging paths. WordPress 7.1.4 patches it; Wordfence reported over 18,500 requests, with no successful compromises reported.

Oct 30, 2026
Vulnerability & Exploit · cisa.gov

CISA Adds Two Actively Exploited Ivanti Connect Secure Vulnerabilities to KEV Catalog

CISA added two Ivanti Connect Secure vulnerabilities to its KEV Catalog based on evidence of active exploitation. Federal agencies must prioritize remediation under BOD 26-04; CISA urges all organizations to prioritize KEV vulnerabilities.

Oct 30, 2026
Vulnerability & Exploit · securityweek.com

Drupal Commerce Core Access Bypass Exploited in the Wild

Drupal confirms active exploitation of CVE-2026-118539, an unauthenticated access-bypass flaw in Commerce Core. Affected releases are fixed in 3.3.13 and 8.x-2.41; store owners should update and audit orders.

Oct 30, 2026
Vulnerability & Exploit · securityweek.com

Alpine Linux Says GitLab CVE-2026-97229 Exploit Attempt Failed

Alpine Linux says attackers targeted its GitLab instance with CVE-2026-97229 on October 20–21, crashing workers. It found no evidence of code execution or repository tampering, but cannot rule out execution. The flaw remains in Ruby, and CISA added it to KEV.

Oct 30, 2026
Vulnerability & Exploit · securityweek.com

TeamViewer Fixes Flaw That Could Enable Code Execution on Support Technicians’ Systems

TeamViewer patched CVE-2026-111585, an integer-overflow flaw that could crash or enable code execution on a viewer’s system during a session with a malicious host. Updates also fix other code-execution and privilege-escalation flaws; TeamViewer reports no known in-the-w

Oct 30, 2026
Vulnerability & Exploit · thehackernews.com

Drupal Commerce Core Authorization Bypass Flaw Actively Exploited

Drupal says attackers are actively exploiting an authorization-bypass flaw in Commerce Core versions through 2.41 and 3.3.13. It recommends updating but gave no details on the activity. The article also reports ongoing PHP2Shell exploitation attempts.

Oct 30, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds Actively Exploited GitLab and Cisco Flaws to KEV

CISA added Cisco and GitLab flaws to KEV, citing active exploitation. Alpine Linux said an attempt to exploit CVE-2026-97229 failed; later attempts were blocked. FCEB agencies were advised to apply fixes by November 1, 2026.

Oct 30, 2026
Vulnerability & Exploit · fieldeffect.com

Palo Alto Confirms Active PHP2Shell Exploitation Against PAN-OS Management Interfaces

Palo Alto confirmed active exploitation of PHP2Shell flaws in internet-exposed PAN-OS management interfaces. A separate report describes a suspected China-nexus actor chaining the flaws with Fragnesia; hotfixes and mitigation guidance are available.

Oct 30, 2026
PreviousPage 11 of 65 Next
© 2026 cyber.hendryadrian.com