
Resecurity Reports ExfilSquad Claims 13 Victims and Shares Data via Torrents
Summary
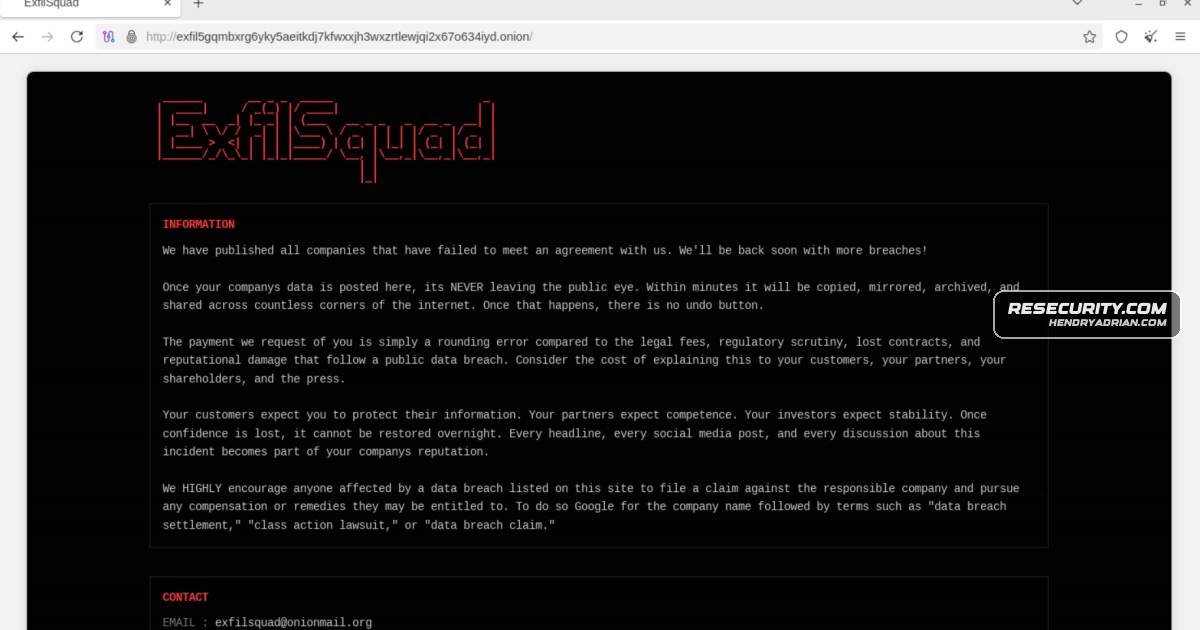
Resecurity reports that ExfilSquad claimed 13 organizations as victims and posted torrents said to contain stolen data. Its analysis found more than 50 later seeds and early activity from hosts in China and Russia, without linking those hosts to the group.
Key points
- Resecurity describes ExfilSquad as a financially motivated extortion group that threatens to publish data rather than typically using ransomware or destructive malware.
- The group claimed 13 organizations as victims and posted multiple torrents on August 7, 2026. The posts are evidence of the group’s claims, not independent confirmation of every alleged compromise.
- The report says the claims involve data from organizations across sectors, including customer, employee, student, and resident information.
- Resecurity identifies CRM, case-management, and consumer-facing portals as notable targets; an ExfilSquad representative said members targeted inadequately protected Microsoft Power Pages data tables.
- Resecurity observed more than 50 torrent seeds over time. Hosts in China and Russia were among the early active participants, but the report says they are unlikely to be directly associated with the group.
- ExfilSquad’s claim about Zenith Bank, alleging theft of around 90 million records, had been removed from its leak site by August 7. The bank had acknowledged an investigation into a possible cybersecurity incident; the outcome was unknown.
- Resecurity recommends ongoing vulnerability assessments and stronger access controls for CRM systems, employee portals, and consumer-facing portals that store sensitive data.
Article Details
- Publisher
- Resecurity
- Report Period
- 2026-07-26 to 2026-08-07
- Scope
- ExfilSquad activity, data-extortion tactics, and torrent-based distribution of stolen data.
- Sample Size
- 13 announced victim organizations; the separately discussed Zenith Bank claim was later removed from the group's Data Leak Site.
- Key Statistics
- The group announced 13 organizations from the U.S., the UK, and Sweden as victims.
- The article reports 135,000 law-enforcement contact records compromised in the Police National Legal Database incident.
- Torrent-sharing hosts from China and Russia increased to 16 by 11 a.m. PDT on August 7, 2026; the article says this may indicate interest or involvement, not confirmed attribution.
- Resecurity detected more than 50 seeds appearing at different times; the article says they were unlikely to be directly associated with the actors.
- ExfilSquad claimed to have stolen around 90 million Zenith Bank records totaling 874 GB; the claim was later removed from its Data Leak Site and was not confirmed.
- Recommendations
- Conduct ongoing Vulnerability Assessment and Penetration Testing (VAPT) to identify misconfigurations before adversaries exploit them.
- Strengthen access controls for CRM systems, employee portals, and consumer-facing portals that store sensitive PII and other records.
Threat Actors
Cl0p RansomwareNamed as an extortion group that used TOR-generated URLs and surface-web links; the article also reports that Cl0p created torrents for more than 20 victims.ExfilSquadResecurity identifies the group as responsible for data breaches and extortion. The article reports that it targeted organizations, threatened to publish stolen data, and distributed data through torrents; its claimed Zenith Bank breach remains unconfirmed.LockBit 3.0Named as an extortion group that has used TOR-generated URLs and surface-web links in connection with data leaks.
Vendors
Products
Countries
ChinaInterestingly, hosts from China and Russia were among the most active during August 7, 2026, which may suggest that the operators behind them had prior knowledge of the data publication or were involved in itsNigeriaNotably, in July, the group was also targeting a major financial institution in Nigeria.RussiaInterestingly, hosts from China and Russia were among the most active during August 7, 2026, which may suggest that the operators behind them had prior knowledge of the data publication or were involved in itsSwedenThis time, the list of victims includes 13 organizations from the U.S., the UK, and Sweden.United KingdomThis time, the list of victims includes 13 organizations from the U.S., the UK, and Sweden.United StatesThis time, the list of victims includes 13 organizations from the U.S., the UK, and Sweden.
Industries
AirlinesFrontier AirlinesEducationUK Department for Education (education.gov.uk)GovernmentThe stolen data reportedly included PII, account and financial information, government identifiers, customer contacts, and banking support records.Law enforcement135k law enforcement contact records with first/last name, email, police force area, etc.