cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3613 articles

Security News · krebsonsecurity.com

Two Alleged TeamPCP Members Arrested in Australia

Australian authorities arrested two men alleged to be linked to TeamPCP, a cybercrime group behind software supply-chain attacks and data extortion. Both face cybercrime charges and are due back in court in September.

Aug 27, 2026
Security News · afp.gov.au

Australia Charges Two Men Over Alleged TeamPCP Supply-Chain Campaign

Two men in Western Australia were charged after a joint investigation into alleged TeamPCP activity involving malicious open-source software. Authorities estimate the code potentially affected 1,000+ organizations and enabled theft of 500,000+ credentials.

Aug 27, 2026
Security News · thehackernews.com

CISA Adds Six Exploited Vulnerabilities to KEV, Including NetScaler Flaw

CISA added six vulnerabilities to its KEV catalog, including actively exploited CVE-2026-8452 affecting NetScaler. It set federal patch deadlines and highlighted persistent software weaknesses and AI-assisted exploitation.

Aug 27, 2026
Security News · thehackernews.com

Weedhack Malware Campaign Uses Fake Minecraft Clients and SEO Poisoning

McAfee Labs reports that fake Minecraft client sites and links on familiar platforms are distributing Weedhack. It detected and blocked more than 6,300 attempts to access malicious sites; JAR payloads can collect system data, add Defender exclusions, and steal sensitive

Aug 27, 2026
Security News · therecord.media

NSA Plans Reunion for Former TAO Staff as It Seeks to Rebuild Unit

The NSA plans an invitation-only reunion at Fort Meade for former Tailored Access Operations staff as part of a recruitment push. Former members raised internal-security concerns about the event’s Signal group, but one said no classified information had been shared.

Aug 27, 2026
Security News · aikido.dev

Australian Authorities Arrest Two Men Alleged to Be Behind TeamPCP

Australian authorities announced the arrest of two men they allege are behind TeamPCP. The author says there is no indication the group was behind the original S1ngularity and Shai-Hulud attacks, though it cloned the worm.

Aug 27, 2026
Security News · huntress.com

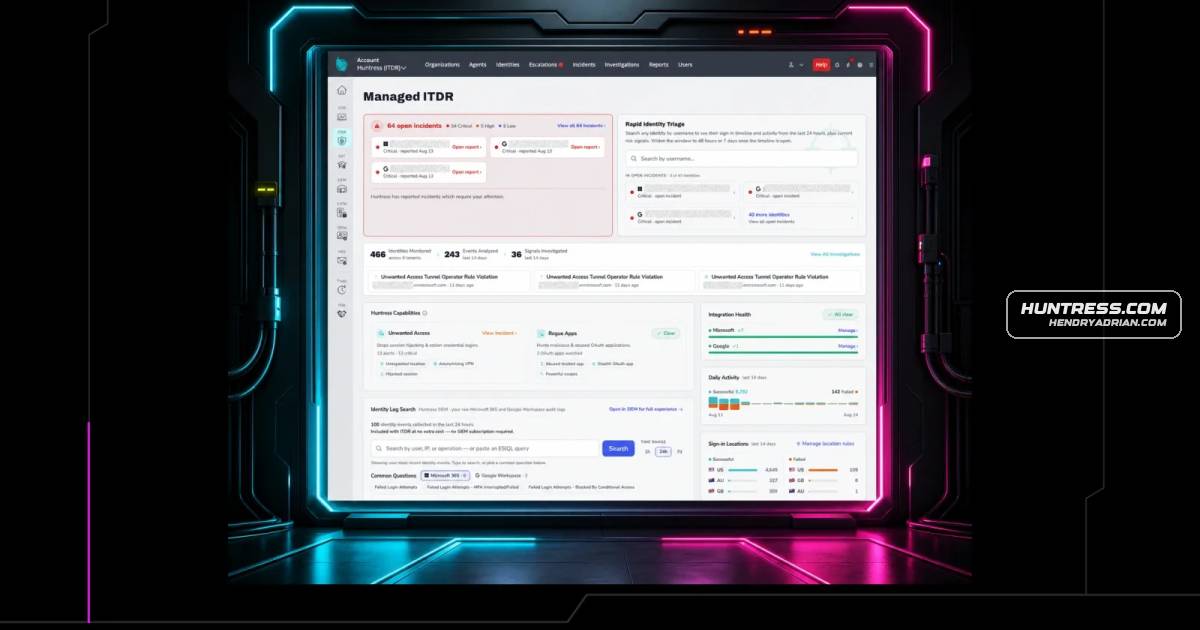
Huntress Launches Redesigned Managed ITDR Dashboard for Identity Investigations

Huntress has made its redesigned Managed ITDR dashboard generally available, adding rapid identity triage, context for failed logins, and searches of Microsoft Entra audit logs, with options to revoke sessions or disable accounts.

Aug 27, 2026
Security News · cyberscoop.com

U.S. Seizes Domains Tied to QTFY China-Linked Espionage Operation

U.S. authorities seized three domains used by QTFY’s QScan and QTRouter platforms, disrupting an operation officials say targeted federal agencies and critical infrastructure since 2018.

Aug 26, 2026
Security News · cyberscoop.com

Trump Order Restricts Foreign Equipment in U.S. Bulk-Power System Over Security Risks

Trump signed an order declaring a national emergency to secure the U.S. bulk-power system, restricting certain foreign-produced equipment and software deemed risky. The Energy Department has 120 days to develop implementation rules.

Aug 26, 2026
Security News · thehackernews.com

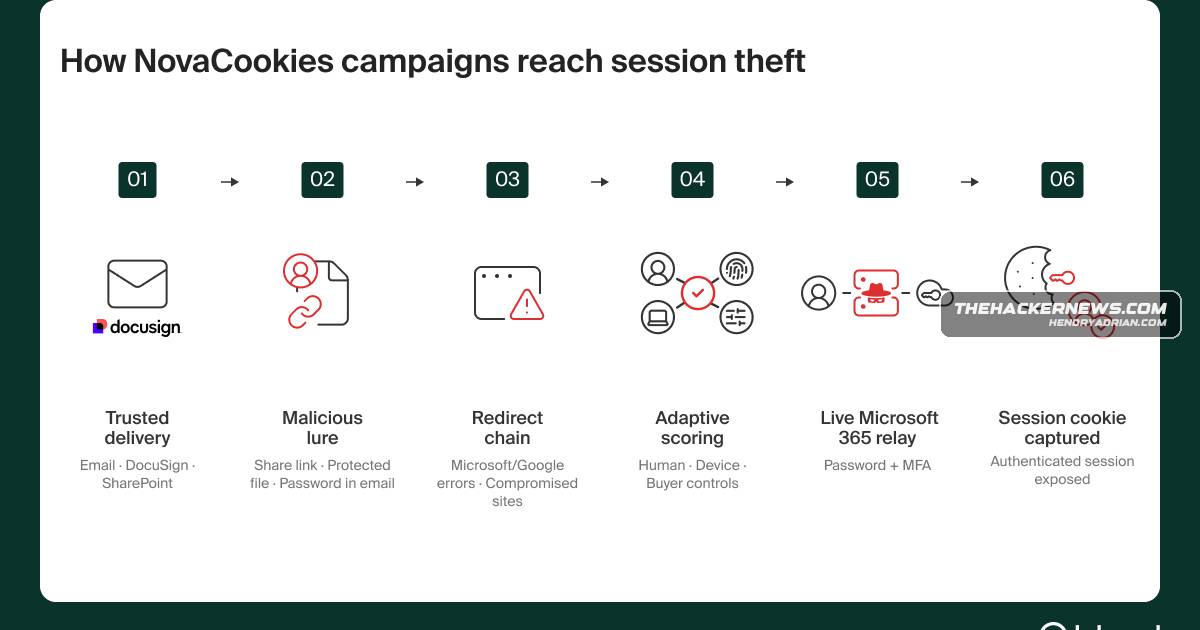
Researchers Detail NovaCookies Phishing Kit Targeting Microsoft 365 Sessions

Researchers report that NovaCookies, a $320/month AitM phishing service, targeted hundreds of organizations using genuine DocuSign notices and redirect hops to capture Microsoft 365 sessions; it also supports Okta and GoDaddy-federated Entra sign-ins.

Aug 26, 2026
Security News · thehackernews.com

Nimbus Manticore Adds TWOSTROKE-Like Backdoor and Reverse SSH Tunneler

Group-IB reports new Tortoiseshell infrastructure across Europe and the Middle East, a reverse SSH tunneler disguised as a Windows Terminal Server SDK API, and a C++ backdoor resembling TWOSTROKE with file, execution and host-information commands.

Aug 26, 2026
Security News · thehackernews.com

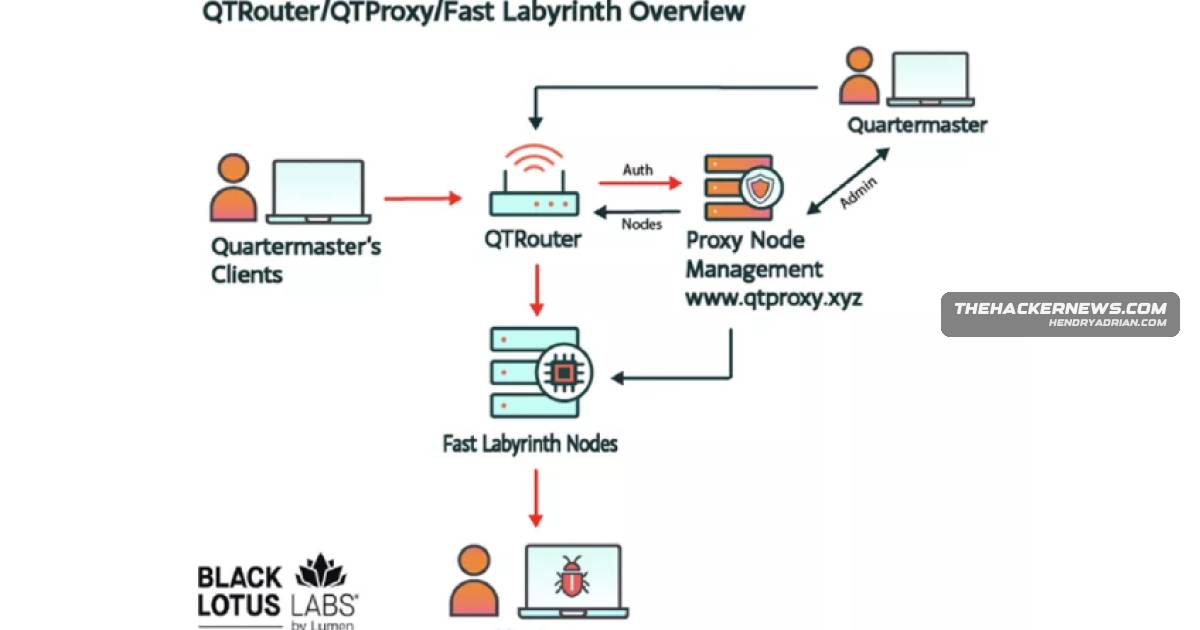
DOJ Disrupts QScan and QTRouter Platforms Attributed to China-Linked QTFY

U.S. DOJ says it disrupted QScan and QTRouter, platforms attributed to China-linked QTFY that scanned vulnerable IoT devices and routed attacks through compromised devices and commercial proxies. The FBI and Lumen described targets and attack methods.

Aug 26, 2026
Security News · cisecurity.org

CIS and SANS Bundle Hardened Cloud Images With AWS Security Training

CIS and SANS have introduced an AWS Marketplace bundle combining CIS Benchmark-aligned hardened images with hands-on cloud security training to help organizations deploy and maintain secure AWS environments.

Aug 26, 2026
Security News · bleepingcomputer.com

Meta Proposes $18 Billion Settlement Over Teen Safety and Data-Collection Claims

Meta has proposed a settlement of up to $18 billion with 52 state attorneys general over allegations of compulsive-use design and unlawful collection of children’s data. Court approval is pending; the deal includes teen-use limits and stronger age verification.

Aug 26, 2026
Security News · cyberscoop.com

Shasta County Offers Tina Peters Election Consultant Role With No System Access

Shasta County Registrar Clint Curtis offered Tina Peters a consultant role for the 2026 elections, saying consultants would not access county systems. Peters has not accepted; California officials emphasized legal and election-integrity requirements.

Aug 26, 2026
Security News · securityweek.com

Unit 42 Finds AI Speeds Malware Development, Not Evasion

Unit 42 analyzed 405 AI-linked malware samples and found that about 97% never reached a real target. Existing defenses detected all 12 samples found on protected endpoints, suggesting AI sped up malware development without making it harder to catch.

Aug 26, 2026
Security News · securityweek.com

Adobe and Nvidia Patch Dozens of Vulnerabilities, Including Critical Flaws

Adobe and Nvidia issued updates addressing dozens of vulnerabilities. The flaws affect products including Nvidia’s AI infrastructure and Adobe’s creative software; Adobe said none had been exploited in the wild.

Aug 26, 2026
Security News · bleepingcomputer.com

Microsoft Tests Per-App Camera, Microphone and Location Controls in Windows 11

Windows 11 Insider Experimental Preview Build 26340.9233 adds per-app controls for camera, microphone and precise location access. Microsoft is also testing consent prompts for apps requesting access to sensitive resources.

Aug 26, 2026
Security News · securityweek.com

CISA Says More Than 100 Internet-Exposed Water Systems Targeted in July

CISA says malicious activity targeted over 100 internet-exposed water and wastewater systems in July 2026, often PLCs connected to cellular modems. It recommends reducing exposure and securing necessary remote access; the attacks caused no significant disruption.

Aug 26, 2026
Security News · blog.barracuda.com

Barracuda Reports GlobalProtect Scanning and Remote-Access Threats

Barracuda’s SOC reports GlobalProtect scanning, credential-stuffing attempts against exposed VPN services, and a ScreenConnect RAT incident. It says scanning was blocked and an affected endpoint was isolated, and recommends patching, MFA, and tighter access controls.

Aug 26, 2026
Security News · securityweek.com

Chrome 152 Patches 327 Vulnerabilities, 299 Found Internally

Google released Chrome 152 with fixes for 327 vulnerabilities, including 10 critical and 61 high-severity flaws. Google says 299 were found internally; its advisory does not mention in-the-wild exploitation.

Aug 26, 2026
Security News · intrinsec.com

Intrinsec and GLIMPS Automate User-Reported Phishing Analysis With PhishReport

Intrinsec’s PhishReport service combines LLM-based email triage with GLIMPS attachment analysis to assess user-reported emails, provide verdicts and recommendations, and alert client security teams to malicious messages.

Aug 26, 2026
Security News · aikido.dev

Aikido Launches Agentic Penetration Testing for Android Apps

Aikido announced Android pentests using agents to test an APK and its backend together. Source code is currently required; findings are reported after exploit confirmation, with reproduction steps and retesting. The vendor says scope controls and safety checks are built

Aug 26, 2026
Security News · aikido.dev

Aikido Security Says It Achieved ISO 42001 Certification

Aikido Security says it achieved ISO 42001:2023 certification for AI governance across its platform. The article describes the audit process and scope, while noting the certification covers governance systems, not the safety of individual AI models or outputs.

Aug 26, 2026
PreviousPage 56 of 151 Next
© 2026 cyber.hendryadrian.com