Two Alleged TeamPCP Members Arrested in Australia
Summary
Australian authorities arrested two men alleged to be linked to TeamPCP, a cybercrime group behind software supply-chain attacks and data extortion. Both face cybercrime charges and are due back in court in September.
Key points
- The Australian Federal Police arrested two men, aged 21 and 23, in Western Australia; they face a combined 14 cybercrime offenses.
- The arrests are linked to TeamPCP, which allegedly compromised open-source software and used stolen developer credentials to spread malicious code.
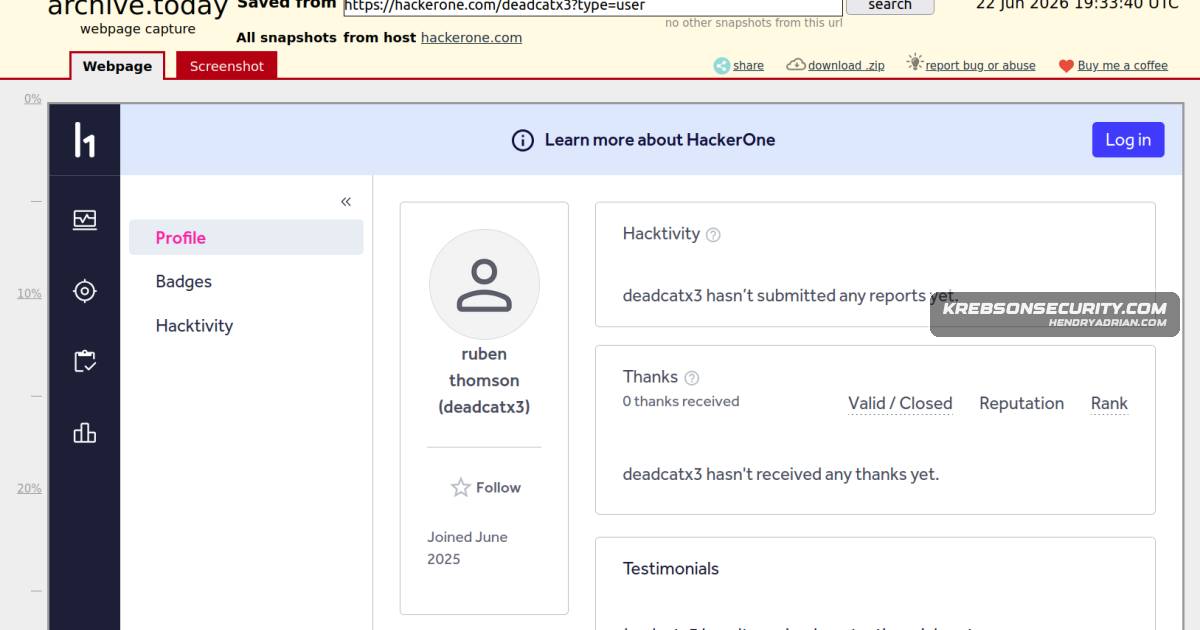
- The article identifies one arrested suspect as Ruben Thomson and reports that Michael Gaebler was also arrested.
- TeamPCP’s campaigns included the Shai-Hulud worm and attacks that allegedly harvested cloud keys and other secrets from more than 2,500 organizations through LiteLLM.
- The group’s members reportedly ran a contest encouraging participants to conduct software supply-chain attacks, with compromised access potentially bought by the group.
- GitHub introduced a three-day cooldown for Dependabot in late July, amid broader adoption of package-update cooldowns to help identify compromised releases.
Article Details
- Event Type
- Australian authorities arrested two alleged TeamPCP members in connection with cybercrime offenses, including alleged creation of malicious open-source software. The arrests follow a series of software supply-chain attacks and data-extortion activity attributed to TeamPCP.
- Impact
- The article reports that TeamPCP’s attacks compromised open-source packages and corporate cloud environments, and that a LiteLLM attack harvested cloud-service keys and other secrets from more than 2,500 organizations. TeamPCP also claimed to have compromised at least 3,800 GitHub repositories. The reported activity prompted GitHub and other coding ecosystems to introduce or support package-update cooldown safeguards.
People
Austin LarsenGoogle Threat Intelligence Group principal threat analyst quoted describing TeamPCP as a peer community of individually skilled actors.Charlie EriksenAikido Security researcher quoted discussing TeamPCP’s activity and its implications for supply-chain security.George PrepakisIdentified in the article as TeamPCP’s center of gravity and as a security researcher and exploit developer; the article does not identify him as one of the arrested men.Michael GaeblerABC News identified him as the other arrested man and reported that he was thought to be the person using the handle @pcpcasper.Ruben Ian ThomsonABC News identified him as one of the two arrested men; the article links him to the TeamPCP leader known as Ellis, but the AFP did not name the defendants.
Threat Actors
Deadcatx3Nickname that the article says multiple security firms have identified as an alias used by TeamPCP.fulcrumsecCybercrime group that claimed credit for data-extortion attacks against Novo Nordisk, LexisNexis, and Avnet.TeamPCPCybercrime group blamed for software supply-chain attacks, data extortion, and compromising open-source packages and corporate environments.xpl0itrsExtortion-group or handle associated with a data-leak site; the article also links a close TeamPCP associate to selling allegedly stolen data.
Malware
Vendors
Products
GitHubcode to open source programs maintained by developers whose credentials at public code repositories like GitHub or NPM were phished or stolen.LiteLLMIn March, TeamPCP executed a supply chain attack targeting AI infrastructure by compromising the code for LiteLLM, an open source AI gateway that connects users to more than 100 different large language models.
Countries
AustraliaAuthorities in Australia have arrested two men believed to be members of TeamPCP, a prolific cybercrime and data extortion group blamed for perpetrating the longest running spree of software supply chain attacks ever.South AfricaIntel 471 finds Express posted on Breachforums across a two-month period in 2025 using four different Internet addresses located in South Africa.