Researchers Detail NovaCookies Phishing Kit Targeting Microsoft 365 Sessions
Summary
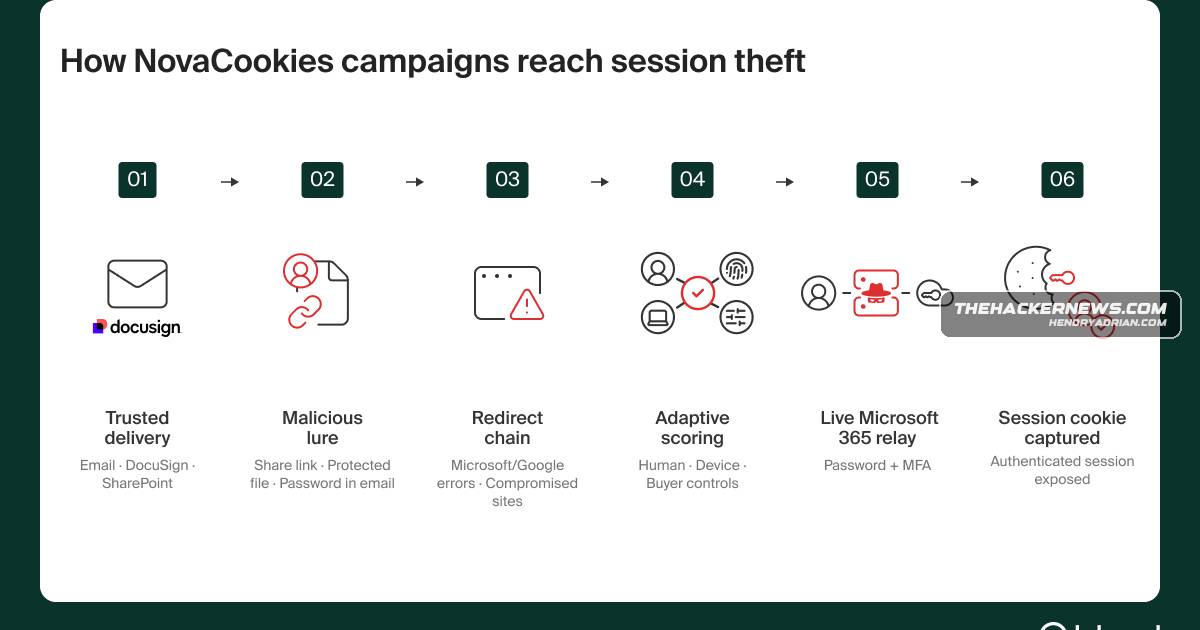
Researchers report that NovaCookies, a $320/month AitM phishing service, targeted hundreds of organizations using genuine DocuSign notices and redirect hops to capture Microsoft 365 sessions; it also supports Okta and GoDaddy-federated Entra sign-ins.
Key points
- Island described NovaCookies as a $320-per-month phishing-as-a-service platform; campaigns reportedly targeted hundreds of organizations across several countries.
- The AitM relay proxies Microsoft 365 sign-ins and captures authenticated sessions after victims enter passwords and MFA codes.
- Campaigns used genuine DocuSign notifications containing malicious document links, with some traffic passing through legitimate Microsoft or Google sign-in endpoints.
- An OAuth error-redirect technique led victims to attacker-controlled infrastructure; the service also uses anti-analysis checks, including a Cloudflare gate and debugging-tool detection.
- Proofpoint assesses NovaCookies as a Sneaky 2FA variant, with added flows for Okta and Entra domains federated to GoDaddy.
- Telegram is reportedly used to advertise the service and manage customer profiles, redirect settings, and support.