cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3613 articles

Security News · reversinglabs.com

ReversingLabs Releases Artifactory Plugin to Block Risky Open-Source Packages

ReversingLabs’ free Artifactory plugin checks npm, PyPI, Maven, NuGet and RubyGems package requests against Spectra Assure Community intelligence, allowing teams to block packages flagged as risky.

Sep 2, 2026
Security News · sysdig.com

August 2026 Security Briefing: ChainDrop, AI Agent Risks and Cl0p

Sysdig’s August 2026 briefing covers ChainDrop’s npm poisoning, Ghostjacking risks in AI coding agents, Claude Code use in ransomware intrusions, Cl0p’s exploitation of PTC Windchill, and governance updates. Sysdig says 7 of 8 AI-enabled attacks used ordinary command-ex

Sep 1, 2026
Security News · securityweek.com

Palo Alto Networks Acquires Console to Add AI Agents to Cortex

Palo Alto Networks acquired Console, an AI-native platform it says will expand Cortex with natural-language workflows for investigating signals, prioritizing work, and automating security actions.

Sep 1, 2026
Security News · securityweek.com

Sevii Adds AI Module for Autonomous Security Detection and Remediation

Sevii says its new AI security module analyzes alerts, hunts for context and can autonomously contain threats, including isolating compromised laptops and disabling accounts.

Sep 1, 2026
Security News · securityweek.com

U.S. Coast Guard Establishes Maritime Cybersecurity Policy Office

The U.S. Coast Guard created the Office of Maritime Cybersecurity Policy to set maritime cyber policy, coordinate compliance and enforcement, and liaise with industry and government. The move follows a GAO report identifying gaps, though a direct link was not stated.

Sep 1, 2026
Security News · securityweek.com

Five Venezuelans Plead Guilty to Attempted ATM Jackpotting in Kansas

Five Venezuelan nationals pleaded guilty after trying to install remotely activated malware on Kansas ATMs to force cash dispensing. The attempts failed. The FBI reported more than 700 jackpotting incidents in 2025, causing over $20 million in losses.

Sep 1, 2026
Security News · wiz.io

Wiz Launches Continuous Vulnerability Assessment in Public Preview

Wiz’s Continuous Vulnerability Assessment updates its vulnerability catalog when new vulnerabilities are discovered and reassesses customer exposure in near-real time. The service is in public preview and includes remediation context through Wiz’s Green Agent.

Sep 1, 2026
Security News · darkowl.com

Cybersecurity Roundup: Medusa Ransomware, Sandworm Campaign and Major Breaches

A weekly threat-intelligence roundup covers Medusa ransomware’s impact, a Sandworm-linked campaign, attacks disrupting ports and water utilities, major data theft, arrests, and new macOS malware.

Sep 1, 2026
Security News · stepsecurity.io

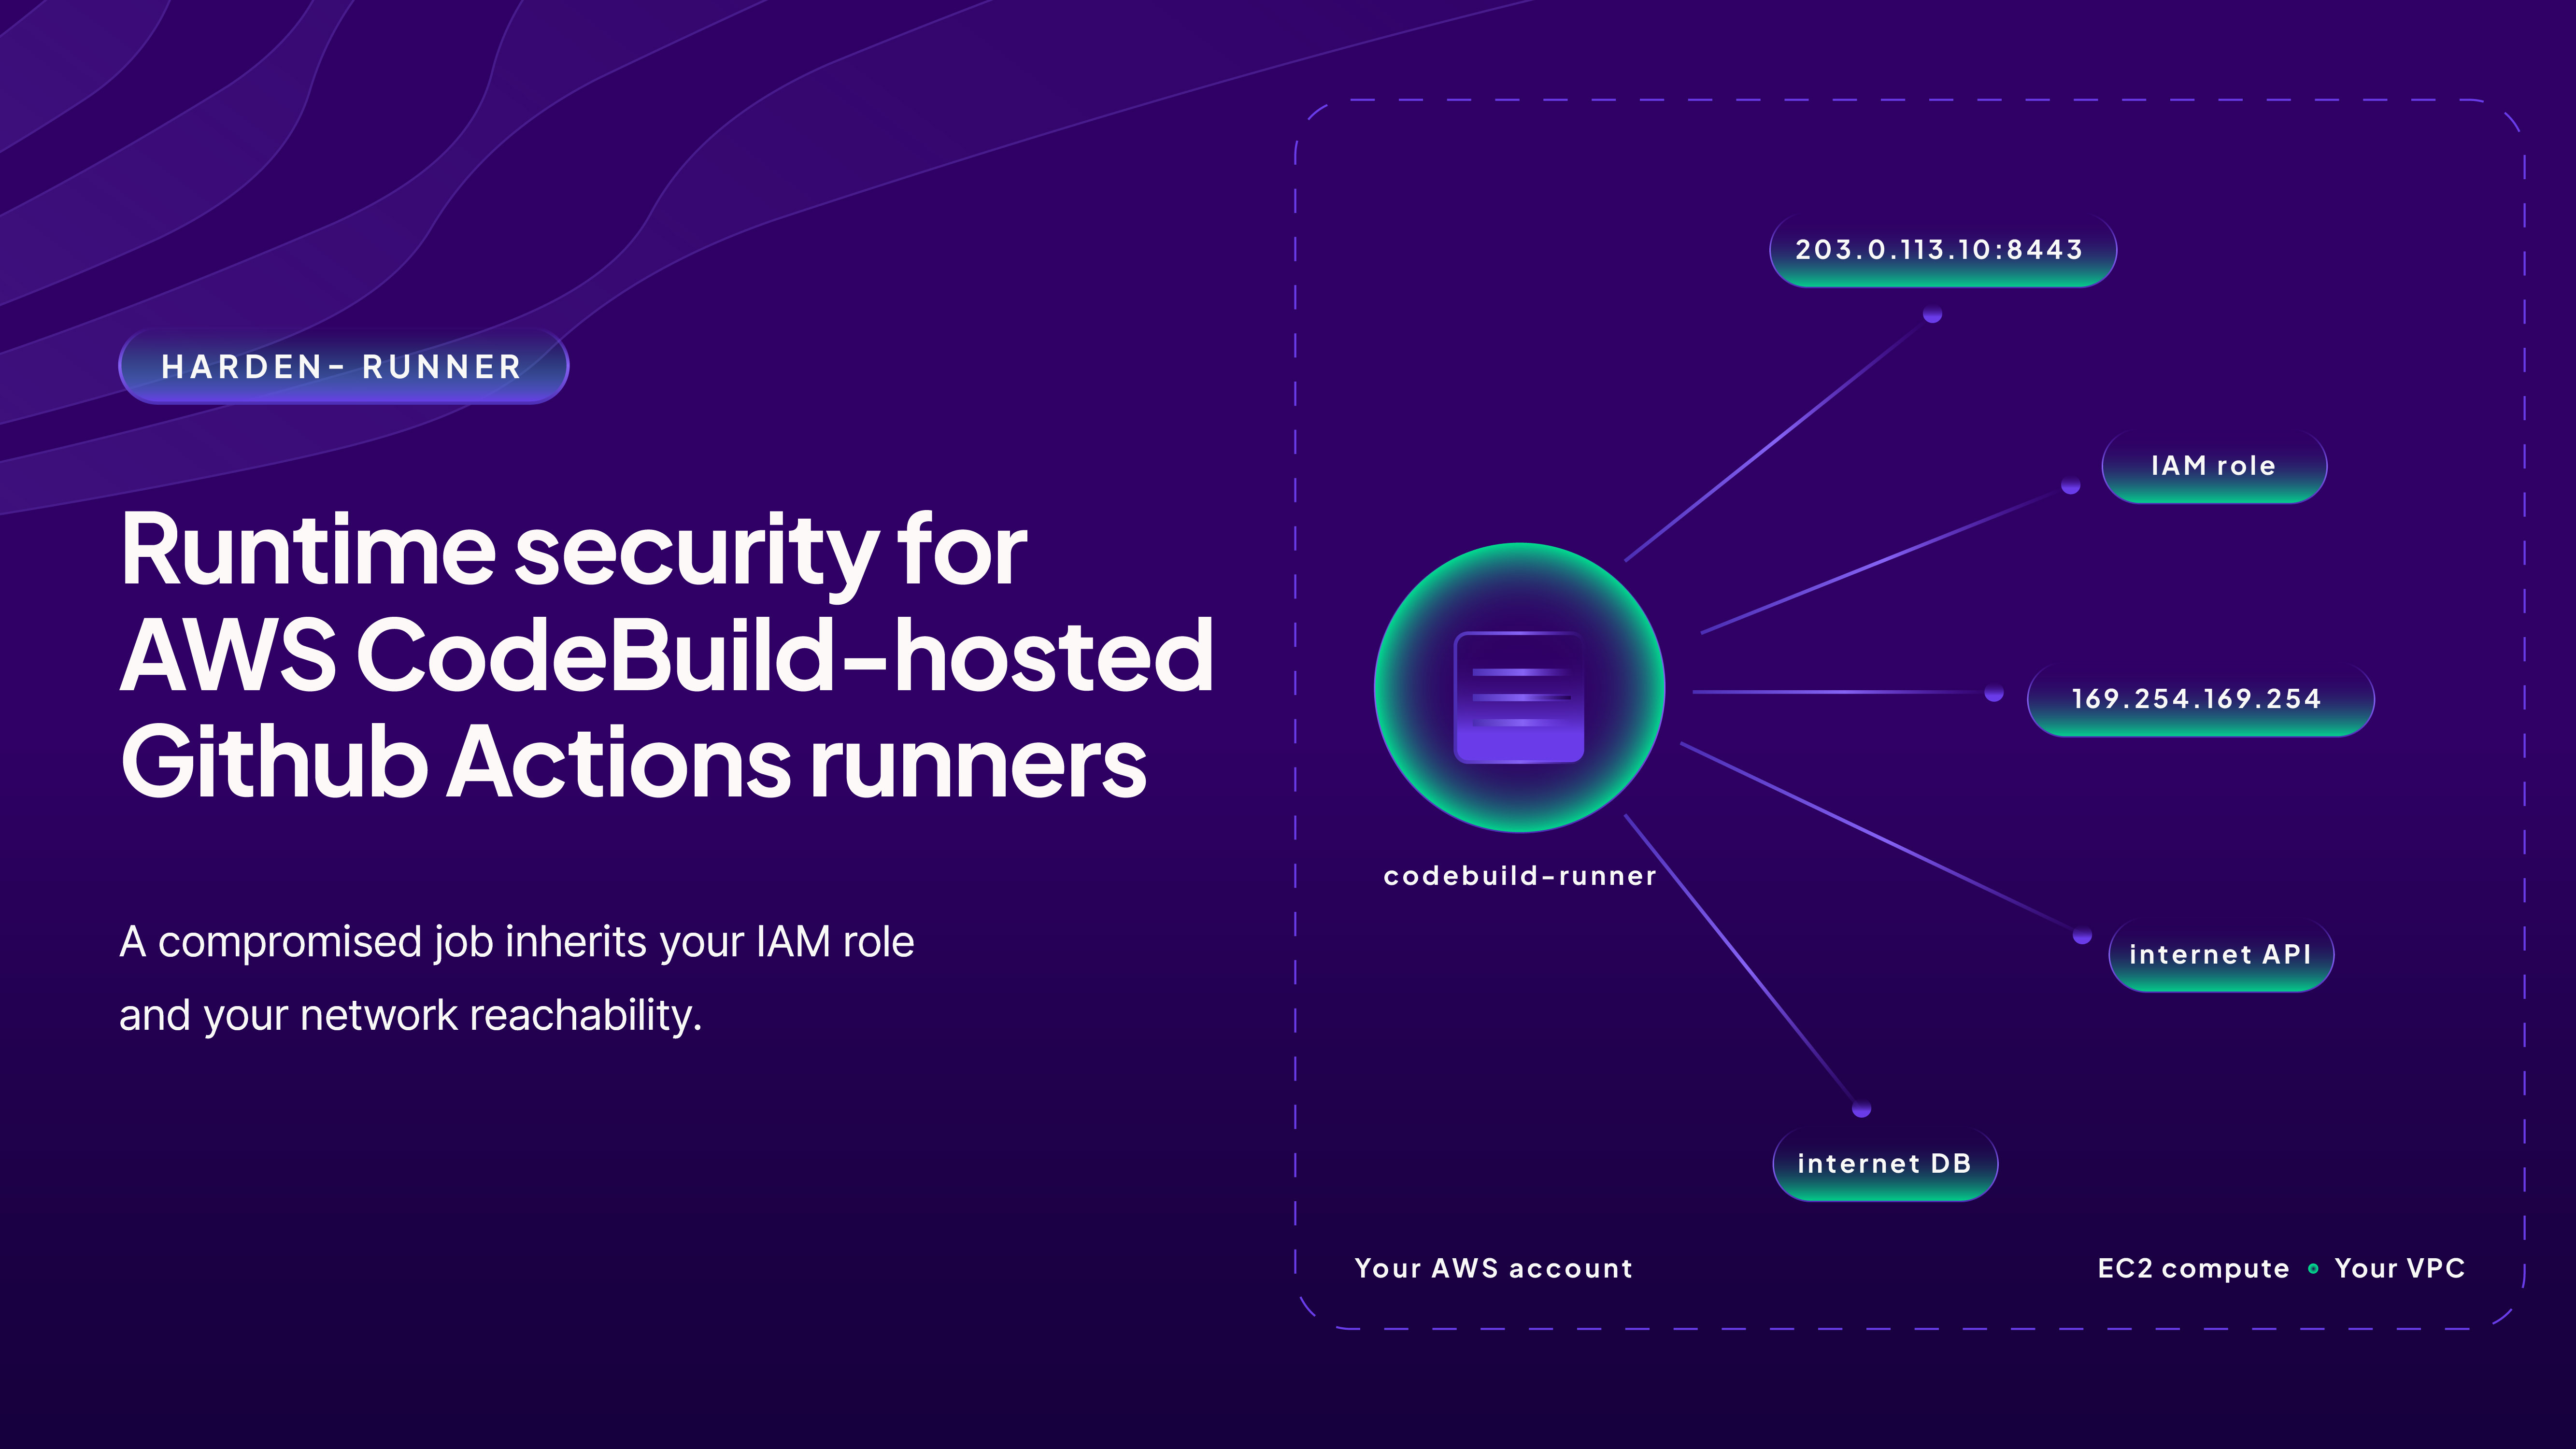
Step Security Adds Harden-Runner Support for AWS CodeBuild GitHub Actions Runners

Step Security says Harden-Runner now supports GitHub Actions runners hosted on AWS CodeBuild, with runtime monitoring for network activity, file writes and process execution. Support requires specific CodeBuild settings and Harden-Runner versions.

Sep 1, 2026
Security News · bleepingcomputer.com

Spur’s Monocle Adds Infrastructure Signals to Edge Session Risk Decisions

Spur’s sponsored article describes Monocle Session Enrichment, which adds real-time VPN, proxy, anonymization and network signals to sessions so organizations can apply existing edge policies to authentication and other risky activity.

Sep 1, 2026
Security News · any.run

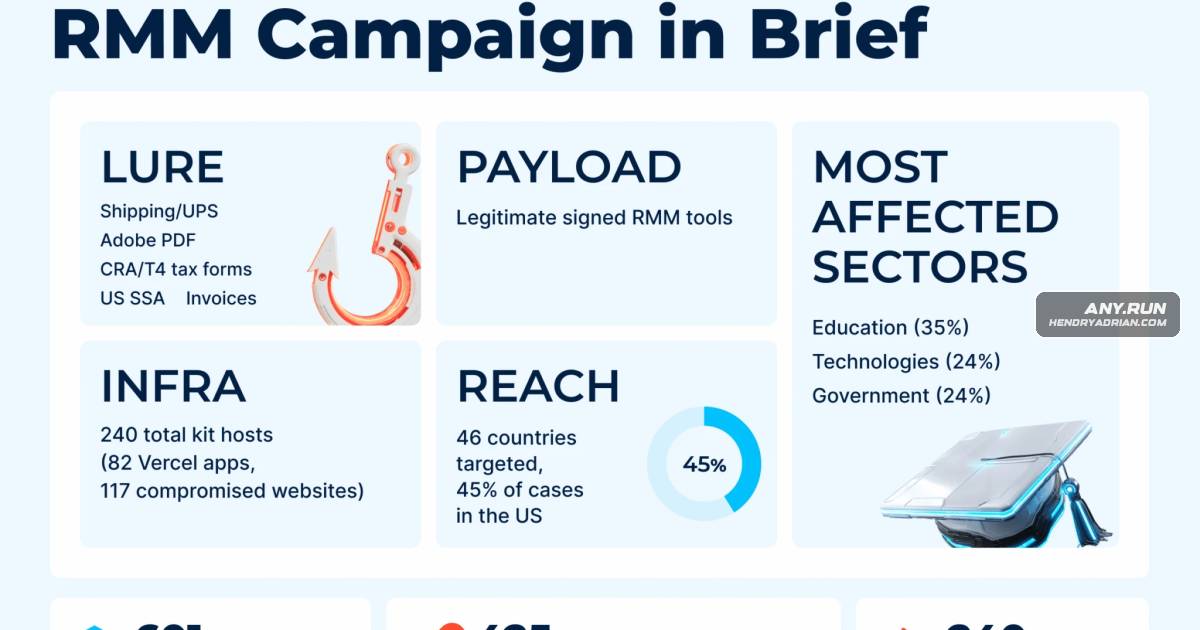
August 2026 Cyberattacks Targeted U.S. and European Businesses Through Session Theft and Remote Access

ANY.RUN's August roundup describes campaigns abusing legitimate remote-management tools, Microsoft 365 sessions, hiring processes and business-themed files to gain access, steal credentials and deploy remote-control malware against U.S. and European organizations.

Sep 1, 2026
Security News · thehackernews.com

Weekly Cybersecurity Roundup: QTYF Disruption, AI-Agent Breach, ZBT Router Backdoors

This weekly roundup covers the FBI’s QTYF disruption, OpenAI’s account of AI agents accessing Hugging Face, PaperCut exploitation, ZBT router backdoors, Fire Ant intrusions, and social-engineered malware and ransomware campaigns.

Aug 31, 2026
Security News · thehackernews.com

DPRK-Linked Job Fraud Expands Beyond IT Into Healthcare, Sales and Finance

Investigations say DPRK-linked job-fraud operators are targeting roles beyond IT, using synthetic identities, forged documents, VPNs and AI. Cases span healthcare, finance, sales and marketing; one PurpleDelta cluster applied to jobs at more than 1,100 companies.

Aug 31, 2026
Security News · cyberscoop.com

U.S. Launches Texas Pilot to Strengthen Water System Cybersecurity

Project Watershed 250 is a six-month Texas pilot bringing federal, state and private-sector expertise to identify water-system weaknesses, test defenses and scale protections. Texas Cyber Command and the Office of the National Cyber Director will oversee it.

Aug 31, 2026
Security News · bleepingcomputer.com

Microsoft Exchange Online outage disrupts email, authentication and Microsoft 365 services

Microsoft is investigating an Exchange Online outage causing authentication errors, email delays and mailbox failures. It cites a core authentication configuration issue; OneDrive, SharePoint, Teams, Purview and Defender XDR are also affected.

Aug 31, 2026
Security News · helpnetsecurity.com

Attackers Exploit PaperCut Zero-Days to Install Remote Access Tools

PaperCut says attackers exploited two zero-days in NG and MF servers to install SimpleHelp and AnyDesk. Emergency patches are available; customers are urged to restrict access, preserve evidence, review logs, and rebuild suspected compromised servers.

Aug 31, 2026
Security News · helpnetsecurity.com

AWS Makes Console Private Access Generally Available for Isolated VPCs

AWS Console Private Access is generally available, routing supported console traffic through PrivateLink in isolated VPCs and allowing policies to restrict sign-ins from unexpected networks. IAM Identity Center sign-in still requires public internet access.

Aug 31, 2026
Security News · bleepingcomputer.com

Microsoft Tells Users to Ignore False Defender Antivirus Disabled Alerts

Microsoft says false Defender Antivirus disabled alerts appear after recent updates on supported Windows client and server versions, although protection remains active. A fix is planned for a future update.

Aug 31, 2026
Security News · bleepingcomputer.com

Two Nigerian Men Extradited to U.S. on Sextortion Charges Linked to Two Teen Deaths

Two Nigerian men were extradited to the U.S. and charged in sextortion schemes linked to the deaths of two minors. The case is part of Operation Artemis, targeting Nigeria-based rings that prey on U.S. minors.

Aug 31, 2026
Security News · helpnetsecurity.com

Halo-record adds tamper-evident audit trails for AI agents

Halo-record is an open-source Python package that hash-chains AI-agent actions for independent tamper checks. It redacts and hashes raw arguments, but cannot detect omitted records; completeness requires an external witness.

Aug 31, 2026
Security News · helpnetsecurity.com

OpenClaw 2.0 Moves Sessions to SQLite and Adds Sharing and Incognito Controls

OpenClaw 2.0 migrates sessions to SQLite and adds credential checks, shared cloud sessions, and incognito mode. The release warns that sharing is not isolation, incognito does not hide activity from providers or operators, and browser snapshots are unencrypted.

Aug 31, 2026
Security News · thehackernews.com

ThreatsDay Roundup: 296,000-Device IoT Botnet, 100+ Water Systems Targeted, SharePoint Flaws Probed

This ThreatsDay roundup covers Dysphoria’s nearly 296,000 compromised IoT devices, attacks targeting 100+ exposed U.S. water systems, SharePoint flaw probing, and new phishing, malware, botnet, and AI-agent threats.

Aug 31, 2026
Security News · therecord.media

Finnish Appeals Court Revives Case Against Eagle S Officers Over Baltic Cable Damage

Finland’s appeals court restored the case against three Eagle S officers, ruling that Finland has jurisdiction and that the crew’s conduct after authorities contacted the ship was not protected as a maritime accident.

Aug 31, 2026
Security News · stepsecurity.io

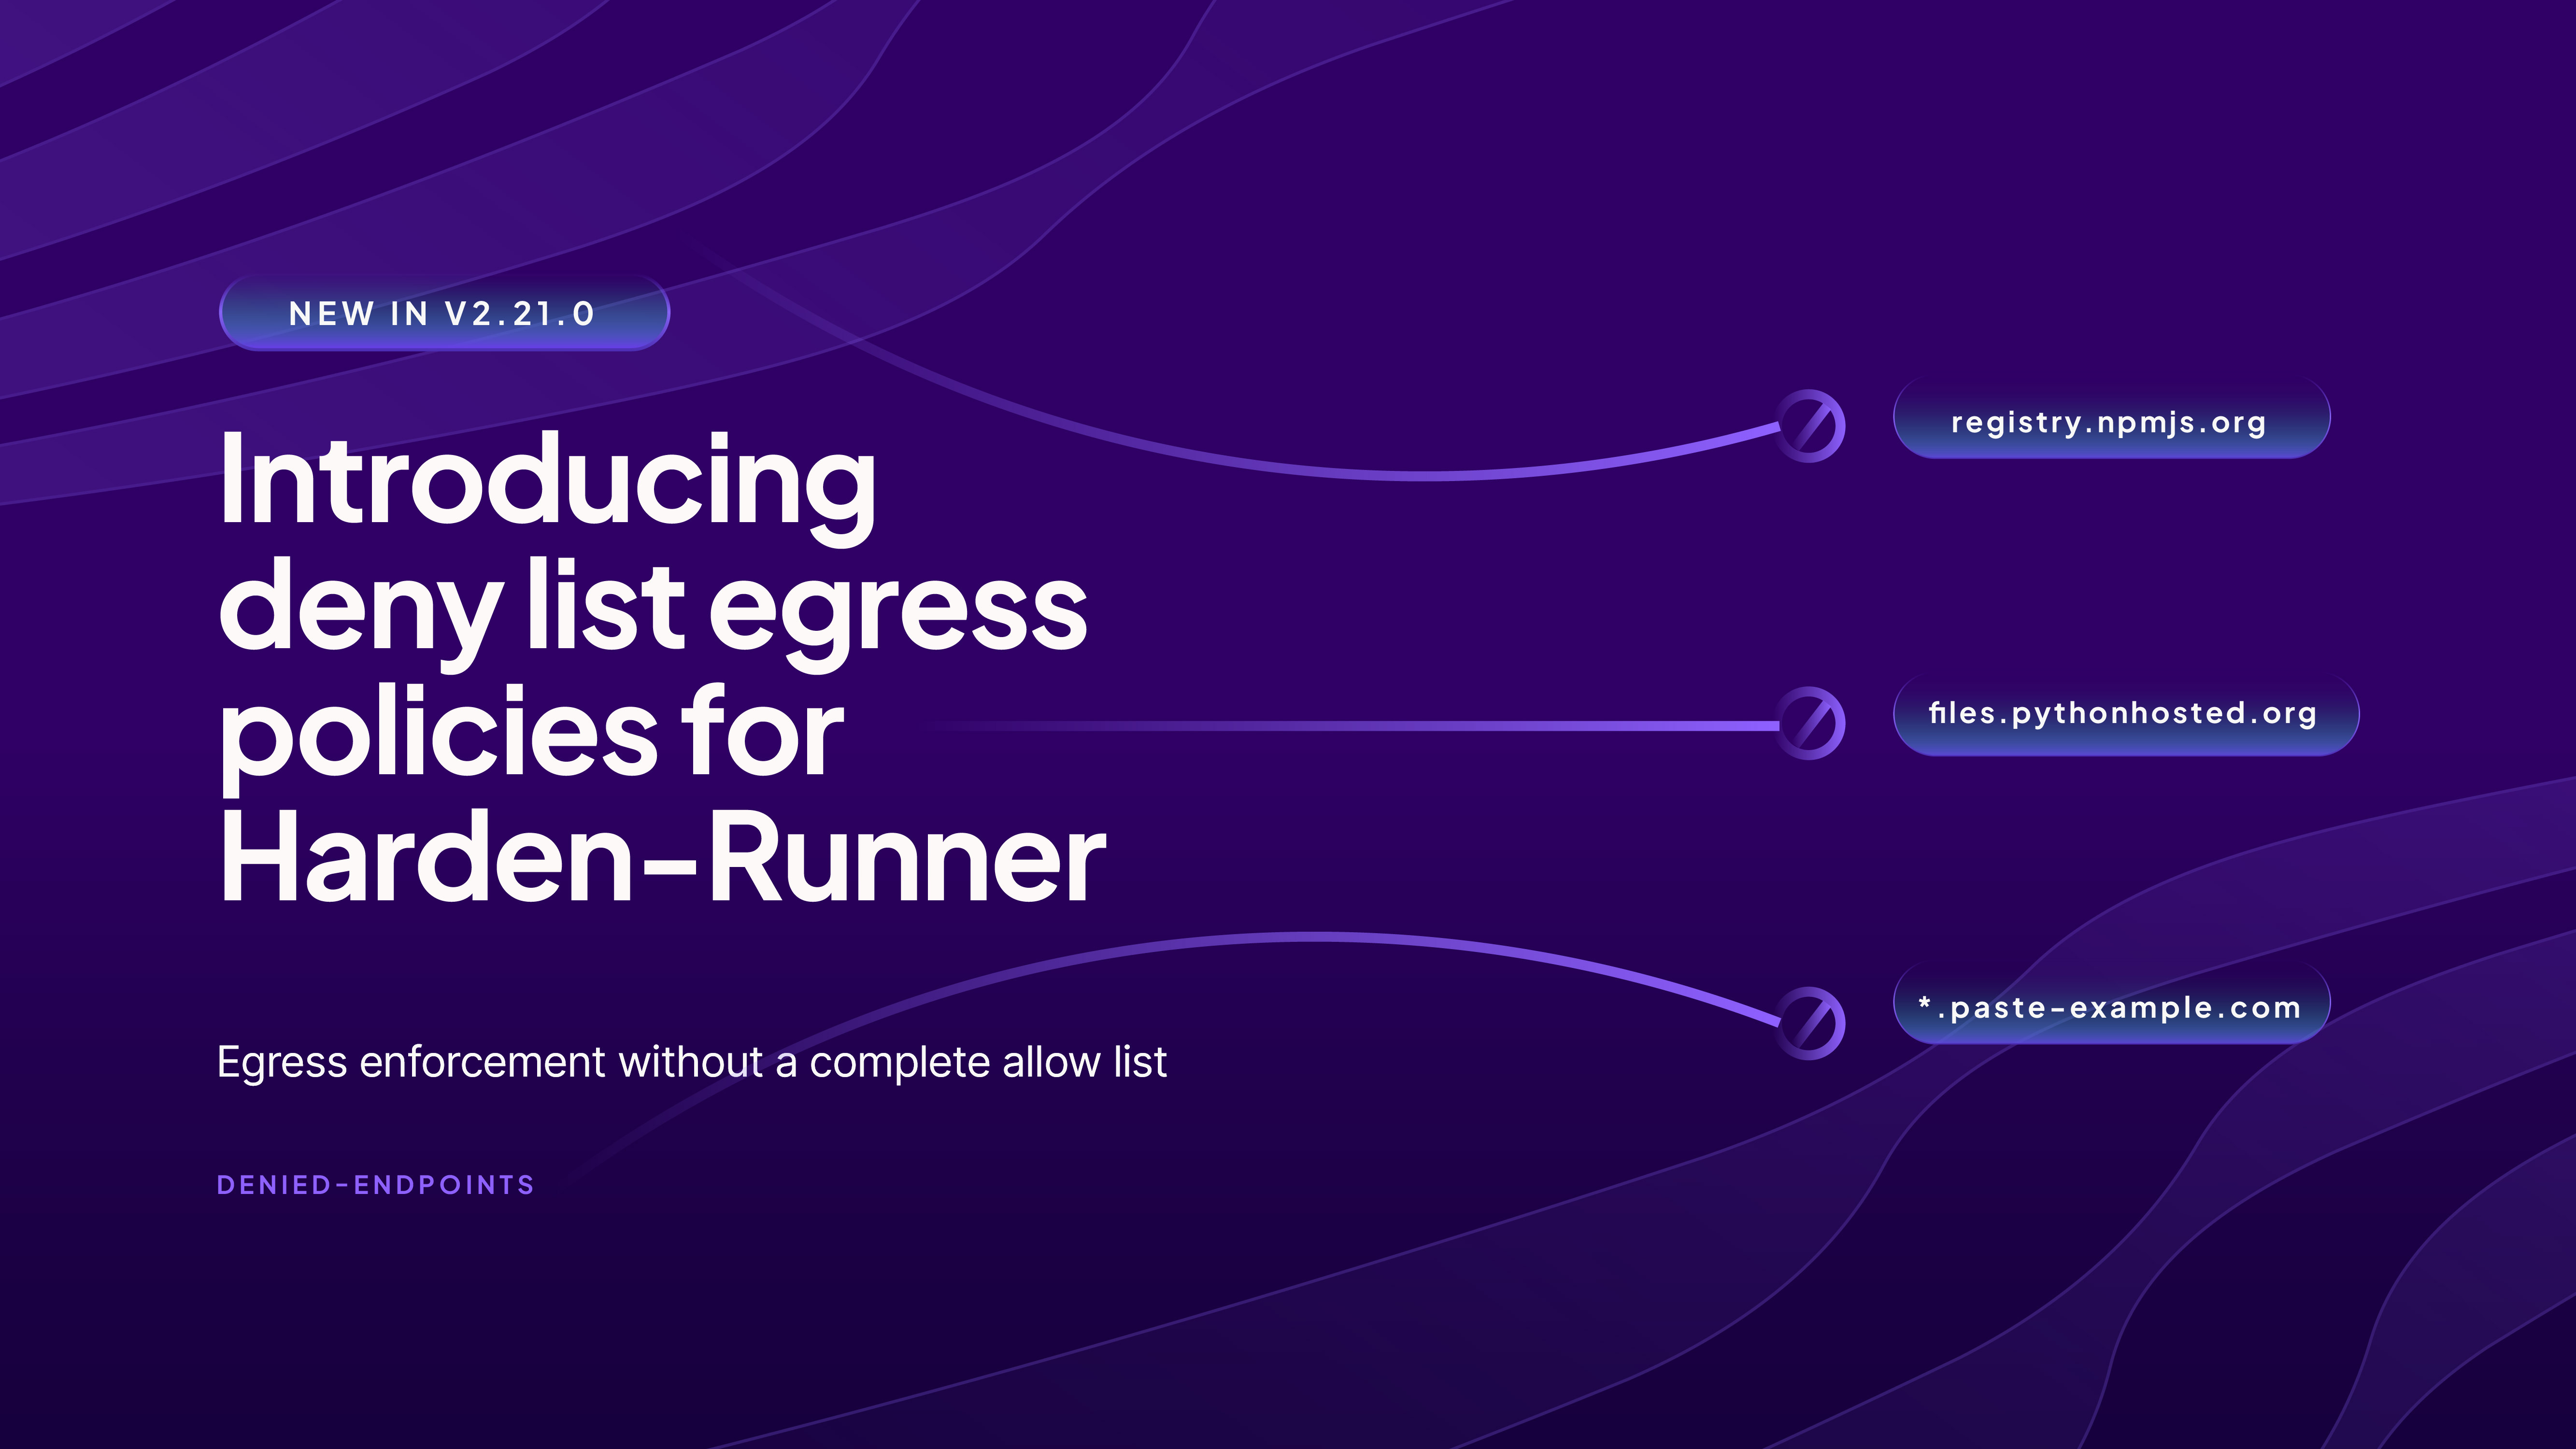
Step Security Adds Deny-List Egress Policies to Harden-Runner

Step Security added deny-list egress policies to Harden-Runner, letting teams block specified domains and IPs while leaving other destinations reachable. The vendor says policies can be centrally applied and cautions they do not replace allow lists.

Aug 31, 2026
PreviousPage 54 of 151 Next
© 2026 cyber.hendryadrian.com