
Step Security Adds Harden-Runner Support for AWS CodeBuild GitHub Actions Runners
Summary
Step Security says Harden-Runner now supports GitHub Actions runners hosted on AWS CodeBuild, with runtime monitoring for network activity, file writes and process execution. Support requires specific CodeBuild settings and Harden-Runner versions.
Key points
- Harden-Runner v2.20.1 supports CodeBuild runners on EC2; v2.21.0 adds support for Linux containers on EC2.
- The required CodeBuild configuration includes EC2 compute, the kernel-6 host kernel and privileged mode.
- Step Security says Harden-Runner captures outbound network calls, file writes and process executions, correlating them with the workflow step that triggered them.
- The article says the tool detects memory-reading behavior associated with CVE-2025-8217 and provides an attached triage runbook.
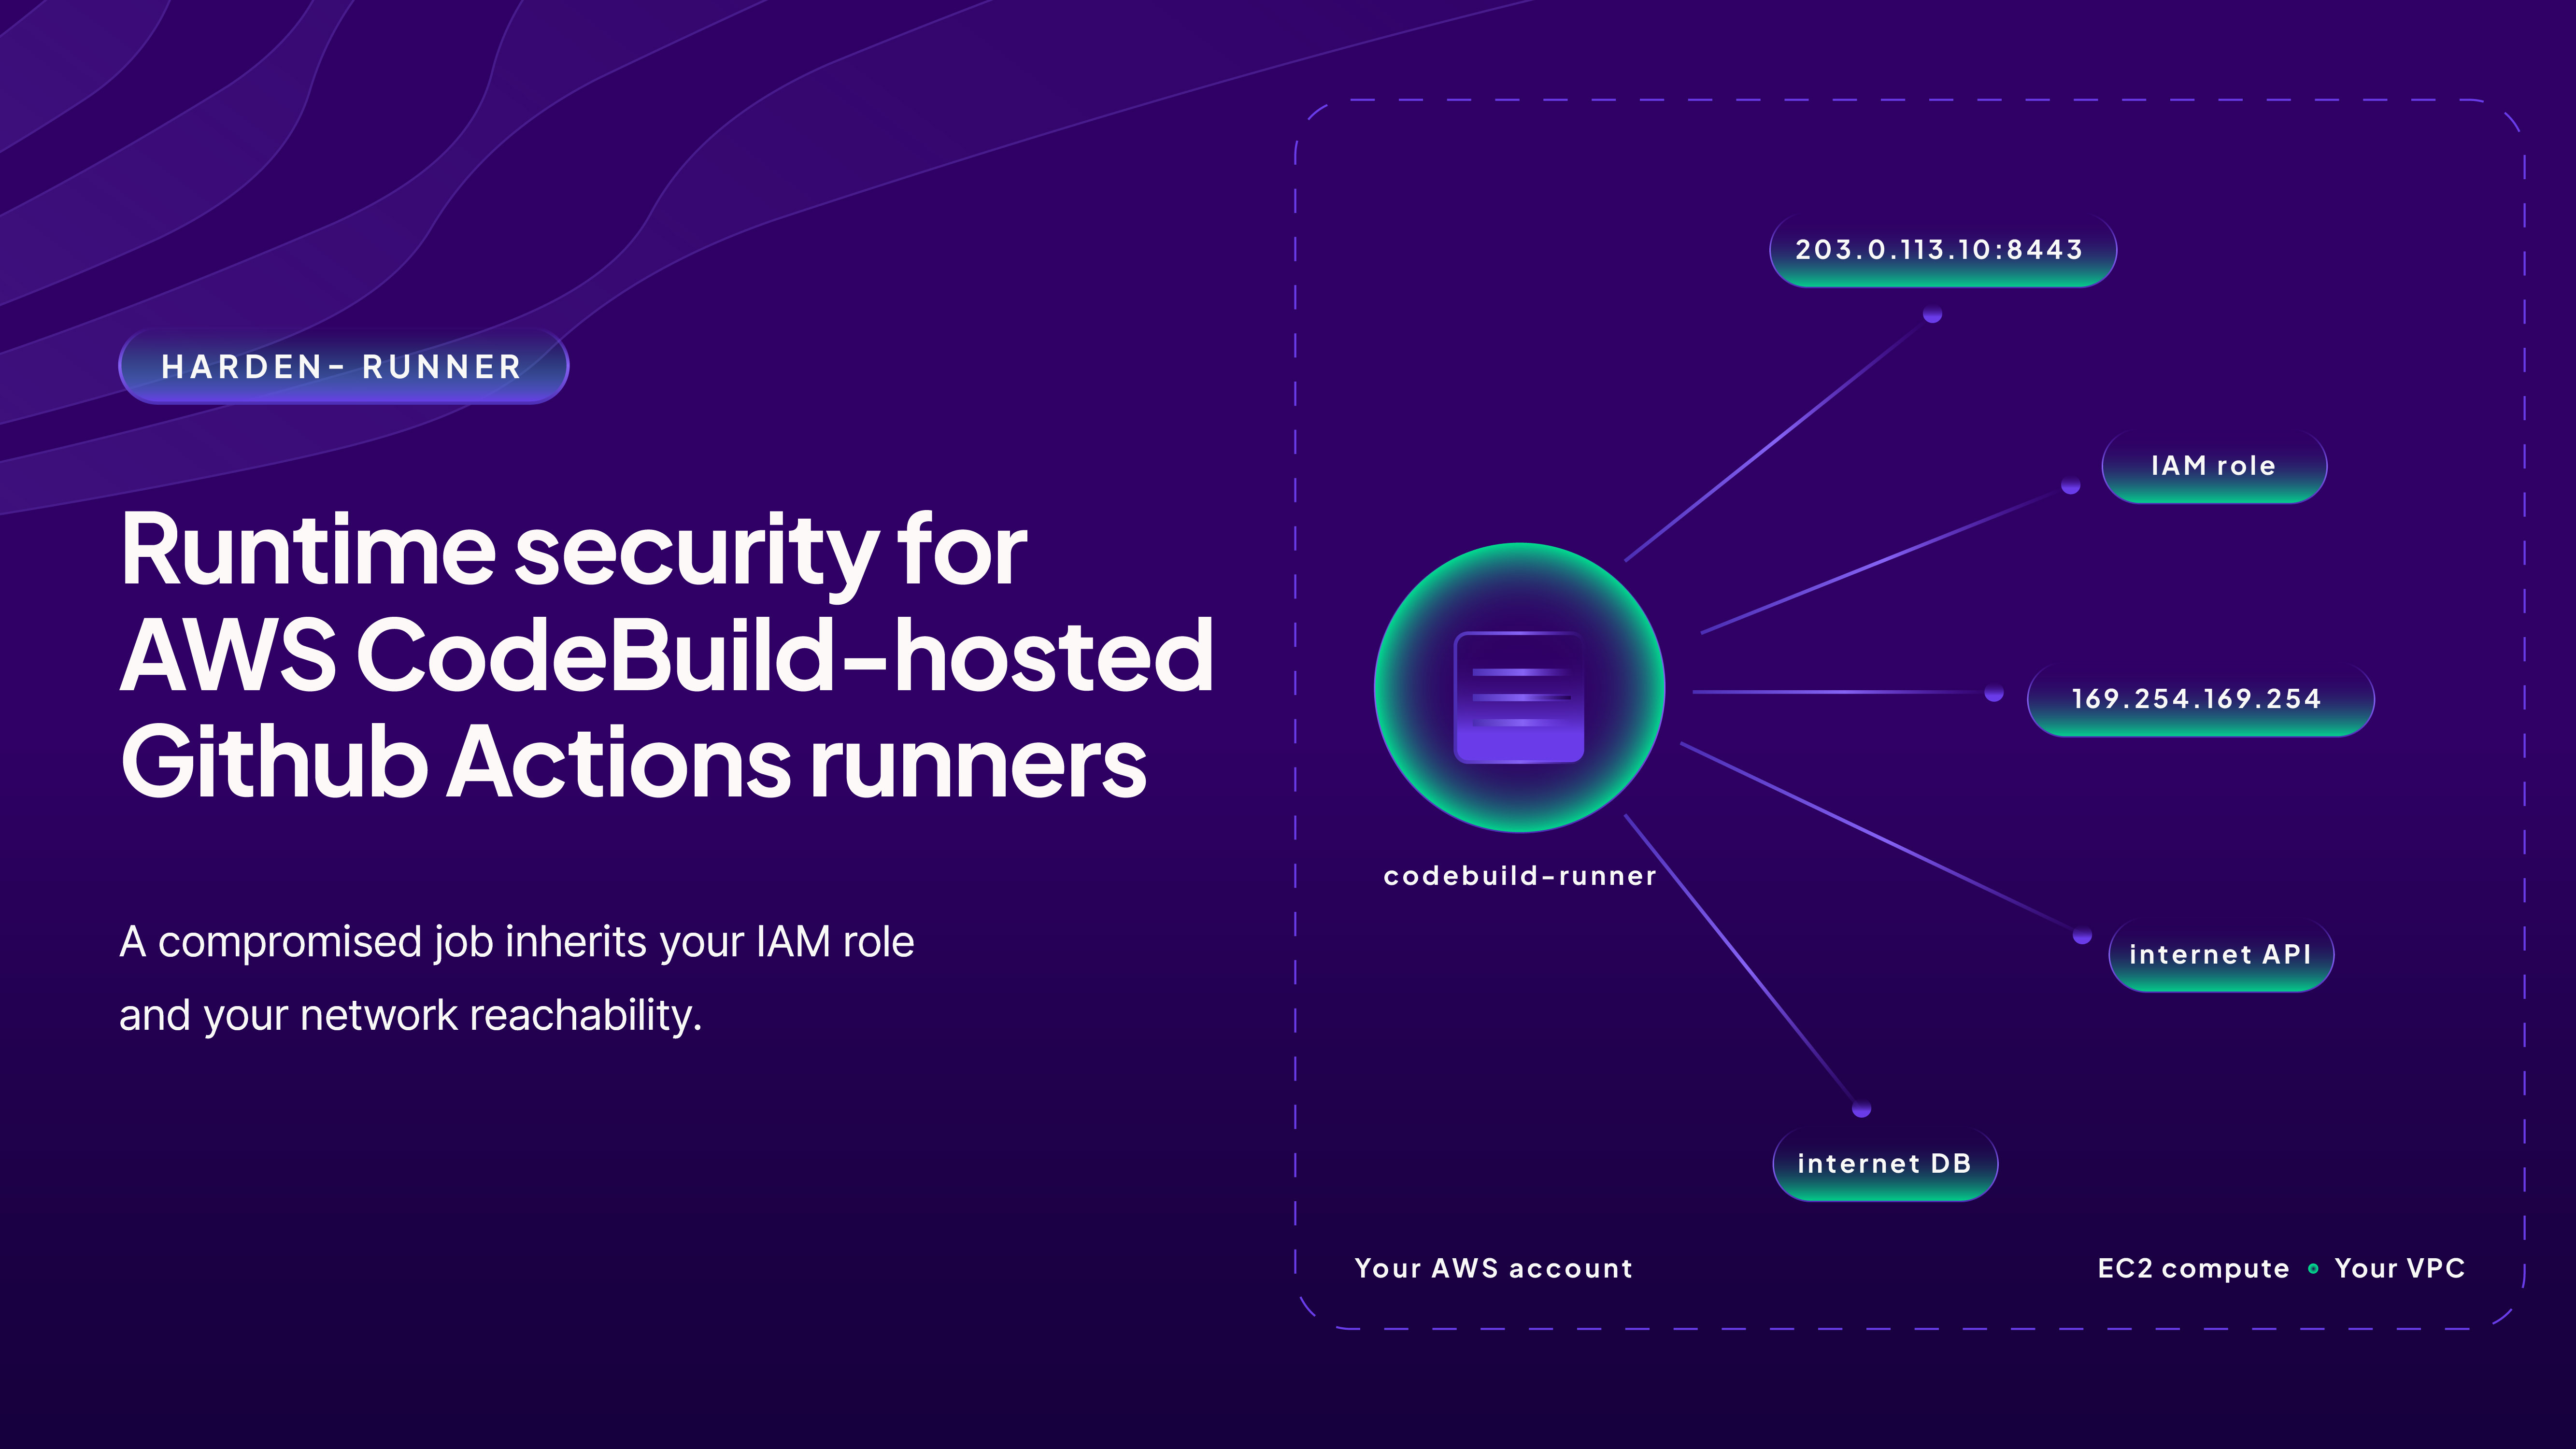
- CodeBuild-hosted jobs can inherit the build environment's IAM role and, when configured in a VPC, its network reachability, increasing the potential impact of a compromised job.
- The article cites a July 2025 CodeBuild memory-dump incident and the Team PCP campaign as examples of credential theft risks in CI pipelines.
Article Details
- Event Type
- Security product capability announcement: Harden-Runner added support for GitHub Actions runners hosted on AWS CodeBuild.
- Impact
- Harden-Runner captures and correlates outbound network calls, file writes, and process executions to workflow steps on supported CodeBuild runners, providing visibility into activity that may not appear in GitHub job logs. The article highlights the elevated risk of compromised jobs inheriting a CodeBuild project's IAM role and VPC network access, and notes that Harden-Runner detects the memory-reading technique associated with CVE-2025-8217.
CVE
Vendors
Amazon Web ServicesIn July 2025, AWS disclosed that a threat actor had stolen source repository access tokens by dumping the memory of a CodeBuild build environment. A malicious pull request was enough. When the build ran, it read theGitHubThat is the environment more and more teams are now pointing their GitHub Actions jobs at. AWS CodeBuild can register itself as a just-in-time GitHub Actions runner, so a job that used to run on ubuntu-latest runs
Products
AWS CodeBuildStudio Code and the AWS SDK for .NET. We covered the incident and the technique in Lessons from AWS CodeBuild's Memory-Dump Incident (CVE-2025-8217).AWS SDK for .NETthe attacker used it to reach the repositories behind the AWS Toolkit for Visual Studio Code and the AWS SDK for .NET. We covered the incident and the technique in Lessons from AWS CodeBuild's Memory-Dump IncidentAWS Toolkit for Visual Studio Codememory and exfiltrated it, and the attacker used it to reach the repositories behind the AWS Toolkit for Visual Studio Code and the AWS SDK for .NET. We covered the incident and the technique in Lessons from AWSGitHub ActionsThat is the environment more and more teams are now pointing their GitHub Actions jobs at. AWS CodeBuild can register itself as a just-in-time GitHub Actions runner, so a job that used to run on ubuntu-latest runsHarden-RunnerHarden-Runner now supports those runners.