August 2026 Cyberattacks Targeted U.S. and European Businesses Through Session Theft and Remote Access
Summary
ANY.RUN's August roundup describes campaigns abusing legitimate remote-management tools, Microsoft 365 sessions, hiring processes and business-themed files to gain access, steal credentials and deploy remote-control malware against U.S. and European organizations.
Key points
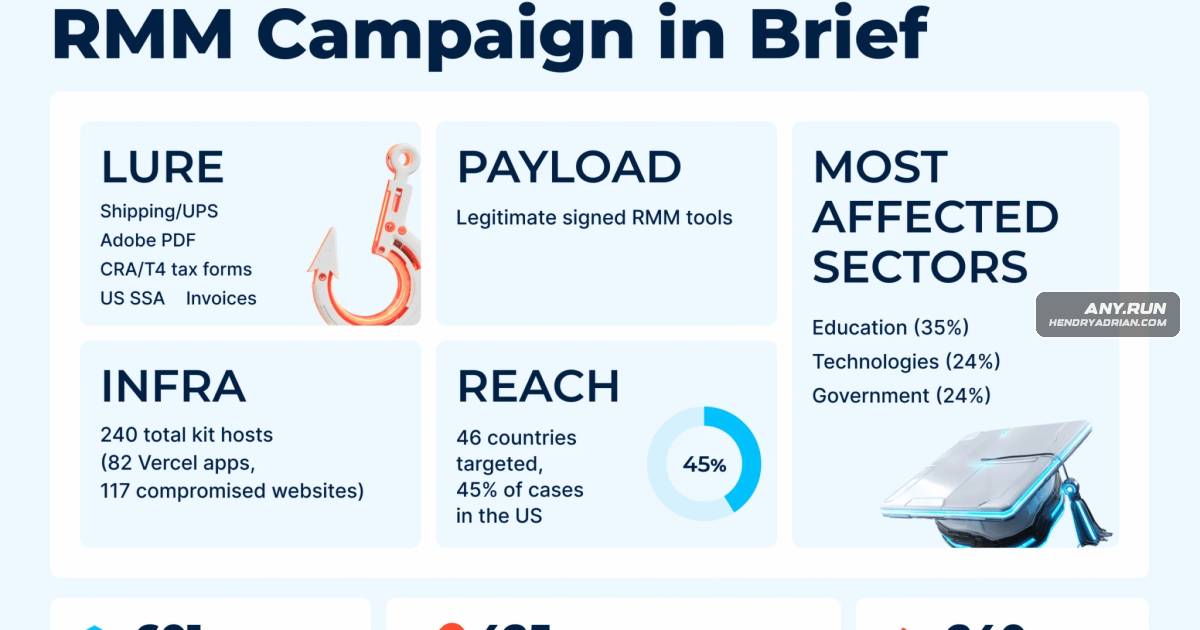
- A phishing campaign observed in 46 countries used business-themed documents to trick victims into installing legitimate RMM tools; 45% of observed activity was associated with the United States.
- An investigation into suspected Famous Chollima operatives found forged or stolen identities and remote-access tools used in a fake hiring process, exposing how false identities could gain legitimate access to internal systems and intellectual property.
- Mirage2FA reportedly targeted more than 4,000 U.S. victims, stealing credentials, MFA codes and session cookies to hijack Microsoft 365 sessions.
- SnakeBiteAgent, a .NET remote-access trojan delivered in a business-themed ZIP file, can steal credentials, log keystrokes, capture webcam and microphone activity, and install additional remote-access tools.
- The 3DBlast phishing kit impersonated Microsoft, Office 365 and Google login flows and could switch techniques, including AiTM and OAuth/device-code phishing.
- The article recommends revoking compromised sessions and tokens, investigating activity under affected identities, using phishing-resistant MFA, and monitoring for unexpected RMM installations and remote-access activity.
Article Details
- Event Type
- Reporting on phishing, session hijacking, remote-access malware, abuse of legitimate remote-management software, and suspected insider infiltration observed in August 2026.
- Impact
- ANY.RUN reported a remote-management phishing operation spanning 46 countries, with 45% of observed activity associated with the United States. Mirage2FA affected over 4,000 victims in the United States, with session theft reported as the most common compromise outcome. Reported exposure included corporate accounts, credentials, email, cloud files, and internal documents. SnakeBiteAgent could provide full remote control, credential theft, and persistent surveillance. An investigation involving suspected Famous Chollima operatives demonstrated how fraudulent hiring identities could obtain legitimate access to source code, internal systems, and intellectual property.
MITRE ATT&CK
T1056.001 · KeyloggingSnakeBiteAgent included keylogging capabilities.T1123 · Audio CaptureSnakeBiteAgent could capture microphone audio.T1125 · Video CaptureSnakeBiteAgent could capture webcam activity.T1219 · Remote Access ToolsAttackers abused legitimate remote-management applications for remote access; SnakeBiteAgent could silently install AnyDesk and MeshCentral.T1539 · Steal Web Session CookieMirage2FA intercepted authenticated Microsoft 365 session cookies.T1550.004 · Web Session CookieStolen authenticated session cookies allowed attackers to hijack active Microsoft 365 sessions after users completed MFA.T1557 · Adversary-in-the-MiddleMirage2FA used adversary-in-the-middle techniques to intercept credentials, authentication codes, and session cookies; 3DBlast also supported AiTM flows.T1566.001 · Spearphishing AttachmentBusiness-themed documents and archives were used as phishing delivery mechanisms, including a ZIP archive containing SnakeBiteAgent.
Threat Actors
Famous ChollimaA joint investigation hired suspected operatives into a fake DeFi startup and observed forged and stolen identities, mule bank accounts, VPNs, remote desktop software, and AI-assisted document manipulation.Lazarus APTThe article described the investigated IT workers as Lazarus APT's workers; the investigation narrative identified them as suspected Famous Chollima operatives.
Malware
Vendors
Products
AnyDeskIts capabilities include credential theft, keylogging, hidden desktop access, webcam and microphone capture, and silent installation of AnyDesk and MeshCentral for additional remote access.ConnectWiseThe campaign abused signed RMM tools including GoTo Resolve, LogMeIn Rescue, ScreenConnect, ConnectWise, and ITarian to establish hands-on remote access.GoTo ResolveThe campaign abused signed RMM tools including GoTo Resolve, LogMeIn Rescue, ScreenConnect, ConnectWise, and ITarian to establish hands-on remote access.ITarianThe campaign abused signed RMM tools including GoTo Resolve, LogMeIn Rescue, ScreenConnect, ConnectWise, and ITarian to establish hands-on remote access.LogMeIn RescueThe campaign abused signed RMM tools including GoTo Resolve, LogMeIn Rescue, ScreenConnect, ConnectWise, and ITarian to establish hands-on remote access.MeshCentralIts capabilities include credential theft, keylogging, hidden desktop access, webcam and microphone capture, and silent installation of AnyDesk and MeshCentral for additional remote access.Microsoft 365Across the US and Europe, attackers abused Microsoft 365 sessions, legitimate remote-management tools, business-themed files, and even hiring processes to reach corporate systems.Office 365A newly observed phishing kit, 3DBlast, targeted users in the United States while impersonating Microsoft 365, Office 365, and Google.ScreenConnectThe campaign abused signed RMM tools including GoTo Resolve, LogMeIn Rescue, ScreenConnect, ConnectWise, and ITarian to establish hands-on remote access.
Tools
3DBlastIdentity compromise threatened core workflows: Mirage2FA and 3DBlast targeted Microsoft 365 sessions, OAuth, device-code authentication, and MFA flows, putting email, cloud files, supplier communication, and financeANY.RUN Interactive SandboxFull attack behavior revealed inside ANY.RUN’s Interactive SandboxANY.RUN Threat Intelligence FeedsANY.RUN’s Threat Intelligence Feeds provide newly observed malicious IPs, domains, and URLs that teams can integrate into SIEM, SOAR, TIP, firewalls, and other security tools.ANY.RUN Threat Intelligence LookupAnalysts can use ANY.RUN’s Threat Intelligence Lookup to pivot from recurring campaign patterns and uncover related activity:Mirage2FAIdentity compromise threatened core workflows: Mirage2FA and 3DBlast targeted Microsoft 365 sessions, OAuth, device-code authentication, and MFA flows, putting email, cloud files, supplier communication, and finance
Countries
Industries
ConsultingTechnology, manufacturing, education, consulting, and telecommunications were among the industries exposed.EducationTechnology, manufacturing, and education ManufacturingTechnology, manufacturing, and education TechnologyTechnology, manufacturing, and education TelecommunicationsTechnology, manufacturing, education, consulting, and telecommunications were among the industries exposed.