cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3810 articles

Security News · huntress.com

TrickBot Adds TrickBoot Module for Firmware Attacks

Huntress reported new TrickBot functionality, dubbed TrickBoot, that can identify firmware vulnerabilities and may read, write, or erase device firmware. The article outlines indicators, attack flow, and Huntress’s detection efforts.
Dec 2, 2020
Security News · darkowl.com

Darknet Vendors Market Disinformation Services and Claimed Blockchain-Based Persistence

DarkOwl describes darknet vendors offering social media manipulation, reputation attacks and disinformation services. One vendor claimed blockchain-based content persistence; the article also discusses election-related typosquatting and financially motivated disinfo.

Oct 13, 2020
Security News · darkowl.com

DarkOwl Finds Thousands of Stolen Accounts Listed on UpShop Darknet Market

DarkOwl researchers observed 3,121 stolen accounts for sale on UpShop, along with 10 identities and an email-flooding service. The market appeared operational at the time of the report.

Sep 23, 2020
Security News · huntress.com

Huntress Launches External Recon to Monitor Internet-Exposed Services

Huntress External Recon scans organizations’ public IPs for exposed services using Shodan, helping identify changes to the external attack surface. It cannot identify which internal endpoint exposes a service.

Jul 21, 2020
Security News · darkowl.com

Maze Ransomware Group Announces New Extortion Terms and Names Alleged Victims

Maze said it would name alleged victims within three days, require contact within 72 hours, and publish their data after ten days without successful negotiations. Its list included Xerox and LG Electronics.

Jul 15, 2020
Security News · huntress.com

Huntress Announces Ransomware Canaries and External Port Monitoring

Huntress announced two services for its platform: Ransomware Canaries to support faster detection during ransomware incidents, and Open Port Detection to monitor external exposure, including open RDP ports.

Jun 22, 2020
Security News · darkowl.com

REvil Expands Ransomware Extortion Campaign, Auctions Alleged Agromart Data

DarkOwl tracked REvil/Sodinokibi’s expanding extortion campaign, including leak-site claims against multiple companies, an auction of alleged Agromart data, and Elexon’s confirmation of an intrusion; other breach and data-release claims remained uncertain.

Jun 2, 2020
Security News · darkowl.com

Zoom Account Listings Linked to Credential Stuffing, Not a Breach of Zoom

DarkOwl linked Zoom account listings to credential stuffing using credentials from earlier breaches, not a breach of Zoom’s systems. The article also covers Zoom-bombing, privacy concerns, security updates, and user safeguards.

May 1, 2020
Security News · darkowl.com

DarkOwl Reports COVID-19 Scams on the Darknet, Finds No Evidence of Increased Forum Use

DarkOwl analysts found darknet offers for fake COVID-19 vaccines, samples, test kits and drugs, plus redirects to potentially malicious downloads. Their forum-registration data showed no evidence of increased darknet use during the pandemic.

Apr 9, 2020
Security News · darkowl.com

Darknet Markets See COVID-19 Scams and Fraudulent Medical Supply Listings

DarkOwl reports COVID-19-related offers and discussions on darknet platforms, including allegedly infected bodily fluids, purported vaccines, masks and sanitizer. The article warns that many listings appear fraudulent and describes pandemic-driven discussion channels.

Mar 24, 2020
Security News · huntress.com

Huntress Rewrites Its Agent Updater in Go to Support TLS 1.2

Huntress rewrote its agent updater in Go to avoid .NET compatibility issues with TLS 1.2. The company said it would test the new updater before a planned rollout later in 2019.

Oct 3, 2019
Security News · darkowl.com

8chan’s ZeroNet Backup Sees Surge in Activity Amid Service Disruptions

DarkOwl reported that an 8chan backup on ZeroNet, observed since April, became active as the forum faced service disruptions and DDoS attacks. An 8chan admin denied that the team created the backup; the claim remained under investigation.

Aug 6, 2019
Security News · darkowl.com

New Dream Market-Based Saṃsāra Market Faces Security and Legitimacy Concerns

Saṃsāra, a market launched by a former Dream moderator using Dream Market source code, drew skepticism over its legitimacy, early security bugs, legacy Tor mirrors and apparent IP-address leaks.

Jul 9, 2019
Security News · darkowl.com

2019 Darknet Market Turmoil: Seizures, Exit Scams and DDoS Disruptions

A 2019 overview traces darknet market closures, alleged exit scams, law-enforcement seizures and arrests, DDoS disruptions, and shifts to alternative services, while noting uncertainty around some claims and the volatile status of active markets.

Jun 28, 2019
Security News · darkowl.com

KickAss Forum Goes Offline Amid Unconfirmed Takedown and Phishing Concerns

KickAss’s recent Tor addresses went offline after the forum switched to private access. DarkOwl notes an unfamiliar Jabber contact and a move to OTR, raising—but not confirming—the possibility of a law-enforcement seizure or phishing attempt.

Jan 11, 2019
Security News · darkowl.com

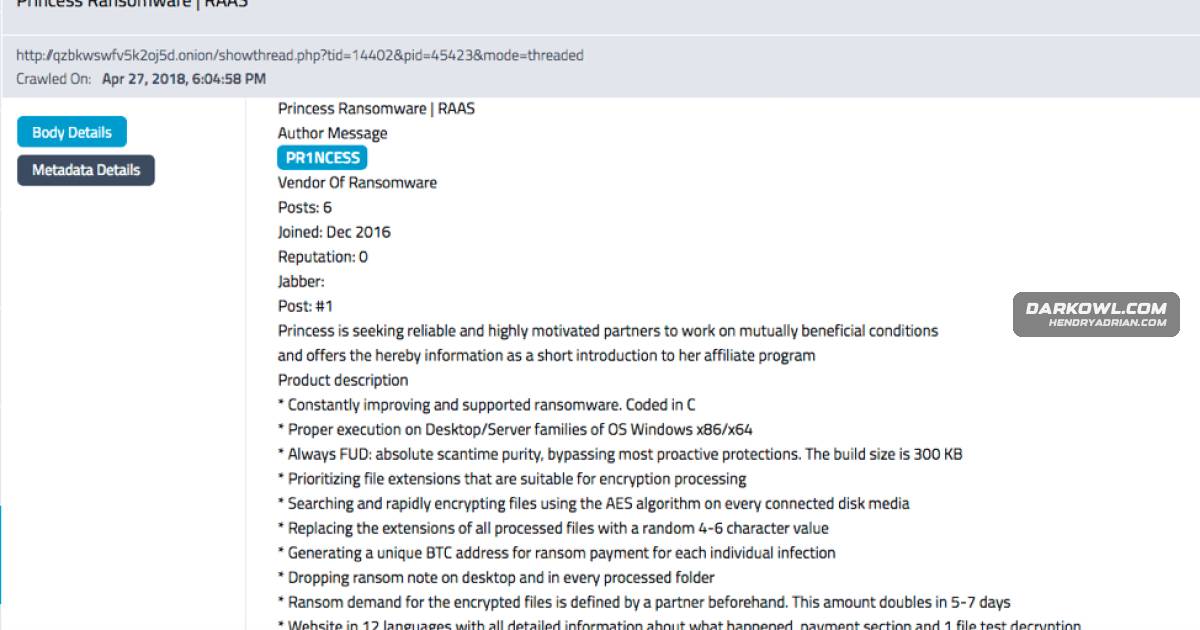
Princess Evolution Ransomware Was Advertised on Darknet Markets Months Earlier Than Reported

DarkOwl analysts found Princess Evolution advertised on darknet marketplaces as early as April 2018, months before mid-August reports. The ransomware was offered as a service, and DarkOwl counted over 100 comments from prospective associates.

Sep 20, 2018
Security News · darkowl.com

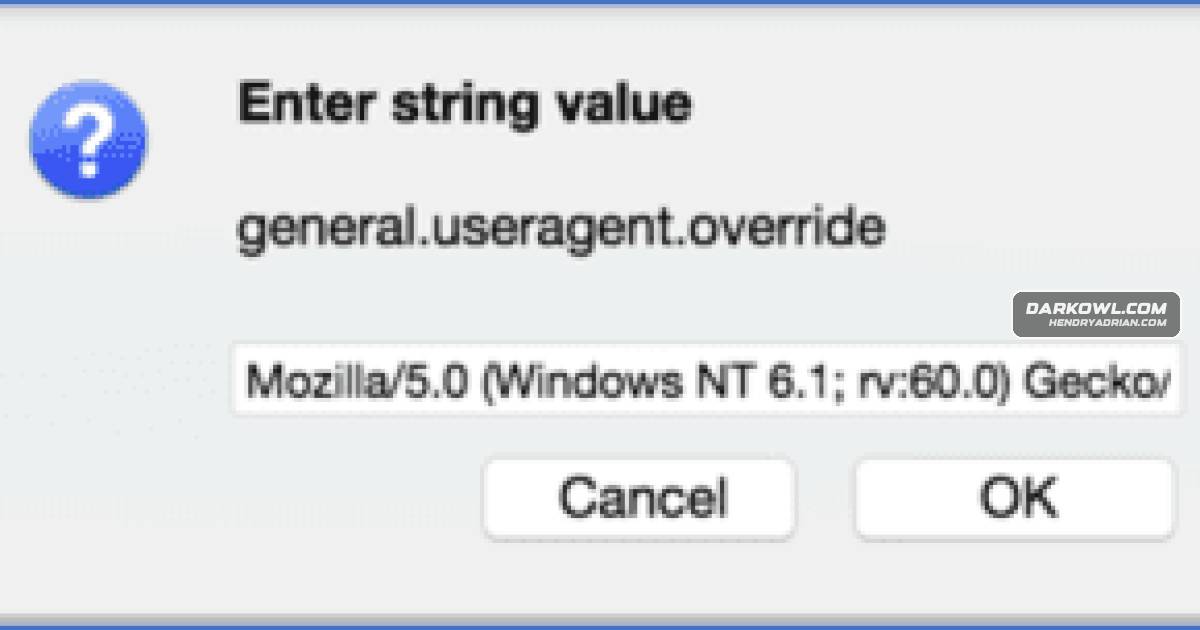
Tor Browser Release Exposed Users’ Operating Systems, While Compromised MEGA Extension Stole Credentials

The article reports that Tor Browser 8.0/8.5a1 exposed users’ operating systems in user-agent strings and that a compromised MEGA Chrome extension harvested credentials and cryptocurrency keys before an update was released.

Sep 18, 2018
Security News · huntress.com

Huntress Sets October Deadline for Updating Agents Affected by Symantec Certificate Changes

Huntress said agents version 0.7.85 and older would stop communicating with its servers after October 6, 2018, following changes affecting Symantec-issued certificates. Partners were urged to deploy newer installers.

Sep 6, 2018
PreviousPage 159 of 159
© 2026 cyber.hendryadrian.com