
Zoom Account Listings Linked to Credential Stuffing, Not a Breach of Zoom
Summary
DarkOwl linked Zoom account listings to credential stuffing using credentials from earlier breaches, not a breach of Zoom’s systems. The article also covers Zoom-bombing, privacy concerns, security updates, and user safeguards.
Key points
- DarkOwl said it found no evidence that attackers breached Zoom’s servers or user database.
- The researchers assessed that credential stuffing with previously exposed username-password pairs was used to validate Zoom logins; a sample of listed accounts matched credentials in earlier breach collections.
- A marketplace offered a claimed 500,000 verified accounts for $10,000, but the seller’s identity and the listing’s legitimacy were unclear.
- The article describes Zoom-bombing risks from guessing meeting IDs and cites reports of a tool that could automate this activity.
- Zoom’s updates included longer meeting IDs, more complex meeting-password support, default password protection for shared cloud recordings, and removing the Join Before Host option.
- The article recommends unique passwords for each service and password-protecting meetings and shared recordings.
- It also discusses privacy concerns over Zoom sharing user data with Facebook and a related lawsuit.
Article Details
- Event Type
- Credential-stuffing exposure and sale of Zoom account credentials, alongside reported Zoom-bombing and privacy concerns.
- Impact
- DarkOwl assessed that credentials from prior breaches were tested against Zoom logins, with about 500,000 verified accounts reportedly offered for sale; it found no indication Zoom itself was breached. Unauthorized meeting access and Zoom-bombing were also reported. Zoom users faced account and meeting security risks, and some organizations said they would stop using the software.
MITRE ATT&CK
T1110.004 · Credential StuffingDarkOwl assessed that attackers used credential stuffing to test previously exposed username and password combinations against Zoom authentication.T1595.003 · Wordlist ScanningThe article describes automated enumeration of Zoom meeting IDs by generating candidate numbers and testing meeting URLs.
People
Vendors
Products
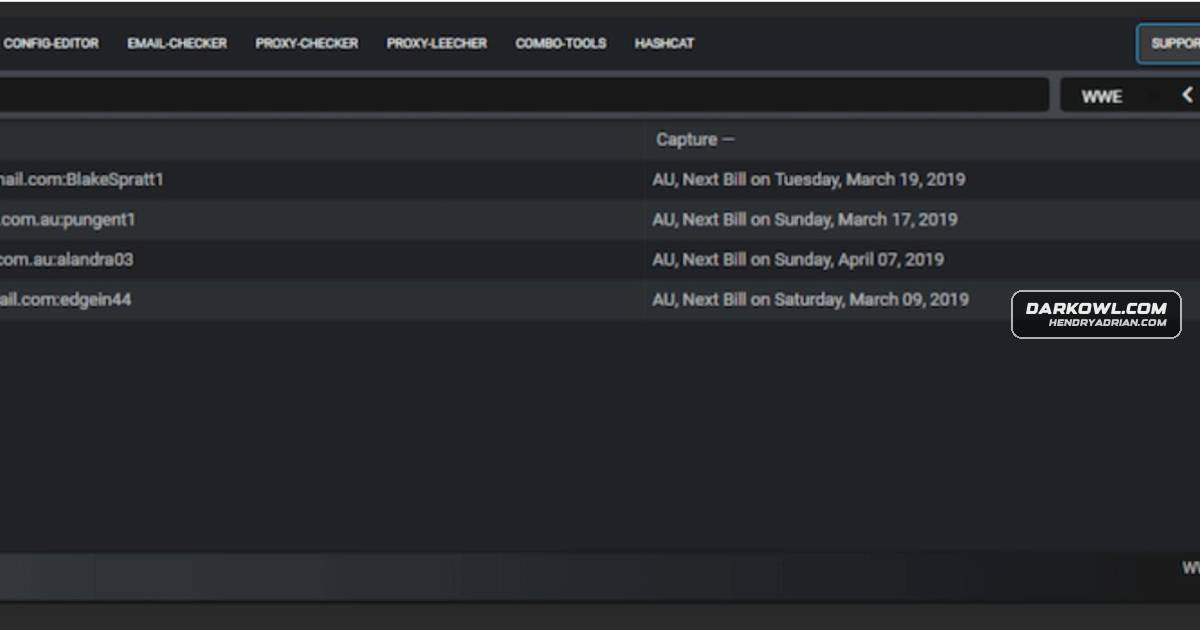
SNIPROne such tool called SNIPR (pictured) is a leading credential-stuffing toolkit supporting multiple attack surfaces including web requests (http/s) and IMAP-based email accounts without the need for any command-line orZoomAs most of the world shelters in place due to the COVID-19 pandemic, Zoom – the video conferencing tool we’re all very familiar with by now – has witnessed an extraordinary surge in use.Zoom iOS appThe lawsuit follows a MotherBoard report that verified how the Zoom iOS app for Apple smartphones was sharing information with Facebook about its users without their consent.ZWarDialFor example, last week, hackers on popular darknet cybersecurity forum Torum mentioned a resourceful tool called the ZWarDial code, developed by KCSec.
Tools
SniprOne such tool called SNIPR (pictured) is a leading credential-stuffing toolkit supporting multiple attack surfaces including web requests (http/s) and IMAP-based email accounts without the need for any command-line orZWarDialFor example, last week, hackers on popular darknet cybersecurity forum Torum mentioned a resourceful tool called the ZWarDial code, developed by KCSec.