REvil Expands Ransomware Extortion Campaign, Auctions Alleged Agromart Data
Summary
DarkOwl tracked REvil/Sodinokibi’s expanding extortion campaign, including leak-site claims against multiple companies, an auction of alleged Agromart data, and Elexon’s confirmation of an intrusion; other breach and data-release claims remained uncertain.
Key points
- DarkOwl observed 41 data-leak posts on REvil’s Happy Blog, whose post numbering had reached 76; it assessed that other victims may have paid or not yet been named.
- REvil advertised Agromart data for auction, claiming it held more than 22,000 files and three databases. The hackers set a $50,000 starting price and a $100,000 blitz price.
- REvil posted claims involving companies including Telkom, Elexon, law firms, and FARO. Elexon acknowledged an intrusion on May 14, 2020, and said there was no risk to the public, customer-level data, or power supplies.
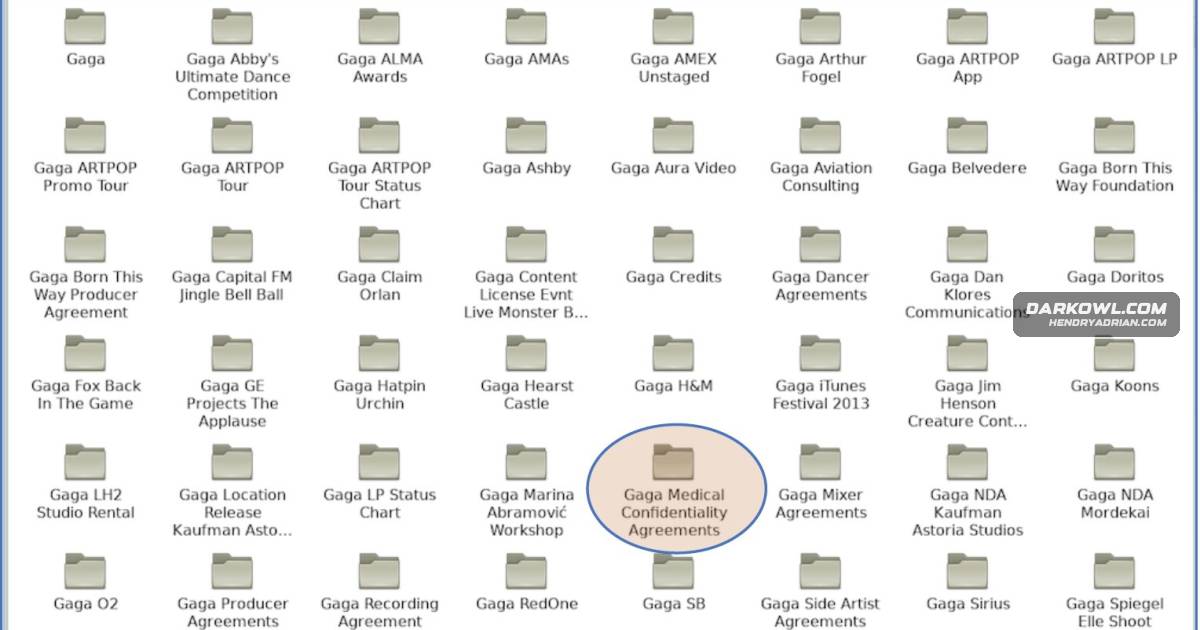
- Grubman Shire Meiselas & Sacks confirmed a ransomware attack in May 2020. The attackers demanded $21 million, later claiming to double the demand, and published more than 2 GB of files concerning Lady Gaga; the article says Trump-related correspondence appeared, but his personal files were not published.
- REvil claimed it released FARO data after a ransom deadline; its post later disappeared. DarkOwl said this might indicate payment, but the outcome was unclear.
- The article describes Sodinokibi as spreading through infected JavaScript on WordPress sites, deleting Shadow Volume Copies, disabling Windows Startup Repair, and encrypting files.
Article Details
- Event Type
- Ransomware and data-extortion campaign attributed in the article to REvil/Sodinokibi, involving data theft, public leaks, and auctions of compromised data.
- Impact
- The article reports attacks against organizations in several sectors, including Grubman Shire Meiselas & Sacks, Sherwood Food Distributors, Agromart Group, FARO Technologies, and others. The attackers claimed to have stolen sensitive business, legal, and personal data; some data was published or offered for sale, and victims faced ransom demands. The article says Elexon reported no risk to the public, no loss of customer-level data, and no impact to power supplies. It is unclear whether Agromart’s attack affected Canada’s farming industry, and the article does not establish whether all reported compromises or data claims were independently verified.
MITRE ATT&CK
People
Donald TrumpThe attackers threatened to publish information about him and later claimed to have additional information; the article says the disclosed material included references to him and associates, not his personal files.Lady GagaThe article reports that data relating to her was published in a leak from the Grubman Shire Meiselas & Sacks attack.MadonnaThe attackers announced plans to auction personal files they claimed to have.
Threat Actors
REvilThe article identifies REvil as a name for the ransomware hackers responsible for the reported attacks; it also refers to the group as Sodinokibi.SodinokibiThe article identifies Sodinokibi as a name for the ransomware hackers responsible for the reported attacks; it also refers to the group as REvil.
Malware
Countries
Industries
AgricultureThey also introduced an “auction” feature to their website, with Canadian agriculture company Agromart Group’s data as their first lot, starting bids at $50,000 USD.EnergyTELECOMMUNICATIONS AND ENERGY FIRMS NOT IMMUNEManufacturingFARO Technologies, a Leading 3D Printing/Manufacturing Company, is Latest Victim of REvil Hackers’ Ransomware AttacksTelecommunicationsTELECOMMUNICATIONS AND ENERGY FIRMS NOT IMMUNE