
Princess Evolution Ransomware Was Advertised on Darknet Markets Months Earlier Than Reported
Summary
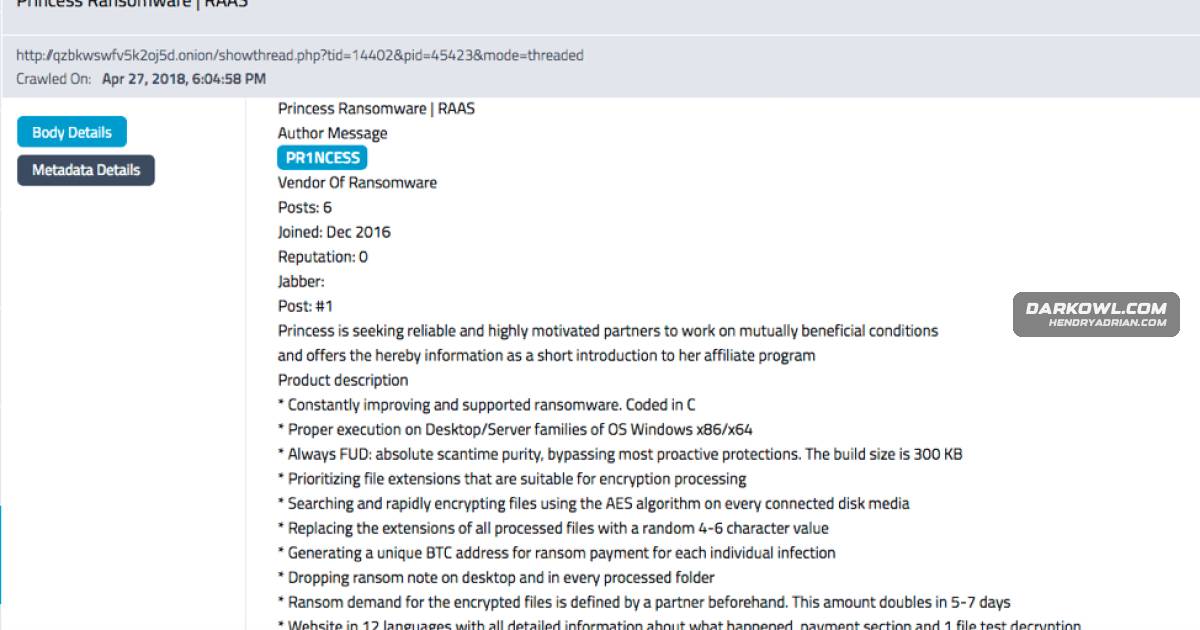
DarkOwl analysts found Princess Evolution advertised on darknet marketplaces as early as April 2018, months before mid-August reports. The ransomware was offered as a service, and DarkOwl counted over 100 comments from prospective associates.
Key points
- DarkOwl analysts found Princess Evolution listings on darknet marketplaces dating back to April 2018, earlier than mid-August coverage suggested.
- The malware was advertised on the 0day forum as ransomware-as-a-service, seeking associates to spread it.
- DarkOwl counted more than 100 comments from people interested in joining the campaign since the April listing was scraped.
- The article says the ransomware encrypts files, changes their extensions to random character strings, and leaves victims a ransom note.
- As of August 8, 2018, the ransom demand was 0.12 bitcoin, reported at the time as equivalent to US$773.
- The article recommends following a ransomware recovery guide and maintaining security best practices and employee education.
Article Details
- Event Type
- Princess Evolution ransomware was found being advertised as ransomware-as-a-service on darknet marketplaces earlier than contemporaneous news reports suggested.
- Impact
- The ransomware encrypts most files on an infected computer and holds them for ransom. The article says that, as of August 8, 2018, victims were instructed to pay 0.12 bitcoin. Associates were being solicited to distribute the malware; DarkOwl analysts estimated that more than 100 people had commented with interest since the original post was scraped in April.
Malware
Princess EvolutionNews broke out mid-August that Princess Evolution, a revamped form of the infamous Princess Locker ransomware that was first seen several years ago, is back with a fresh toolkit (see this article for example).Princess LockerNews broke out mid-August that Princess Evolution, a revamped form of the infamous Princess Locker ransomware that was first seen several years ago, is back with a fresh toolkit (see this article for example).