
Team Cymru RADAR Uses Passive Telemetry for External Asset Discovery
Team Cymru says RADAR uses PureSignal’s 40+ telemetry datasets to map internet-facing IPs, ranges, domains and subdomains, with CVE and known exploited vulnerability context.
Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.
3802 articles
Team Cymru says RADAR uses PureSignal’s 40+ telemetry datasets to map internet-facing IPs, ranges, domains and subdomains, with CVE and known exploited vulnerability context.
Huntress reports that attackers used fake Social Security, invitation, and invoice lures to trick employees into installing rogue ScreenConnect clients. It observed recurring domains across businesses and recommends auditing RMM use and reviewing execution logs.
Hunt.io reviews 2025 platform upgrades for threat investigations, its internet-scale reconnaissance figures, threat-hunting resources, and research on campaigns, malware, and malicious infrastructure.
Wiz says its platform now maps OCI identities, permissions, and policies into a unified security graph, enabling cross-cloud access analysis and checks for risks such as excessive permissions, missing MFA, and unused keys.
Team Cymru says Operation Sentinel supported law enforcement in 19 African countries, resulting in 573 arrests, $3 million recovered, more than 6,000 malicious links taken down and six ransomware variants decrypted.
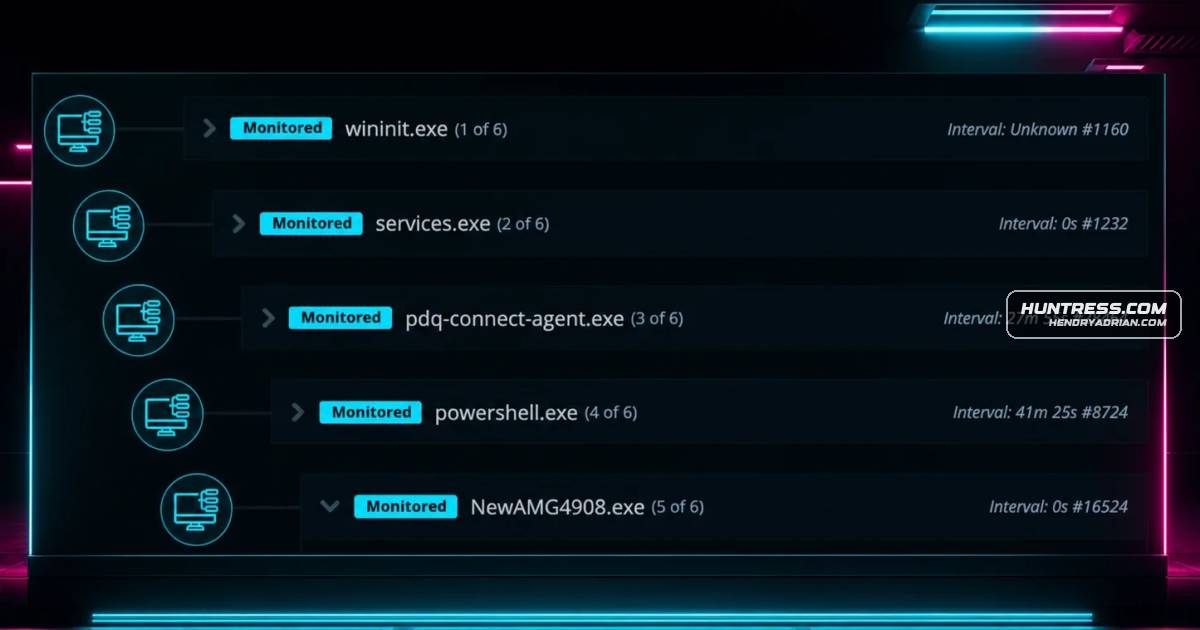
Huntress describes incidents where phishing-led access through tools such as GoTo Resolve or PDQ enabled attackers to install additional RMM software, including ScreenConnect and SimpleHelp, for continued access. Its SOC says it stopped the reported attacks.
Hunt 2.8 adds negative filters for C2 and AttackCapture listings, improves IOC Hunter and provider visibility, expands bulk enrichment, and fixes issues affecting malware hosts, time-range pivots, and phishing false positives.
Zscaler says its upcoming ThreatLabz 2026 AI Security Report will examine enterprise AI usage, including popular models and applications, regional and industry patterns, and risk mitigation. The preview’s preliminary data runs through November 2025.
At Wiz Research’s two-day cloud hacking competition, researchers reported successful vulnerability demonstrations involving Redis, PostgreSQL, MariaDB, Grafana and the Linux kernel, earning $320,000. Attempts involving vLLM and Ollama timed out.
Google will stop scanning for users’ data on the dark web on January 15, 2026, and delete past reports on February 16. It says the alerts did not provide helpful next steps.
Team Cymru says RADAR can pivot selected IPs or CIDR ranges into automatically generated Scout queries, surfacing recent NetFlow, PassiveDNS and certificate activity and tagged malicious-IP communications for threat hunting and attribution.
CVE-2025-55182, an unauthenticated remote-code-execution flaw in React Server Components affecting React 19 and related frameworks such as Next.js, is being actively exploited. Apply the listed patches and review dependencies.
The article reviews AWS announcements including browser-based CLI login, outbound identity federation with AWS principals, IAM policy generation, temporary delegation, organization-level S3 Block Public Access, and a TLS proxy.
Team Cymru says RADAR links domains to internet-facing assets, enriches IPs with CVE data, and filters for known exploited vulnerabilities to help teams prioritize remediation.
A reported npm campaign includes 36 Christmas-themed packages across 23 users. Older packages send /opt/index.js to a collection endpoint; newer ones use a preinstall script to send files from /opt to a webhook.
Team Cymru and Abusix announced a partnership combining Team Cymru botnet intelligence with Abusix reporting to help ISPs and hosting providers address Mirai infections. The companies say a one-week test processed more than 43 million feed records.
Wiz says its SAST tool is in public preview for Wiz Code customers, with repository and pull request scanning, Security Graph context, AI-assisted triage and remediation, and integrations for findings from other scanners.
Wiz announced general availability of Exposure Management, combining tools to ingest and contextualize security findings, validate external exposure and exploitability, and prioritize remediation across cloud, on-prem, code, AI and SaaS environments.
Team Cymru says RADAR uses PureSignal data to map third-party internet-facing IPs, domains and CIDR ranges, with graph views and details including CVEs, KEVs, shared infrastructure, location and ASNs.
Wiz reports continued, slower Shai-Hulud 2.0 spread, with a December 1 spike. Analysis of more than 30,000 repositories found exposed credentials, including still-valid npm tokens, and infections across npm, OpenVSX, and Maven.
Wiz says WizOS provides container images with near-zero CVEs and verifiable provenance. The GA release adds image catalog coverage and AI-assisted migration planning and image swaps through Wiz’s platform and MCP.
A roundup covers BlackCat ransomware indictments, actively exploited vulnerabilities, a University of Pennsylvania data breach, malicious NuGet packages, APT37 Android attacks, Iranian malware activity and a new ransomware-as-a-service platform.
A 2024 international operation dismantled iServer, a phishing-as-a-service platform used to steal credentials and one-time codes to unlock stolen devices. Authorities arrested 17 people and seized the platform’s domain.
Group-IB says its investigation linked an actor using aliases including ALTDOS and DESORDEN to data breaches and extortion across multiple regions. Intelligence shared with Thai and Singapore police contributed to a raid and arrest in Thailand.