Hunt 2.8 Adds C2 Filters, IOC Hunter Improvements, and More Accurate Threat Views
Summary
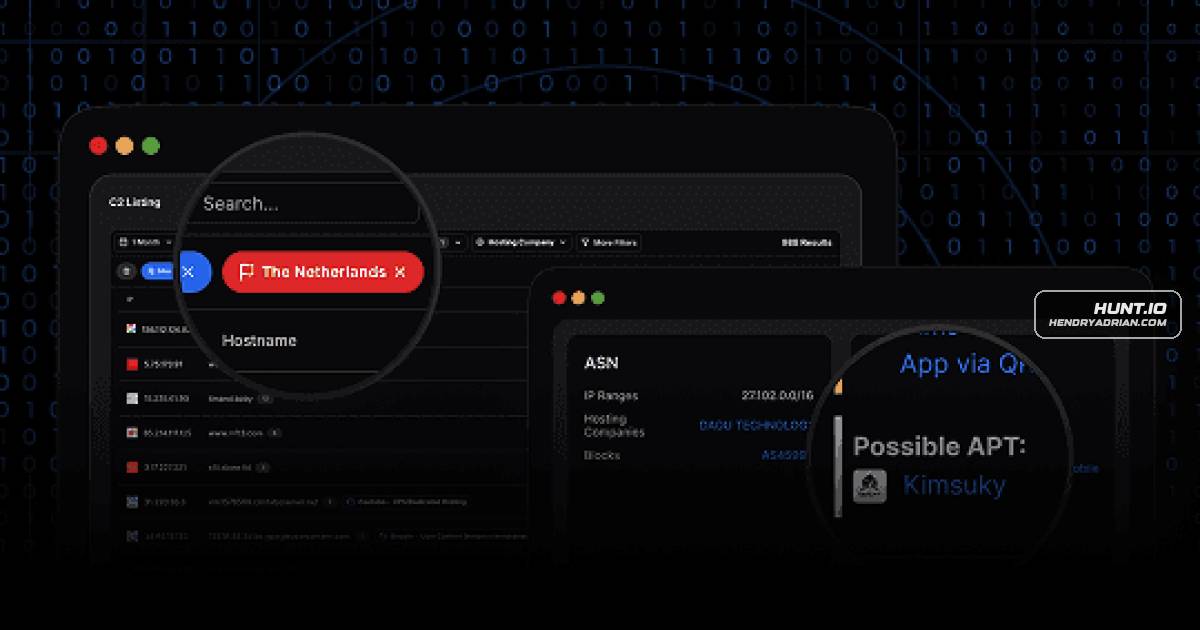
Hunt 2.8 adds negative filters for C2 and AttackCapture listings, improves IOC Hunter and provider visibility, expands bulk enrichment, and fixes issues affecting malware hosts, time-range pivots, and phishing false positives.
Key points
- C2 and AttackCapture listings now support negative filters for providers, countries, ports, and top-level domains.
- Provider tags are visible in IP search and C2 listings; bulk enrichment now includes registrar and domain creation date.
- IOC Hunter adds direct links to hosts and IPs, malware-family labels, custom date ranges, and a unified shareable post layout.
- Host Radar improvements restore malware-related hosts and improve partial-name matching.
- Reputation & Risk phishing filtering was corrected to remove false positives and show only confirmed malicious URLs.
- AttackCapture time-range pivots were fixed, and IP pages now display HTTP and HTTPS status codes for open ports.
Article Details
- Event Type
- Hunt 2.8 product release with improvements to threat-investigation workflows, filtering, data visibility, and detection accuracy.
- Impact
- The release adds provider tags, expanded bulk enrichment, faster IOC pivots, and negative filters for C2 and AttackCapture listings. It also fixes indexing, display, time-range pivoting, and phishing-filter issues; the source says the phishing filter now shows only confirmed malicious URLs.
Vendors
Products
AttackCaptureC2 & AttackCapture⢠Improvements Added negative filters to the C2 listing page and the AttackCapture listing page, enabling more focused C2 investigations.Host RadarUsability Improvements Faster pivots through direct IOC Hunter linking, refined phishing dark mode, and consistent unified filters across malware lists and Host Radar.Hunt 2.8Hunt 2.8 brings major improvements across C2 listings, IOC Hunter, AttackCaptureâ¢, IP search, and domain risk assessment.IOC HunterHunt 2.8 brings major improvements across C2 listings, IOC Hunter, AttackCaptureâ¢, IP search, and domain risk assessment.Reputation & RiskRadar, fixed malware name display in IOC Hunter posts, and removed phishing false positives from Reputation & Risk views.