cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3802 articles

Security News · darktrace.com

Darktrace Reports 620% Surge in Black Friday Phishing Attempts

Darktrace says Black Friday-related phishing attempts rose 620% in the weeks before the holiday, with a further 20–30% increase expected during Black Friday week. Campaigns impersonate retailers and use fake deal sites to steal personal and payment data.
Nov 27, 2025
Security News · team-cymru.com

Team Cymru Details RADAR Tool for Mapping Internet-Exposed Assets

Team Cymru describes RADAR, a tool that uses PureSignal data to map linked internet-facing IPs, CIDR ranges and domains, then enriches results with tags for providers, open ports and systems carrying known vulnerabilities.

Nov 19, 2025
Security News · huntress.com

Huntress Acquires Inside Agent to Build Identity Security Posture Management Offering

Huntress says its acquisition of Microsoft 365 security company Inside Agent will support an Identity Security Posture Management product planned for 2026. The company says existing Inside Agent tools, pricing, and support will remain unchanged for now.

Nov 18, 2025
Security News · team-cymru.com

Operation Endgame Disrupts Infrastructure Linked to Rhadamanthys, VenomRAT and Elysium

Team Cymru says its analysis helped identify Rhadamanthys infrastructure as Europol-coordinated Operation Endgame disrupted 1,025 servers, seized 20 domains and led to an arrest in Greece.

Nov 14, 2025
Security News · huntress.com

Huntress Details Threats and Attacks Targeting Schools

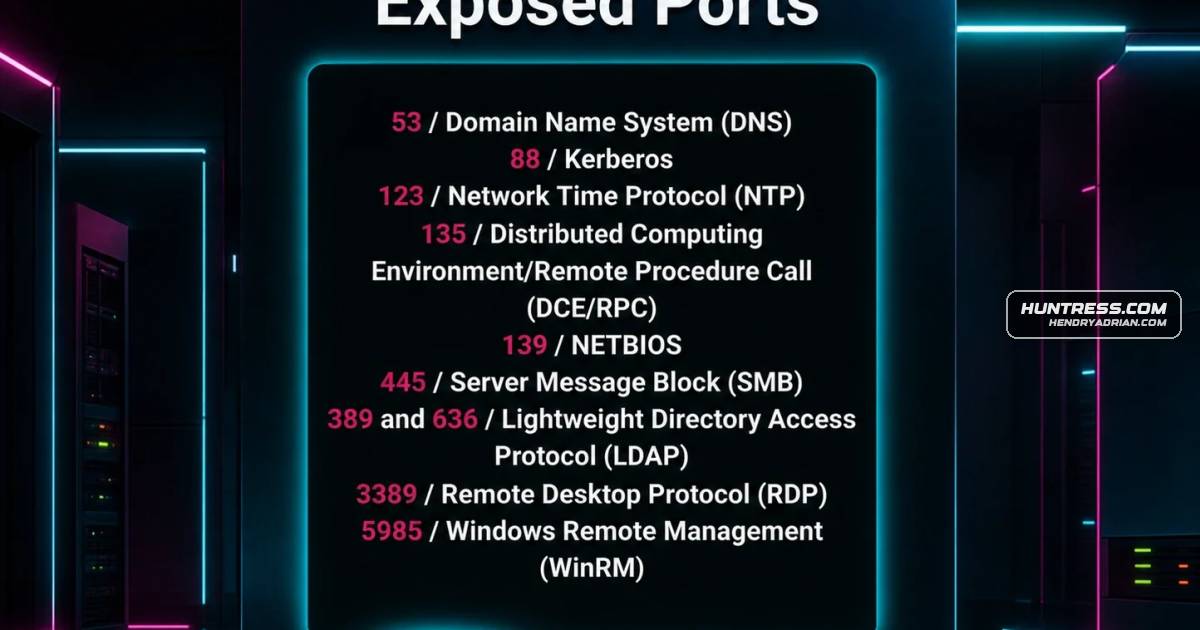
Huntress reports education accounted for 21% of incidents it observed in 2024, including attacks involving exposed RDP, compromised RMM tools and attempted data theft. It recommends MFA, patching, tested backups and monitoring.

Nov 13, 2025
Security News · wiz.io

Wiz Launches Posture Issues to Organize Cloud Security Backlogs

Wiz introduced Posture Issues, which group cloud vulnerability, secrets, or data findings under configurable policies to help teams prioritize remediation, track SLAs, and monitor security-posture progress.

Nov 12, 2025
Security News · team-cymru.com

Team Cymru Introduces PureSignal RADAR for Passive Exposure Discovery

Team Cymru says PureSignal RADAR uses observed network traffic to discover internet-facing assets and enrich them with context such as threat indicators, CVEs, and KEVs. The vendor describes uses in shadow IT and third-party risk assessment.

Nov 12, 2025
Security News · hunt.io

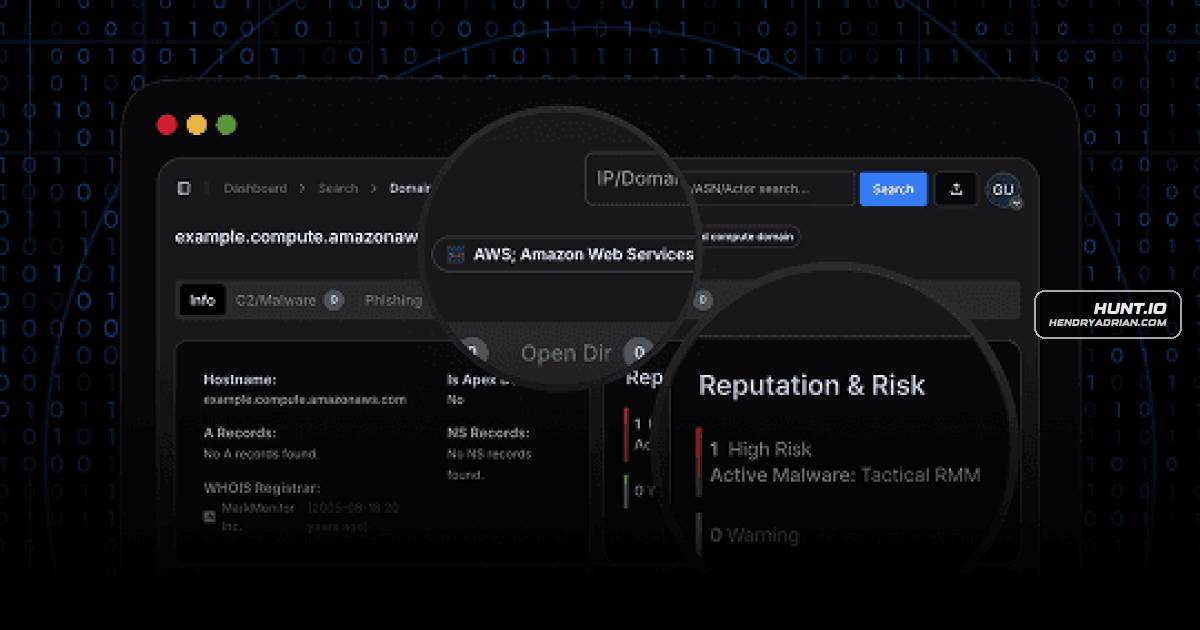
Hunt 2.7 Adds Threat Indicators, IOC Visibility, and Faster Investigations

Hunt 2.7 updates its threat-hunting platform with expanded domain risk indicators, threat actor visibility on IP and domain pages, faster C2 listings and risk cards, and new AttackCapture filters and investigation pivots.

Nov 6, 2025
Security News · huntress.com

Huntress and DEFCERT Release Resources to Help Organizations Prepare for CMMC Assessments

Huntress and DEFCERT created CMMC preparation resources, including responsibility matrices and documentation templates. Huntress Sensitive Data Mode limits which file extensions SOC analysts can retrieve from hosts, helping address CUI handling in assessments.

Nov 5, 2025
Security News · wiz.io

Wiz Announces AI Security Agents, Agentless Workload Detection and Expanded Cloud Security Features

At its Wizdom 2025 conference, Wiz announced AI agents, Microsoft 365 security integration, agentless workload threat detection, expanded AI security posture management, and attack surface management, with several features entering public preview.

Nov 4, 2025
Security News · darkowl.com

DarkOwl’s October Threat Intelligence Roundup Covers Breaches, Malware and Exploits

DarkOwl’s roundup highlights ransomware and data-breach claims, a $15 billion crypto seizure, malware campaigns, Salesforce-related extortion, actively exploited vulnerabilities, and a breach affecting 17.6 million Prosper accounts.

Nov 3, 2025
Security News · arstechnica.com

Leaked Cellebrite Matrix Details Pixel Data-Extraction Capabilities

A leaked Cellebrite briefing screenshot reportedly says its tools can extract data from stock Pixel 6–9 phones in BFU, AFU and unlocked states, while updated GrapheneOS builds resist extraction. The claims are not independently verified.

Oct 30, 2025
Security News · darkowl.com

DarkOwl Adds Darknet Marketplace Research Features to Vision

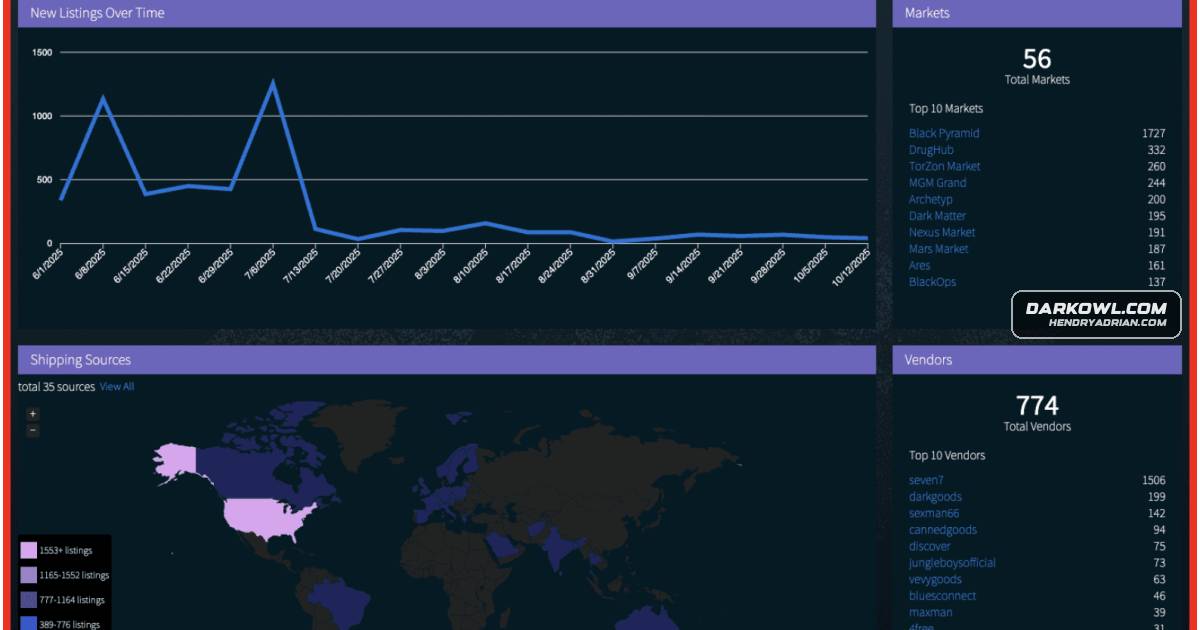
DarkOwl added marketplace search, summaries, and listing details to Vision UI and API, alongside other search updates. The post also highlights curated information on several alleged data leaks, including an Allianz Life incident reportedly confirmed by the company.

Oct 23, 2025
Security News · darktrace.com

Darktrace Adds Endpoint Process Context to Network Threat Investigations

Darktrace announced NEXT, combining network visibility with endpoint process telemetry to support automated threat investigations, alongside updates to network detection, response, and security-platform management.

Oct 23, 2025
Security News · hunt.io

Hunt 2.6 Adds IP Risk and Reputation Data and Expands IOC Hunting

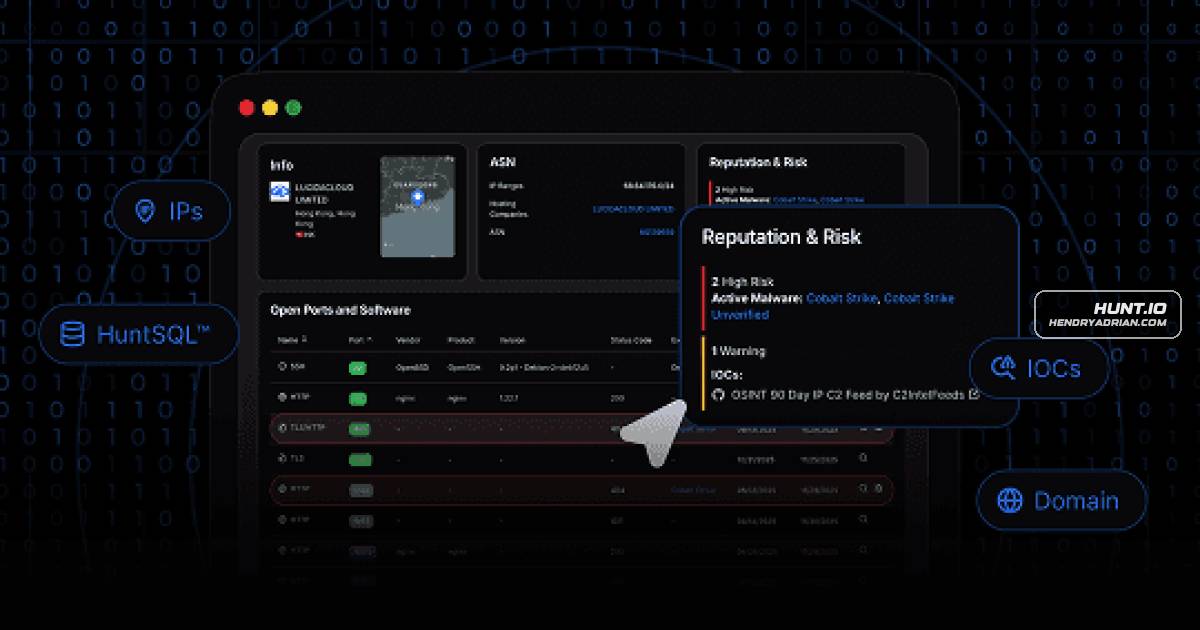
Hunt 2.6 adds IP risk and reputation details, expands IOC Hunter sources and C2 infrastructure data, and updates its API, integrations, search, and investigation features.

Oct 20, 2025
Security News · wiz.io

Wiz Finds 550 Leaked Secrets in VSCode Extensions, Including Tokens That Could Enable Malicious Updates

Wiz found over 550 secrets in more than 500 VSCode and Open VSX extensions, including over 100 tokens that could enable malicious updates affecting a reported 150,000 installs. Microsoft revoked marketplace tokens and added secret scanning and blocking.

Oct 15, 2025
Security News · ncsc.gov.uk

NCSC Urges F5 Customers to Apply Security Updates After Network Compromise

F5 reported a network compromise and data exfiltration that included some BIG-IP source code and vulnerability information. The NCSC advises identifying F5 products, securing management interfaces and installing F5’s latest security updates; no customer network impact,

Oct 15, 2025
Security News · wiz.io

Wiz Open-Sources HoneyBee to Automate Cloud Honeypot Deployment

Wiz introduced HoneyBee, an open-source tool that generates intentionally misconfigured Docker environments for honeypots, testing detections, and research. Wiz says its honeypots observed attackers exploiting exposed JDWP and weak PostgreSQL credentials.

Oct 7, 2025
Security News · darkowl.com

UK and EU Cybersecurity Rules Extend Accountability Across Supply Chains

A webinar discusses how the EU Cyber Resilience Act, NIS2 and the UK Cyber Security and Resilience Bill expand cybersecurity duties, including continuous monitoring, supply-chain oversight and incident reporting.

Oct 7, 2025
Security News · threatfabric.com

OneSpan Makes Strategic Investment in Mobile Fraud-Prevention Firm ThreatFabric

ThreatFabric says OneSpan has made a strategic investment to support its global fraud-prevention efforts. OneSpan will join ThreatFabric’s Board of Directors and Strategic Advisory Board.

Oct 6, 2025
Security News · arstechnica.com

Study Finds AI-Designed Toxin Variants Could Evade DNA Screening Tools

Researchers tested about 75,000 AI-designed variants of 72 toxins against four DNA-order screening programs. Detection varied, and three packages were updated; the study relied on predicted structures and did not establish that the variants were functional toxins.

Oct 3, 2025
Security News · arstechnica.com

Google details free and paid Android developer verification, with no public developer list

Google says Android 16 will add verification for sideloaded apps, with a $25 paid tier and a free hobbyist/student option. Checks may require internet access, and Google says harmful apps could trigger deactivation across a developer’s apps.

Oct 3, 2025
Security News · huntress.com

ClickFix Variants, Deepfake Scams and ViewState Attacks Feature in 2025 Threat Trends

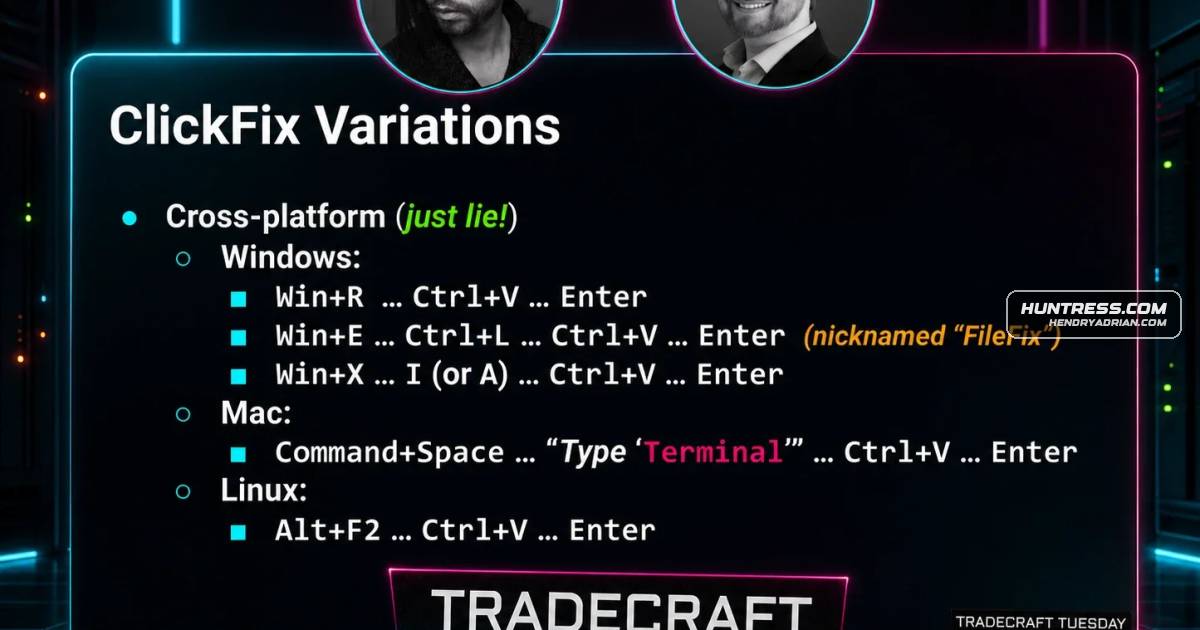
Huntress reviews 2025 threat trends, including cross-platform ClickFix lures, deepfake-enabled social engineering and attacks exploiting exposed ASP.NET machine keys for ViewState code injection.

Oct 2, 2025
Security News · darkowl.com

Threat Intelligence Roundup Highlights Breaches, Malware and Cybercrime Operations

A September threat intelligence roundup covers a fintech breach, phishing targeting diplomats, cybercrime arrests, FBI alerts, ransomware-related airport disruption, malware attacks on developer accounts and Android ad fraud.

Oct 1, 2025
PreviousPage 145 of 159 Next
© 2026 cyber.hendryadrian.com