Huntress Details 2025 Social-Engineering Lures Used to Deploy Rogue ScreenConnect
Summary
Huntress reports that attackers used fake Social Security, invitation, and invoice lures to trick employees into installing rogue ScreenConnect clients. It observed recurring domains across businesses and recommends auditing RMM use and reviewing execution logs.
Key points
- Huntress observed rogue ScreenConnect activity throughout 2025, including an uptick in compromised instances at the end of September.
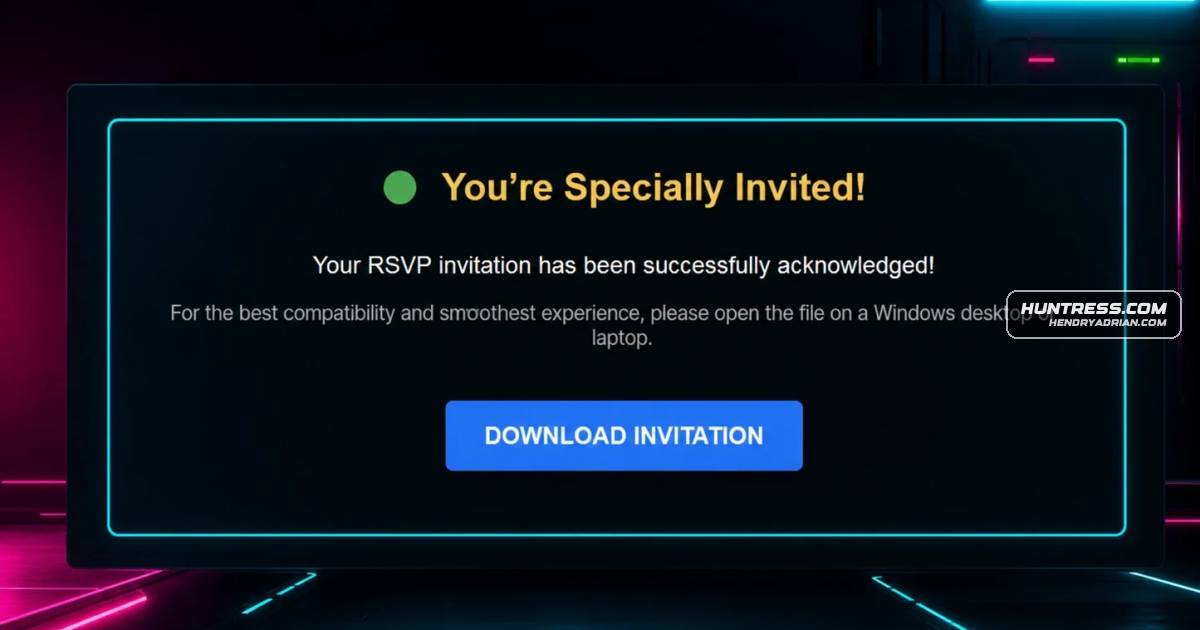
- Lures impersonated Social Security documents, event invitations, invoices, and financial statements to persuade employees to run executable files.
- In one investigated case, a phishing email led a user through a Google Docs URL to an invitation-themed download; the rogue client then gave the attacker remote access to the endpoint.
- Huntress found domains reused across multiple customer accounts; lory473[.]top appeared across 15 accounts from January 13 to February 5, 2025, with many targeted businesses in accounting.
- The article identifies domains and SHA256 hashes associated with rogue ScreenConnect signals, including subjent25[.]zapto[.]org; Huntress says attackers abused dynamic DNS services to host infrastructure.
- Huntress says ScreenConnect accounted for 74.5% of the top abused remote-access tools it observed.
- Recommended steps include auditing and monitoring RMM tools, reviewing execution logs, and updating RMM software; Huntress also describes checking installer callback domains and their reputation.
Article Details
- Event Type
- Huntress reported recurring social-engineering campaigns in 2025 that tricked employees into downloading rogue ScreenConnect clients, often disguised as Social Security documents, invitations, invoices, or financial statements.
- Impact
- The rogue ScreenConnect installations provided threat actors remote access to victim endpoints. Huntress reported repeated use of malicious domains across multiple customer accounts, including incidents affecting businesses in the accounting sector; one invoice-themed attack led several users at a retail organization to download the executable.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 0bd0[.]adrsxpjm0rga0n[.]de | Listed by Huntress among domains linked to rogue ScreenConnect instances. |
| DOMAIN | advancedaiinfrastructures[.]com | Listed as an attack domain associated with a rogue ScreenConnect executable. |
| DOMAIN | lory473[.]top | Huntress reported this malicious domain was used in rogue ScreenConnect incidents across 15 customer accounts. |
| DOMAIN | pv-sq[.]innocreed[.]com | Listed as an attack domain associated with a rogue ScreenConnect executable. |
| DOMAIN | rok628[.]mxhelp[.]top | Listed by Huntress among malicious domains associated with rogue ScreenConnect incidents. |
| DOMAIN | sans[.]infosedi[.]de | Domain configured to manage a rogue ScreenConnect installation that gave the threat actor remote access to an endpoint. |
| DOMAIN | slplegalfinance[.]com | Listed by Huntress among malicious domains linked to rogue ScreenConnect instances. |
| DOMAIN | subjent25[.]zapto[.]org | Huntress linked this domain to rogue ScreenConnect attacks and described its use in the malicious incidents. |
| DOMAIN | yoc736[.]ikhelp[.]top | Listed by Huntress among malicious domains associated with rogue ScreenConnect incidents. |
| SHA256 | 1af6e82e53622e4404668aa00e2772aae2515110a4440721c2ece040011fe981 | SHA-256 hash listed for an executable associated with a domain used in rogue ScreenConnect incidents. |
| SHA256 | 44b6b1de9a618c97788631bc89372435a6ea0357e50497152a67219dea400209 | SHA-256 hash listed for an executable associated with a rogue ScreenConnect domain. |
| SHA256 | 7fdfe8b34ad911fa007d9f2c8b2cb99cea0ac760d23643850a72e75cf8aa62c3 | SHA-256 hash identified by Huntress among hashes linked to rogue ScreenConnect instances. |
| SHA256 | 82cb1fee5f4a7420d378efe0c4a9fc52d547208cb04c87d17c37b714778c9935 | SHA-256 hash listed for a rogue ScreenConnect-related executable. |
| SHA256 | 8b7cf22511ad2579339c7b05f513d02dd2d0d8c35f523cb79875006520f8435b | SHA-256 hash listed for an executable associated with a rogue ScreenConnect domain. |
| SHA256 | 9681d73bdba27623a68e4faf1a10d928e6ca0e9fe697a378b96957c6aa46c38e | SHA-256 hash listed for an executable associated with a rogue ScreenConnect domain. |
| SHA256 | 99d2abed5ce05b6616a33c16911038a40a7fabda7a6a4c2220daaf7ae4e6512c | SHA-256 hash identified by Huntress among hashes linked to rogue ScreenConnect instances. |
| SHA256 | 9d6a88f2458481cfe1b3c5f4ce4dc76a1cf04f210fb6cbaa106bde3f7116330d | SHA-256 hash listed for an executable associated with a domain used in rogue ScreenConnect incidents. |
| SHA256 | a3e314dc43a4410e9bc8d93b27da8a7764138c6b453b8eb5fb6845f948901cf6 | SHA-256 hash listed for an executable associated with a domain used in rogue ScreenConnect incidents. |
| SHA256 | afa765b692d2952cf8693c9d5b7070214e11f9f681f4b4f14142531cadaf3e92 | SHA-256 hash identified by Huntress among hashes linked to rogue ScreenConnect instances. |
| SHA256 | b218a4d70fabb2b1e986449597e4c40f9b8d10b1b5038e9e53d14534703ba8d1 | SHA-256 hash listed for an executable associated with a rogue ScreenConnect domain. |
| SHA256 | b3636a27cba5ba4c0c41e60c90a57a3250cbfbd1042879515cc132f74354d06e | SHA-256 hash listed for a rogue ScreenConnect-related executable. |
| SHA256 | bdbac9fe9e7aca3a03d55867eddd905c4e222f3045b0015b823df4f034ee007a | SHA-256 hash listed for rogue ScreenConnect invoice-lure executables. |
| SHA256 | d8afcd4a1ad314c4f310a90e4f55d08155685585ac7dd03353794e493f312ce0 | SHA-256 hash listed for a rogue ScreenConnect-related executable. |
MITRE ATT&CK
T1219 · Remote Access ToolsThreat actors deployed or abused ScreenConnect and other remote monitoring and management software to gain remote access and maintain persistence.T1566.002 · Spearphishing LinkThreat actors used phishing lures to prompt employees to download rogue ScreenConnect installers.
People
Vendors
Products
AteraIn fact, out of the top abused remote access tools Huntress has observed, ScreenConnect makes up 74.5%, leading other tools like RDP, LogMeIn, TeamViewer, Atera, VNC, and NinjaRMM.Huntress Managed EDRIf a rogue ScreenConnect attack is underway, however, Huntress Managed Endpoint Detection and Response (EDR) can help businesses determine if the instance is legitimate or malicious.LogMeInAttackers are using RMMs like ScreenConnect, TeamViewer, LogMeIn, and more as a way to gain access, blend in, move laterally, and maintain persistence.NinjaRMMIn fact, out of the top abused remote access tools Huntress has observed, ScreenConnect makes up 74.5%, leading other tools like RDP, LogMeIn, TeamViewer, Atera, VNC, and NinjaRMM.Remote Desktop Protocol (RDP)In fact, out of the top abused remote access tools Huntress has observed, ScreenConnect makes up 74.5%, leading other tools like RDP, LogMeIn, TeamViewer, Atera, VNC, and NinjaRMM.ScreenConnectThe Huntress Security Operations Center (SOC) frequently comes across incidents involving rogue ScreenConnect installations.TeamViewerAttackers are using RMMs like ScreenConnect, TeamViewer, LogMeIn, and more as a way to gain access, blend in, move laterally, and maintain persistence.VNCIn fact, out of the top abused remote access tools Huntress has observed, ScreenConnect makes up 74.5%, leading other tools like RDP, LogMeIn, TeamViewer, Atera, VNC, and NinjaRMM.
Industries
accountingNotably, in looking at data linked to lory473[.]top (in Figure 6 above), we found that almost all the targeted businesses were firms in the accounting sector.InsuranceIn April, Huntress observed a user at an insurance agency executing a suspicious process after downloading the executable Social_Security_Statements_April2025_Updates.Client.exe from a website.real estateIn May, Huntress observed a user at a real estate developer executing a malicious process (special invitation letter(2).exe).RetailThe latter executable (RevisedStatementJAN2025.exe) was part of a targeted phishing attack sent to several different users at a retail organization in January.