Researchers Say APT28 Exploited Zimbra Flaw in Ukrainian Government Attacks
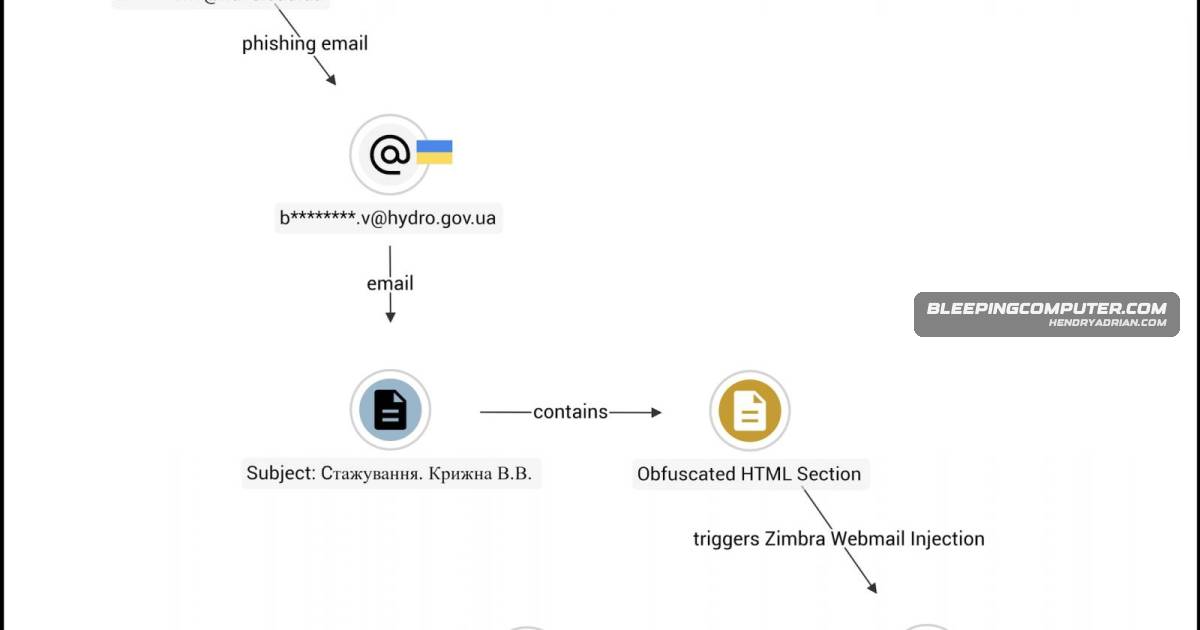
Seqrite Labs says APT28 exploited Zimbra’s stored XSS flaw CVE-2025-66376 in Operation GhostMail against Ukrainian government entities, harvesting email and account data. CISA added the flaw to its exploited-vulnerability catalog and ordered federal agencies to patch.