
Perseus Android Malware Scans Notes for Secrets and Enables Device Takeover
Summary
ThreatFabric reports that Perseus Android malware, distributed through sideloaded IPTV apps, scans notes for sensitive information and abuses Accessibility Services for device control. It targets financial institutions and crypto apps, especially in Turkey and Italy.
Key points
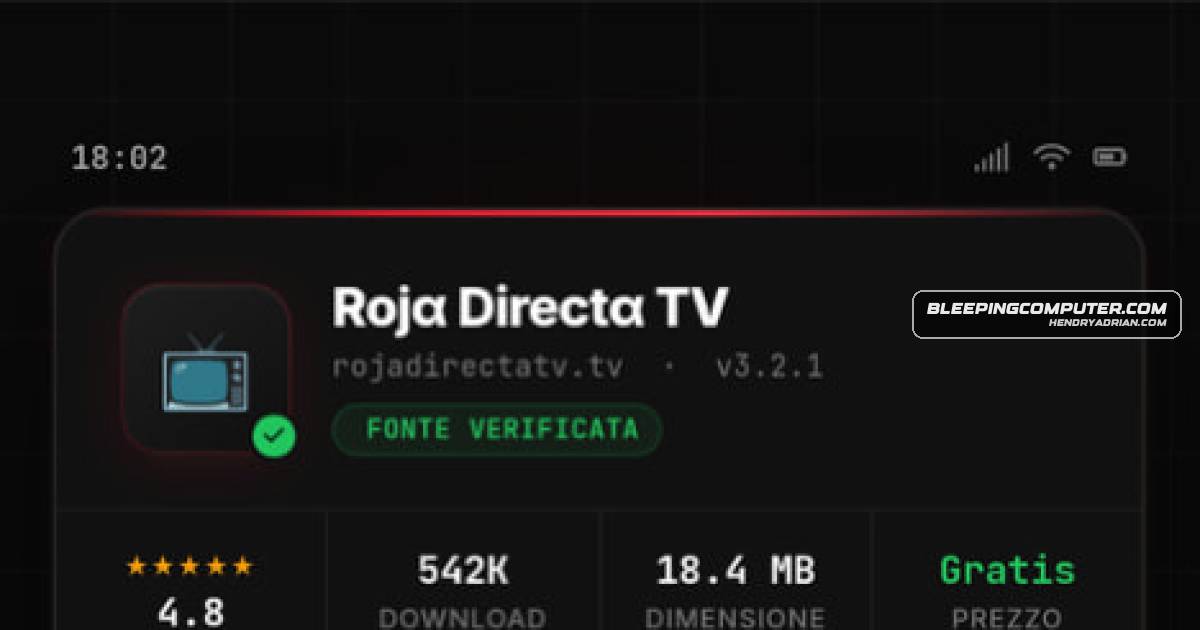
- ThreatFabric says Perseus is distributed through unofficial IPTV apps, including Roja Directa TV; its dropper can bypass Android 13+ sideloading restrictions.
- The malware scans note-taking apps for passwords, recovery phrases, financial details and other sensitive information.
- Perseus abuses Android Accessibility Services for remote interaction, screenshots, keylogging and overlay attacks.
- Reported targets include financial institutions in Turkey, Italy and other European countries, plus nine cryptocurrency apps.
- Before acting, Perseus checks device and environment details, calculates a “suspicion score” and sends it to its command-and-control panel.
- Researchers describe Turkish and English variants and say Perseus appears to build on the Phoenix codebase, derived from Cerberus.
Article Details
- Event Type
- Android malware campaign involving Perseus, distributed through unofficial IPTV apps.
- Impact
- Perseus scans notes for passwords, recovery phrases, and financial information, and can use Accessibility Services to remotely control infected devices, capture screenshots, simulate input, display overlays, and log keystrokes. Researchers report targeting financial institutions in Turkey, Italy, Poland, Germany, and France, as well as cryptocurrency apps.
Malware
Cerberusscore” to its C2 before acting, has Turkish and more refined English variants, and builds on the Phoenix/Cerberus codebase with signs of AI-assisted development.KlopatraThe dropper for Perseus can bypass Android 13+ sideloading restrictions and is the same one for delivering the Klopatra and Medusa malware.MassivIn a recent campaign, threat actors leveraged the IPTV app lure to distribute the Massiv Android banking malware.MedusaThe dropper for Perseus can bypass Android 13+ sideloading restrictions and is the same one for delivering the Klopatra and Medusa malware.PerseusPerseus is a new Android malware distributed via unofficial IPTV apps that steals sensitive information by scanning user-curated notes and can fully take over infected devices.Phoenixscore” to its C2 before acting, has Turkish and more refined English variants, and builds on the Phoenix/Cerberus codebase with signs of AI-assisted development.
Products
AndroidPerseus is a new Android malware distributed via unofficial IPTV apps that steals sensitive information by scanning user-curated notes and can fully take over infected devices.ColorNotePerseus scans note-taking apps (Google Keep, Samsung Notes, Evernote, Microsoft OneNote, ColorNote, Xiaomi Notes, Simple Notes) to harvest passwords, recovery phrases, and financial data.EvernotePerseus scans note-taking apps (Google Keep, Samsung Notes, Evernote, Microsoft OneNote, ColorNote, Xiaomi Notes, Simple Notes) to harvest passwords, recovery phrases, and financial data.Google KeepPerseus scans note-taking apps (Google Keep, Samsung Notes, Evernote, Microsoft OneNote, ColorNote, Xiaomi Notes, Simple Notes) to harvest passwords, recovery phrases, and financial data.Microsoft OneNotePerseus scans note-taking apps (Google Keep, Samsung Notes, Evernote, Microsoft OneNote, ColorNote, Xiaomi Notes, Simple Notes) to harvest passwords, recovery phrases, and financial data.Samsung NotesPerseus scans note-taking apps (Google Keep, Samsung Notes, Evernote, Microsoft OneNote, ColorNote, Xiaomi Notes, Simple Notes) to harvest passwords, recovery phrases, and financial data.Simple NotesPerseus scans note-taking apps (Google Keep, Samsung Notes, Evernote, Microsoft OneNote, ColorNote, Xiaomi Notes, Simple Notes) to harvest passwords, recovery phrases, and financial data.Xiaomi NotesPerseus scans note-taking apps (Google Keep, Samsung Notes, Evernote, Microsoft OneNote, ColorNote, Xiaomi Notes, Simple Notes) to harvest passwords, recovery phrases, and financial data.
Countries
FranceA focus on Turkey is also evident in the list of targeted financial institutions in the country (17), followed by Italy with 15, Poland with 5, Germany (3), and France (2).GermanyA focus on Turkey is also evident in the list of targeted financial institutions in the country (17), followed by Italy with 15, Poland with 5, Germany (3), and France (2).ItalyResearchers say the campaign leverages sideloading lures like Roja Directa TV, abuses Accessibility Services for remote control and overlays, and primarily targets financial and crypto services in Turkey and Italy.PolandA focus on Turkey is also evident in the list of targeted financial institutions in the country (17), followed by Italy with 15, Poland with 5, Germany (3), and France (2).TurkeyResearchers say the campaign leverages sideloading lures like Roja Directa TV, abuses Accessibility Services for remote control and overlays, and primarily targets financial and crypto services in Turkey and Italy.