
Mesh Security Walkthrough Describes CSMA Platform for Mapping Cross-Domain Attack Paths
Summary
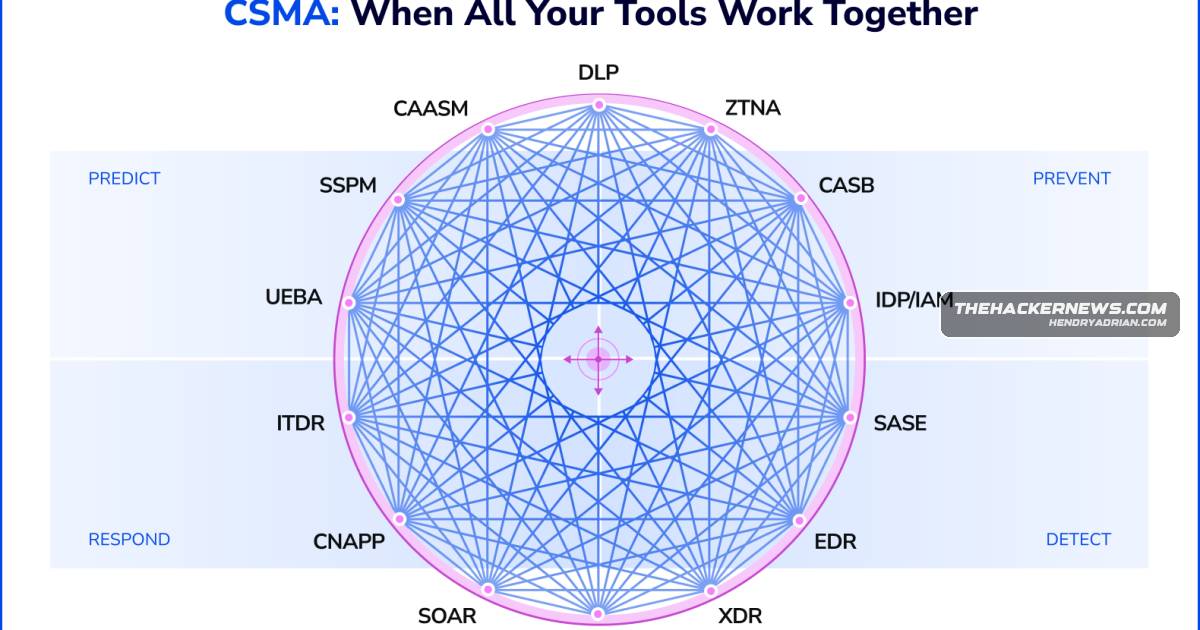
Mesh Security says its CSMA platform links existing tools in a context graph to map multi-hop paths to sensitive assets, prioritize them with threat intelligence, coordinate fixes, and identify detection gaps.
Key points
- Mesh says it connects existing security tools agentlessly and builds a continuously updated graph of identities, assets, workloads, data stores, and their relationships.
- The platform is described as correlating cloud posture, identity permissions, vulnerabilities, and detection gaps to identify multi-hop paths to sensitive assets.
- A hypothetical example links a potentially trojanized VS Code Marketplace extension, weak workstation controls, developer credentials, AWS access, and a production RDS database; the article says no breach has occurred.
- Mesh says it ranks paths using live threat intelligence and displays the entry point, intermediate steps, reachable asset, and enabling weaknesses.
- Suggested remediation examples include revoking a role binding, enforcing MFA, changing a CSPM policy, or isolating a workload, with actions coordinated across CSPM, IGA, and ZTNA tools.
- The vendor says the platform continually checks detection coverage and updates its risk model as infrastructure and threat intelligence change.
Article Details
- Event Type
- Product walkthrough of the Mesh CSMA security platform
- Impact
- The article describes Mesh CSMA as a platform that correlates security findings across tools to identify and prioritize multi-hop attack paths, then coordinates remediation and continuously validates detection gaps. The developer-workstation-to-production-database scenario is presented as a hypothetical exposure path; the article reports no breach or confirmed exploitation.