cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3801 articles

Security News · stepsecurity.io

Step Security Adds Windows Support to Dev Machine Guard

Step Security says Dev Machine Guard now runs natively on Windows 10 and 11, extending its inventory of developer tools, packages, extensions and MCP configurations across Windows and macOS fleets.

Apr 15, 2026
Security News · attackiq.com

AttackIQ Releases RoningLoader Emulation for DragonBreath Behaviors

AttackIQ added a RoningLoader emulation to its AEV platform, modeling DragonBreath (APT-Q-27) post-compromise behaviors across execution, persistence, privilege escalation, defense evasion and discovery to help organizations test security controls.

Apr 14, 2026
Security News · bleepingcomputer.com

Microsoft’s April 2026 Patch Tuesday Fixes 167 Vulnerabilities, Including Two Zero-Days

Microsoft’s April 2026 updates fix 167 vulnerabilities, including an actively exploited SharePoint spoofing flaw and a publicly disclosed Defender elevation-of-privilege flaw. Eight issues are Critical; multiple Office RCEs can be triggered through the preview pane or a

Apr 14, 2026
Security News · bleepingcomputer.com

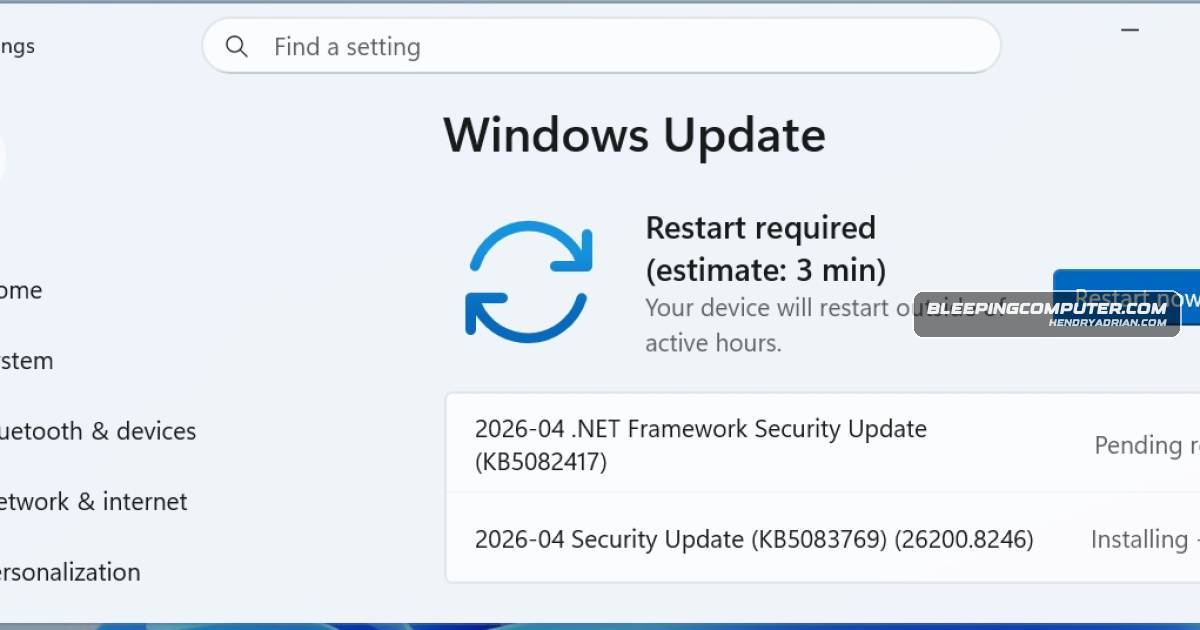
Windows 11 April 2026 Updates Add Security Fixes and Smart App Control Toggle

Microsoft released mandatory April 2026 updates KB5083769 and KB5082052 for Windows 11 25H2/24H2 and 23H2, delivering security fixes and allowing Smart App Control to be toggled without a clean install, alongside reliability and feature updates.

Apr 14, 2026
Security News · bleepingcomputer.com

Researchers Find 100+ Malicious Chrome Extensions Targeting Google and Telegram Accounts

Socket researchers found 100+ Chrome Web Store extensions across five publisher identities, with behaviors including Google OAuth token theft, account-data harvesting, backdoors and Telegram session hijacking. They suspect a Russian MaaS operation and notified Google.

Apr 14, 2026
Security News · therecord.media

Virginia Bans Sale of Precise Geolocation Data

Virginia enacted a law barring sales of precise geolocation data within a 1,750-foot radius. The measure amends the state privacy law, takes effect July 1, and follows similar laws in Maryland and Oregon.

Apr 14, 2026
Security News · securityweek.com

Microsoft Fixes 165 Flaws, Including Exploited SharePoint Zero-Day

Microsoft’s April 2026 updates fix 165 vulnerabilities, including the reportedly exploited SharePoint zero-day CVE-2026-32201. CISA added it to its KEV catalog and set an April 28 patch deadline for federal agencies.

Apr 14, 2026
Security News · bleepingcomputer.com

Microsoft releases Windows 10 KB5082200 update with 167 security fixes

Windows 10 update KB5082200 addresses 167 April 2026 vulnerabilities, including two zero-days, and adds protections for Remote Desktop .rdp files and Secure Boot certificate rollout.

Apr 14, 2026
Security News · securityweek.com

Adobe Patches 55 Vulnerabilities Across 11 Products

Adobe patched 55 vulnerabilities across 11 products. Five critical ColdFusion flaws can bypass security features, read files or execute code; Adobe says it is unaware of in-the-wild exploitation of the patched flaws.

Apr 14, 2026
Security News · thehackernews.com

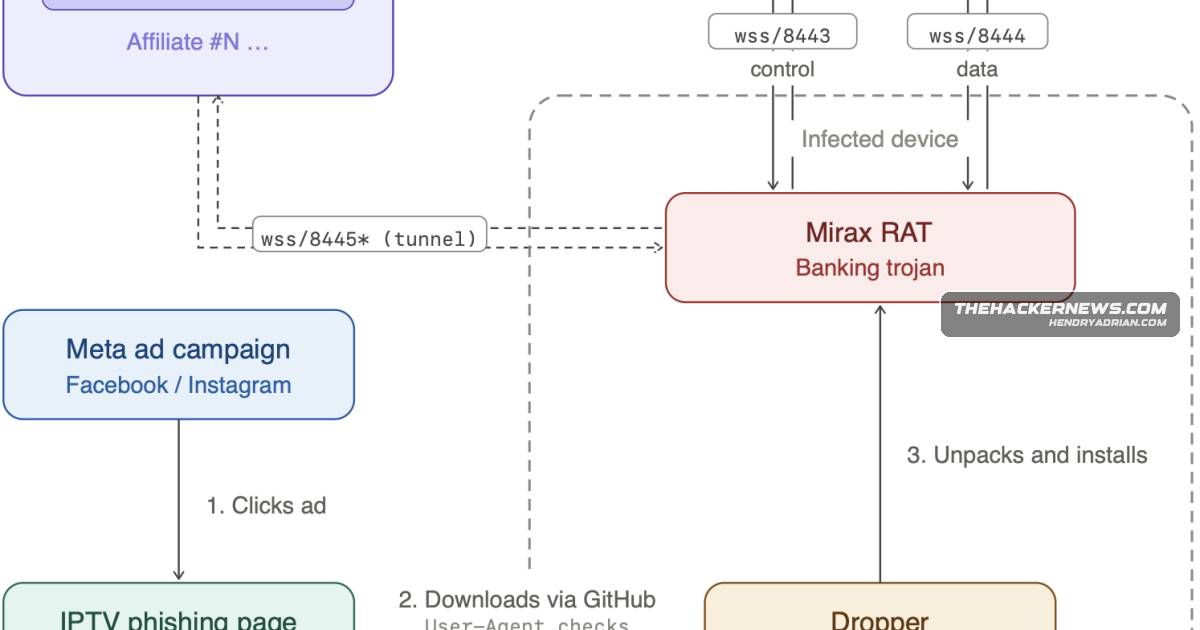
Mirax Android RAT Campaign Reaches 220,000 Accounts Through Meta Ads

Cleafy reports that Meta ads targeting Spanish-speaking users promote Mirax droppers, reaching over 220,000 accounts. The Android RAT steals credentials and can route traffic through infected devices as SOCKS5 proxies.

Apr 14, 2026
Security News · thehackernews.com

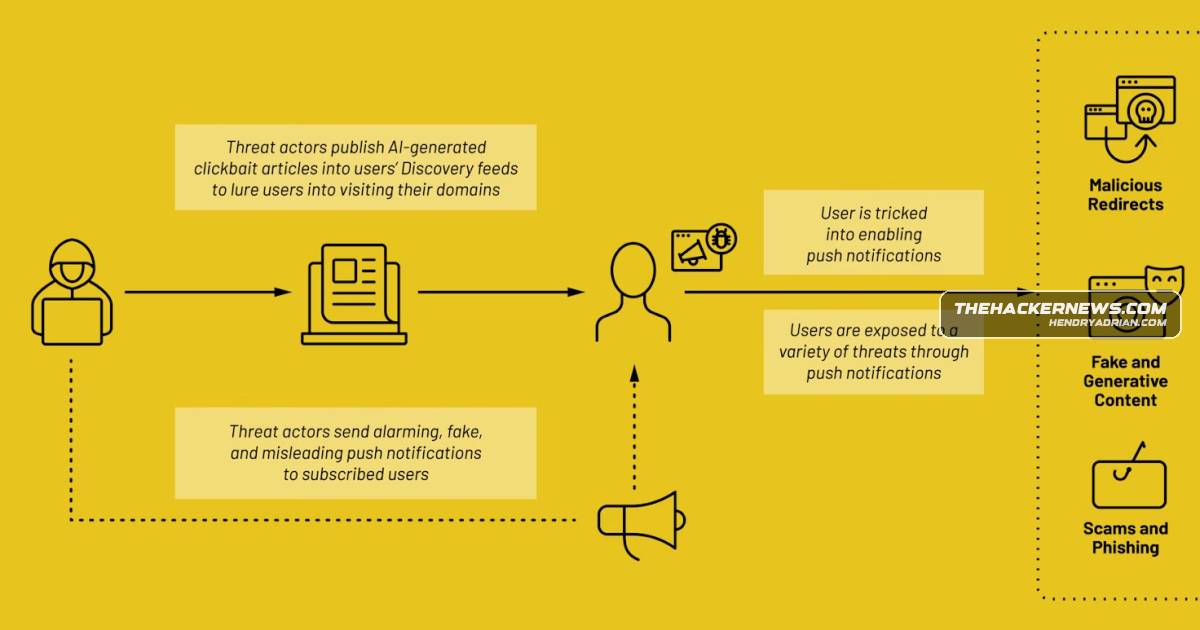
Researchers Detail Pushpaganda’s AI-Driven Ad-Fraud Campaign

Researchers say Pushpaganda used AI-generated stories in Google Discover to lure users into enabling notifications that delivered scareware and scams. The campaign was linked to 240 million bid requests across 113 domains in a week; Google says it rolled out a fix.

Apr 14, 2026
Security News · thehackernews.com

Google Adds Rust DNS Parser to Pixel 10 Modem to Reduce Memory-Safety Risk

Google says Pixel 10 modem firmware now uses an adapted Rust DNS parser to reduce memory-safety risk in the cellular baseband. The implementation uses hickory-proto and cargo-gnaw; Google notes the crate is not optimized for memory-constrained systems.

Apr 14, 2026
Security News · therecord.media

Russia reportedly blocks Bluesky amid widening internet restrictions

RKS Global says Roskomnadzor added Bluesky to Russia’s registry of banned websites. The agency has not publicly explained the move, which comes amid broader platform restrictions, efforts to limit VPN use, and mobile internet shutdowns.

Apr 14, 2026
Security News · wiz.io

Wiz and Cloudflare Integrate Cloud Visibility With AI Endpoint Protection

Wiz and Cloudflare announced an integration combining cloud-context visibility with AI endpoint protections, helping teams identify exposed AI workloads and endpoints and apply safeguards against prompt injection and PII exposure.

Apr 14, 2026
Security News · securityweek.com

SAP’s April 2026 Security Updates Fix Critical ABAP SQL Injection

SAP released 20 new and updated security notes for April 2026. The most severe fixes a critical SQL injection flaw in Business Planning and Consolidation and Business Warehouse; SAP reported no known in-the-wild exploitation.

Apr 14, 2026
Security News · wiz.io

Wiz Adds Shadow Data Detection to Identify Redundant and Stale Cloud Data

Wiz introduced Shadow Data Detection, a capability that analyzes cloud-provider inventory reports to identify duplicated, stale, and over-retained data, helping teams prioritize removal and reduce storage costs and unnecessary exposure.

Apr 14, 2026
Security News · thecyberexpress.com

Goldman Sachs Assesses Cybersecurity Risks of Anthropic’s Mythos AI Model

Goldman Sachs says it is working with Anthropic and cybersecurity partners to assess risks from Mythos, which Anthropic says can find and exploit sophisticated software vulnerabilities. The model is being shared with 11 organizations through Project Glasswing.

Apr 14, 2026
Security News · cert-agid.gov.it

CERT-AGID Reports SPID Phishing Campaign Targeting Public Administrations

CERT-AGID identified phishing impersonating Agenzia delle Entrate–Riscossione, using a fake SPID login to steal passwords. It notified the affected entity, sought takedown of the site and shared IoCs.

Apr 14, 2026
Security News · thehackernews.com

CISA Adds Six Exploited Vulnerabilities to KEV Catalog

CISA added six vulnerabilities to its KEV catalog. Reported exploitation includes Fortinet FortiClient EMS and Microsoft Exchange flaws; federal agencies must apply fixes by April 27, 2026.

Apr 14, 2026
Security News · thecyberexpress.com

TierOne Forum Announces $10,000 Exploit-Writing Contest

The TierOne dark web forum announced an exploit-writing contest running April 13–May 14, 2026, with $10,000 in prizes. Topics include RCE, IDOR, firmware attacks and AV/EDR bypasses; the ransomware group cry0 reportedly sponsors it.

Apr 14, 2026
Security News · reversinglabs.com

ReversingLabs Offers Free Spectra Assure Community for Open-Source Supply-Chain Security

ReversingLabs describes Spectra Assure Community, a free tool for assessing open-source package risks, including malware, vulnerabilities, secrets, and tampering, with integrations for development workflows.

Apr 14, 2026
Security News · bleepingcomputer.com

OpenAI to Revoke and Rotate macOS Signing Certificates After Axios Attack

After a GitHub Actions workflow ran compromised Axios 1.14.1, OpenAI began rotating macOS app signing certificates as a precaution. It reported no evidence of misuse or data exposure and required users to update by May 8, 2026.

Apr 13, 2026
Security News · bleepingcomputer.com

FBI and Indonesian Authorities Dismantle W3LL Phishing Platform; Alleged Developer Arrested

U.S. and Indonesian authorities seized W3LL infrastructure and arrested its alleged developer. The platform reportedly harvested credentials and session cookies, facilitated sales of more than 25,000 accounts, and supported business email compromise fraud.

Apr 13, 2026
Security News · cofense.com

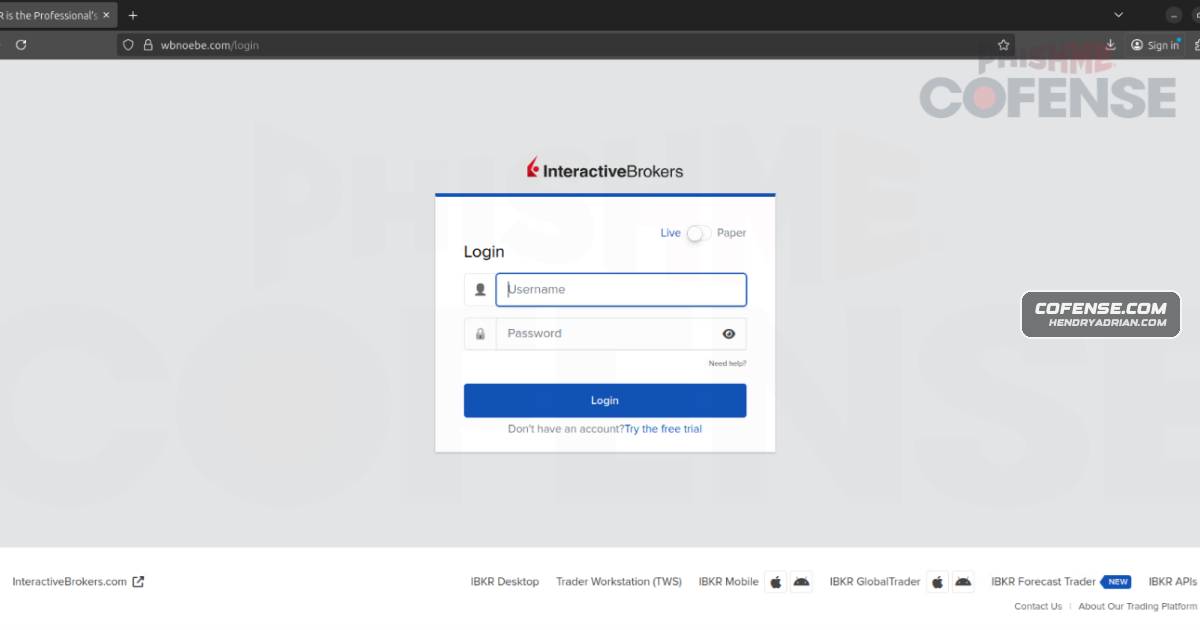
Cofense Reports Fake Interactive Brokers W-8BEN Phishing Campaign

Cofense reports a phishing campaign impersonating Interactive Brokers with a fake IRS Form W-8BEN renewal lure. The login page at wbnoebe[.]com reportedly sends submitted credentials to an actor-controlled server; Cofense recommends checking links and enabling MFA.

Apr 13, 2026
PreviousPage 118 of 159 Next
© 2026 cyber.hendryadrian.com