
Mirax Android RAT Campaign Reaches 220,000 Accounts Through Meta Ads
Summary
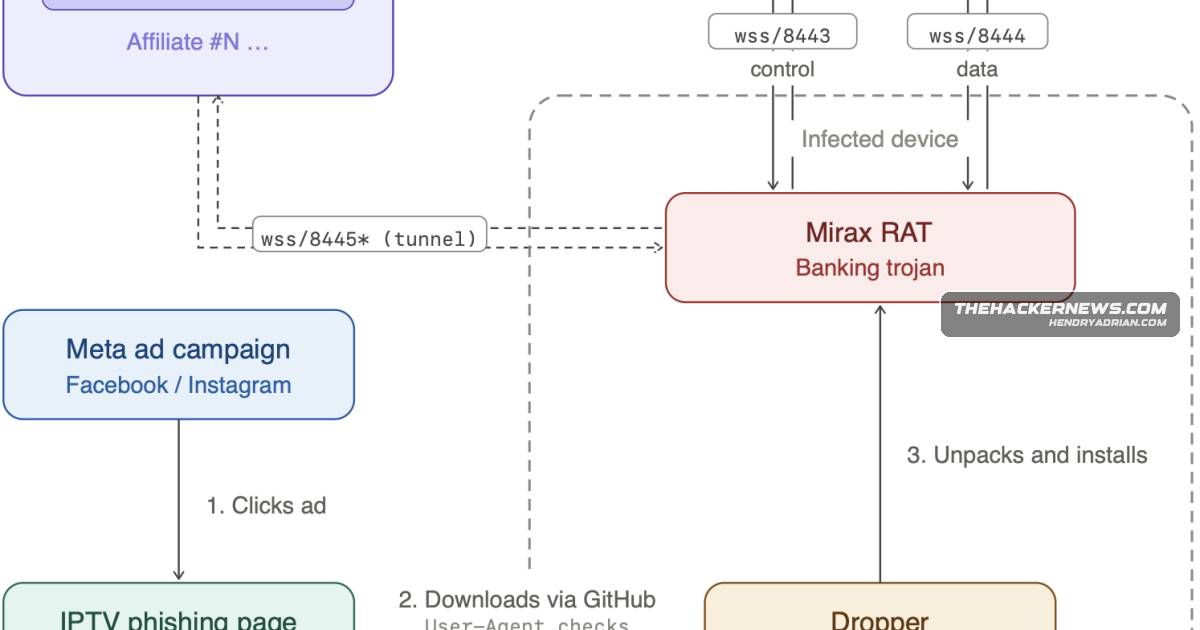
Cleafy reports that Meta ads targeting Spanish-speaking users promote Mirax droppers, reaching over 220,000 accounts. The Android RAT steals credentials and can route traffic through infected devices as SOCKS5 proxies.
Key points
- Researchers observed Mirax campaigns using Meta ads and streaming-service-themed dropper pages to target Spanish-speaking users, particularly in Spain.
- The ads reportedly reached more than 220,000 accounts; this is ad reach, not a count of infected devices.
- Mirax supports remote device control, keystroke capture, photo theft, and credential theft through overlays displayed over legitimate apps.
- The RAT can turn infected devices into SOCKS5 residential proxies using Yamux multiplexing, allowing attackers to route traffic through victims’ IP addresses.
- Dropper APKs hosted on GitHub use multi-stage extraction and prompt users to enable installation from unknown sources and accessibility services.
- The malware uses separate WebSocket channels for remote access and commands, streaming and data exfiltration, and proxy setup.
- The campaign’s exact end goals are unknown; the article also briefly describes a separate Arabic-language Android RAT called ASO RAT.
Article Details
- Event Type
- Distribution of the Mirax Android remote access trojan through Meta ads and malicious dropper pages.
- Impact
- The campaign's ads reportedly reached more than 220,000 accounts; this is not a reported count of infected devices. Mirax can control compromised devices, steal credentials using overlays, and route traffic through victims' IP addresses via SOCKS5 proxies. The article says the campaign's exact end goals are unknown.
People
Alberto GiustIdentified as a researcher who described Mirax's controlled MaaS distribution model.Alessandro StrinoIdentified as a researcher who described Mirax's controlled MaaS distribution model.Federico ValentiniIdentified as a researcher who described Mirax's controlled MaaS distribution model.
Threat Actors
Malware
ASO RATThe disclosure comes as Breakglass Intelligence detailed an Arabic-language Android RAT called ASO RAT that’s distributed via apps disguised as PDF readers and Syrian government applications.MiraxMirax, a nascent Android remote access trojan, is being spread via Meta ads that lure Spanish-speaking users to dropper pages masquerading as streaming services and has reached over 220,000 accounts.
Vendors
GitHubDropper APKs are hosted on GitHub, employ multi-stage extraction, request accessibility and unknown-source installs, and use anti-analysis checks.MetaMirax, a nascent Android remote access trojan, is being spread via Meta ads that lure Spanish-speaking users to dropper pages masquerading as streaming services and has reached over 220,000 accounts.
Products
Facebookactively targeting Spanish-speaking countries, with campaigns reaching more than 220,000 accounts on Facebook, Instagram, Messenger, and Threads through advertisements on Meta.Facebook MessengerSpanish-speaking countries, with campaigns reaching more than 220,000 accounts on Facebook, Instagram, Messenger, and Threads through advertisements on Meta.GitHubDropper APKs are hosted on GitHub, employ multi-stage extraction, request accessibility and unknown-source installs, and use anti-analysis checks.Instagramtargeting Spanish-speaking countries, with campaigns reaching more than 220,000 accounts on Facebook, Instagram, Messenger, and Threads through advertisements on Meta.Threadscountries, with campaigns reaching more than 220,000 accounts on Facebook, Instagram, Messenger, and Threads through advertisements on Meta.