
Cofense Reports Fake Interactive Brokers W-8BEN Phishing Campaign
Summary
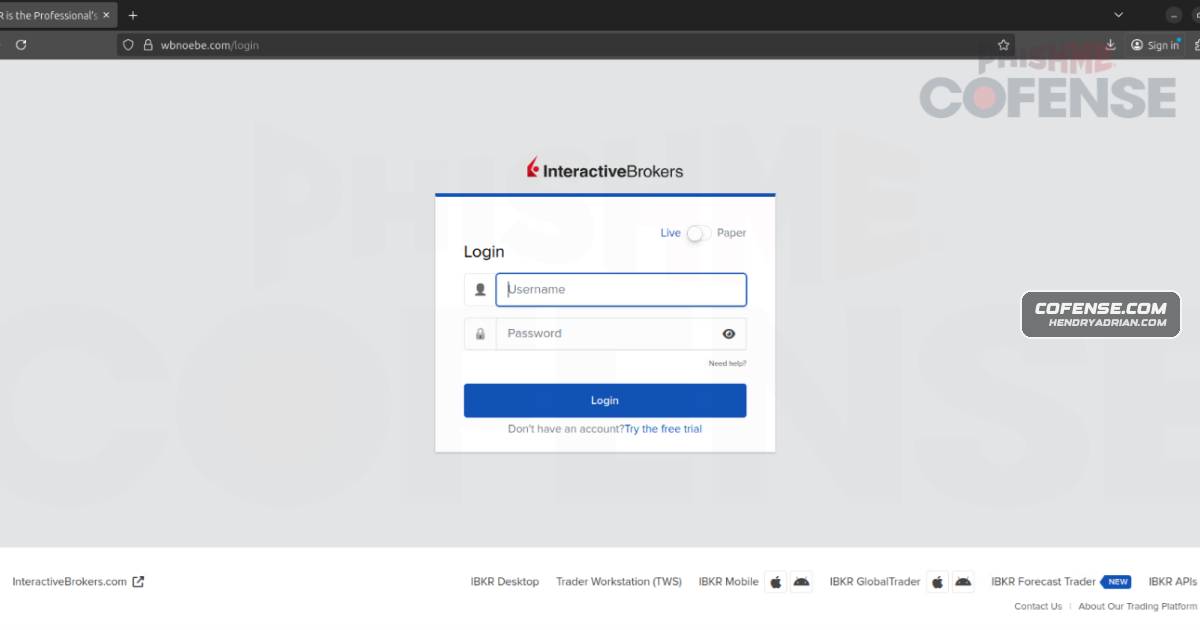
Cofense reports a phishing campaign impersonating Interactive Brokers with a fake IRS Form W-8BEN renewal lure. The login page at wbnoebe[.]com reportedly sends submitted credentials to an actor-controlled server; Cofense recommends checking links and enabling MFA.
Key points
- The reported emails impersonate Interactive Brokers and use an IRS compliance notice requesting Form W-8BEN renewal as a lure.
- The sender address [email protected] does not use Interactive Brokers’ official interactivebrokers[.]com domain.
- The “Renew Certification Now” link leads to a fake login page hosted at wbnoebe[.]com.
- Cofense reports that credentials entered on the page are sent to an actor-controlled server.
- The article recommends validating sender addresses and URLs and enabling multi-factor authentication.
Article Details
- Event Type
- Phishing campaign impersonating Interactive Brokers with a fake Form W-8BEN renewal lure and credential-harvesting page.
- Impact
- The campaign sought to collect Interactive Brokers login credentials and transmit them to an attacker-controlled server. Stolen credentials could put victim accounts and financial investments at risk; the article does not report confirmed account access or financial losses.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | wbnoebe[.]com | Phishing domain hosting a fake Interactive Brokers login page and used in the credential-harvesting campaign. |
banking@pmcmlw[.]com | Sender address identified in the phishing emails impersonating Interactive Brokers. | |
| IPV4 | 104[.]21[.]64[.]219 | IP address reported as observed hosting or C2 infrastructure for the phishing campaign. |
| IPV4 | 172[.]67[.]187[.]230 | IP address reported as observed hosting or C2 infrastructure for the phishing campaign. |
| URL | hxxps[:]//wbnoebe[.]com?token=eIqv7TknECn4EImFVxFD | Observed URL identified in the article as part of the attacker-controlled infrastructure receiving submitted credentials. |
| URL | hxxps[:]//wbnoebe[.]com/login | Phishing login-page URL used to collect Interactive Brokers credentials. |
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelCredentials entered on the phishing page were reportedly transmitted to the threat actor's C2 server.T1078 · Valid AccountsThe article states that credentials stolen through the fake login page could be used to access victim accounts as legitimate users.T1566.002 · Spearphishing LinkThe phishing emails included a link prompting recipients to visit the credential-harvesting page.