cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3801 articles

Security News · bleepingcomputer.com

Attackers exploit Marimo RCE to deploy NKAbuse variant via Hugging Face

Sysdig reports attackers exploiting Marimo CVE-2026-39987 to deploy an NKAbuse variant from Hugging Face Spaces. It recommends upgrading to Marimo 0.23.0 or blocking external access to /terminal/ws.
Apr 16, 2026
Security News · securityweek.com

OpenAI Expands GPT-5.4-Cyber Access to Verified Defenders

OpenAI is expanding its Trusted Access for Cyber program to thousands of verified defenders and hundreds of teams, offering GPT-5.4-Cyber with relaxed guardrails and binary reverse-engineering capabilities. Model performance data was not disclosed.

Apr 16, 2026
Security News · bleepingcomputer.com

ATHR Platform Automates AI-Assisted Voice-Phishing Attacks

Abnormal researchers say ATHR automates telephone-oriented attack delivery with spoofed lures, AI or human voice operators, and credential harvesting. Advertised on underground forums, it targets services including Google, Microsoft and Coinbase.

Apr 16, 2026
Security News · dailydarkweb.net

BreachForums Announces VECT Partnership and Security Upgrades

BreachForums says a security audit led to WAF, CSP, anti-XSS and anomaly-detection upgrades. The forum also announced a VECT partnership and planned affiliate keys, Monero multisignature escrow, and dataset imports.

Apr 16, 2026
Security News · wiz.io

Wiz Extends AI Application Security From Code to Runtime Remediation

Wiz says its platform will detect AI-specific risks in code, validate whether they are exploitable at runtime, trace findings to their code roots, and route fixes through developers’ workflows.

Apr 16, 2026
Security News · bleepingcomputer.com

Two U.S. Nationals Sentenced for Helping DPRK IT Workers Get Jobs at U.S. Firms

Two U.S. nationals were sentenced for helping DPRK IT workers use stolen identities to get jobs at over 100 U.S. companies. Court documents cite more than $5 million in DPRK revenue and an estimated $3 million in company damages.

Apr 16, 2026
Security News · bleepingcomputer.com

Microsoft Investigates Windows Server 2025 Update Failures and BitLocker Recovery Issue

Microsoft is investigating KB5082063 installation failures on some Windows Server 2025 systems, including 0x800F0983 errors. Some affected servers may also enter BitLocker recovery; Microsoft says the configurations are typically enterprise-managed.

Apr 16, 2026
Security News · thecyberexpress.com

EU Age-Verification App Nears Rollout With Privacy-Focused Design

The European Commission says its open-source age-verification app is technically ready and will let users prove their age without revealing their identity. Several EU countries plan wallet integration as officials signal stricter platform enforcement.

Apr 16, 2026
Security News · cybersecuritypulse.net

AI-Driven Vulnerability Discovery Puts Bug Bounties and Remediation Under Pressure

The newsletter covers Anthropic’s and OpenAI’s gated security models, OX Security’s reported MCP STDIO command-execution flaws, and HackerOne’s pause on new Internet Bug Bounty submissions as AI-assisted findings outpace remediation.

Apr 16, 2026
Security News · hendryadrian.com

Indonesia Faces Active nginx-ui Exploitation, W3LL Takedown and Emerging Malware Threats

A roundup reports active exploitation of nginx-ui CVE-2026-33032, the FBI–Indonesian police W3LL takedown, Storm infostealer and Android banking trojans targeting Indonesian users, Google’s developer-verification rollout, and an unverified Nova ransomware claim againstB

Apr 16, 2026
Security News · thehackernews.com

April Patch Tuesday Updates Address Critical Flaws Across Major Vendors

April’s patch releases cover many vendors. Adobe Acrobat Reader CVE-2026-34621 and Microsoft SharePoint CVE-2026-32201 are reported as actively exploited; other highlighted fixes address critical SAP and FortiSandbox flaws.

Apr 16, 2026
Security News · thehackernews.com

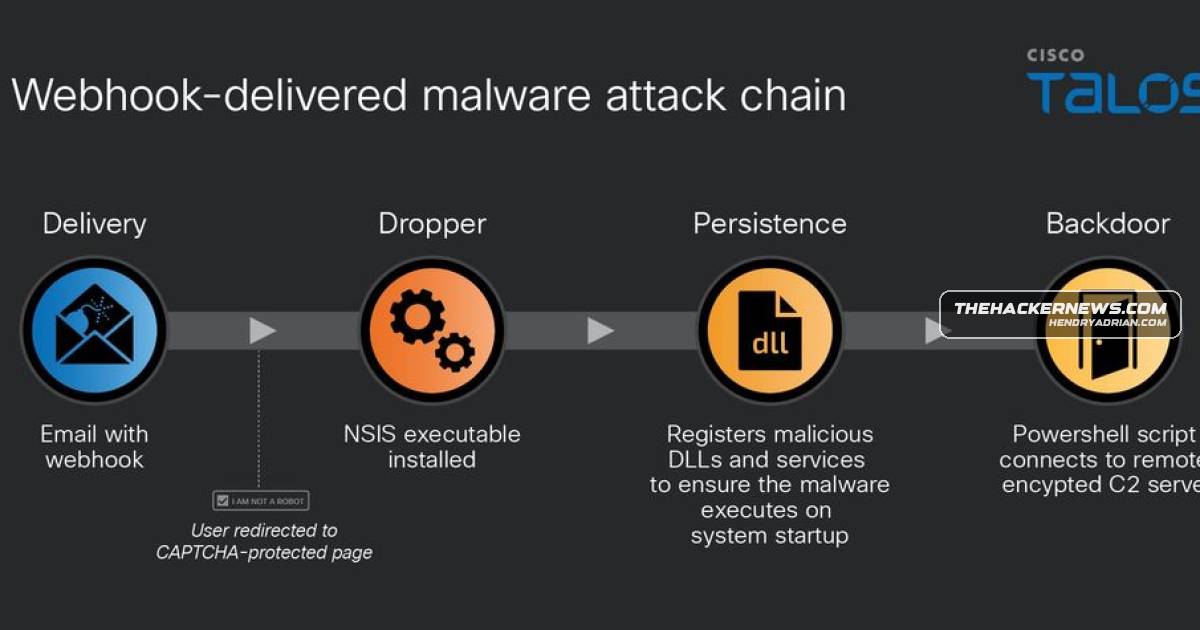
Attackers Abuse n8n Webhooks for Phishing, Malware Delivery and Device Fingerprinting

Cisco Talos says attackers have abused n8n cloud webhooks since October 2025 to host phishing pages, deliver modified Datto and ITarian RMM installers, and fingerprint email recipients. Webhook-linked email volume rose 686% in March 2026 versus January 2025.

Apr 16, 2026
Security News · therecord.media

NIST narrows CVE enrichment as submissions outpace capacity

NIST will prioritize NVD enrichment for CISA-listed exploited flaws and vulnerabilities in federal or critical products, move older backlog records to “Not Scheduled,” and rely on submitter severity scores as submissions outpace staff capacity.

Apr 16, 2026
Security News · mk.co.kr

Kazakhstan Arrests Man Accused of Leading Ransomware Attacks on Korean Organizations

South Korean police say a Kazakh man accused of leading a ransomware group was arrested in Almaty. The group reportedly encrypted servers at six Korean organizations, including hospitals, using weak or default credentials; outages occurred, but victims paid no ransom.

Apr 16, 2026
Security News · thecyberexpress.com

CERT-UA Reports UAC-0247 Campaign Targeting Ukrainian Hospitals and Government

CERT-UA reported a March–April 2026 surge in UAC-0247 activity targeting Ukrainian hospitals, emergency services, municipalities and defense-linked users, using humanitarian-aid phishing, malware and credential theft.

Apr 15, 2026
Security News · bleepingcomputer.com

Microsoft Awards $2.3 Million After Zero Day Quest Identifies 80+ Cloud and AI Flaws

Microsoft says it awarded $2.3 million after nearly 700 submissions to Zero Day Quest, where researchers identified more than 80 high-impact cloud and AI flaws. Testing was limited to authorized environments; findings will be shared through the CVE program.

Apr 15, 2026
Security News · securityweek.com

Sweden Attributes Failed Heating Plant Cyberattack to Pro-Russian Group

Sweden’s civil defense minister said a pro-Russian group linked to Russian security and intelligence services targeted a western Swedish heating plant last year, but the attack failed. Sweden gave no further details.

Apr 15, 2026
Security News · therecord.media

Research Says Major Ad Firms Often Ignore GPC Opt-Out Signals

webXray says 194 ad services ignored Global Privacy Control signals in a March audit of California web traffic, including Google, Microsoft and Meta. The companies dispute or qualify the findings; failures may violate the CCPA.

Apr 15, 2026
Security News · securityweek.com

Capsule Security Emerges From Stealth With $7 Million for AI Agent Security

Israeli startup Capsule Security emerged from stealth with $7 million in seed funding. It says its platform monitors AI agents at runtime and can intervene to block anomalous activity, risky commands and data exposure.

Apr 15, 2026
Security News · securityweek.com

Socket Finds 108 Malicious Chrome Extensions, More Than 20,000 Installs

Socket identified 108 malicious Chrome extensions with more than 20,000 installs, linked by shared command-and-control infrastructure. They reportedly steal Google and Telegram data, inject ads, or open attacker-selected URLs; Google had not immediately removed them.

Apr 15, 2026
Security News · thecyberexpress.com

OpenAI Expands Trusted Access for Cyber and Launches GPT 5.4 Cyber

OpenAI says it is expanding Trusted Access for Cyber and rolling out GPT 5.4 Cyber to vetted defenders. The program uses identity verification and phased access to provide defensive capabilities while managing dual-use risks.

Apr 15, 2026
Security News · bleepingcomputer.com

April Windows Server Update Can Trigger BitLocker Recovery on Some Devices

Microsoft says April 2026 update KB5082063 can trigger a one-time BitLocker recovery prompt on some Windows Server 2025 devices with a specific PCR7 policy configuration. Administrators can remove the policy or apply a Known Issue Rollback.

Apr 15, 2026
Security News · bleepingcomputer.com

Microsoft Adds Warnings and Default Restrictions for Risky RDP Files

April 2026 Windows updates add warnings before .rdp files connect, identify the publisher and remote address, and disable local resource redirection by default to reduce phishing-related credential and data theft.

Apr 15, 2026
Security News · stepsecurity.io

StepSecurity Adds Dependabot Grouping and Cooldown Controls

StepSecurity added group and cooldown controls to centralized Dependabot configuration, allowing teams to batch updates and set PR cadence across supported ecosystems. The company says they complement its npm Package Cooldown check.

Apr 15, 2026
PreviousPage 117 of 159 Next
© 2026 cyber.hendryadrian.com