cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3800 articles

Security News · cyberscoop.com

Pentagon Cyber Official Calls Advanced AI ‘Revolutionary Warfare’

A senior Pentagon cyber official called frontier AI a watershed moment for warfare and cyber operations. The department is using Mythos to hunt vulnerabilities despite labeling it a supply-chain risk, and is considering AI’s offensive and defensive roles.
May 14, 2026
Security News · cisecurity.org

CIS Guide Recommends Controls to Secure Model Context Protocol

CIS, Astrix Security, and Cequence Security developed AI security companion guides. The MCP guide recommends enforcing authorization outside the model, securing transports, governing capability changes, and validating tools and inputs.

May 14, 2026
Security News · thehackernews.com

Ghostwriter Uses Geofenced PDFs to Target Ukrainian Government

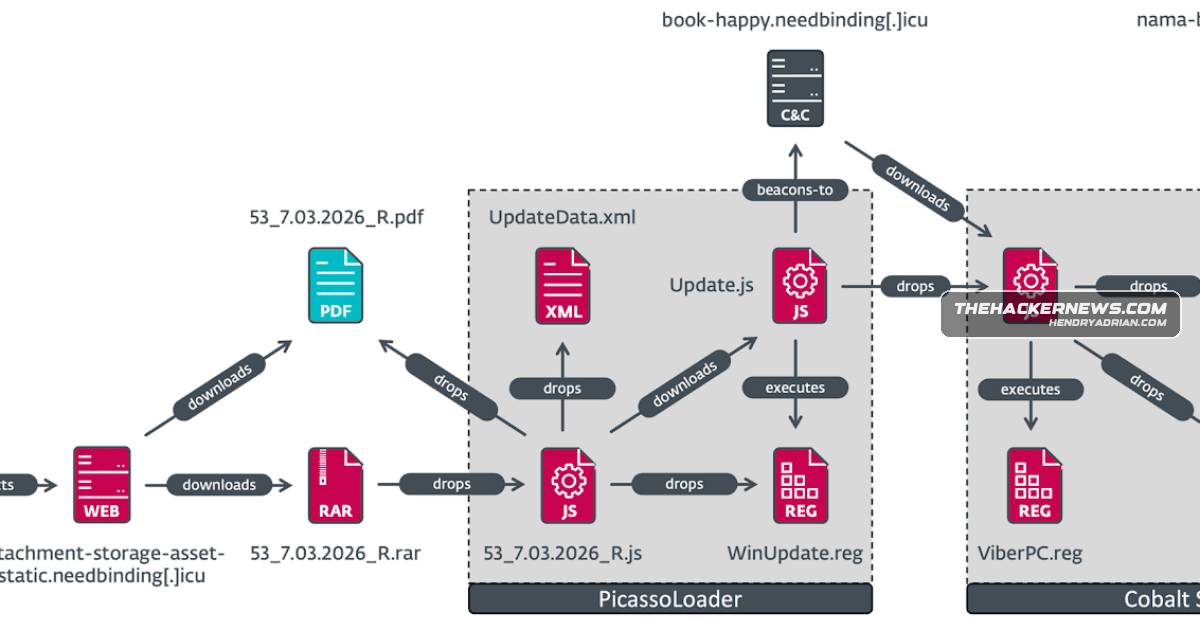
ESET reports Ghostwriter used geofenced spear-phishing PDFs impersonating Ukrtelecom to deliver PicassoLoader and Cobalt Strike to Ukrainian government targets. The article also summarizes campaigns attributed to Gamaredon, BO Team, and Hive0117.

May 14, 2026
Security News · thehackernews.com

Weekly Security Roundup: PAN-OS Exploitation, Langflow Attacks and Supply-Chain Threats

The roundup covers limited exploitation of a PAN-OS flaw, campaigns using phishing and legitimate tools, a reported Schemata data exposure, and emerging techniques including GhostLock and NATS-based C2.

May 14, 2026
Security News · securityweek.com

XBOW Finds Mythos Strong at Vulnerability Discovery, With Limits Elsewhere

XBOW’s tests found Mythos Preview particularly strong at source-code vulnerability discovery, native-code analysis and reverse engineering, but mixed in judgment and not best-in-class on cost-normalized benchmarks.

May 14, 2026
Security News · opensourcemalware.com

Podcast Covers RubyGems Attack, Canvas Ransomware and Team PCP’s Supply-Chain Campaign

The OpenSourceMalware Show discusses malicious RubyGems uploads, the ShinyHunters attack on Canvas operator Instructure, and Team PCP’s package compromises using GitHub Actions cache poisoning.

May 14, 2026
Security News · bleepingcomputer.com

U.S. Indicts Alleged Dream Market Administrator in Money-Laundering Case

U.S. prosecutors indicted Owe Martin Andresen, alleged Dream Market administrator “Speedstepper,” on 12 money-laundering counts. Authorities allege he moved marketplace proceeds through crypto wallets and gold purchases; German searches recovered gold, cash and assets.

May 14, 2026
Security News · therecord.media

UK Plans Cybercrime Law Overhaul to Support Security Researchers

The UK plans to update the Computer Misuse Act 1990 and is considering Cyber Crime Risk Orders and evidence-concealment powers. Draft legislation has not been published, and the scope of the reforms remains unclear.

May 14, 2026
Security News · cyberscoop.com

House Homeland Security Panel Plans Hearing on Anthropic’s Mythos

A House Homeland Security briefing demonstrated Anthropic’s Mythos identifying software vulnerabilities. A subcommittee chair plans a hearing on federal use amid reports that CISA is excluded while the NSA and DoD use the model; DoD has labeled Anthropic a supply-chain

May 14, 2026
Security News · therecord.media

Alleged Dream Market Administrator Arrested in Germany on Money-Laundering Charges

German and U.S. authorities arrested Owe Martin Andresen, accused of administering Dream Market, after prosecutors alleged he laundered about $2 million in marketplace commissions through cryptocurrency and gold. He faces money-laundering charges in both countries.

May 13, 2026
Security News · infostealers.com

Research Highlights Ransomware Groups’ Use of Infostealer Credentials

Check Point’s analysis of leaked Gentlemen chats describes the group’s use of stolen credentials for access. Hudson Rock reports that 80% of the Coinbase Cartel’s 100+ victims had prior infostealer infections indexed in its database.

May 13, 2026
Security News · cyberscoop.com

DOJ Memo Asserts Authority to Collect Nationwide Voter Data Despite Court Setbacks

A DOJ Office of Legal Counsel memo argues federal laws authorize nationwide collection of state voter records and sharing with immigration agencies. Courts have dismissed multiple suits seeking the data, while states resist handing over sensitive personal information.

May 13, 2026
Security News · thehackernews.com

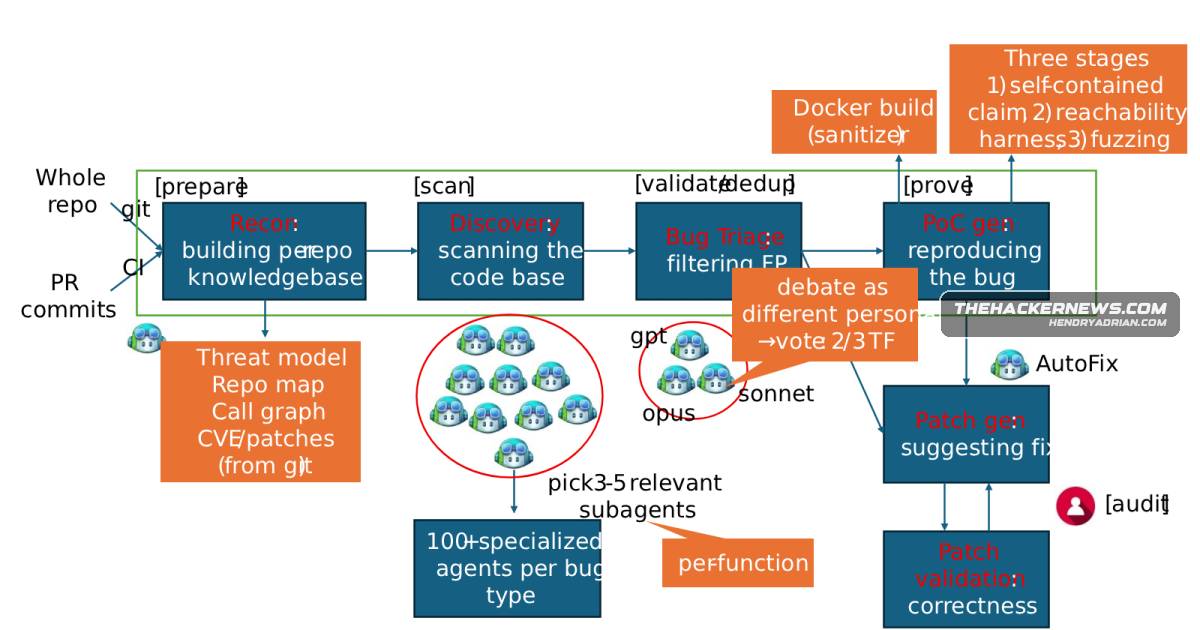
Microsoft Says MDASH AI System Found 16 Windows Flaws Fixed in Patch Tuesday

Microsoft says its MDASH system, which coordinates more than 100 specialized AI agents, found 16 Windows flaws fixed in the latest Patch Tuesday update. Two listed flaws could enable remote code execution.

May 13, 2026
Security News · cyberscoop.com

OpenAI Launches Daybreak AI Initiative for Vulnerability Discovery and Remediation

OpenAI launched Daybreak, combining its language models with Codex to help find, patch, and validate vulnerabilities. Three access tiers range from general use to controlled cybersecurity workflows; the article does not report independent testing.

May 13, 2026
Security News · bleepingcomputer.com

Microsoft Fixes Windows Autopatch Bug That Bypassed Driver Restrictions

A Windows Autopatch bug let some managed Windows 11 devices in the EU install restricted driver updates without approval, sometimes causing reboots or system failures. Microsoft says a service-side fix is in place; no customer action is needed.

May 13, 2026
Security News · bleepingcomputer.com

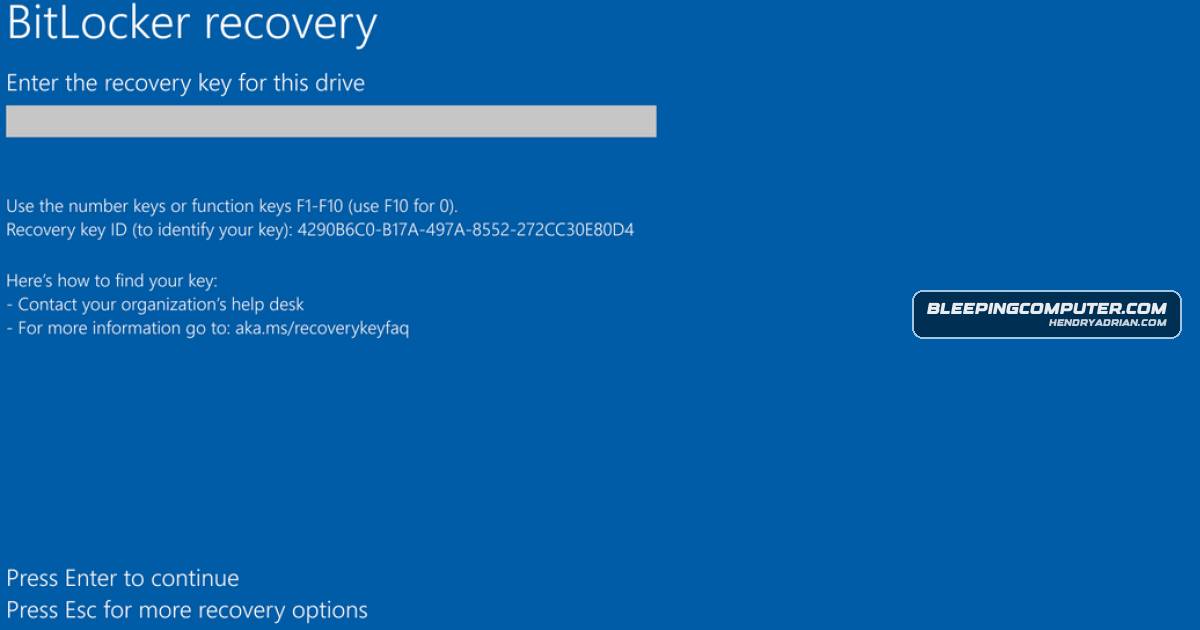
Microsoft fixes BitLocker recovery issue on Windows 11 25H2

Microsoft fixed a BitLocker recovery issue on Windows 11 25H2 with KB5089549. Windows 10 and Windows Server still await a fix; admins are advised to adjust TPM validation Group Policy settings before deploying the April 2026 updates.

May 13, 2026
Security News · securityweek.com

Microsoft and Palo Alto Networks Report AI-Driven Vulnerability Discoveries

Microsoft says its MDASH system found 16 vulnerabilities fixed in its latest Patch Tuesday updates. Palo Alto Networks says AI-assisted scans led to 75 vulnerabilities across 26 advisories; none are critical or known to be exploited.

May 13, 2026
Security News · securityweek.com

Sweet Security Launches Continuous Agentic AI Red Teaming Tool

Sweet Security says Sweet Attack uses runtime data from customer environments to continuously assess exploitable attack paths. The company says the tool is available to its customers; a beta tester reported finding attack chains and receiving remediation guidance.

May 13, 2026
Security News · wiz.io

Wiz and HackerOne Integration Adds Cloud Context to Security Findings

Wiz and HackerOne announced an integration that brings penetration-test and bug-bounty findings into Wiz, linking exploitability to cloud infrastructure, identities, data flows, and remediation workflows.

May 13, 2026
Security News · securityweek.com

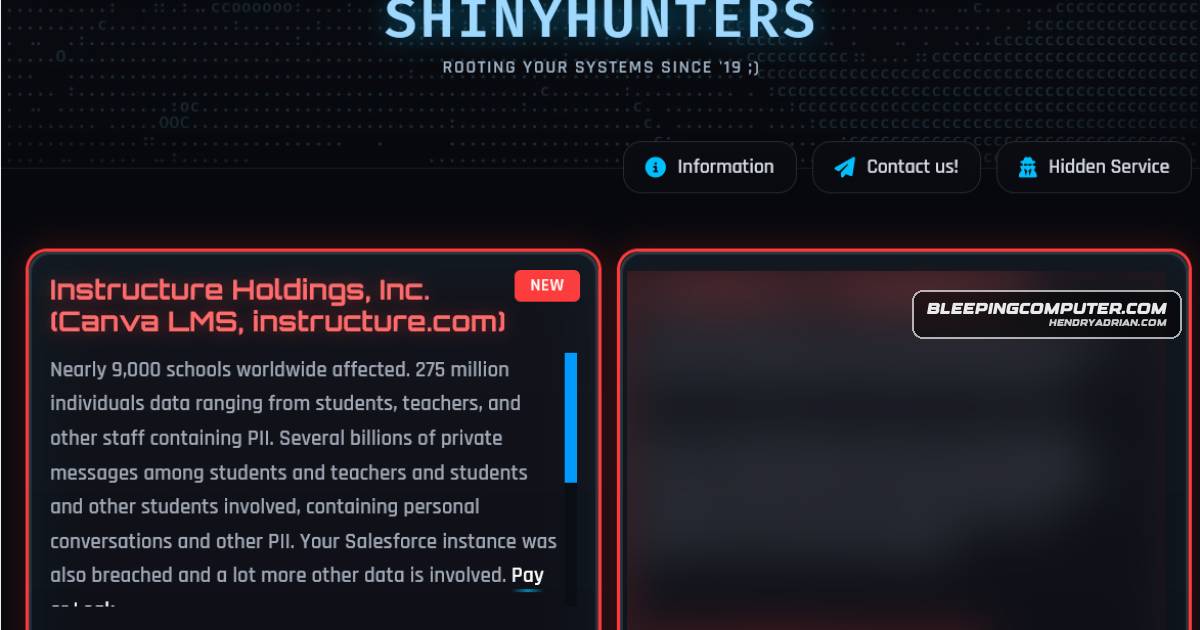
U.S. House Committee Seeks Answers on Canvas Intrusions and Data Claims

The House Homeland Security Committee is seeking answers from Instructure about two Canvas intrusions and disruptions. Instructure says a Free-For-Teacher account issue was exploited; ShinyHunters claims 3.65 TB was stolen, unconfirmed in the article.

May 13, 2026
Security News · bleepingcomputer.com

U.S. House Committee Seeks Instructure Testimony on Canvas Attacks

The House Homeland Security Committee seeks an Instructure briefing on two reported ShinyHunters attacks on Canvas, including a confirmed data breach and login-page defacements that disrupted exams.

May 13, 2026
Security News · thehackernews.com

RubyGems Pauses New Signups After Reported Attack Involving Hundreds of Packages

RubyGems paused new account registrations after Mend.io’s Maciej Mensfeld reported a malicious attack involving hundreds of packages, some said to carry exploits. The incident remains under investigation, and no actor has been identified.

May 13, 2026
Security News · cyberscoop.com

Microsoft Patches 137 Vulnerabilities in May Patch Tuesday, Reports No Actively Exploited Zero-Days

Microsoft addressed 137 vulnerabilities, including 13 rated critical, and reported no actively exploited zero-days. Researchers highlighted potential unauthenticated remote code execution in Windows DNS and Netlogon, plus a critical Dynamics 365 flaw.

May 12, 2026
Security News · cyberscoop.com

G7 Agencies Set Voluntary Baseline for AI Software Bills of Materials

G7 agencies, including CISA, issued voluntary guidance on AI software bills of materials to improve transparency and identify supply-chain risks. Experts welcomed its scope but cited implementation and runtime gaps.

May 12, 2026
PreviousPage 103 of 159 Next
© 2026 cyber.hendryadrian.com